


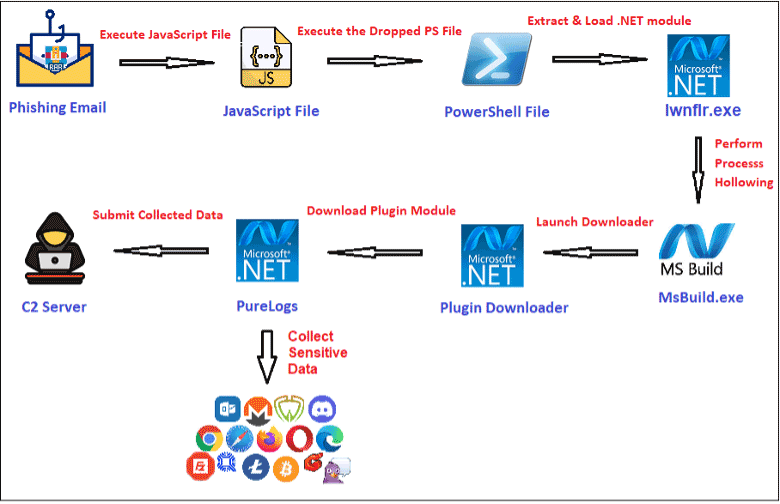
FortiGuard Labs has disclosed its findings about a new email campaign targeting Windows users with a malicious data-stealing program called PureLogs. According to their research, the attack begins with fake purchase order emails that trick targets into opening a malicious archive named “PO 2026-P0803.rar” as an initial trap.
After this, a hidden script called “kpankocrs.js” runs automatically and drops a randomly named file like "ps_qnSEGUkU0LIY_1777592585573.ps1” into the "C:\Temp" folder. It uses the Windows script engine (wscript.exe) to trigger PowerShell.exe and bypass system restrictions.
Process hollowing helps hackers avoid detection. In this technique, a genuine program is hijacked to hide the malware, which, in this case, is a legitimate Windows process at "C:\Windows\Microsoft.NET\Framework\v4.0.30319\MsBuild.exe.” Its safe code is replaced with a malicious downloader module.
Researchers further noted that this hijack relies on specific system commands to trick the computer. The malware calls CreateProcessA() to open the safe program in a frozen state, uses ZwUnmapViewOfSection() to empty its memory, plants the malicious code with WriteProcessMemory(), and triggers ResumeThread() to force the computer to run the hidden threat.
Once active inside MsBuild.exe, the malware extracts an inner module named “Iwnflr.exe” to initiate the next phase. This file loads the “Eqxcpvgf.Ybrgdoxas” resource via ResourceManager.GetObject().
It then decrypts it using the DES algorithm and decompresses it with Gunzip to assemble a downloader called “Rmiyj.dll”.
This downloader’s task is to establish a connection to a remote C2 server at 77.83.39.211 via port 8443 to send web requests. That’s when the final payload is retrieved. It sends an initial HTTP GET request to the “/ping” endpoint to confirm the server is active, followed by an HTTP POST request to the “/plugin” endpoint to download a fileless PureLogs variant named “zgSGkYYzqVe.dll”. Because of the plugin’s in-memory execution, no traces are left on the physical hard drive.
The malware now starts extracting sensitive data, targeting a broad range of browsers, cryptocurrency wallets, and apps. It steals saved login credentials, history, and cookies from Chrome, Firefox, Brave, Vivaldi, and Microsoft Edge, targets crypto wallet files, private keys, and transaction histories from Bitcoin Core, Dogecoin Core, Litecoin Core, Exodus, and Atomic Wallet.
Additionally, the malware grabs Discord authentication tokens and account passwords from Outlook, FileZilla, ProtonVPN, and OpenVPN. However, its final job is to bundle the data with a desktop JPEG screenshot, system information, clipboard data, and the username, serialise the data packet, compress it with GZip, and encrypt it using an AES key.
Now, the encrypted bundle is transmitted to the hackers’ server via HTTP POST requests to the /browser and /discord endpoints. The good aspect is that FortiMail security filters caught these phishing emails and marked the subject line as “virus detected” so that the malicious files couldn’t reach users’ inboxes.
To mitigate risks against this evasive campaign, researchers note that organisations should enforce strict email filtering, disable unnecessary script execution, and actively monitor for anomalous PowerShell activity and process hollowing.
Several cybersecurity leaders shared their insights with Hackread.com regarding the multi-layered nature of this campaign and the challenges it poses to modern defence strategies.
Jason Soroko, Senior Fellow at Sectigo, pointed out that the campaign demonstrates how threat actors are successfully hiding within normal business activities and system management tools. Soroko noted:
“The campaign relies on process hollowing to inject a .NET downloader into the trusted Windows MSBuild executable, masking it within a heavily used framework component and complicating detection. Once embedded, the downloader contacts a remote command server to retrieve modular plugins, giving the attacker dynamic post-compromise control. Layered encryption combined with legitimate system processes shows a sophisticated approach to data theft that demands equally adaptive, behavior-focused defenses.”
While the execution phase happens on desktop environments, Kern Smith, Senior Vice President of Global Solutions Engineering at Zimperium, warned that security teams must look at the bigger picture across all user devices. Smith stated:
“What makes these attacks effective is not just the malware itself, but the ability to move users from initial engagement to compromise while avoiding detection across devices and environments. Organizations should think beyond traditional endpoint visibility and ensure they can identify suspicious activity early, correlate signals across mobile devices, applications, and endpoints, and rapidly determine whether an alert represents a real incident.”
“As attack paths become more distributed and AI accelerates attacker execution, security teams need AI-empowered security capabilities that reduce investigation time and provide clearer paths from signal to response.”
Since the attack chain depends entirely on someone opening a fake purchase order attachment, the human element remains the primary barrier. Maxime Cartier, Vice President of Human Risk at Hoxhunt, explained that fixing these gaps requires changing how security risks are handled internally:
“Historically, risky behavior and the human element have been linked to up to 90% of breaches, mainly via social engineering and phishing. However, when you look meticulously at recent research, many of the risks and barriers are behavioral, not technical. This creates a significant opportunity for security awareness and Human Risk Management teams to collaborate more closely with vulnerability management teams. We spend a lot of time thinking about how to influence secure behavior at scale. Those same principles apply directly to improving remediation outcomes across the organisation.”
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。