


Hackers are exploiting the global interest in artificial intelligence (AI) to trick Windows users into downloading malware, according to the latest research from cybersecurity experts at FortiGuard Labs.
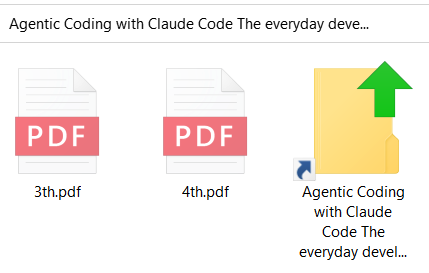
In one case spotted by researchers, cybercriminals were distributing a compressed folder disguised as a helpful AI technical guide. The folder was titled “Agentic Coding with Claude Code, The everyday developer’s guide to agentic coding with Claude Code.7z.” It looked completely safe at first glance, but it starts a complex chain of hidden scripts once opened.
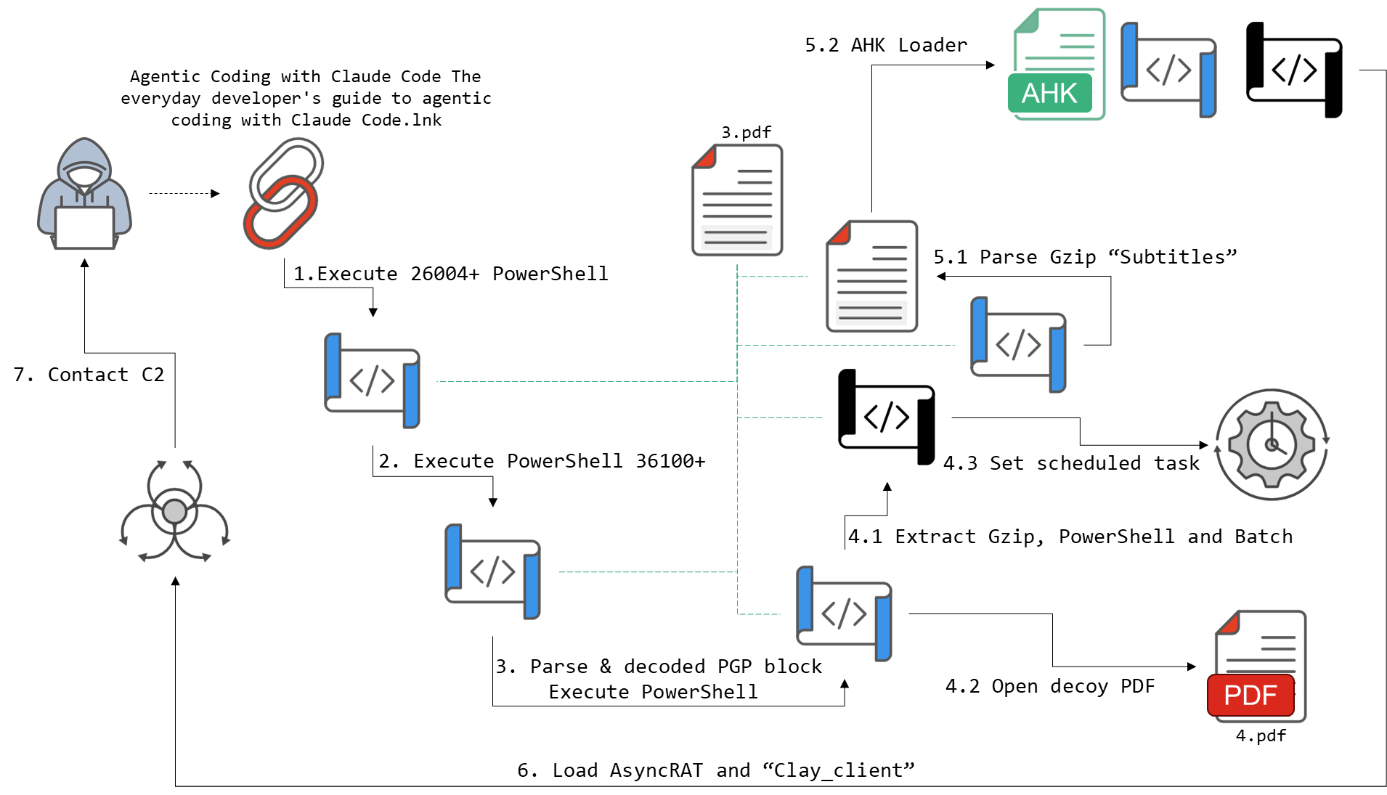
The attack begins when a victim opens a shortcut file (.lnk) inside the compressed archive. This file runs hidden commands using native Windows components like cmd.exe and findstr, and fetches data from files named 3th.pdf and 4th.pdf. that aren’t real documents but storage containers.
Now, the attack chain formally starts with a PowerShell script that drops a secondary script into the system’s AppData folder using AES-CBC decryption. This step transfers the malicious code onto the computer in an unreadable format.
Next, the malware runs a command to add the entire C:\ drive and PowerShell.exe to Microsoft Defender’s exclusion paths to blind the built-in antivirus software so that it ignores the attack. The third step is abusing AutoHotkey.exe, which is renamed to appear as a legitimate Realtek audio service. This helps the malware blend into the background processes flawlessly.
The malware uses process hollowing to create a legitimate .NET process in a suspended state and then injects malicious code into its memory space. This prevents the file from getting stored onto the disk, and the payload easily evades static file scanning.
While this happens, the malware displays readable decoy documents titled “AI-Ready PostgreSQL 18 or A Guide for Thinking Marketers in the Age of AI.” This tricks the victim into thinking the download was safe, completely distracting them from the malicious activity in the background.
In their report shared with Hackread.com, researchers confirmed that this framework is “purpose-built for stealthy payload delivery” and long-term remote access. The attack chain splits into two branches to drop two specific Remote Access Trojans (RATs).
One branch deploys a modular .NET client with surveillance capabilities, while the other installs AsyncRAT. Both tools allow hackers to monitor user desktops, track mouse movements, and upload basic system information to command-and-control servers like shampobiskworld.nl.
Interestingly, while determining adversary attribution, researchers found evidence of automated assistance. They noticed that the intermediate PowerShell scripts make heavy use of Simplified Chinese variable names. The code even contains a messy, unedited Chinese comment line and a random emoji.
Researchers conclude that human operators may have designed the overall attack logic but used generative AI tools to write the code quickly. The hackers didn’t remember to sanitize and clean up the scripts before launching the campaign.
FortiGuard Labs warns that any organisation can be targeted; therefore, users must monitor for strange scheduled tasks and avoid opening unexpected shortcut files from unverified sources.
In statements shared with Hackread.com, Ram Varadarajan, CEO at Acalvio, highlighted the danger of the multi-step nature of this campaign, stating, “This class of attack – via compositional opacity — reflects a growing threat class. Essentially, decomposing the attack into multiple, subtle steps, none of which individually raise a flag, but whose cumulative effect causes the damage.”
“We can expect such attacks to become increasingly AI-tuned, hence increasingly subtle, with attacks executed against unwitting humans and AI agents alike. Defending against them will require layered defenses, culminating in AI-aware tripwires,” he warned.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。