
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

G
Google Developers Blog
阮一峰的网络日志
阮一峰的网络日志
博客园 - 聂微东
F
Fortinet All Blogs
H
Help Net Security
让小产品的独立变现更简单 - ezindie.com
D
DataBreaches.Net
MyScale Blog
MyScale Blog
B
Blog
I
InfoQ
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
GbyAI
GbyAI
Google DeepMind News
IT之家
IT之家
The GitHub Blog
The GitHub Blog
有赞技术团队
有赞技术团队
博客园_首页
L
LangChain Blog
V
V2EX
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
T
The Blog of Author Tim Ferriss
Cyber Security Advisories - MS-ISAC
Microsoft Azure Blog
博客园 - Franky

Hackread – Cybersecurity News, Data Breaches, AI and More

Operation Endgame Disrupts StealC, Amadey and SocGholish Malware Networks New GhostShell Hacking Group Targets Ukraine’s Drone Defense Sector Fake npm Packages Impersonate PostCSS Tool to Steal Chrome Passwords Best Crypto Payment Solutions for E-Commerce Businesses Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity LastPass Confirms Customer Data Breach After Klue OAuth Token Theft ‘Cordyceps’ CI/CD Flaw Exposes Microsoft, Google, Apache Repos to Pipeline Hijacking The Rise of AI-Powered Academic Fraud: Beyond Traditional Plagiarism New CryptoBandits Malware Uses USB Drives and Tor to Steal Crypto The Evolution of iGaming Fraud: What Security Teams Should Expect in 2027 2 Scattered Spider-Linked Hackers Plead Guilty Over £39M TfL Cyberattack Beats Studio Buds Flaw Could Let Nearby Attackers Eavesdrop on Users Texas Parks and Wildlife Data Breach Affects Over 3M License Customers Threat Hunting Beyond Alerts: Finding the Activity Detection Misses Scammers Use Fake GitHub Stars, VirusTotal Reviews to Spread Crypto Clipper Salesforce Disables Klue Integration After OAuth Token Theft Hits Customer Data MDR Provider Comparison: Time to Discover and Respond to Threats Meteor 3.0 Migration Helped Rocket.Chat Move Off End-of-Life Node.js Runtime Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections Nintendo America Employee Data Exposed After Shadowbyt3$ Targets TinyPulse eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks FIFA World Cup 2026: Hackers Target Football Fans With Fake Tickets Sites MacBook Neo vs Windows Laptops for Cybersecurity Tasks Operation Endgame Disrupts SocGholish Malware Infrastructure What Businesses Should Know Before Migrating Their CMS DragonForce Ransomware Abused Microsoft Teams to Hide Malware Activity Agentjacking: Researchers Show How One Fake Bug Report Can Hijack AI Coding Agents FortiBleed Attack Exposes Fortinet Firewall Credentials in 194 Countries SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Fake Search Clicks
ShinyHunters Leak 40GB of University of Nottingham Studen...
Deeba Ahmed · 2026-06-12 · via Hackread – Cybersecurity News, Data Breaches, AI and More

The University of Nottingham is the newest victim of the infamous ShinyHunters hacking group. On Wednesday, the university released a statement confirming that unauthorised individuals gained access to its Campus Solutions network- a system used to manage student records. Reportedly, the breach impacted data from the university’s China and Malaysia campuses, too, and this exposure impacts both current students and alumni.

Immediate Response

After detecting the attack on Tuesday, 9th June, the university immediately took the affected systems offline to contain the impact. While the university didn’t publicly name the perpetrators, its chief governance and risk officer, Jason Carter, stated in an internal email to students that the hackers had previously targeted a number of other organisations.

An investigation is also launched with assistance from Action Fraud and the Information Commissioner’s Office. A dedicated support line is set up by the university at 0115 74 86500 to handle student inquiries and provide updates.

What is the scope of the breach?

In its official statement, the university admitted that a “significant amount” of its student record system data was accessed “by an external third party.” Also, it confirmed the exposed data includes contact details, student ID numbers, course information, and National Insurance numbers, which are unique numbers used in the UK for tax and employment tracking.

However, before this statement, ShinyHunters had already published the alleged stolen data on their dark web leak site. Independent data breach monitoring services analysed the data and confirmed verifying around 455,000 unique email addresses along with extensive personal details.

According to the ShinyHunter’s public post on their extortion site, they have stolen more than 40GB of data as part of their “pay or leak” extortion campaign.

This includes “billing and payment records, credit card and payment details, student finance data, and campus portal exports from the University of Nottingham and its Malaysia and China campuses.”

Additionally, the group alleges stealing “payer contact information, transaction amounts, IP addresses, full names, home addresses, postcodes, email addresses, phone numbers, dates of birth, and other internal campus data” as well.
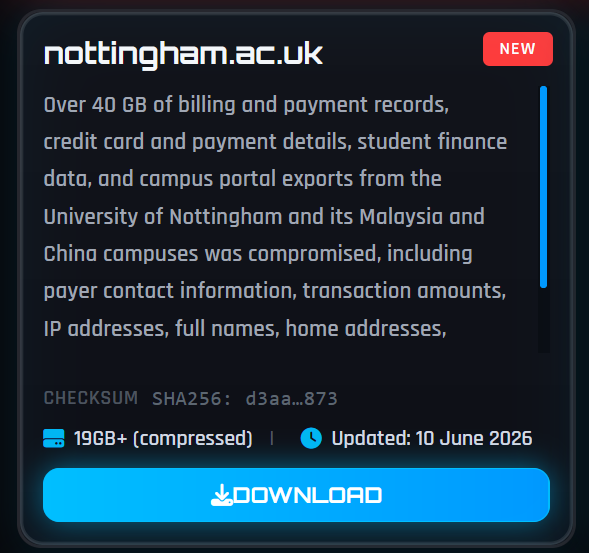
ShinyHunters Leaks 40GB of University of Nottingham Student Data
Screenshot credit Hackread.com

Wrong Timing

This incident’s timing is crucial since the university is already dealing with a labour dispute after notifying 2,700 staff members (a third of its workforce) about their probable redundancy over financial challenges, with the aim of cutting 600+ full-time jobs over the next three years. In response, the University and College Union members started an assessment boycott. They have refused to mark exams and assignments.

Students, especially those in the final year, are the most affected in this situation as they have to face complications arising from the data leak and the boycott. Many students were already anxious about how their degrees would be graded, and this incident has added an angle of vulnerability, as their personal details were exposed online.

(Photo by Alicja Ziaj on Unsplash)