

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Y
Y Combinator Blog
MyScale Blog
MyScale Blog
Recent Announcements
酷 壳 – CoolShell
酷 壳 – CoolShell
GbyAI
GbyAI
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
Cyber Security Advisories - MS-ISAC
N
Netflix TechBlog - Medium
V
V2EX
MongoDB | Blog
MongoDB | Blog
Microsoft Security Blog
博客园 - 三生石上(FineUI控件)
Stack Overflow Blog
Stack Overflow Blog
U
Unit 42
B
Blog
Microsoft Azure Blog
博客园_首页
H
Help Net Security
D
DataBreaches.Net
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
阮一峰的网络日志
阮一峰的网络日志
T
The Blog of Author Tim Ferriss
C
Check Point Blog
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报

Hackread – Cybersecurity News, Data Breaches, AI and More

Operation Endgame Disrupts StealC, Amadey and SocGholish Malware Networks New GhostShell Hacking Group Targets Ukraine’s Drone Defense Sector Fake npm Packages Impersonate PostCSS Tool to Steal Chrome Passwords Best Crypto Payment Solutions for E-Commerce Businesses Internet Society Foundation Opens Global Call for Common Good Cyber Fund to Strengthen Cybersecurity LastPass Confirms Customer Data Breach After Klue OAuth Token Theft ‘Cordyceps’ CI/CD Flaw Exposes Microsoft, Google, Apache Repos to Pipeline Hijacking The Rise of AI-Powered Academic Fraud: Beyond Traditional Plagiarism New CryptoBandits Malware Uses USB Drives and Tor to Steal Crypto The Evolution of iGaming Fraud: What Security Teams Should Expect in 2027 2 Scattered Spider-Linked Hackers Plead Guilty Over £39M TfL Cyberattack Beats Studio Buds Flaw Could Let Nearby Attackers Eavesdrop on Users Texas Parks and Wildlife Data Breach Affects Over 3M License Customers Threat Hunting Beyond Alerts: Finding the Activity Detection Misses Scammers Use Fake GitHub Stars, VirusTotal Reviews to Spread Crypto Clipper Salesforce Disables Klue Integration After OAuth Token Theft Hits Customer Data MDR Provider Comparison: Time to Discover and Respond to Threats Meteor 3.0 Migration Helped Rocket.Chat Move Off End-of-Life Node.js Runtime Gcore Helps Ucom Safeguard Public Live Broadcast Infrastructure During Armenia’s Parliamentary Elections Nintendo America Employee Data Exposed After Shadowbyt3$ Targets TinyPulse eFAQ Publishes Investigation Into Alleged Scam Activity and Coordinated Reputation Attacks FIFA World Cup 2026: Hackers Target Football Fans With Fake Tickets Sites MacBook Neo vs Windows Laptops for Cybersecurity Tasks Operation Endgame Disrupts SocGholish Malware Infrastructure What Businesses Should Know Before Migrating Their CMS DragonForce Ransomware Abused Microsoft Teams to Hide Malware Activity Agentjacking: Researchers Show How One Fake Bug Report Can Hijack AI Coding Agents FortiBleed Attack Exposes Fortinet Firewall Credentials in 194 Countries SpyCloud Report Finds Phishing Attacks Surge as Employee Data Is Exposed at 86% of Fortune 100 Companies 152 Chrome Live Wallpaper Extensions Hid Ad Tracking and Fake Search Clicks
Trojanized Gemini and Claude Installers Target Developers...
Deeba Ahmed · 2026-05-27 · via Hackread – Cybersecurity News, Data Breaches, AI and More

Cybercriminals are using fake websites for popular Artificial Intelligence (AI) tools to trick software developers into downloading data-stealing malware. The issue was first spotted on 21 April 2026 by an independent security researcher known as @g0njxa on X (formerly Twitter).

Following this discovery, on 21 May 2026, the security research firm EclecticIQ released a full report showing that a single, financially motivated threat actor had been setting up malicious domains since early March 2026. This campaign specifically targets developers in the US and the UK by exploiting their trust in new AI utilities.

The Search Engine Trap

This attack involves using SEO poisoning to push fake installation pages to the top of Google search results so that developers searching for tools like the Google Gemini Command Line Interface (CLI) or Anthropic’s Claude Code end up on typosquatted domains like geminicli.co.com and claudecode.co.com. These domains perfectly copy official vendor documentation.

When a user visits the fake Gemini page, they are told to copy and paste a PowerShell command into their terminal. This command contacts gemini-setup.com and downloads a malicious script named start.ps1.

In a clever move to avoid suspicion, the script uses the npm package manager to install the actual, legitimate Gemini CLI in the background. While the developer uses the real tool, the malware quietly compromises the system. A parallel campaign started on 30 March using claudecode.co.com and claude-setup.com to deploy the same setup.

Memory Injection and Data Theft

The payload, a fileless infostealer, runs entirely in memory via PowerShell, which means it doesn’t write files to the local disk and hence doesn’t leave a forensic trail. When active, according to EclecticIQ’s blog post, it starts by shutting down the Antimalware Scan Interface (AMSI) and Event Tracing for Windows (ETW). This helps to blind the system’s local endpoint defences before collecting sensitive data from three areas:

  • Browsers: It captures login credentials, session cookies, and autofill history from Firefox, Chrome, Edge, Brave, and other browsers.
  • Apps: It targets Slack, Microsoft Teams, Zoom, Discord, Mattermost, Notion, Telegram, and Zoho Mail to steal DPAPI-protected keys and session cookies. This data lets cybercriminals infiltrate internal corporate networks without entering passwords.
  • Files and Wallets: It collects OpenVPN configuration files, cryptocurrency data from Brave and Spectre wallets, and files from cloud storage paths like Google Drive, OneDrive, iCloud, Proton Drive, and MEGA.

And, there’s also a remote code execution feature, which allows attackers to shift from passive, automated data theft to live, hands-on keyboard invasions inside the compromised network. All stolen data is encrypted and exfiltrated to C2 servers at vents.msft23.com, events.ms709.com, and mo2307.com.

Over 30 other fake domains targeting tools like Node.js, Chocolatey, KeePassXC, WinSCP, Cyberduck, and Putty are also run by hackers, and they even used a stolen Extended Validation (EV) certificate from Shenzhen Xingzhongxing Electronic Technology Co., Ltd. to bypass Windows security warnings. With these fake sites ranking so high on search engines, developers need to double-check their download sources instead of just trusting the top web results.
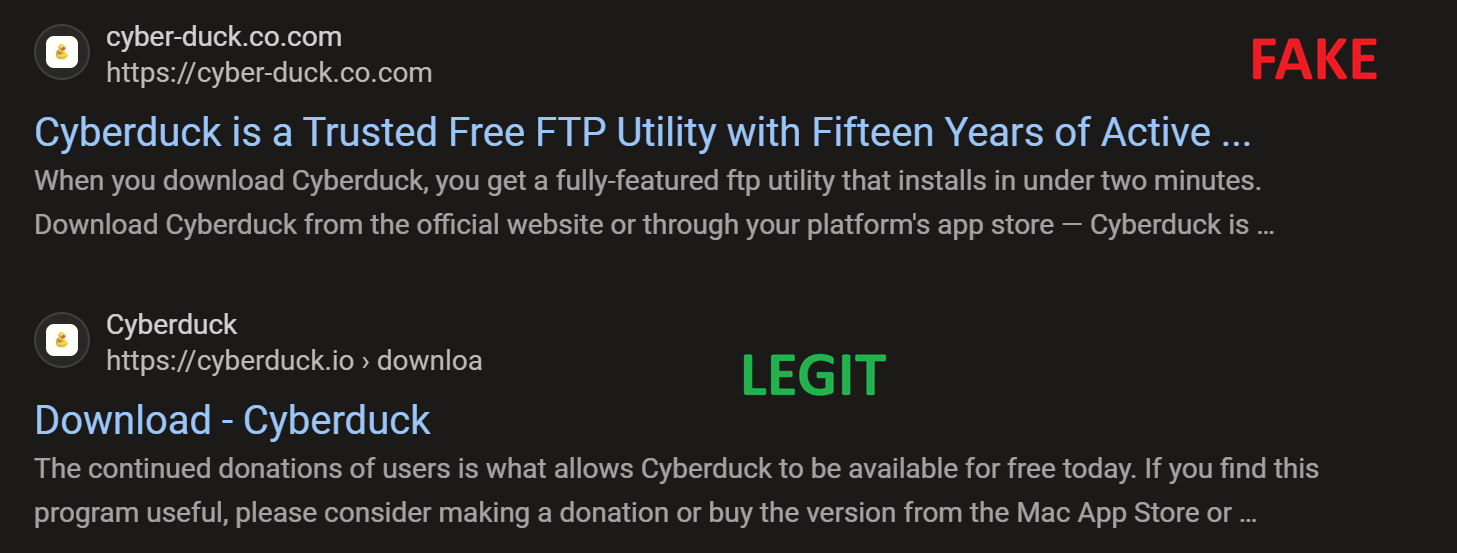
Source: @g0njxa on X

If you are a developer or downloading an AI tool, download it only from official websites. Do not trust look-alike domain names, and scan any downloaded files with VirusTotal before executing or installing them on your device.