





A group of Chrome extensions offering live wallpapers has been linked to a large ad monetization and traffic attribution scheme, according to new research from Socket’s Threat Research Team.
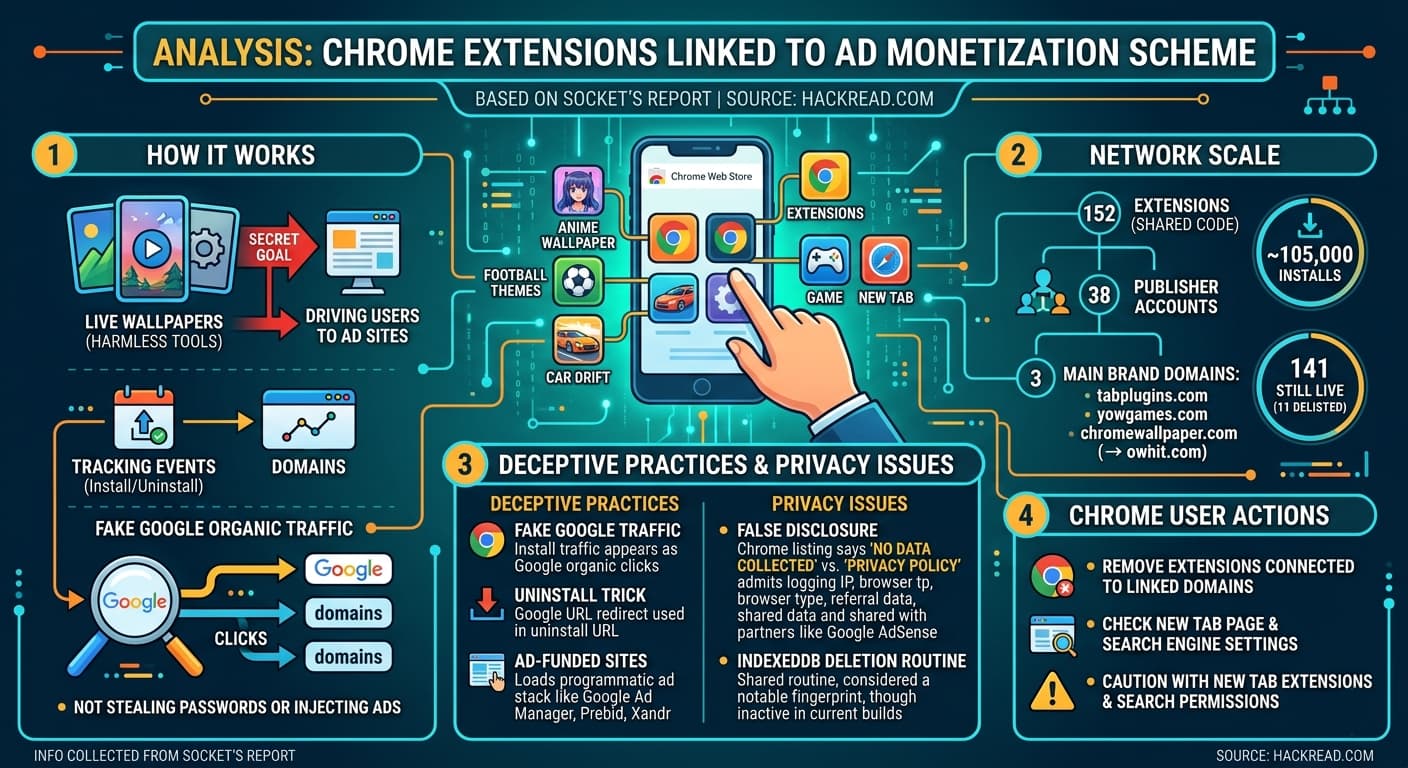
The extensions were marketed as harmless new tab customization tools featuring anime, football, cars, games, and other popular themes. Behind the familiar Chrome Web Store listings, researchers found a shared codebase used by 152 extensions connected to 38 publisher accounts and three main brand domains.
Socket said 141 of the extensions were still live and retrievable from the Chrome Web Store during its analysis, while 11 had already been delisted. Together, the network had about 105,000 reported installs.
The extensions did not steal passwords or inject ads into pages visited by users, according to the research. Their main purpose is to drive users to ad monetized websites, track install and uninstall events, and make extension generated traffic appear as if it came from real Google organic search clicks.
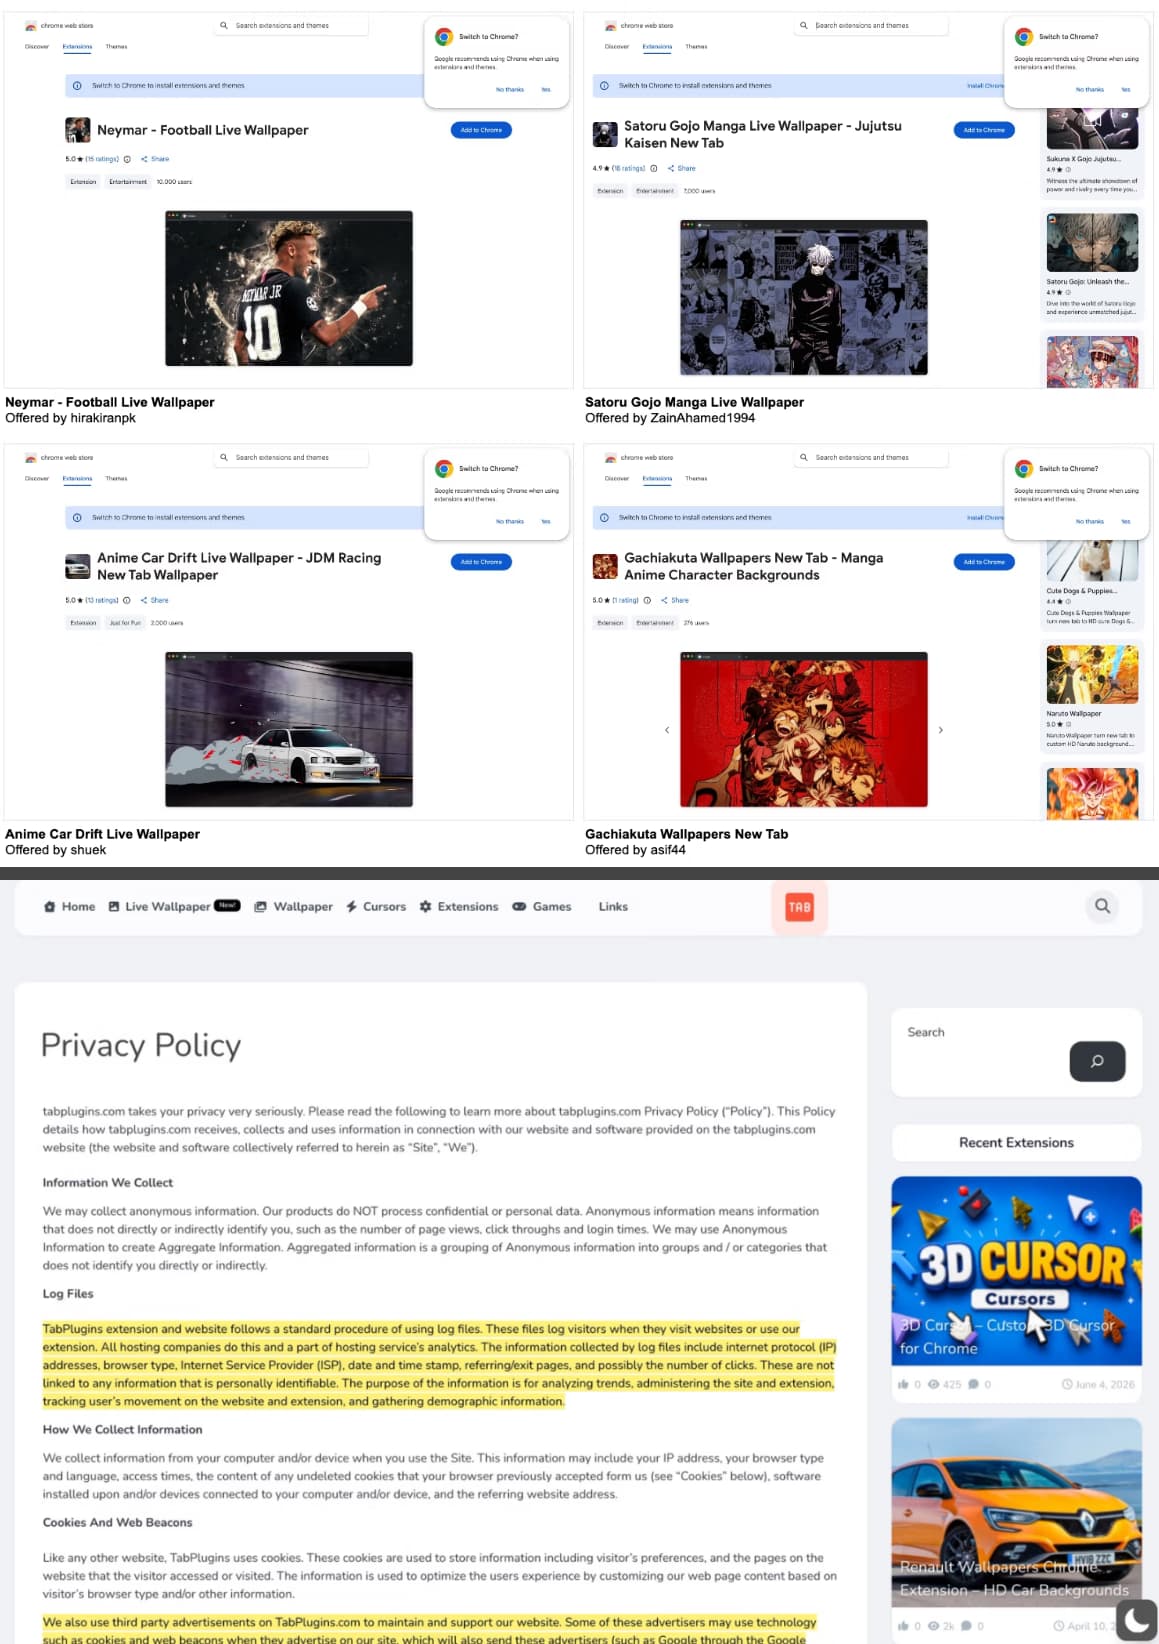
Many of the extensions used names and visuals based on well known topics, including Neymar, Satoru Gojo, Anime Car Drift, Gachiakuta, Hello Kitty, Minecraft, BMW, Naruto, and other entertainment brands. The listings presented them as simple live wallpaper or new tab extensions.
Socket found that the operation was split between three brand backends: tabplugins.com, yowgames.com, and chromewallpaper.com. The chromewallpaper domain redirected users to owhit.com, another domain linked to the same monetization setup.
The most active part of the campaign was connected to tabplugins.com. A subset of 54 extensions using the newer tabplugins template added fake Google organic search attribution to install traffic. When a user installed one of these extensions, the background script opened a tab to the operator’s site with tracking parameters claiming the visit came from Google organic search.
For context, organic search traffic is valuable to publishers, advertisers, and analytics systems. A site receiving visits from Google search may look more trusted and more popular than one sending traffic to itself. In this case, Socket found that the traffic was created by the extension, not by a person searching Google and clicking a result.
The uninstall process used another trick. The extensions set an uninstall URL that wrapped the operator’s site inside a google.com/url redirect format, including Google style tracking parameters. This made an uninstall related visit appear closer to a real Google search result click.
In its blog post, Socket described the behavior as deceptive traffic measurement and adware adjacent activity, not a classic malware infection. The extensions worked as wallpaper tools, but they also pushed users into an advertising funnel and misrepresented how traffic reached the operator’s sites.
The operation also carried a privacy issue. Chrome Web Store listings for the extensions stated that the developer would not collect or use user data. However, the linked privacy policy said something else.
According to Socket, the policy admitted logging IP addresses, browser type, internet service provider, date and time stamps, referrers, click counts, and other data, with sharing involving Google AdSense, DoubleClick, Google Analytics, and third party ad partners.
It is worth noting that Google’s Chrome Web Store rules require privacy disclosures to match an extension’s actual behavior and its published privacy policy. Socket said the same “no data collected” disclosure appeared on all 141 live listings it resolved.
The extensions also included an IndexedDB deletion routine inside the background script. On each service worker start, the code attempted to list and delete databases visible to the extension’s own origin. Socket found that the routine did not delete website data, cookies, sessions, or browsing data because Manifest V3 extension storage is separated by origin.
Still, researchers considered it a notable fingerprint of the family because the same routine appeared in every analyzed extension. In the current build, it appeared inactive in practical terms because the extensions stored their own settings in localStorage, not IndexedDB.
Socket also found signs of rushed mass production. Three tabplugins-based extensions shipped a broken background script because of a syntax error in the install URL. Those extensions are still installed and changed the new tab page, but their background tracking logic failed to run.
The monetization setup was based on sending users to ad-funded sites. The tabplugins domain loaded a programmatic ad stack involving Google Ad Manager, Prebid, AppNexus or Xandr, PixFuture, SmileWanted, Google Analytics 4, and other ad-related services. Socket also found Google AdSense and Google Analytics use on the yowgames and owhit domains through archived pages.
The researchers did not attribute the operation to a confirmed country or real world person. They noted some public contact details and names that could suggest a Turkish connection, but said those clues were not enough for firm attribution.
Nevertheless, remove live wallpaper or new tab extensions connected to tabplugins.com, yowgames.com, chromewallpaper.com, or owhit.com. After removal, users should check that Chrome’s new tab page and default search engine are set to their preferred choices.
Chrome users should also treat new tab extensions with caution, especially when they request search related permissions or route users to outside web pages. A wallpaper extension should not need to play games with Google search attribution or send install and uninstall traffic to ad funded sites.
Socket published indicators of compromise covering publisher accounts, email addresses, domains, advertising IDs, analytics properties, and Chrome extension IDs connected to the operation.
(Photo by Justin Min on Unsplash)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。