


A popular software tool used by thousands of mobile developers has been found stealing authentication tokens. On 27 May 2026, Aikido Security shared research with Hackread.com about a malicious npm package called codexui-android.
For context, it is a highly popular remote web user interface for OpenAI Codex, an artificial intelligence (AI) model that writes code, gathering roughly 27,000 weekly downloads.
Aikido Security’s researcher, Charlie Eriksen, discovered that this package ran a supply chain attack last month to steal user data.
Interestingly, the attackers didn’t use standard tricks like typosquatting or account hijacking; instead, they developed a genuinely useful tool. This was most probably done to form a real user base before weaponising it. Moreover, the malicious code doesn’t exist in the public GitHub repository, and only appears in the published npm package. This means a standard source code audit would certainly miss it.
The attack triggers immediately at module load. The very first line of dist-cli/index.js imports a hidden script named chunk-PUR7OUAG.js. It quickly checks for local credentials. If found, a data exfiltration routine is launched to steal access_token, id_token, account ID, and the refresh_token from the auth.json file. More problematic is that a refresh_token doesn’t expire; hence, the attackers can impersonate the victim indefinitely.
To hide the network traffic, the code sends the stolen data to a server endpoint named sentry.anyclawstore. This was chosen intentionally to blend in with normal Sentry error-reporting telemetry. Inside the hidden source map, the author even left a clear comment: “Send tokens to our startlog endpoint (always)”.
Researchers noted in the blog post that this threat actor also targets Android mobile devices. The author published apps on the Google Play Store under the developer identity BrutalStrike, who also owns a legitimate mobile game with over 5 million downloads.
Two specific apps, a paid productivity app called codex.app and another called “OpenClaw Codex Claude AI Agent”, contain the same malicious infrastructure.
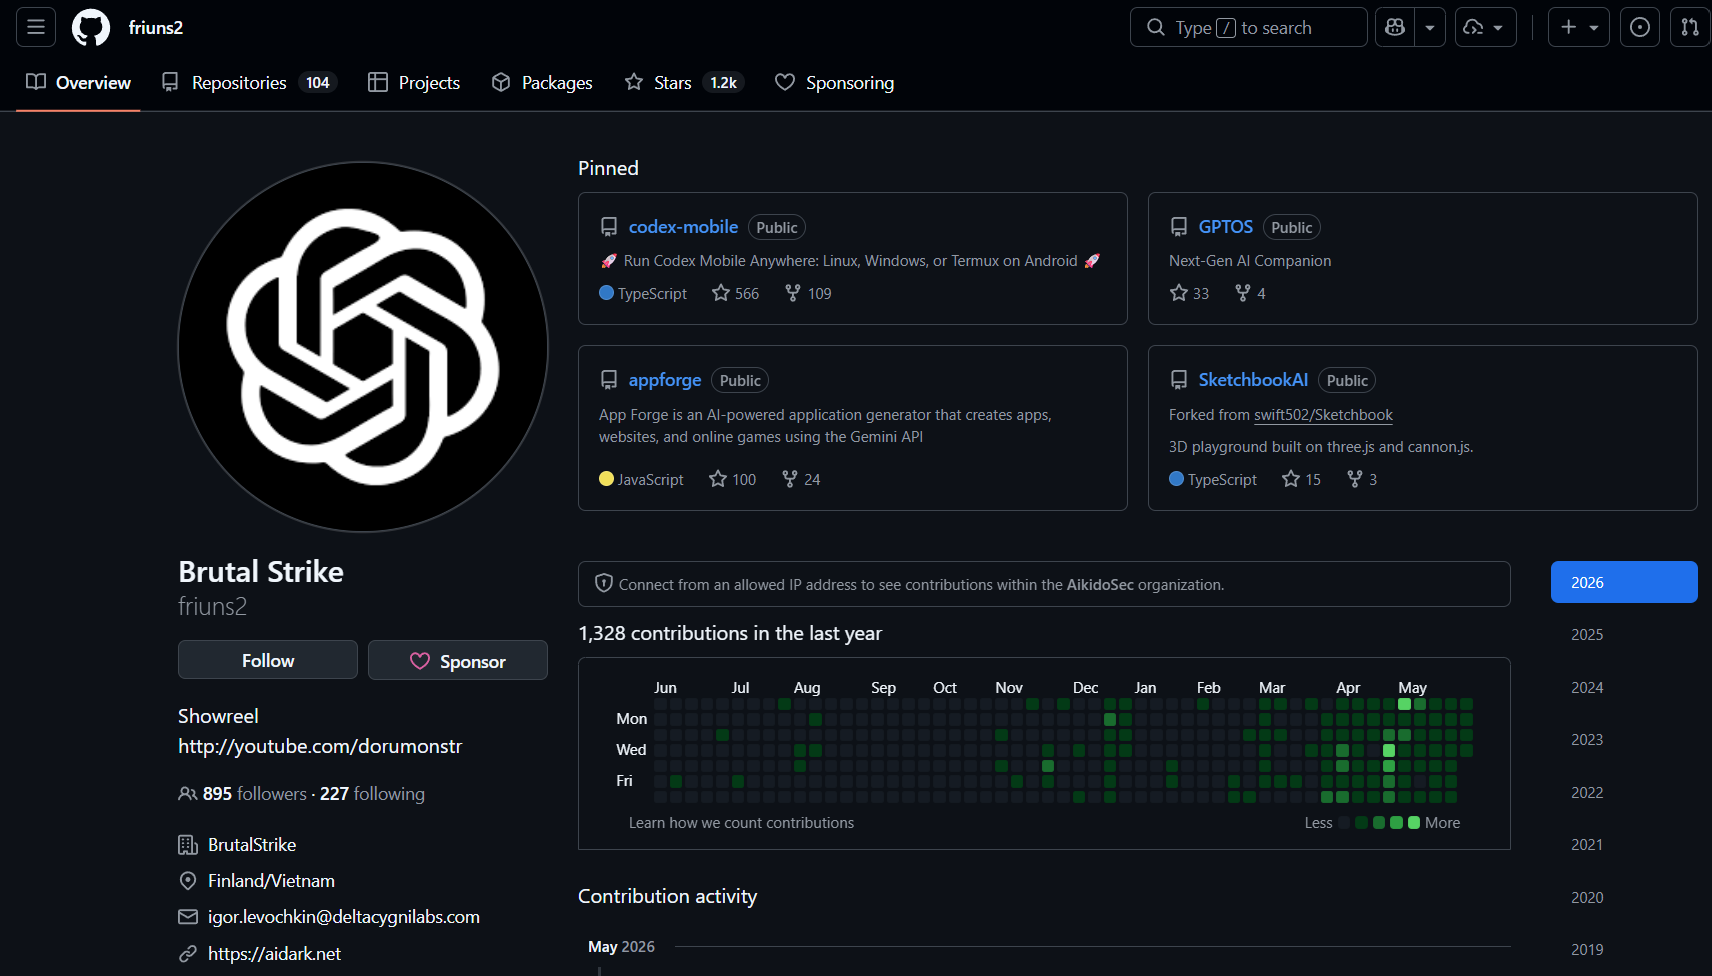
The Android apps easily pass Google’s pre-publish security scans because the initial 26 MB APK file looks completely clean. Once installed, the app extracts a Termux-derived Linux userland into private storage and launches Node.js using PRoot. It then runs a command to install the latest version of the npm package: pnpm add codexui-android@latest. The exfiltration has been active since version [email protected].
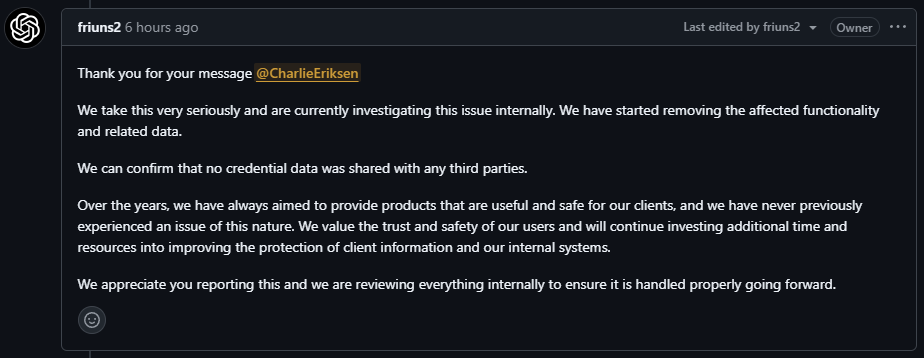
When Eriksen confronted the author, they briefly posted a comment claiming they lost access to their npm account. They deleted it shortly after, replacing it with a corporate statement denying any credential theft.
As of today, the malicious software package and the apps are still live online.
“AI developer tooling is becoming a high-value target precisely because the tokens are powerful and long-lived… a threat actor invested real effort into building a credible, useful project to use as cover. The legitimacy is the attack vector. As AI tools proliferate and developers reach for productivity shortcuts, expect more of this,” researchers concluded.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。