


LastPass has confirmed it was affected by the Klue supply chain incident, saying an unauthorised actor used stolen OAuth tokens from the third-party market intelligence platform to access customer data stored in its Salesforce environment.
The company said it learned of the Klue incident on June 12, 2026, after Klue, a market intelligence platform used by LastPass go-to-market teams, notified customers about unauthorised activity. Klue integrates with business tools, including Salesforce and Gong, which made the stolen tokens valuable because they could be used to reach connected customer systems without needing normal login credentials.
According to LastPass, the exposed data was limited to customer relationship management information inside Salesforce. This included customer names, phone numbers, email addresses, physical addresses, support case data, and sales-related records. The company said LastPass products, services, infrastructure, and customer vaults were not affected.
The incident follows earlier reporting that Salesforce disabled Klue Battlecards’ integration infrastructure on June 17, 2026, after detecting unusual activity involving the app’s connection to Salesforce. Salesforce said the issue was limited to Klue’s app connection and did not come from a vulnerability in the Salesforce platform itself.
The Klue incident has already been linked to data theft from several companies using the platform. The group behind these attacks is a new extortion group named Icarus, after it gained access to Klue’s backend systems, pushed a malicious code update, and harvested OAuth tokens used by customer integrations. Those tokens were then used to query Salesforce environments and copy CRM data.
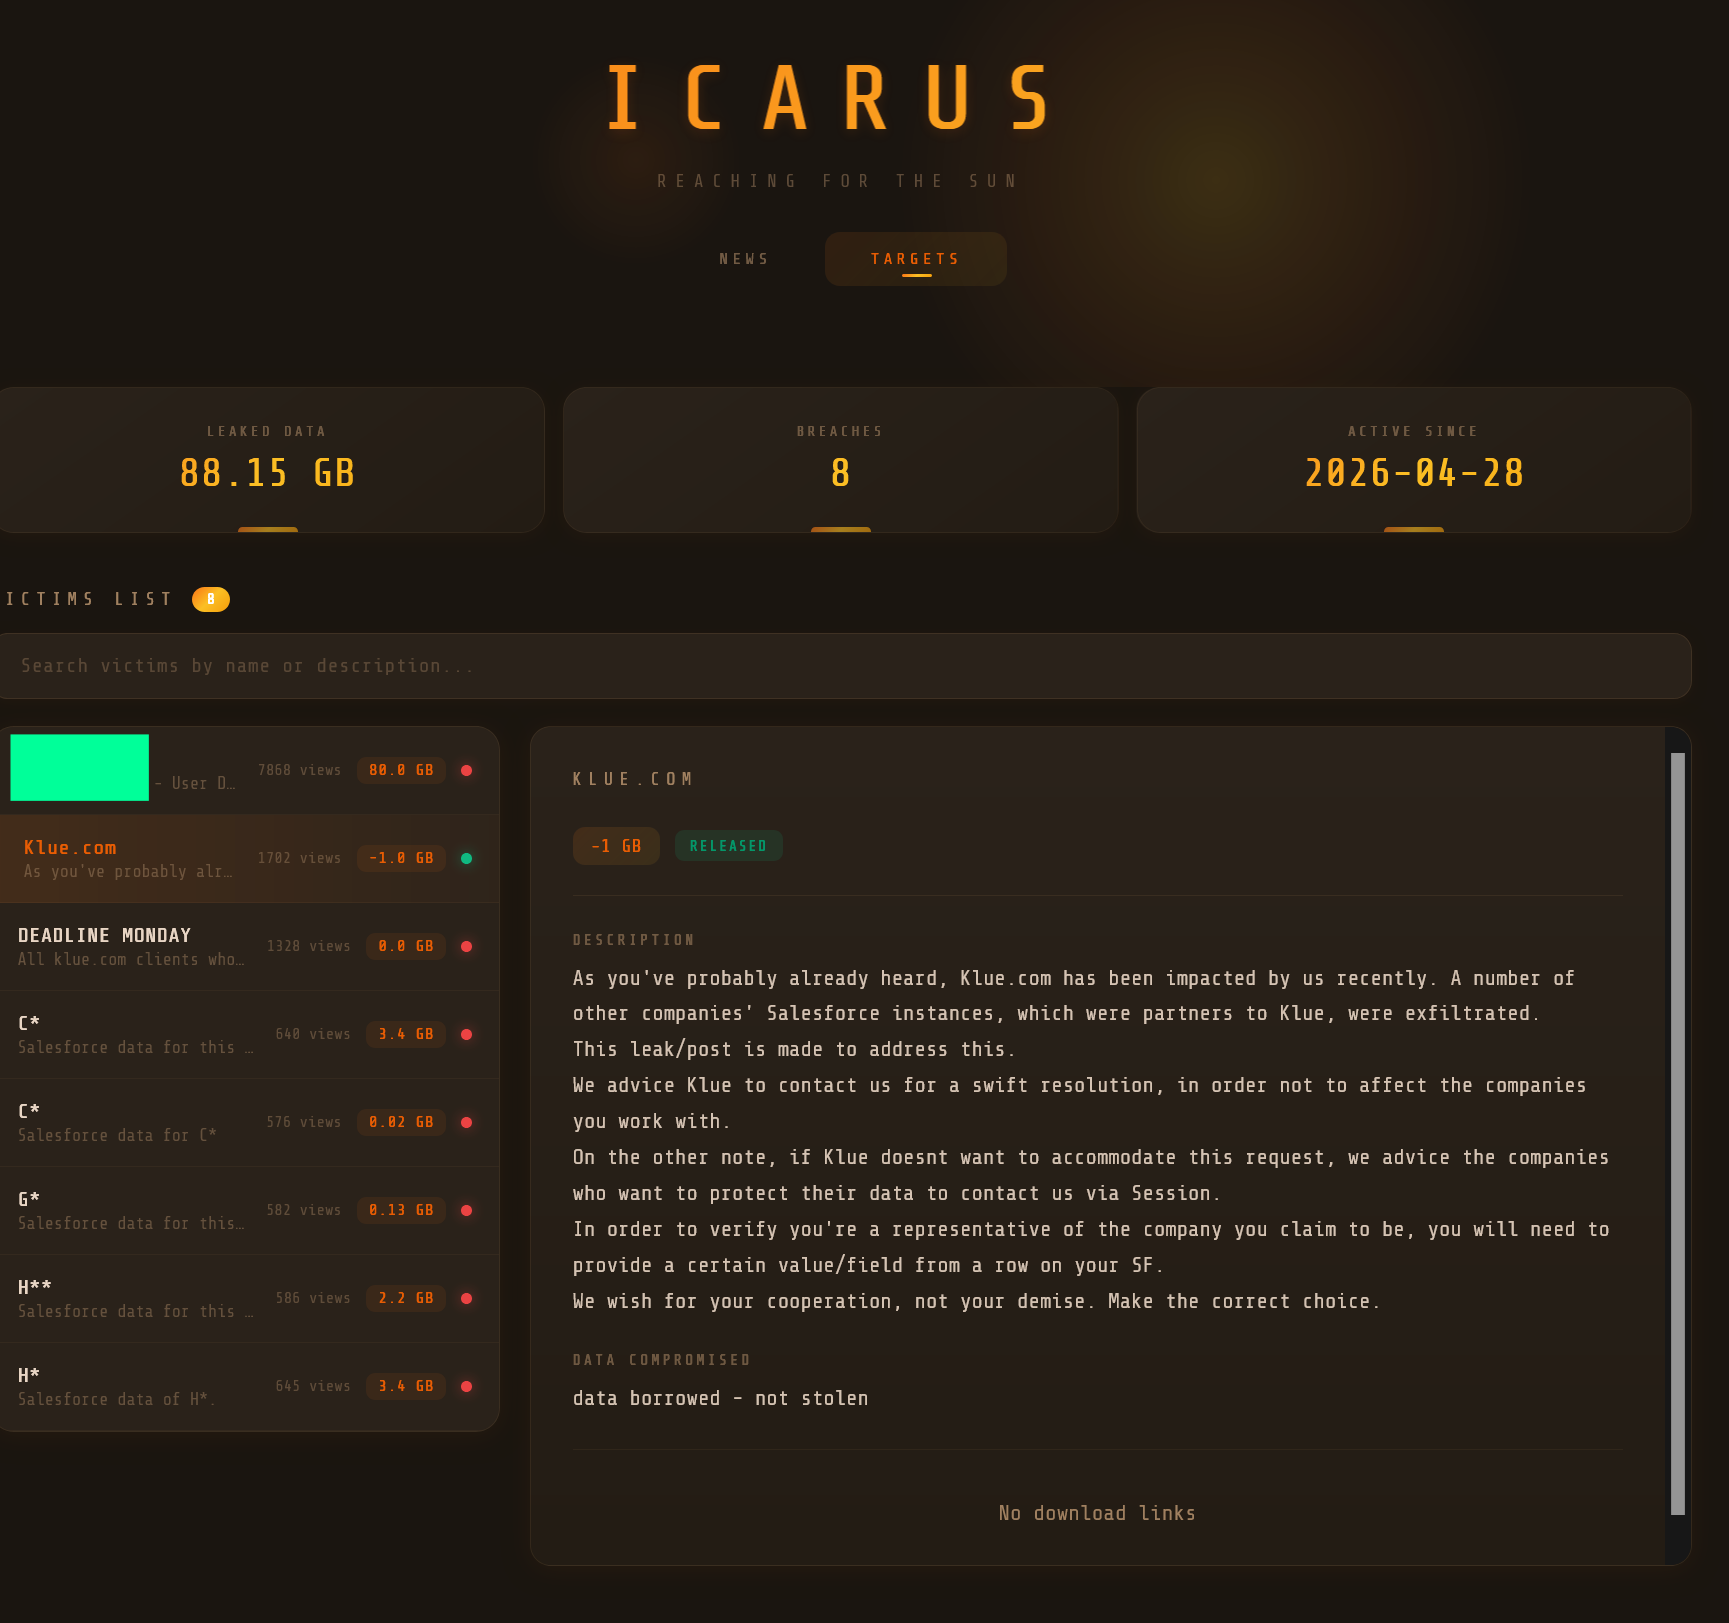
OAuth tokens are designed to let connected applications share information without asking users to log in repeatedly. That convenience also creates risk when a third-party service holding those tokens is compromised, because attackers may be able to access connected systems until the tokens are revoked or rotated.
LastPass said it has completed remediation and rotated the exposed Klue OAuth tokens. The company also discontinued employee access to Klue, launched an investigation with Klue and Salesforce, and notified law enforcement. Its ongoing response includes sharing technical details with the security community and adding safeguards to reduce the chance of similar incidents.
For customers, LastPass advised caution around phishing and social engineering attempts, since exposed contact details and CRM records can be used to make scams look more credible. The company also reminded users that LastPass staff will never ask for a master password and that official support communication should come through trusted LastPass channels.
The company published indicators of compromise connected to the incident, including IP addresses and email sender domains. Those details are meant to help organisations review logs and spot activity linked to the Klue campaign.
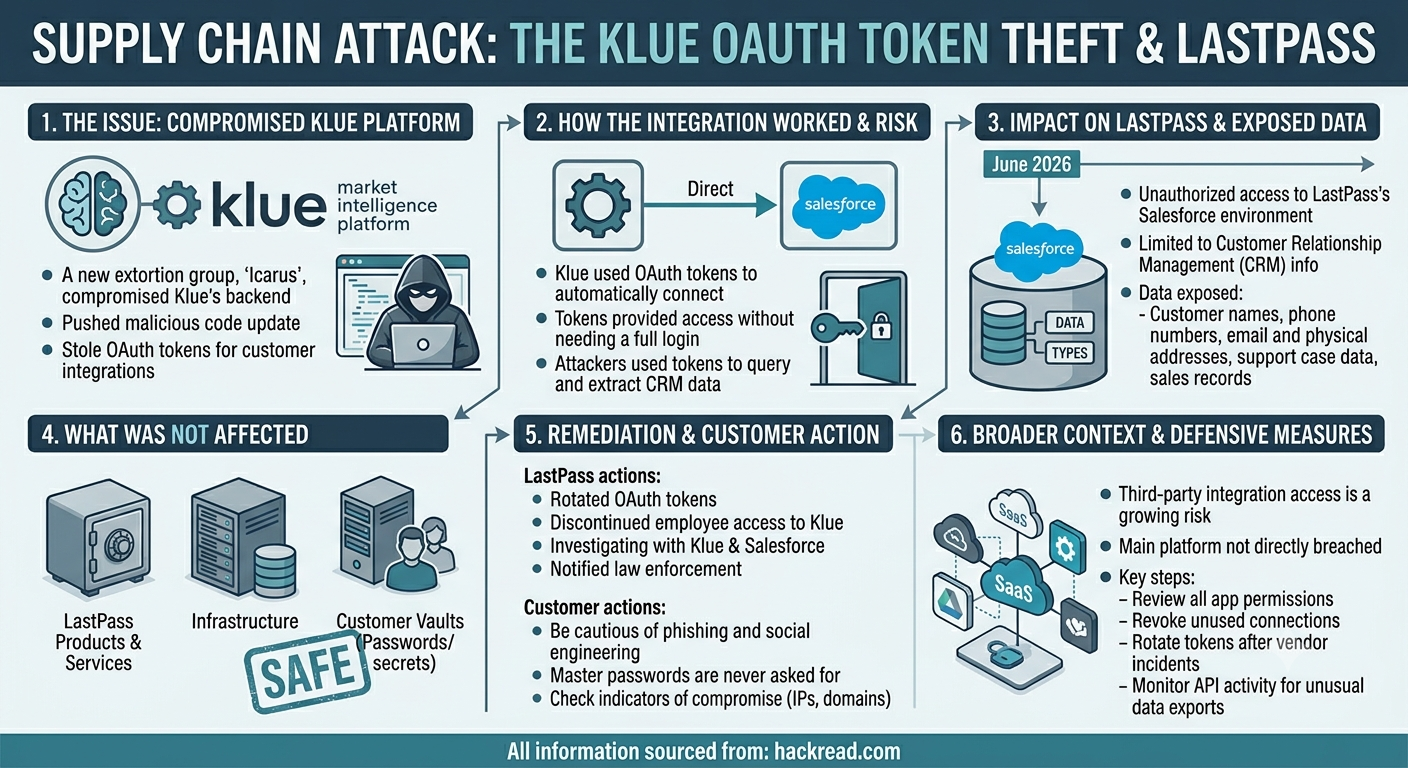
The Klue case adds to a run of incidents where attackers abused third-party application access to reach Salesforce data. In earlier cases, compromised app tokens and integrations were used to pull large volumes of CRM information from customer environments. These incidents show how SaaS connections can become an entry point even when the main platform is not directly breached.
If your company is using integrated sales and marketing tools, the LastPass disclosure is a prime example to review which apps have access to CRM data, revoke unused connections, rotate tokens after vendor incidents, and monitor API activity for unusual data exports.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。