


A newly discovered remote access Trojan (RAT) called Backdoor.Mistic (Mistic backdoor), tracked by Zscaler as MLTBackdoor, is helping hackers infiltrate corporate networks. Detected in April 2026, this RAT is used by a specific group to set up hidden entry points inside businesses. Instead of disrupting systems themselves, these actors operate as brokers, selling network access to major ransomware operations.
Security firms like Broadcom’s Symantec team, Carbon Black, Zscaler, and ThaiCert have been tracking this activity. They linked the campaign to a group active since May 2024 known as Woodgnat hackers (aka KongTuke).
Woodgnat hackers, who also deploy a tool called ModeloRAT, act as a middleman for ransomware networks like Qilin, Interlock, Rhysida, Akira, 8Base, and Black Basta. The group hits schools, insurance firms, and IT services at random just to find any opportunity to profit.
To compromise a system, the hackers rely heavily on tricking regular employees. They hijack normal WordPress websites to push fake technical alerts. In a recent tactic from early 2026 called CrashFix, they purposely froze a victim’s web browser and displayed a message telling them to copy-paste a command to fix the issue.
Similar browser tricks were used by these actors in 2025 under the names ClickFix and FileFix. From April 2026, they have also started messaging staff directly on Microsoft Teams, posing as the company’s IT helpdesk to lure workers into running malicious commands.
Once an employee falls for the trick, a multi-stage PowerShell chain downloads the malware. The hackers install Backdoor.Mistic, which lets them manage files and even display fake login screens to steal passwords. Afterward, they use built-in Windows tools like Net.exe and Reg.exe to map out the network, and Curl to transfer data out.
What makes this RAT more dangerous is its excellent hiding mechanism relying on a technique called DLL sideloading. This involves abusing trusted Windows files to trick security software into running the backdoor.
Apart from this, it runs entirely in the computer’s temporary memory without saving files to the hard drive, which makes it hard for antivirus programs to spot it. If the scammers think they may get caught, they use a built-in kill switch to make the malware delete itself instantly.
With such quiet tools to compromise networks readily available to cybercriminals, companies need to closely monitor for unexpected IT support messages or strange computer commands before hackers can sell off their network access.
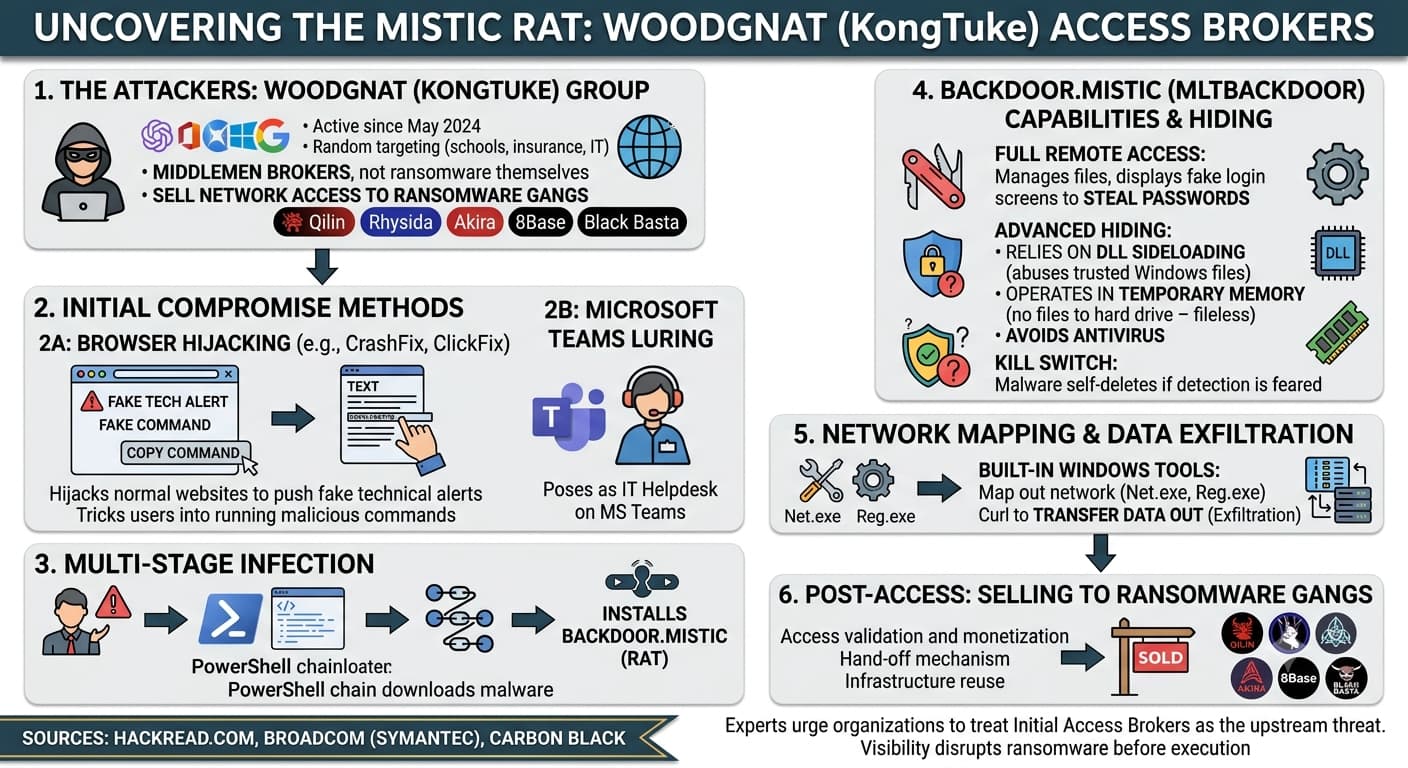
Experts say this threat highlights how organised the online underworld has become. In comments shared with Hackread.com, Roman Sannikov, Global Research Coordinator at iCOUNTER, noted that the emergence of Mistic shows the continued industrialization of the cybercrime ecosystem. He explained that initial access brokers have become critical suppliers, specializing in finding, validating, and monetizing access.
“The C2 patterns, hosting choices, and staging behavior that Woodgnat hackers use to maintain and sell access tend to be more consistent across engagements than the downstream operators who purchase it. Defenders focused only on the ransomware payload are looking at the wrong layer. The access infrastructure is upstream of the incident, and visibility into how brokers like this operate, their routing, their reuse patterns, their handoff mechanisms, is what allows defenders to detect and disrupt before the ransomware operator ever enters the environment,” Sannikov stated.
Josh Picolet, VP of Detection & Analysis at Team Cymru, also shared his perspective with Hackread.com, explaining that defenders who only focus on the final ransomware payload are looking at the wrong layer.
According to Picolet, the infrastructure connecting these groups is the most durable intelligence target. He stated, “The access infrastructure is upstream of the incident, and visibility into how brokers like this operate, their routing, their reuse patterns, their handoff mechanisms, is what allows defenders to detect and disrupt before the ransomware operator ever enters the environment.”
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。