








Australia joins alliance members to warn of the need for swift action to “remain ahead" of AI risk, as one expert warns this is a problem we cannot patch our way out of.
Representatives of the leading Five Eyes cyber security agencies have warned that governments and businesses need to act swiftly if they wish to remain ahead of the looming threat of cyber risks supercharged by rapidly evolving artificial intelligence.
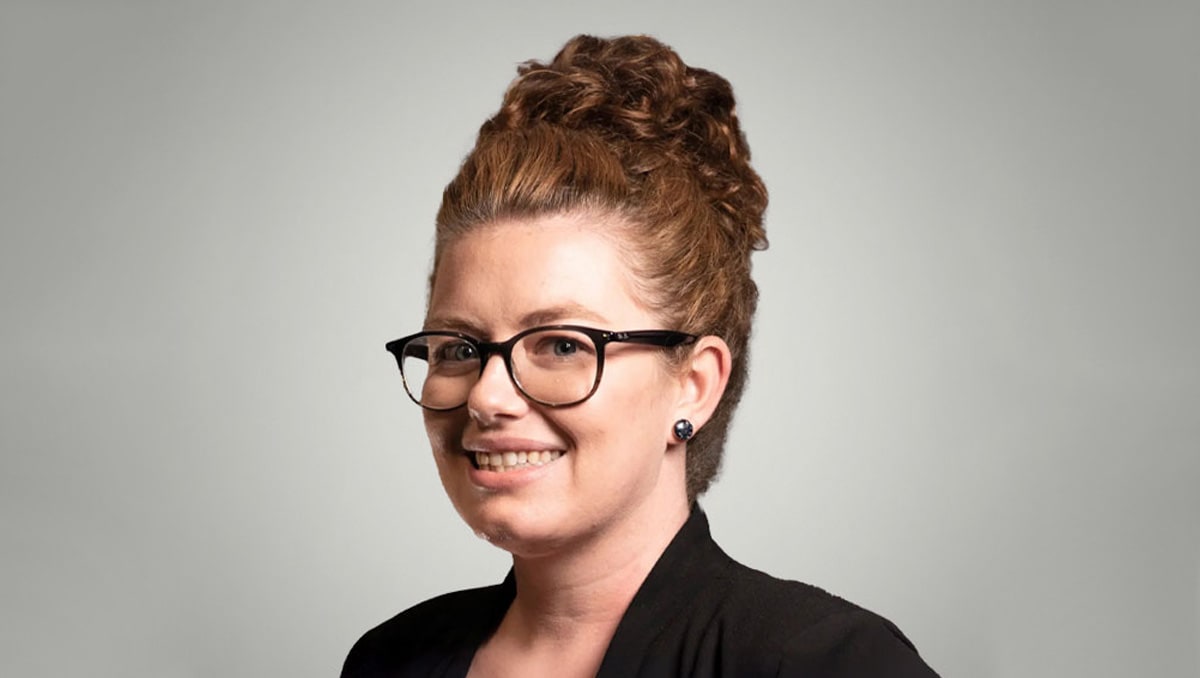
In a call to action released on June 22, titled “The AI shift in cyber risk: why leaders must act now,” Stephanie Crowe (pictured), the head of the Australian Cyber Security Centre
Australian Signals Directorate, joined leaders from the Canadian Centre for Cyber Security, the UK’s National Cyber Security Centre, the United States’ National Security Agency & Cybersecurity and Infrastructure Security Agency to say that while AI is a boon to network defenders, it is also a force multiplier for the speed and scale of cyber threats.
You’re out of free articles for this month
To continue reading the rest of this article, please log in.
“AI is not a future consideration – it is already here,” the leaders said.
“It lowers barriers for malicious actors and increases the speed and complexity of attacks, shrinking the window between vulnerability discovery and exploitation ever more quickly. At the same time, AI offers powerful tools to strengthen defence.”
According to the Five Eyes call to action, organisations must be aware of the risks they face in the current landscape, be accountable, make foundational cyber security practices a priority, give cyber leaders the authority they need to act, and stay engaged with emerging threats and guidance.
Like many in the industry, the Five Eyes agencies said that cyber risk can not be considered a technical issue, but rather a core bore business risk and the responsibility of business leaders.
“Boards and executives should ensure cyber resilience is in place and works under pressure. It is not enough to have controls. Leaders must be confident those controls will perform during a real incident,” the call to action said.
“This requires reassessing long-standing trade-offs and using AI deliberately to strengthen defence – not just improve efficiency.”
The core principles leaders need to adopt are secure-by-design & secure by default standards, defence-in-depth, and an understanding that AI will contribute to a rise in zero-day vulnerabilities.
In addition, the agency representatives listed five key, practical actions for organisations to follow urgently:
- Reduce your attack surface by eliminating unnecessary access paths, limiting external connectivity, and isolating systems that do not need to be exposed.
- Accelerate patching efforts, as AI-driven threats are shrinking the window between vulnerability disclosure and exploitation, making delays increasingly risky.
- Address legacy systems proactively, as unsupported technologies represent strategic liabilities that attackers can readily exploit.
- Strengthen identity and access management by enforcing strong authentication, restricting access to critical systems, and regularly reviewing user permissions.
- Prepare for incidents in advance by testing response plans, training teams, and focusing on rapid containment and recovery when breaches occur.
While AI may be a threat driver, the agencies said, it is, however, still a vital tool in network defence, and defenders must be able to move as quickly as their adversaries.
“Organisations that integrate AI tools into their security operations can detect vulnerabilities earlier, improve software quality, monitor unusual behaviour, and respond faster to incidents – reducing both the cost and impact of incidents,” the call to action said.
“Success will not come from having the most tools. It will come from getting the basics right, acting quickly, and integrating cyber security into core business strategy.”
Speaking to the urgency of the Five Eyes statement, Gary Barlet, Public Sector CTO at cyber security firm Illumio, said the idea that advanced models such as Anthropic’s Mythos would be a cyber silver bullet were “wishful thinking”.
“Whether it's Mythos, Fable, or the next frontier model, it isn't a matter of if these capabilities become widely available; it's when,” Barlet said.
“The Five Eyes warning is a wake-up call that AI is about to dramatically accelerate the speed, scale, and sophistication of cyberattacks, lowering barriers for adversaries and giving them capabilities that were once limited to highly skilled actors."
What concerns Barlet most, however, is the common attitude that organisations can “patch their way out of the problem”.
"We couldn't keep up before AI, and we certainly won't keep up after it. Attackers have always had the upper hand because they don't operate under the same constraints as defenders, and that's even more true in the age of AI,” Barlet said.
“It's time for organisations to stop treating a breach as a possibility and start treating it as an inevitability."
 Want to see more stories from trusted news sources?
Make Cyber Daily a preferred news source on Google.

David Hollingworth
David Hollingworth has been writing about technology for over 20 years, and has worked for a range of print and online titles in his career. He is enjoying getting to grips with cyber security, especially when it lets him talk about Lego.