


Threat actors have claimed a cyber attack on a Queensland-based chain of pharmacies, threatening to leak staff and patient data.
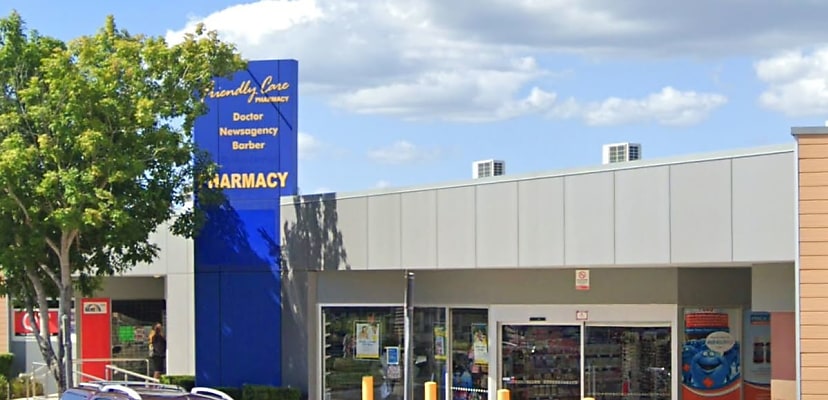
With seven locations, FriendlyCare Pharmacy provides pharmaceutical services to the state of Queensland, including over and under the counter medication, beauty, general health advice, personal care and more.
The company was listed on the dark web leak site of the Kairos ransomware group overnight, which claimed to have stolen 113 gigabytes of data.
You’re out of free articles for this month
To continue reading the rest of this article, please log in.
The group posted a data sample, which contains medical details, including scripts, an incident report, employment detail correspondence and a licence, all of which contain personal details, including names, medical information and more. The data also seems to pertain to the Booval location.
At the time of writing, Kairos said it will publish the data in just over six days.
Without request, Kairos reached out to Cyber Daily to outline the incident, once again acting like penetration testers without any malicious intent and accusing the victim of hiding the incident.
“FriendlyCare Pharmacy (Booval QLD 4304) has suffered a data breach,” Kairos told Cyber Daily.
“In six days, all downloaded data will be published on the internet.
“FriendlyCare Pharmacy is currently keeping quiet about the data leak. We believe that people should know about what has happened.”
Cyber Daily reached out to FriendlyCare for comment and is currently awaiting a response.
Who is Kairos?
According to threat intelligence firm CYJAX, Kairos is active on several Russian-language hacking forums and does not appear to be linked to other hacking groups.
The group provides some information on its operations on its leak site, however. According to Kairos, victims are initially given seven days to respond to its demands, and once that deadline is passed, the gang publishes its initial leak post.
“If no agreement is reached within seven days, we will publish the fact of the data compromise on our website,” Kairos said.
“If the situation remains unresolved after seven days, we will notify your partners, competitors, and customers and then publish your data in full. This could lead to legal actions, termination of contracts, reputational damage, stock value drops, and potential closure of your organisation.”
Kairos was first observed in November 2024 and the gang has claimed at least 79 victims since then. Its most recent Australian victim was Seagrass Boutique Hospitality Group, which it claimed responsibility for on 12 February 2026.
 Want to see more stories from trusted news sources?
Make Cyber Daily a preferred news source on Google.

Daniel Croft
Born in the heart of Western Sydney, Daniel Croft is a passionate journalist with an understanding for and experience writing in the technology space. Having studied at Macquarie University, he joined Momentum Media in 2022, writing across a number of publications including Australian Aviation, Cyber Security Connect and Defence Connect. Outside of writing, Daniel has a keen interest in music, and spends his time playing in bands around Sydney.