





Threat actors have claimed a cyber attack on a Victoria-based RV dealer, allegedly having stolen data.
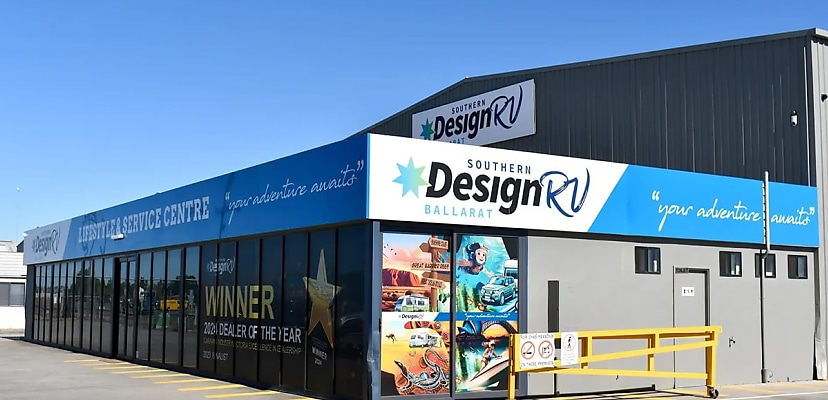
Southern Design RV is a Ballarat, Victoria-based caravan and RV dealer that sells both new and used Australian-made caravans. It also services, repairs and upgrades existing RVs.
The company was listed by a new cyber crime entity calling itself the CMD Organization, which claimed to have exfiltrated data from Southern Design RV.
You’re out of free articles for this month
To continue reading the rest of this article, please log in.
While they did not outline the nature of the incident nor what data it claims to have stolen, it provided a data sample in the listing, which included customer documentation containing names, addresses, emails, phone numbers and details surrounding the purchase of caravans.
CMD Organization has set up an auction for the sale of the data, which is at 5 bitcoin at the time of writing, and is due to expire in just over five days at the time of writing.
Cyber Daily reached out to Southern Design RV for more information, however, they declined to comment on the incident.
Who is CMD Organization?
CMD Organization is a new player on the cyber criminal scene, having been first observed just last month. At the time, it had eight victims but now has a total of 19 listed.
One of those groups was Tasmania hospitality company Goodstone Group, which confirmed it was aware of the incident at the time and said it was in the process of responding to the cyber attack.
The group advertises itself as a legitimate service and company, as do many groups of its kind.
“CMD is a new kind of company that specialises in corporate system security and in identifying vulnerabilities across all aspects of the software used by a company. CMD operates on a global scale recognising the critical importance of timeliness and confidentiality,” the group said on its leak site.
“Our mission is to create a secure online environment where every company is safely protected and immune to user data breaches.”
According to cyber security firm Beazley Security, CMD Organization operations began in March and its tradecraft suggests a “potentially well-networked operator but with limited operational maturity, possibly leveraging initial access brokers (IABs) and limited original tooling”.
One of the group’s unique tactics is allowing anyone to bid on stolen data offered on its website, potentially driving up the price for victims to secure their data.
“If CMD Organization can shift part of the traditional ransom and extortion process away from private negotiations to public bidding opportunities, selling exclusive access to stolen data could increase the price according to the given demand of an actor,” Beazley Security said in a 14 May blog post.
“Locking the sale to a single buyer could empower the winner with exclusive access to the stolen data, giving time to sift through and operationalise credentials, identities, customer records, or other sensitive information before it is circulated to competing threat actors.”
 Want to see more stories from trusted news sources?
Make Cyber Daily a preferred news source on Google.

Daniel Croft
Born in the heart of Western Sydney, Daniel Croft is a passionate journalist with an understanding for and experience writing in the technology space. Having studied at Macquarie University, he joined Momentum Media in 2022, writing across a number of publications including Australian Aviation, Cyber Security Connect and Defence Connect. Outside of writing, Daniel has a keen interest in music, and spends his time playing in bands around Sydney.