
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

人人都是产品经理
人人都是产品经理
有赞技术团队
有赞技术团队
WordPress大学
WordPress大学
月光博客
月光博客
T
Tailwind CSS Blog
阮一峰的网络日志
阮一峰的网络日志
小众软件
小众软件
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
Last Week in AI
Last Week in AI
大猫的无限游戏
大猫的无限游戏
S
SegmentFault 最新的问题
罗磊的独立博客
Jina AI
Jina AI
酷 壳 – CoolShell
酷 壳 – CoolShell
宝玉的分享
宝玉的分享
让小产品的独立变现更简单 - ezindie.com
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
博客园 - 三生石上(FineUI控件)
量子位
雷峰网
雷峰网
Apple Machine Learning Research
美团技术团队
博客园 - 聂微东
V
V2EX

Unit 42

Unmasking Cloud Identities: From Behavioral Clustering to Automated Detection The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams Perturbation Probing: A New Diagnostic for the Fragility of LLM Safety The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution Connecting the Dots: Securing the Overlooked Corners of the Software Development Lifecycle (SDLC) Supply Chain Identity Abuse Through Trusted Communication Channels Kimwolf v7: An Evolution of the Kimwolf Botnet The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications Inside the Modern SOC: The Identity Front Door ChainDrop: Inside a Self-Propagating npm Worm Token Jacking: Cybercriminals Could Be Stealing Your AI Resources The Frontier AI Vulnerability Burst: Industrializing Autonomous Zero-Day Discovery in Open-Source Software Almost Half of Malware Samples Communicate Direct to IP Pass the Passkey: A Novel Attack Surface in Passwordless Authentication The Xcode Assassin Returns: A Deep Dive Into the Latest XCSSET Version Chinese-Speaking Threat Actor Harnesses AI Models for Autonomous Cyberattacks Russian Global Webmail Espionage Three Steps to the Terminal: A Siemens ROX II Zero-Day Trilogy AI, Automation and Attacks: Unpacking the Unit 42 2026 Global Incident Response Report AI, Automation and Attacks: Unpacking the Unit 42 2026 Global Incident Response Report TuxBot v3: Inside an IoT Botnet Framework With LLM-Assisted Development No Manners Here: The Ruthless Rise of The Gentlemen Ransomware Vidar Stealer Unmasked: Code Signing Abuse, Go Loaders and File Inflation How We Added WebAuthn to a Browser-Based RDP Client Phantom Squatting: AI-Hallucinated Domains as a Software Supply Chain Vector CL-STA-1062 Targets Southeast Asian Governments and Critical Infrastructure OpenClaw’s Skill Marketplace and the Emerging AI Supply Chain Threat
An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation
Renzon Cruz, Nicolas Bareil, Eric Semaan, Omar Jbari · 2026-09-02 · via Unit 42

Unit 42 responded to an incident where a human attacker used frontier AI to breach an enterprise network autonomously as part of a ransomware attack. The agents breached the company's security layers in a methodical manner, each targeting a different layer of defense to achieve a shared goal. The impact was at the scale of a coordinated effort from multiple red teams, which would normally take human operators around two weeks.

The threat actor told us in negotiations that they leveraged frontier AI models and attack-specific agentic AI frameworks. By shifting execution to an automated loop, the attacker compressed weeks of methodical intrusion tradecraft (using more than 50 MITRE ATT&CK techniques) into less than 10 hours.

After they gained initial access, the attacker used agents to map the internal architecture, raid source repositories and seize root credentials. The agents also triggered unauthorized continuous integration/continuous delivery (CI/CD) builds and claimed master keys to the victim's cloud AI infrastructure.

What made the attack stand out was AI-assisted operational efficiency, without the need for a novel zero-day or super elite tradecraft. The attacker left tactical execution to AI agents that monitored, evaluated, acted and re-planned in real time, increasing speed throughout the attack chain.

The attacker also directed the agent to leave behind a “report” on the organization’s security posture: an 80-page, technical audit detailing dozens of exploited findings.

Inside the Machine-Speed Attack Chain

The adversary ran their operation using current AI-enabled software development processes. We observed multiple indicators consistent with AI usage:

  • LLM calls to multiple frontier AI agents in parallel
  • Structured Markdown files passing information between agents and sessions
  • Custom scripts (assessed with high confidence to be AI-generated due to UI elements) managing dynamic operations

The 10-hour operational timeline included the following:

  • Infiltration and mapping: The actor breached a public API endpoint to tunnel into the network, deploying an automated recon agent to map internal microservices.
  • Secrets harvesting: Sub-agents combed enterprise code repositories, extracting hard-coded tokens and service passwords.
  • Privilege takeover: Using exposed tokens, the actor infiltrated the secrets management system, harvesting master administrative credentials to seize control of root system access.
  • Pipeline exploitation: The actor hijacked an enterprise code application via custom workflows to exfiltrate cloud access keys. They attempted to plant backdoors in Terraform configurations, but hard branch-protection controls stopped this.
  • AI infrastructure hijacking: Using stolen cloud keys, the actor turned the victim’s AI endpoints into post-compromise infrastructure — using the company’s compute power to perpetrate future moves.

Figure 1 maps the AI-orchestrated workflow.
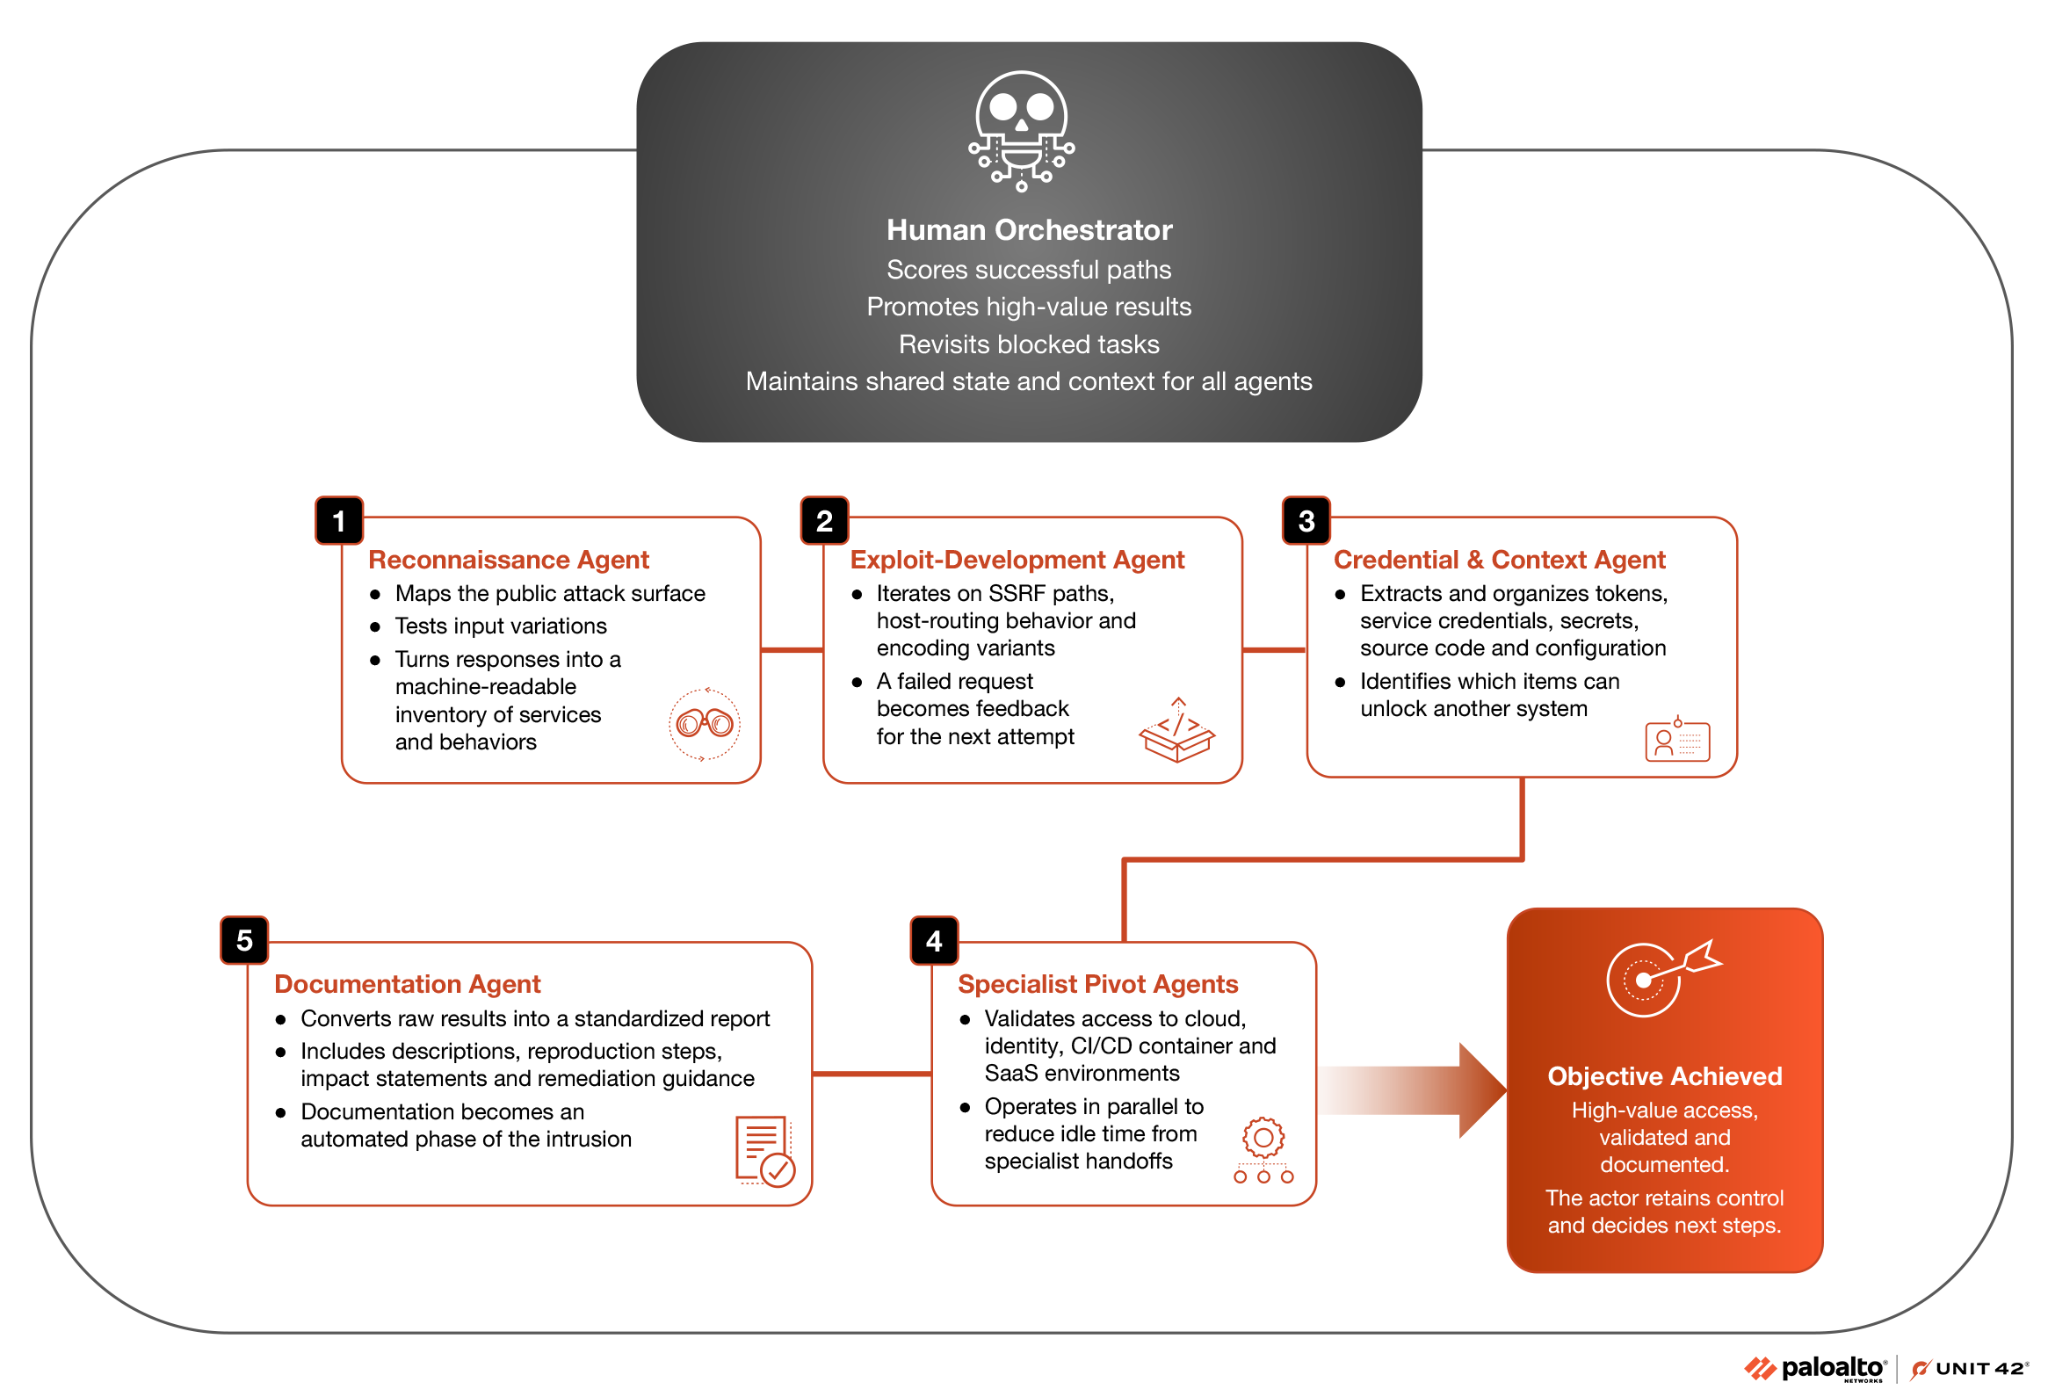
Figure 1. AI-orchestrated intrusion workflow. The actor sets objectives and makes consequential decisions. Specialized agents execute, share results and adapt in real time.

Unified Threat Framework Mapping

For illustration, Table 1 below maps some of the techniques used against the MITRE ATT&CK and ATLAS frameworks:

Intrusion Stage Threat Actor Action MITRE ATT&CK® Mapping MITRE ATLAS™ (AI-Specific) Mapping
Initial Access and Recon API breach; automated service mapping via service discovery tool T1190: Exploit Public-Facing Application

T1046: Network Service Discovery

AML.T0000: Initial Access

AML.T0002: AI-Automated Reconnaissance

Credential Access Code scraping for secrets across code repos T1552.001: Credentials In Files AML.T0014: Credentials Harvesting
Privilege Escalation Infiltrating secrets manager to harvest admin system secrets T1555: Credentials from Password Stores AML.T0016: Privilege Escalation via Automated Pivot
Pipeline Abuse Executing CI/CD actions; attempting cloud provisioning tool edits T1578: Modify Cloud Compute Infrastructure AML.T0010: ML/DevOps Pipeline Interception
AI Infrastructure Abuse Invoking cloud AI models via stolen keys T1078: Valid Accounts AML.T0043: LLM Invocations via Stolen API Keys

Table 1. Major MITRE ATT&CK and MITRE ATLAS techniques used by the attacker.

Key Lessons: Addressing Agentic Attacks

This incident exposes how an attacker who understands how to deploy frontier AI agents effectively can dramatically speed up the pace of their attack. We assess that attackers will increasingly add AI agents to their tool sets. Organizations should take note of the following to address agentic attacks:

  • AI agents reduce the time between steps in the attack flow: AI agents in this attack were designed to parse raw tool output and quickly take next steps, speeding up the overall attack flow.
  • AI agents leave recognizable indicators: Defenders can identify agentic attacks by watching for indicators such as the use of structured Markdown, Python caches and paired asset folders.
  • Attackers can use AI to establish redundant persistence across the environment: In this incident, the attacker used AI agents to efficiently establish overlapping persistence across SSH keys, serverless functions, container restart policies, cloud identities and CI/CD pipelines. Using AI agents can make it easier for an attacker to maintain and test this entire portfolio in parallel.
  • Attackers can use an organization’s AI tools as post-compromise infrastructure: Attackers can hijack enterprise AI services to assist in their attacks. This allows threat actors to hide orchestration traffic among expected traffic, and offload the financial cost onto the victim.

Defending Against Machine-Speed Attacks

Defending against automated agent loops requires matching the speed and adaptability of AI-driven attacks:

  • Execute synchronized containment: Deploy automated playbooks that simultaneously revoke credentials, terminate OAuth sessions, freeze CI/CD pipelines and isolate cloud accounts across all operational planes.
  • Govern AI as core infrastructure: Inventory every model endpoint, API key, Model Context Protocol (MCP) gateway and AI tool integration. Apply strict rate limits, least-privilege policies and diagnostic logging.
  • Detect behavioral loops: Hunt for operational loops including bursty API requests, rapid 401/200 HTTP state shifts, parallel authentications and sudden model usage from unexpected identities.
  • Lock down DevOps pipelines: Enforce mandatory, multi-party code reviews and immutable branch protection on all infrastructure-as-code repos to block automated backdoor injection.

Learn more about how Unit 42 can help defend against AI-driven threats through Unit 42 Frontier AI Defense.