
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

让小产品的独立变现更简单 - ezindie.com
U
Unit 42
IT之家
IT之家
Y
Y Combinator Blog
T
Tailwind CSS Blog
B
Blog
大猫的无限游戏
大猫的无限游戏
博客园 - 叶小钗
Jina AI
Jina AI
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
I
InfoQ
J
Java Code Geeks
F
Fortinet All Blogs
T
The Blog of Author Tim Ferriss
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
H
Hackread – Cybersecurity News, Data Breaches, AI and More
人人都是产品经理
人人都是产品经理
腾讯CDC
Hugging Face - Blog
Hugging Face - Blog
GbyAI
GbyAI
博客园 - 司徒正美
The GitHub Blog
The GitHub Blog
酷 壳 – CoolShell
酷 壳 – CoolShell
L
LangChain Blog

Unit 42

The Machine With Many Faces: Post-Exploitation Identity Misuse in SPIFFE/SPIRE Untracked Nightmares: The Threats Hiding Behind Commodity Infrastructure Attackers Expose Ongoing AI Tool Use Targeting Organizations in Latin America An AI-Assisted Cyber Attack: Inside a Unit 42 Investigation Spring Ring: An Inside Look at Voice Phishing Campaigns in Microsoft Teams Perturbation Probing: A New Diagnostic for the Fragility of LLM Safety The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic Execution Connecting the Dots: Securing the Overlooked Corners of the Software Development Lifecycle (SDLC) Supply Chain Identity Abuse Through Trusted Communication Channels Kimwolf v7: An Evolution of the Kimwolf Botnet The Permanent Threat: Analyzing Aeternum’s Blockchain-Based C2 Operations and Communications Inside the Modern SOC: The Identity Front Door ChainDrop: Inside a Self-Propagating npm Worm Token Jacking: Cybercriminals Could Be Stealing Your AI Resources The Frontier AI Vulnerability Burst: Industrializing Autonomous Zero-Day Discovery in Open-Source Software Almost Half of Malware Samples Communicate Direct to IP Pass the Passkey: A Novel Attack Surface in Passwordless Authentication The Xcode Assassin Returns: A Deep Dive Into the Latest XCSSET Version Chinese-Speaking Threat Actor Harnesses AI Models for Autonomous Cyberattacks Three Steps to the Terminal: A Siemens ROX II Zero-Day Trilogy AI, Automation and Attacks: Unpacking the Unit 42 2026 Global Incident Response Report AI, Automation and Attacks: Unpacking the Unit 42 2026 Global Incident Response Report TuxBot v3: Inside an IoT Botnet Framework With LLM-Assisted Development No Manners Here: The Ruthless Rise of The Gentlemen Ransomware Vidar Stealer Unmasked: Code Signing Abuse, Go Loaders and File Inflation How We Added WebAuthn to a Browser-Based RDP Client Phantom Squatting: AI-Hallucinated Domains as a Software Supply Chain Vector CL-STA-1062 Targets Southeast Asian Governments and Critical Infrastructure OpenClaw’s Skill Marketplace and the Emerging AI Supply Chain Threat The Global Namespace Risk: Universal Bucket Hijacking Technique for Cloud Data Exfiltration
Russian Global Webmail Espionage
Unit 42 · 2026-07-23 · via Unit 42

Executive Summary

Unit 42 has observed a persistent cyberespionage campaign we track as CL-STA-1114. This activity cluster overlaps with activity from a Russian threat actor tracked by other vendors as Void Blizzard and LAUNDRY BEAR.

The attackers behind this campaign targeted Zimbra webmail in organizations in the following sectors:

  • Governments
  • Defense
  • Transportation
  • Financial organizations across the following regions:
    • NATO member states
    • Ukraine
    • Commonwealth of Independent States (CIS) countries
    • Africa

Unique to this campaign, the group leveraged zero-click phishing emails that exploit a vulnerability in the Zimbra Collaboration Suite (ZCS) webmail platform (CVE-2025-66376). The exploit automatically injects a malicious JavaScript payload without requiring recipient interaction. Once executed, the payload exfiltrates sensitive user data, including login credentials, email archives, and search histories. Threat actors continue to actively target unpatched ZCS instances using CVE-2025-66376.

Palo Alto Networks customers are better protected from the threats discussed above through the following products:

If you think you might have been compromised or have an urgent matter, contact the Unit 42 Incident Response team.

Technical Analysis

The attackers behind CL-STA-1114 have been active since at least 2024, and this campaign targeting Zimbra servers started in July 2025. Initial access starts with a phishing email that contains either an HTML attachment or embedded HTML in the message text. This lure is designed to catch recipients' attention with news headlines.

Figure 1 shows an example of the lure used and a snippet of the underlying HTML code.
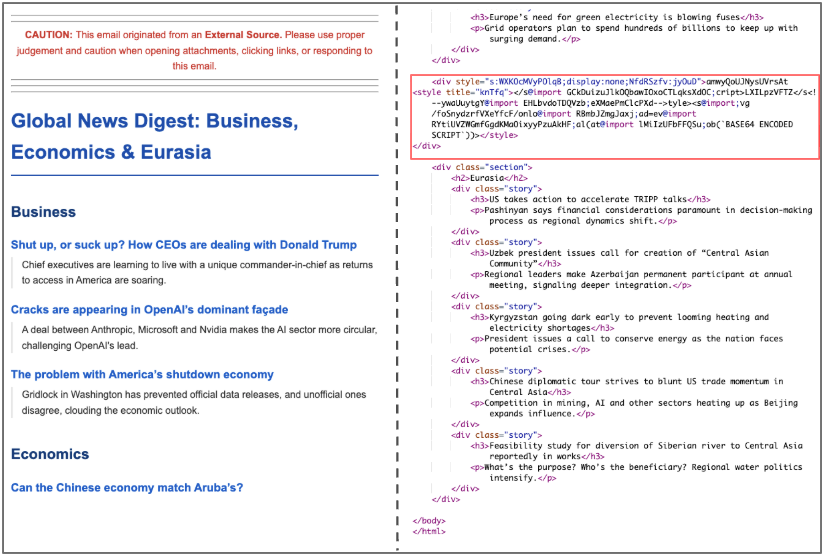
A screenshot of a split screen image displaying a webpage layout. On the left, content under 'Global News Digest: Business, Economics & Eurasia' with articles discussing CEOs, OpenAI, and the impact of American technology firms. On the right, rows of HTML code and text highlighting technical aspects of webpage formatting. The content covers topics such as business strategies, economic developments, and technological advancements
Figure 1. Example lure and a snippet of its underlying HTML content.

The HTML text contains an obfuscated division with a Base64-encoded script (highlighted in red in Figure 1). The obfuscated section creates an invisible Scalable Vector Graphics (SVG) element that, upon loading, decodes the Base64-encoded script into a JavaScript payload that it injects into the victim’s browser.

When executed, this JavaScript exfiltrates the victim’s Zimbra webmail data to a hard-coded command and control (C2) server. Exfiltrated data includes:

  • CSRF tokens
  • Email address and password
  • Two-factor authentication (2FA) scratch codes
  • System and environment details
  • The victim’s last 90 days of email and search history

Over the course of this campaign, we observed minimal changes to the JavaScript payload.

Figure 2 illustrates the attack chain.
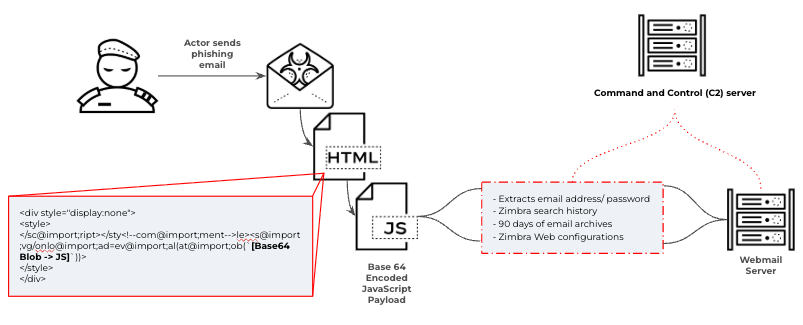
A flowchart illustrating a cybersecurity attack chain. On the left, a person sends a phishing email leading to downloads of HTML and JavaScript files. The files are depicted with labels "Base 64 Encoded JavaScript Payload." The process connects to a "Command and Control (C2) server" and a "Webmail Server," showing the extraction of emails, passwords, search history, email archives, and Zimbra Web configurations.
Figure 2. The attack chain.

Since we began tracking this campaign, there have been at least nine IP addresses and nine domains for the C2 servers. These servers were active for an average of 35.4 days. See the Indicators of Compromise (IoC) section for a list of the IP addresses and domains used in CL-STA-1114 activity.

Conclusion

This campaign activity in CL-STA-1114 illustrates the persistent and evolving threat of state-sponsored cyberespionage. The attacker behind this activity targets widely used mail platforms like Zimbra, posing a risk to critical industries globally.

This research highlights the need for vigilance, proactive patching and advanced threat detection to protect organizations. Network administrators, defenders and security researchers should patch vulnerable systems and use the IoCs below to investigate and strengthen defenses against CL-STA-1114 and similar activity.

Palo Alto Networks customers are better protected from the threats discussed above through the following products:

If you think you may have been compromised or have an urgent matter, get in touch with the Unit 42 Incident Response team or call:

  • North America: Toll Free: +1 (866) 486-4842 (866.4.UNIT42)
  • UK: +44.20.3743.3660
  • Europe and Middle East: +31.20.299.3130
  • Asia: +65.6983.8730
  • Japan: +81.50.1790.0200
  • Australia: +61.2.4062.7950
  • India: 000 800 050 45107
  • South Korea: +82.080.467.8774

Palo Alto Networks has shared these findings with our fellow Cyber Threat Alliance (CTA) members. CTA members use this intelligence to rapidly deploy protections to their customers and to systematically disrupt malicious cyber actors. Learn more about the Cyber Threat Alliance.

Indicators of Compromise

IP addresses

  • 37.120.247[.]228
  • 64.226.124[.]190
  • 104.248.134[.]194
  • 185.86.79[.]95
  • 193.238.152[.]66
  • 194.156.103[.]193
  • 216.252.238[.]18
  • 216.252.238[.]64
  • 216.252.238[.]104

Domains

  • analyticemailmeter[.]com
  • emailanalytics[.]com[.]ua
  • istc-cloud[.]com
  • mailnalysis[.]com
  • synacorzimbra[.]nl
  • zimbra-metadata[.]com
  • zimbrastat[.]com
  • zimbrasoft[.]com[.]ua
  • zmailanalytics[.]com

Additional Resources