


The average cost of downtime has reached $600 billion for the Global 2000, a 50% increase in two years. According to Splunk’s The Hidden Costs of Downtime report, unplanned outages and service degradation cost each company an average of $300 million.
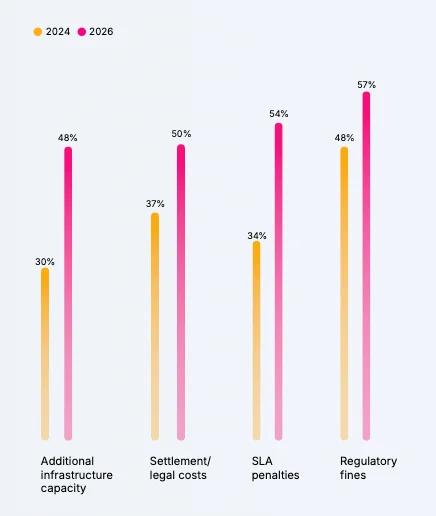
Percentage of technology executives who consider a direct cost very or prohibitively disruptive (2024 versus 2026) (Source: Splunk)
Delayed product launches, brand damage, and stock declines continue to affect companies after systems return online. Customer expectations, cybersecurity threats, rising incident costs, and regulatory pressure have made downtime a priority for technology leaders.
Internal vulnerabilities, cyber threats, AI-related complexity, and growing reliance on third-party services contribute to an average of 60 downtime and service degradation incidents each year.
Costs have also increased since 2024. Lost revenue reached $95 million, nearly double the previous figure, while regulatory fines and ransomware payouts rose to $51 million and $40 million. Technology leaders say regulatory fines create the greatest disruption, with 57% identifying them as highly disruptive.
Regulatory fines have increased as enforcement has become stricter. Rules such as GDPR and DORA place stronger requirements on financial institutions and impose penalties for outages, weak resilience, poor incident reporting, and third-party risks.
Although most finance executives say they advise against paying ransomware demands, ransomware payments remain one of the largest direct expenses, with about 40% of finance leaders admitting they pay attackers.
Ransomware attacks have become more targeted, with attackers focusing on revenue-generating systems, disabling backups, and setting demands based on downtime costs.
When systems fail, customer support requests rise, complaints spread on social media, and security, IT, and engineering teams move to incident response. Marketing teams prepare public statements while executives monitor financial impact.
The effects continue after services recover, delaying product work, increasing investor concerns, and weakening brand trust. Rebuilding trust can take months.
Almost 20% of marketing professionals say brand reputation takes a quarter to recover after an incident. Companies also report an average stock decline of 3.4% following downtime events, up from 2.5% in 2024.
Investors are paying closer attention to operational resilience. Nearly half of technology leaders say shareholders raised concerns about downtime during the past year, viewing it as a sign of broader issues such as weak risk management and outdated infrastructure.
Human error causes most downtime incidents, while phishing, malware, and ransomware often create the greatest impact. AI has also made phishing attacks more convincing and harder to detect.
Third-party services, including SaaS platforms, APIs, and cloud providers, have become a major source of outages. For ITOps and engineering leaders, downtime caused by third parties increased from 24% in 2024 to 63% in 2026.
“When an issue originates from a SaaS or third-party application, security teams must navigate a complex web of cloud, on-premises environments, and other infrastructure they often have no visibility into,” said Peter Sprenger, Splunk Field CTO. “The problem is intensified by siloed ownership and a lack of visibility into critical dependencies.”
Poor coordination between security, IT, and engineering teams can also delay responses and increase the impact of incidents.
Organizations rank end-to-end visibility as their top investment priority for improving resilience, ahead of infrastructure spending.
Organizations are spending a median of $24.5 million annually on AI tools designed to prevent and respond to outages, while 44% of technology respondents already use agentic AI.
The most common use case is incident triage and root cause analysis. 54% of respondents use generative AI and 27% use AI agents for these tasks. AI tools help teams correlate data, summarize incidents, recommend next steps, diagnose problems, and execute fixes such as code rollbacks.
Information services and technology recorded the highest downtime costs at $402 million, driven by disruptions involving cloud, SaaS, and API providers. Energy and utilities followed at $364 million, while retail reached $357 million.
Downtime costs in financial services, manufacturing, and transportation and logistics stem from regulatory, contractual, and legal penalties.
EMEA records the highest downtime costs because of compliance failures and security-related expenses. In APAC, lost revenue remains the largest cost driver. North America records the highest staffing and productivity costs, while LATAM reports lower overall costs.
Security expenses remain a major source of downtime costs worldwide, while system upgrades account for a smaller share, suggesting organizations still spend more on responding to incidents than preventing them.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。