
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

人人都是产品经理
人人都是产品经理
博客园_首页
博客园 - 三生石上(FineUI控件)
V
Visual Studio Blog
Hugging Face - Blog
Hugging Face - Blog
美团技术团队
小众软件
小众软件
T
Tailwind CSS Blog
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
月光博客
月光博客
有赞技术团队
有赞技术团队
WordPress大学
WordPress大学
博客园 - 【当耐特】
Apple Machine Learning Research
罗磊的独立博客
V
V2EX
酷 壳 – CoolShell
酷 壳 – CoolShell
IT之家
IT之家
量子位
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
Recent Announcements
M
MIT News - Artificial intelligence
阮一峰的网络日志
阮一峰的网络日志
The GitHub Blog
The GitHub Blog

Help Net Security

Your work apps are quietly handing 19 data points to someone ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security
Google Play is changing how Android apps access your cont...
Anamarija Pogorelec · 2026-04-16 · via Help Net Security

Google’s new set of Google Play policy updates and account transfer feature strengthen user privacy and protect businesses from fraud. Google is also expanding features for managing new contact and location policy changes to support a smoother, more predictable app review experience.

By October, Play policy insights in Android Studio can help developers identify if their apps should use new features and will guide them on the steps to take. From October 27, new pre-review checks in the Play Console will flag potential contact or location permission policy issues so they can be fixed before the app is submitted for review.

Accessing contacts with Contact Picker

Android Contact Picker is the new standard for accessing contact information that lets users share only the specific contacts they want to.
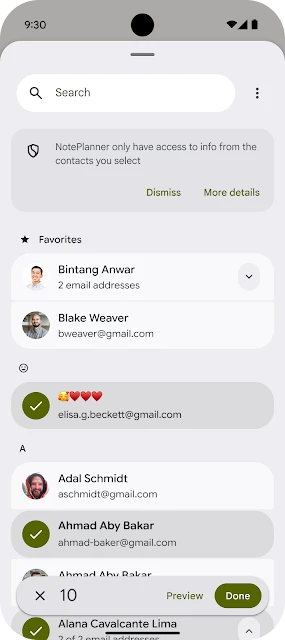
Google Play policy updates

“Alongside this tool, we are updating our policy to require that all applicable apps use the picker, or other privacy-focused alternatives like Sharesheet, as the primary way to access users’ contacts. READ_CONTACTS will be reserved for apps that can’t function without it,” Bennet Manuel, Group Product Manager, App & Ecosystem Trust, explained.

Apps that request access to contacts for features like sharing or inviting should update their code to use the picker and remove the READ_CONTACTS permission when targeting Android 17 and above.

Apps that require ongoing access to a user’s contact list must submit a Play Developer Declaration in the Play Console to justify the need.

Location button for precise location

To make requesting precise location data easier for one-time actions, like finding a store or tagging a photo, Android is introducing a streamlined location button. It helps users choose how much information they share and for how long. Updated policy requires apps to use this button for one-time precise location access. Apps that require always-on location access can continue to request it.

To ensure that they are requesting the minimum amount of location data needed for the app to work, developers should review their apps’ location usage. They should add the onlyForLocationButton flag in their manifest if the app uses precise location for temporary actions and targets Android 17 and above.

If an app requires persistent precise location to function, a Play Developer Declaration in the Play Console must be submitted.

Account transfers in Play Console

Play Console gets an official account transfer feature that supports ownership transfers during sales and mergers while protecting businesses from fraud. This feature must be used from May 27. Unofficial transfers such as sharing login credentials or buying and selling accounts on third-party marketplaces are not permitted.

Through the “Users and permissions” page in the Play Console, developers should initiate any future account owner changes. Every transfer includes a mandatory 7-day security cool-down period to give teams time to spot and cancel any unauthorized account takeover attempts.