


Dependency vulnerability scanning in JavaScript and TypeScript projects has long sat at the end of the development pipeline. Pull requests get opened, continuous integration runs, and a security scanner returns a list of CVE identifiers that developers then have to triage hours or days after writing the code. CVE Lite CLI, now an officially recognized OWASP Incubator Project, moves that check to the developer’s terminal.
The open-source tool, maintained by Sonu Kapoor, reads a project’s lockfile, queries the Open Source Vulnerabilities database, and returns copy-and-run fix commands scoped to the relevant package manager. It supports npm, pnpm, Yarn, and Bun.
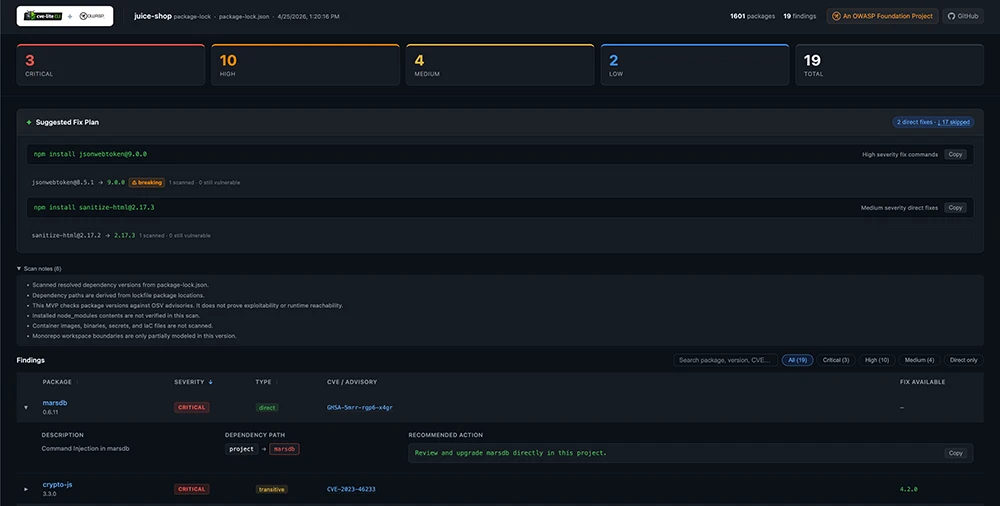
“In many teams, dependency vulnerabilities are first surfaced in CI. That is useful, but it often happens late in the workflow,” Kapoor told Help Net Security. “A developer changes a dependency, pushes the branch, waits for CI, gets a large scanner report, and then has to work backward through the output to understand what changed, whether the vulnerable package is direct or transitive, and what can actually be fixed.”
CVE Lite CLI runs locally with no account, no cloud platform, and no source code leaving the developer’s machine. A scan completes in seconds against a cached advisory database. The output distinguishes direct dependencies from transitive ones, identifies the top-priority fix, and provides the exact install command to apply it. For transitive npm findings, the tool recommends npm update <parent> when the existing parent range can resolve to a non-vulnerable child, and flags cases where the parent itself needs an upgrade.
Kapoor described the design intent in plain terms. “The shift I care about is moving from ‘CI found a large report later’ to ‘the developer gets a clear fix plan locally while the dependency change is still fresh.'”
CVE Lite CLI does not block dependency installation or interrupt development by default. Teams choose where to place the check. It can be run manually, added as a package script, wired into a pre-commit or pre-push hook, or executed in CI through the project’s first-party GitHub Action.
“CVE Lite CLI provides the fast local scanner and the structured output; the team decides where that check belongs in its workflow,” Kapoor said.
For continuous integration, the --fail-on flag exits non-zero when findings meet or exceed a severity threshold. SARIF output uploads directly to GitHub Code Scanning, surfacing results in the Security tab and as inline pull request annotations.
The decision to query OSV reflects the project’s focus on package-and-version-oriented scanning. Kapoor said OSV’s data model fits a lockfile scanner because it maps advisories cleanly to open source package ecosystems and affected version ranges.
He acknowledged the limits of any single source. “I do not think any single advisory source should be treated as perfect. Coverage gaps, timing differences, severity differences, and fixed-version data quality can vary across sources. That is why CVE Lite CLI is explicit in its output that OSV is the advisory source.”
Future work may include clearer alias display, visibility into fixed-version confidence, and cross-referencing additional advisory feeds where it can be done without slowing the tool.
Kapoor said he wanted to see how CVE Lite CLI would perform against real applications with known dependency CVEs, and pointed to OWASP Juice Shop as a representative test because its dependency tree resembles that of real-world JavaScript projects.
According to Kapoor, the tool reduced findings from 39 to 18 across two remediation passes and cleared the high-severity issue, while making upstream dependency risk easier to separate from problems a developer could address locally. “The useful part is helping developers understand which vulnerabilities are direct, which are transitive, which can be fixed now, and which require broader dependency decisions,” Kapoor said.
For restricted-network and air-gapped environments, the CLI supports syncing the advisory database ahead of time. Ingesting roughly 217,000 advisory records completes in under nine seconds, which the project says is 9.9 times faster than the initial implementation. Scans then run with no outbound API calls.
CVE Lite CLI also writes AI assistant skill files for Claude Code, Codex CLI, Gemini CLI, Cursor, and GitHub Copilot through the install-skill command, letting coding assistants parse scan output and produce remediation plans.
CVE Lite CLI is available for free on GitHub.

Must read:

Subscribe to the Help Net Security ad-free monthly newsletter to stay informed on the essential open-source cybersecurity tools. Subscribe here!
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。