


The 2026 InsurSec Report from At-Bay, covering more than 100,000 policy years of claims data, documents a 7% year-over-year rise in overall claim frequency and an all-time high average severity of $221,000. Ransomware severity reached $508,000, up 16% from the prior year, making it the costliest incident type by a wide margin.
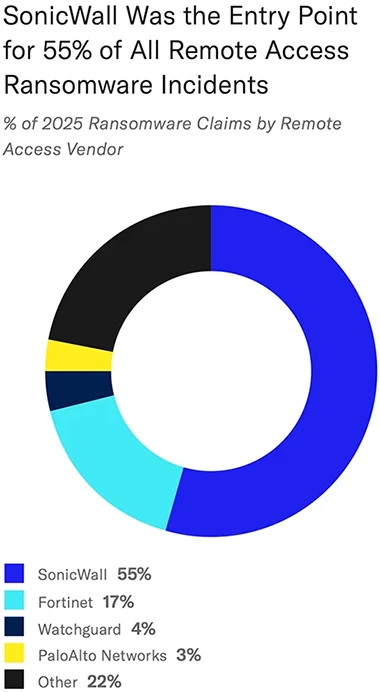
Remote access services served as the entry point for 87% of ransomware claims in 2025, up from 80% the year before. VPN compromises alone accounted for 73% of ransomware intrusions where an entry vector was identified, climbing from 38% in 2023 and 66% in 2024. One in three ransomware claims involved a SonicWall device.
Email did not produce a single ransomware claim for At-Bay in 2025. Improvements in email security filtering have pushed attackers toward remote access infrastructure, where exposed appliances provide faster paths to full network access.
Akira ransomware frequency jumped 364% in the third and fourth quarters of 2025. Attacks moved at unusual speed, with many deployments occurring within hours or minutes of initial access. The group’s average ransom demand reached $1.2 million, 50% higher than non-Akira demands, and average payments came in at $452,000.
Of Akira victims that avoided encryption, every one had 24/7 managed detection and response monitoring in place. Two-thirds of Akira attacks happened at night or on weekends, leaving organizations without round-the-clock coverage with limited opportunity to disrupt the attack chain.
Adam Tyra, CISO for Customers at At-Bay, told Help Net Security that organizations running vulnerable VPN appliances should retire them in favor of cloud or SaaS-based remote access. For companies that cannot yet budget for managed detection and response, he pointed to endpoint detection and response tools as the next line of defense.
“Our data shows that there is no close substitute for professional security monitoring via MDR. But, companies that aren’t ready for that can get almost the same level of protection by deploying an effective EDR tool, configuring it to block identified malicious activity, and keeping a close eye on any alerts that it generates,” Tyra said. “Most EDR tools are capable of stopping malicious activity when they detect it, but many companies aren’t comfortable letting this functionality work automatically. That needs to change. You may not be able to afford professional support, but you can definitely afford to maximize your usage of the tools you already bought.”
Businesses under $25 million in revenue saw the steepest changes in the portfolio. Ransomware frequency in this segment rose 21% year-over-year, and average ransomware severity climbed 40% to $422,000. The infrastructure-driven targeting model used by Akira and similar groups struck vulnerable appliances wherever they existed, pulling smaller organizations into campaigns that had previously concentrated on mid-market and larger firms.
Manufacturing experienced ransomware frequency at 2.2 times the portfolio average. Technology companies posted the highest average ransomware severity at $875,000, followed by finance and insurance at $731,000 and healthcare at $675,000.
Financial fraud remained the most common incident type, accounting for roughly 30% of claims for the third consecutive year. Email served as the initial entry vector in 82% of these incidents. Average stolen funds reached $285,000, a 16% increase over 2024, and the largest single loss recorded was $9.65 million.
Attackers have moved toward routing malicious links through trusted cloud platforms, with Cloudflare appearing in 69% of abused infrastructure alerts analyzed by At-Bay’s email monitoring team between September 2025 and March 2026. Legacy email filters often pass these links because they originate from legitimate services.
Tyra said organizations should not expect content delivery networks to face meaningful liability for hosting abused infrastructure. “It’s unlikely that CDNs like Cloudflare will bear any significant liability here, but people have tried. We can’t say whether this issue may be subject to legal or regulatory attention in the future, but it’s unlikely to have an impact anytime soon,” he said.
“The bottom line is that companies need to assume that there won’t be any upstream support stopping or even throttling this activity. Meaningful protection needs to occur in the company’s own environment through training employees to spot and report fraud and deploying a modern AI-backed email security solution that can identify indicators of fraud before employees are ever exposed to them in the first place.”
Speed of reporting shaped recovery outcomes in fraud cases. Businesses that alerted At-Bay within three days saw some funds returned 70% of the time. Recovery rates dropped to 53% at four to fourteen days and fell below 30% after that. The insurer’s claims team recovered $56 million in stolen funds during 2025.
Third-party liability claims rose 70%, the largest increase among tracked incident types. Lawsuits tied to the California Invasion of Privacy Act made up 34% of third-party liability claims, up from 7% in 2023. CIPA cases have expanded beyond Meta Pixel to cover tracking tools from LinkedIn, TikTok, and other vendors, with 69% of 2025 cases involving non-Meta Pixel technology.
Class action lawsuits followed 6% of ransomware incidents and 4% of data breaches from 2023 and 2024, arriving months after the underlying incident and adding defense costs, discovery expenses, and settlement payouts to organizations that had already absorbed the immediate damage of an attack.
Business interruption coverage was triggered in one in three ransomware claims. Claims involving business interruption averaged $510,000 in severity, compared with $168,000 for ransomware claims without it. The largest single business interruption payment reached $5 million, the coverage limit for that insured.

Webinar: The True State of Security 2026
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。