


Google Cloud introduced AI Threat Defense, an automated cybersecurity platform that combines several of the company’s security assets to find, prioritize, and patch software vulnerabilities at machine speed. The product is aimed at enterprises contending with attackers who use AI to discover and exploit flaws in hours or days, compressing windows that once stretched into weeks.
The platform fuses the Gemini family of models, the cloud security firm Wiz, the AI code-fixing agent CodeMender, and the threat intelligence and incident response practice Mandiant. Google Cloud completed its acquisition of Wiz earlier and folded it into the security portfolio alongside Mandiant, which it acquired in 2022.
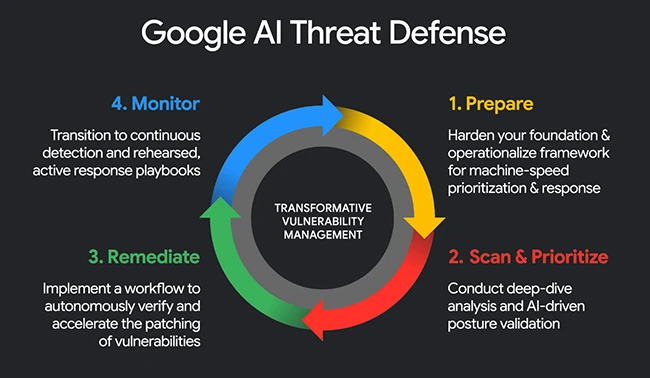
The product operates across a four-stage framework that Google calls Prepare, Scan and Prioritize, Remediate, and Monitor. In the Prepare stage, the platform uses Wiz to map exposed applications, infrastructure, APIs, identities, and runtime environments, reducing what attackers can reach. A pen-testing agent built into Wiz simulates attacks to determine which exposures are exploitable.
In the scanning stage, the system runs multiple AI models against the environment. Lighter, faster models handle broad coverage across assets, and frontier models perform deeper analysis on internet-facing applications, customer-facing services, authentication logic, and other systems judged to carry the highest risk. Google’s reasoning for the multi-model design is that no single model finds every class of vulnerability; performance varies across application logic, cloud configuration, binary analysis, and exploitability validation. Customers access the models through the Gemini Enterprise Agent Platform.
Once a vulnerability is identified, Mandiant supplies the playbooks for response, including guidance on managing surges of critical issues and retiring legacy products.
The remediation stage centers on CodeMender, a Google DeepMind agent that generates fixes inside a developer’s integrated development environment or command-line interface. CodeMender works with Wiz and Antigravity to replace vulnerable code, rewrite older code in memory-safe languages, and analyze library dependencies so patches can be coordinated across components.
Before any patch reaches production, the platform generates tests to verify the fix. Patched libraries are tagged in source control and production, producing an audit trail that records which model generated each fix and when. Google describes the workflow as autonomy under human supervision.
The Monitor stage relies on agents tied to Google Security Operations, the company’s security operations center product. These agents handle detection, triage, investigation, and threat hunting across network, identity, and application telemetry. The platform also uses hardened container images that are built, signed, and verified daily to limit the attack surface at runtime.
“Our secure-by-default architecture automatically blocks 10 million spam emails every minute, and protects billions of users and customers across our broad portfolio,” Francis deSouza, COO, Google Cloud and President, Security Products, explained.
The company’s earlier security work includes zero trust architecture, the Titan security chip, and Google Security Operations.
DeSouza wrote that the collapse of the exploit window has made human-speed vulnerability management unviable for enterprise risk, framing AI Threat Defense as Google’s response to attackers who have automated reconnaissance and exploitation. The product enters a market where most security vendors are layering AI features onto existing tools. Google’s pitch centers on combining vulnerability discovery with prioritized, automatically generated patches, drawing on the Wiz risk context, CodeMender remediation, Gemini reasoning, and Mandiant operational guidance.

此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。