


70% of organizations use GenAI in live environments, and 64% have AI agents in pilot or production deployments. Some of those agents have privileged access to core systems, according to Check Point’s 2026 Cloud Security Report.
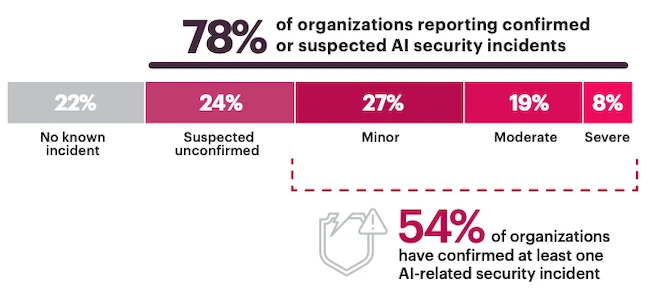
Confirmed and suspected AI incidents (Source: Check Point)
Security architectures built around human users and predictable application behavior are struggling with AI systems that rely on APIs, automation, and autonomous actions.
More than half of companies have experienced at least one AI-related security incident. The most common incidents involve unauthorized or shadow AI use, AI-generated phishing and deepfake content, and sensitive data leaks tied to AI services.
“AI adoption has outpaced the architecture built to govern it. Agents are acting inside live systems; data is moving through external AI services, and most enterprises still lack the visibility and enforcement to keep pace. Visibility, control, and security need to be present at all layers in the stack AI workloads will operate in,” said Paul Barbosa, VP of Cloud Security and SASE at Check Point Software Technologies.
Firms are rewriting acceptable use policies, creating AI governance programs, and increasing investment in AI-specific controls. They still lack the infrastructure needed to enforce those policies consistently.
Only 5% report visibility into AI tools and services used inside their environments. Security teams often lack insight into which tools employees use, what data enters AI workflows, and where that data moves afterward. Only a small share can reliably distinguish legitimate AI activity from suspicious or unauthorized usage.
AI traffic is changing enterprise network patterns. Companies report increases in API-driven traffic, connections to external AI services, and east-west traffic inside hybrid environments.
Inspection gaps remain a problem. Existing network security tools often struggle to inspect AI-related traffic without affecting application performance.
AI infrastructure is moving closer to internal systems and regulated data. Some firms are shifting AI training and inference workloads into private cloud and on-premises environments, placing more focus on datacenter perimeter security and internal traffic inspection.
Approaches to governing employee access to AI services vary widely. Some rely on endpoint security tools, some apply separate rules for on-network and off-network access, and others block external AI tools entirely. Only a small percentage enforce consistent AI access controls regardless of location.
Coverage gaps extend into SaaS traffic inspection, browser-based AI tools, and endpoint monitoring. Many firms report partial visibility into AI SaaS traffic and limited ability to control unauthorized AI applications.
Application-layer protections are under pressure. WAF and WAAP tools struggle with AI-specific attacks such as prompt injection, and increased false positives are becoming a problem in AI environments.
Runtime protection inside AI applications remains immature. Few firms have broadly deployed controls for LLM inputs, outputs, and tool authorization, and many still rely on ad hoc testing for GenAI applications.
Data governance is another weak point. Some companies permit source code in GenAI tools, and many cannot trace the flow of sensitive data through AI processing environments. AI-specific DLP deployment remains low.
Prevention capabilities remain limited across prompts, data flows, and AI-generated outputs. Most organizations detect AI-related risks more easily than they stop them in real time.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。