
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

爱范儿
爱范儿
博客园 - 叶小钗
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
腾讯CDC
S
SegmentFault 最新的问题
D
DataBreaches.Net
Hugging Face - Blog
Hugging Face - Blog
L
LangChain Blog
Recent Announcements
阮一峰的网络日志
阮一峰的网络日志
N
Netflix TechBlog - Medium
大猫的无限游戏
大猫的无限游戏
M
MIT News - Artificial intelligence
酷 壳 – CoolShell
酷 壳 – CoolShell
博客园 - 三生石上(FineUI控件)
F
Fortinet All Blogs
让小产品的独立变现更简单 - ezindie.com
Martin Fowler
Martin Fowler
雷峰网
雷峰网
J
Java Code Geeks
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
小众软件
小众软件
云风的 BLOG
云风的 BLOG
T
Tailwind CSS Blog

Help Net Security

ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
Hundreds of AI-powered iOS apps found exposing credential...
Sinisa Markovic · 2026-06-22 · via Help Net Security

Mobile app developers are packing AI features into everything from writing assistants to productivity tools and lifestyle apps. New research shows that securing access to those services remains a challenge.
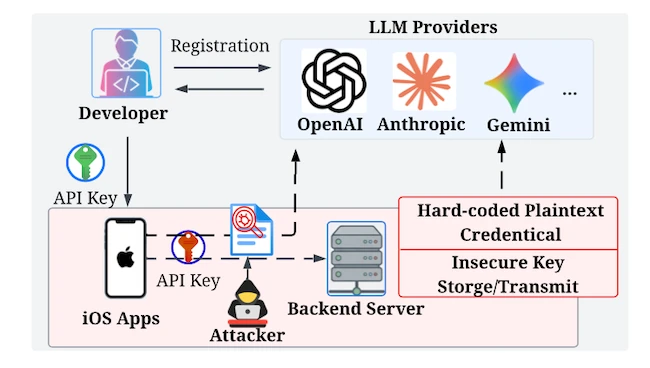
iOS apps credential leakage

LLM API credential leakage via network traffic interception (Source: Research paper)

Researchers from Wake Forest University analyzed 444 iOS applications with LLM features and found 282 that exposed exploitable credentials or backend access mechanisms. The affected apps covered 13 categories, including productivity, entertainment, lifestyle, education, utilities, and health and fitness.

LLM-powered applications reached 17 billion downloads in 2025 and accounted for 13% of all mobile app downloads.

“LLM API key leakage is a widespread and systemic issue in the iOS ecosystem, affecting 26% of analyzed Apps across diverse categories and developer types. The vulnerability’s impact extends from niche Apps to popular apps with hundreds of thousands of users,” the researchers noted.

The team began with more than 38,000 App Store listings before narrowing the dataset to 444 applications with confirmed LLM functionality. Among those apps, 64% exposed credentials or access mechanisms that remained exploitable during testing.

The issue was not confined to little-known applications. Fifteen percent of vulnerable apps had more than 1,000 user ratings, and the most popular affected app had accumulated more than 2.3 million ratings.

Among the vulnerable apps, 136 exposed authentication tokens, 92 allowed unauthenticated backend access, and 54 exposed plaintext API keys. In 28 of the plaintext key cases, the applications also exposed system prompts used by the underlying AI service.

Productivity apps accounted for the largest number of vulnerable applications, followed by entertainment and lifestyle apps. Health & Fitness recorded the highest leakage rate among the categories examined.

The largest group of vulnerable applications relied on custom developer-operated backends. Researchers identified 155 apps in that category. Another 67 used cloud platforms such as Firebase, Google Cloud Run, and AWS, while 60 communicated directly with AI providers.

“Over half of leaked Apps (55%) route LLM traffic through custom developer backends, making provider-side mitigations alone insufficient. Cloud platforms and direct API services account for comparable shares of leakage (23% and 21%, respectively), confirming that adopting a proxy architecture does not prevent credential exposure,” they added.

The issues were disclosed to the developers of all 282 vulnerable applications, and the apps were retested 90 days later.

“After responsible disclosure, 28% of vulnerable applications successfully remediated through credential revocation or access control enforcement. However, 23% remain exploitable due to either absence of remediation action (36 apps) or fundamentally flawed authentication implementations (30 apps),” they concluded.