
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

IT之家
IT之家
Y
Y Combinator Blog
月光博客
月光博客
Blog — PlanetScale
Blog — PlanetScale
GbyAI
GbyAI
Cyber Security Advisories - MS-ISAC
博客园 - 三生石上(FineUI控件)
S
SegmentFault 最新的问题
让小产品的独立变现更简单 - ezindie.com
美团技术团队
雷峰网
雷峰网
酷 壳 – CoolShell
酷 壳 – CoolShell
Last Week in AI
Last Week in AI
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
有赞技术团队
有赞技术团队
博客园 - 司徒正美
V
Visual Studio Blog
小众软件
小众软件
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
T
Tailwind CSS Blog
Apple Machine Learning Research
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
A
About on SuperTechFans
The Cloudflare Blog

Help Net Security

ChatGPT advanced account security adds passkeys and hardware keys Week in review: High-severity LPE vulnerability in the Linux kernel, cPanel 0-day exploited for months Automating Pentest Delivery: A Step-by-Step Guide - PlexTrac Open-source privacy proxy masks PII before prompts reach external AI services Shadow AI risks deepen as 31% of users get no employer training Identity is the control plane for distributed infrastructure AI traffic is getting bigger, louder, and less predictable New infosec products of the month: April 2026 cPanel zero-day exploited for months before patch release (CVE-2026-41940) Cisco releases open-source toolkit for verifying AI model lineage Met Police face criticism for using AI to spy on their own officers Nine-year-old Linux kernel flaw enables reliable local privilege escalation (CVE-2026-31431) Hacker with a special interest in breaching sports institutions ends behind bars - Help Net Security IP Fabric MCP server adds governance and control to enterprise AIOps workflows - Help Net Security Aqua Compass MCP server enables real-time investigation and containment of runtime threats - Help Net Security Google brings instant email verification to Android, no OTP needed - Help Net Security If cyber espionage via HDMI worries you, NCSC built a device to stop it - Help Net Security Apple fixes iPhone bug that let FBI retrieve deleted Signal messages(CVE-2026-28950) - Help Net Security GopherWhisper APT group hides command and control traffic in Slack and Discord - Help Net Security OpenAI tackles a bad habit people have when interacting with AI - Help Net Security A year in, Zoom's CISO reflects on balancing security and business - Help Net Security Scenario: Open-source framework for automated AI app red-teaming - Help Net Security GDPR works, but only where someone enforces it - Help Net Security Ransomware, fraud, and lawsuits drive cyber insurance claims to new peaks - Help Net Security Google’s Workspace Intelligence promises privacy while running on your data - Help Net Security Cyberattack on French government agency triggers phishing alert - Help Net Security Claude Mythos finds 271 Firefox flaws, Mozilla believes zero-days are numbered - Help Net Security Prove Identity Platform connects verification, authentication, and fraud prevention - Help Net Security New Mirai variants target routers and DVRs in parallel campaigns - Help Net Security Acronis GenAI Protection gives MSPs control over AI usage and data risks - Help Net Security
Tigera introduces unified control plane for Kubernetes-ba...
Industry News · 2026-06-17 · via Help Net Security

Tigera has announced the general availability of Tigera Lynx, a unified control plane for Kubernetes-native AI agents. Lynx gives enterprises a single place to find every agent in their Kubernetes estate, tighten security posture, assign sandboxes, provide each agent with a cryptographic identity, enforce policy on every action it takes, audit agent activity, and detect anomalous behavior, all without changing a line of agent code.
Tigera Lynx

AI agents do not behave like the workloads enterprise security stacks were built to manage. They are autonomous and non-deterministic: acting on behalf of users, accessing tools, LLMs, and other agents, operating through delegation chains, and consuming untrusted input. As a result, three teams often view the same challenge from different perspectives. AI teams want to experiment with new technologies and move quickly.

Platform engineering teams are measured on deployment velocity but cannot easily prove the platform is under control. Security teams are asked to approve agents without being able to confidently assess their security posture. A valid credential does not guarantee safe behavior, and the blast radius can change every time a new agent, tool, or platform update is introduced.

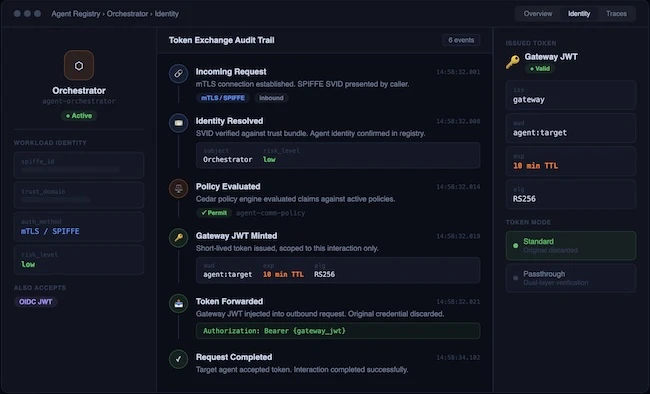
Lynx sits in the path of every agent call, agent-to-agent, agent-to-tool, and agent-to-LLM, to authenticate, authorize, mediate, and audit each one. It plugs into the tools enterprises already run, including their identity provider (EntraID, Okta) or via SPIFFE/SPIRE, and existing observability systems, and is built on open standards rather than proprietary lock-in.

One control plane, five capabilities

  • Discovery, registration, and observability. A central registry catalogs every agent with its owner, purpose, and version, while eBPF-powered auto-discovery finds agents nobody registered. Shadow agents are flagged and quarantined, and any agent’s actions can be reconstructed end-to-end through OpenTelemetry traces.
  • Configuration and posture management. AI-CSPM continuously evaluates every agent against a baseline, surfacing drift and over-permissions the moment they happen, with per-agent sandboxing and pre-built compliance packs mapping to GDPR, HIPAA, SOC 2, and financial services requirements. A Red Team Agent continuously probes for weaknesses in posture and misconfigurations.
  • Identity and authentication. Every agent gets a verifiable cryptographic identity through integration into an enterprise’s identity provider (EntraID, Okta) or through SPIFFE/SPIRE, with no shared secrets. Long-lived API keys are replaced by short-lived and tightly scoped, auto-rotated tokens. A JWT token is minted for every hop in a multi-agent workflow.
  • Policy definition and enforcement. A single default-deny policy governs LLM, MCP, and agent access using the Cedar policy language, enforced at the gateway before any call executes — with no agent code changes. Misbehaving agents can be quarantined instantly and high-stakes calls routed to a human.
  • Anomalous behavior detection. eBPF and LSM watch every syscall, network call, and file access at a layer agents can’t tamper with, catching credential theft and lateral movement even when an action passes policy. This provides a forensic audit trail. Guardian Agent detects anomalous behavior and quarantines suspicious agents.

“For over a decade, Tigera’s Calico platform has served Global 2000 companies running the largest Kubernetes platforms in the world, securing tens of millions of mission-critical transactions every day. AI agents are the next class of workloads: autonomous, distributed, and increasingly embedded in critical business processes. Lynx brings that same unified control and security rigor to AI agents. We’re building on our core competency — securing mission-critical workloads at scale on Kubernetes, in a highly performant way,” said Ratan Tipirneni, CEO of Tigera.

“Control only matters if it’s enforced uniformly. Lynx gives every agent a cryptographic identity, scopes credentials to a single hop, and evaluates every LLM, MCP, and tool call against a default-deny policy at the gateway — with no agent code changes. Because we watch behavior with eBPF and LSM at the kernel, we can detect an agent going wrong even when it carries a valid credential, and produce a reproducible audit trail to prove it,” said Peter Kelly, Chief Technology Officer of Tigera.