


Every year, security and tech leaders come to the RSA conference in San Francisco to take the industry’s pulse, and every RSAC tends to be dominated by a single, overarching theme. Last year, the theme was: “AI agents are coming, and governance isn’t ready.” And sure enough, the theme of RSAC 2026 was: “AI agents are here, and governance needs to catch up.”
Throughout the conference, security practitioners, vendors, and analysts were all asking the same questions:
How can we enable a culture of agentic AI builders, without compromising on bedrock security principles?
How can we mitigate the potential for AI agents to behave unsafely, either via malicious compromise or their own nondeterministic nature?
What are the most impactful safeguards every organization should be putting into place to secure AI and automation in the next year?
1Password provided answers to those urgent questions at RSA. Prior to the event, we announced the release of 1Password® Unified Access, a new platform that helps teams discover, secure, and audit access across humans, agents, and machine identities, so organizations can adopt AI confidently and securely.
At RSA, 1Password leaders spoke on panels, met with customers, discussed what's next in agentic security with industry analysts and press, and demoed our products for booth visitors. Here’s a look at the highlights.
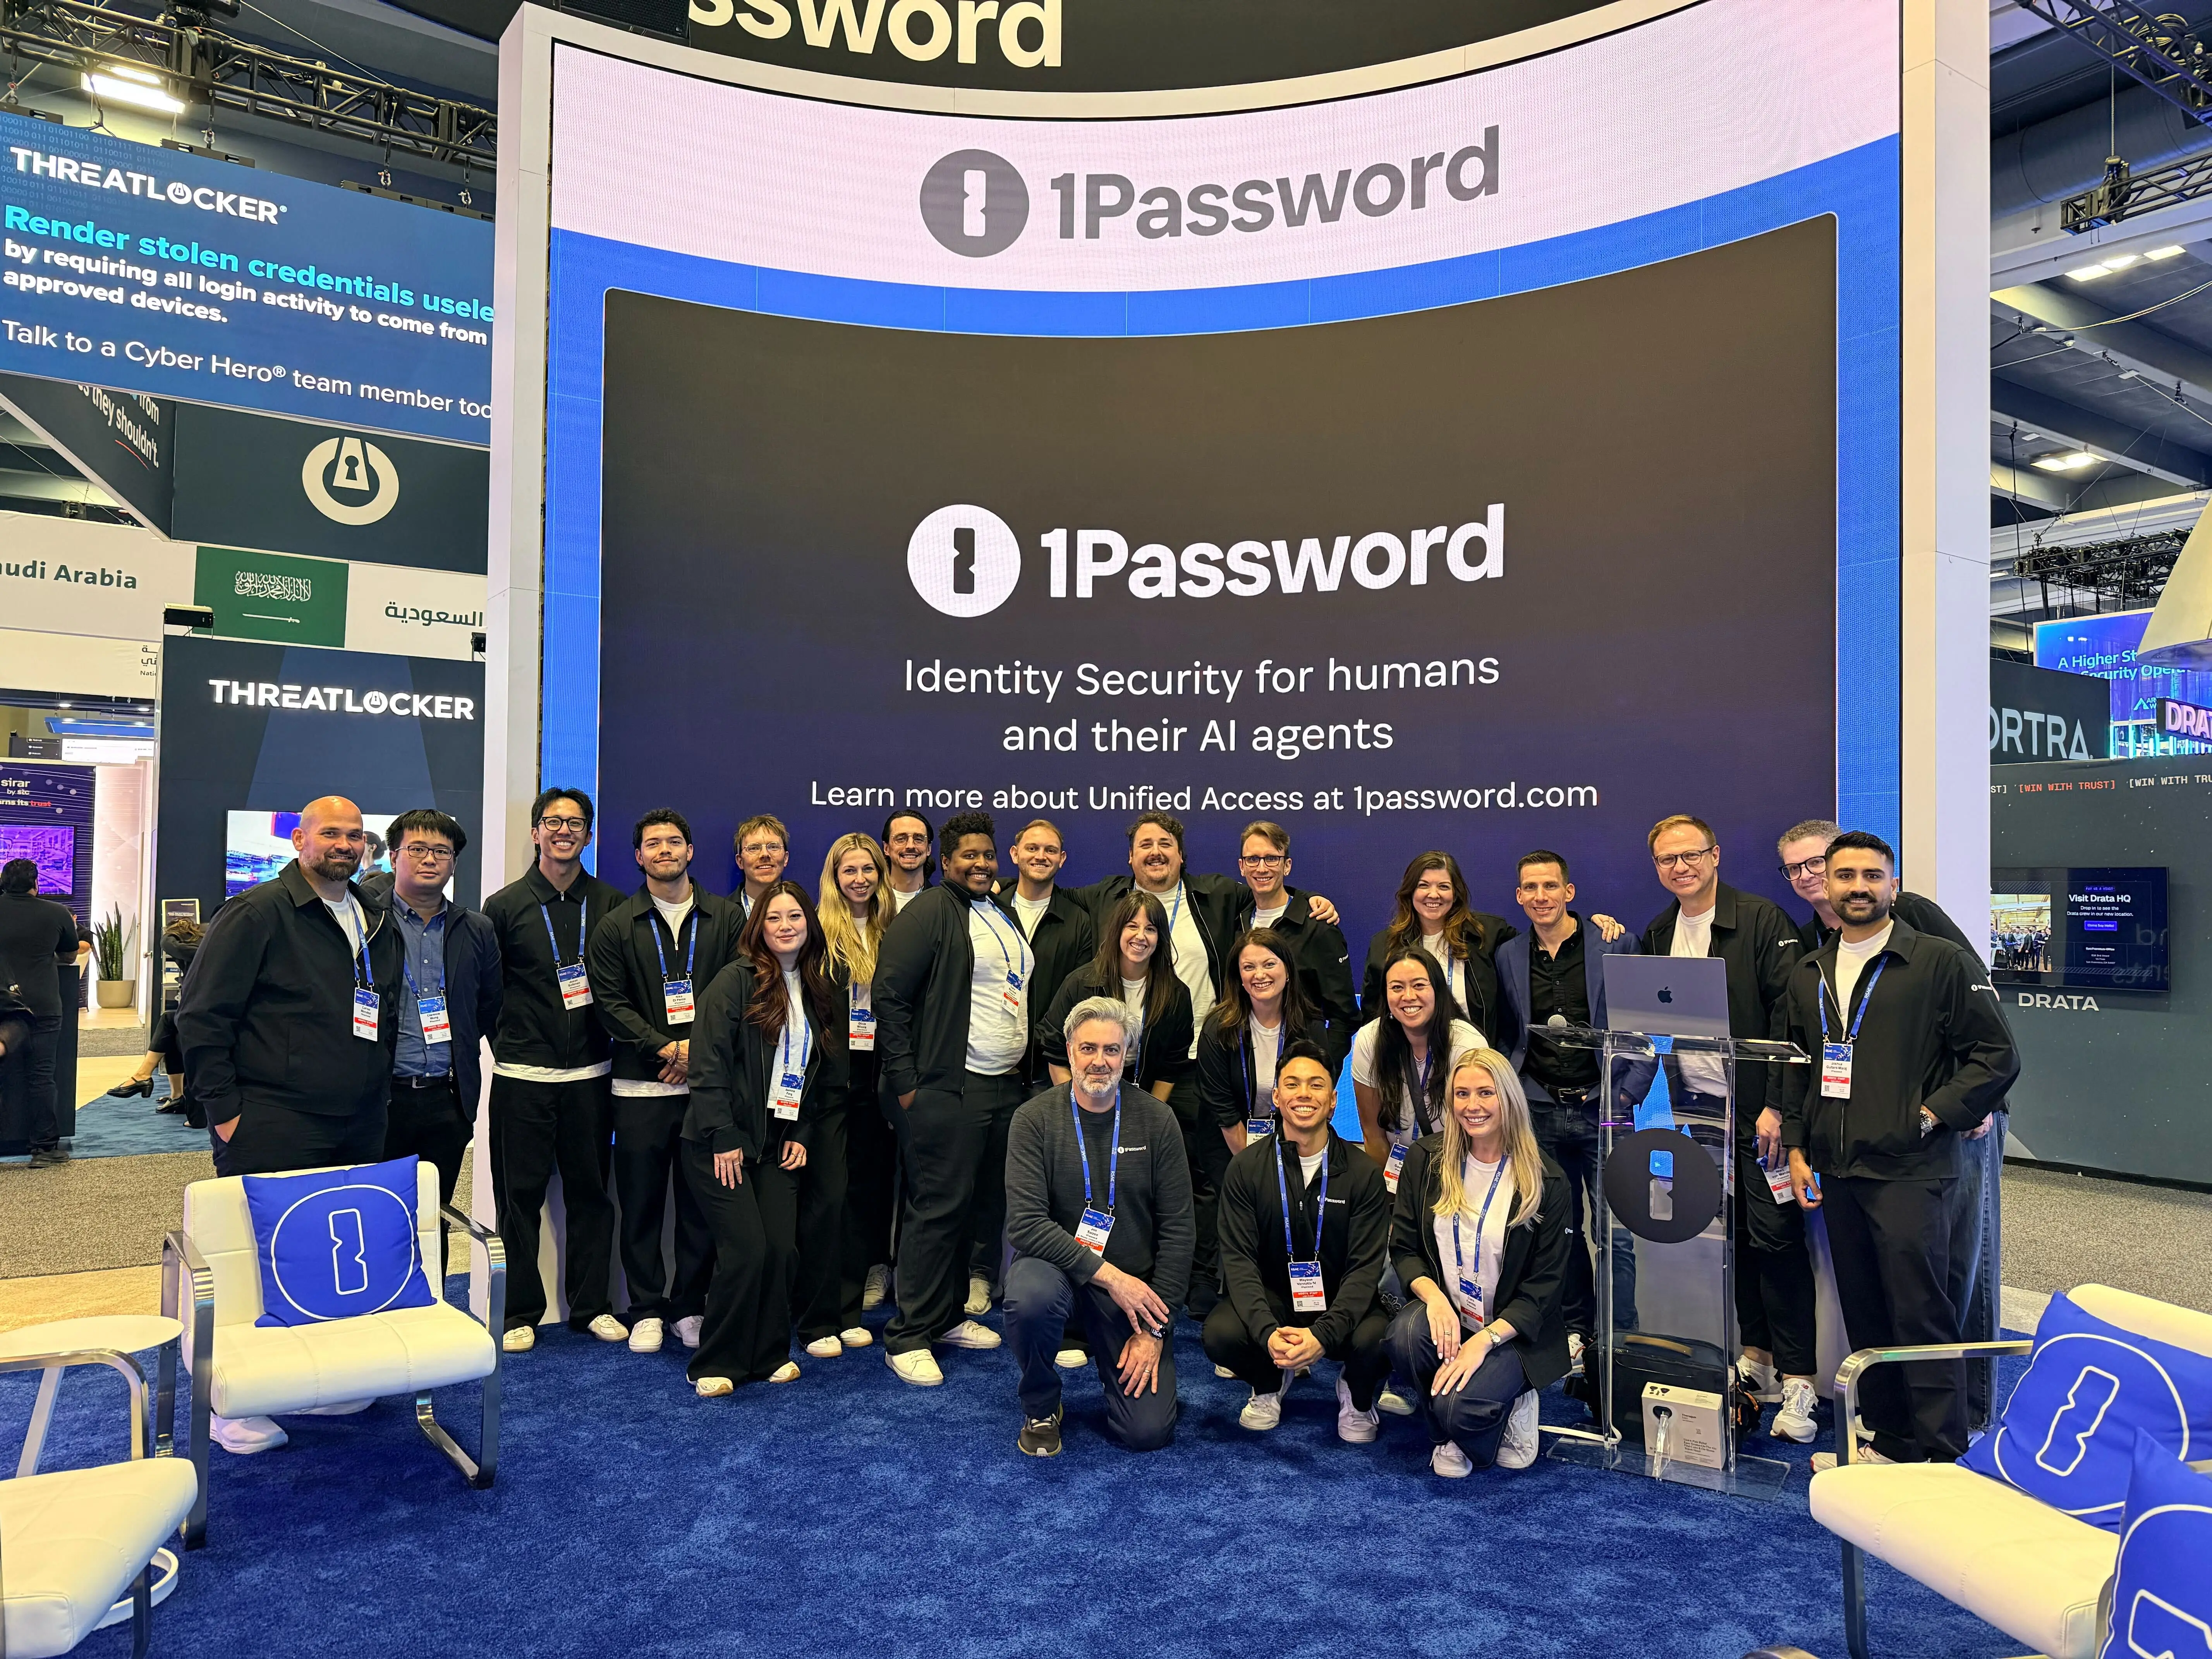
The 1Password booth was buzzing with RSAC attendees eager to learn about how our latest product releases could address their security needs. They experimented with interactive demos of our products, which you can check out for yourself:
Monday night, 1Password leaders hosted a customer appreciation happy hour, where everyone enjoyed the chance to unwind, swap stories, and discuss the shared future for 1Password and our customers.
Throughout RSAC, 1Password hosted sessions at our offsite space featuring company leaders and industry peers. On Tuesday, the theme of the talks – both at the 1Password space and the convention center – was breaches: how to prevent them and how to respond when you’re faced with one.
Over in the convention center, Wendy Nather, 1Password’s Senior Research Initiatives Director, gave two talks about breaches. In the first, playfully titled “Less blood, more bits: Learning from “near misses” in cybersecurity,” she talked with Bob Lord, Head of the Consumer Working Group at Hacklore.org. They shared real-world examples of how close calls can be a blessing in disguise for security professionals. In the second session, she discussed how IAM infrastructure can be a helpful incident response tool, even if it requires some hasty retooling.
This session featured a lively conversation between Dave Lewis, 1Password Global Advisory CISO, Nick Fohs, Senior Manager of Enterprise Systems & Security at Reddit, and Ryan Berckmoes, Systems Analyst II at FranklinCovey. They discussed:
The compounding challenges of SaaS and credential sprawl
Balancing the excitement and anxiety of developers adopting agentic workflows
The need for human-centric design to foster secure employee behavior
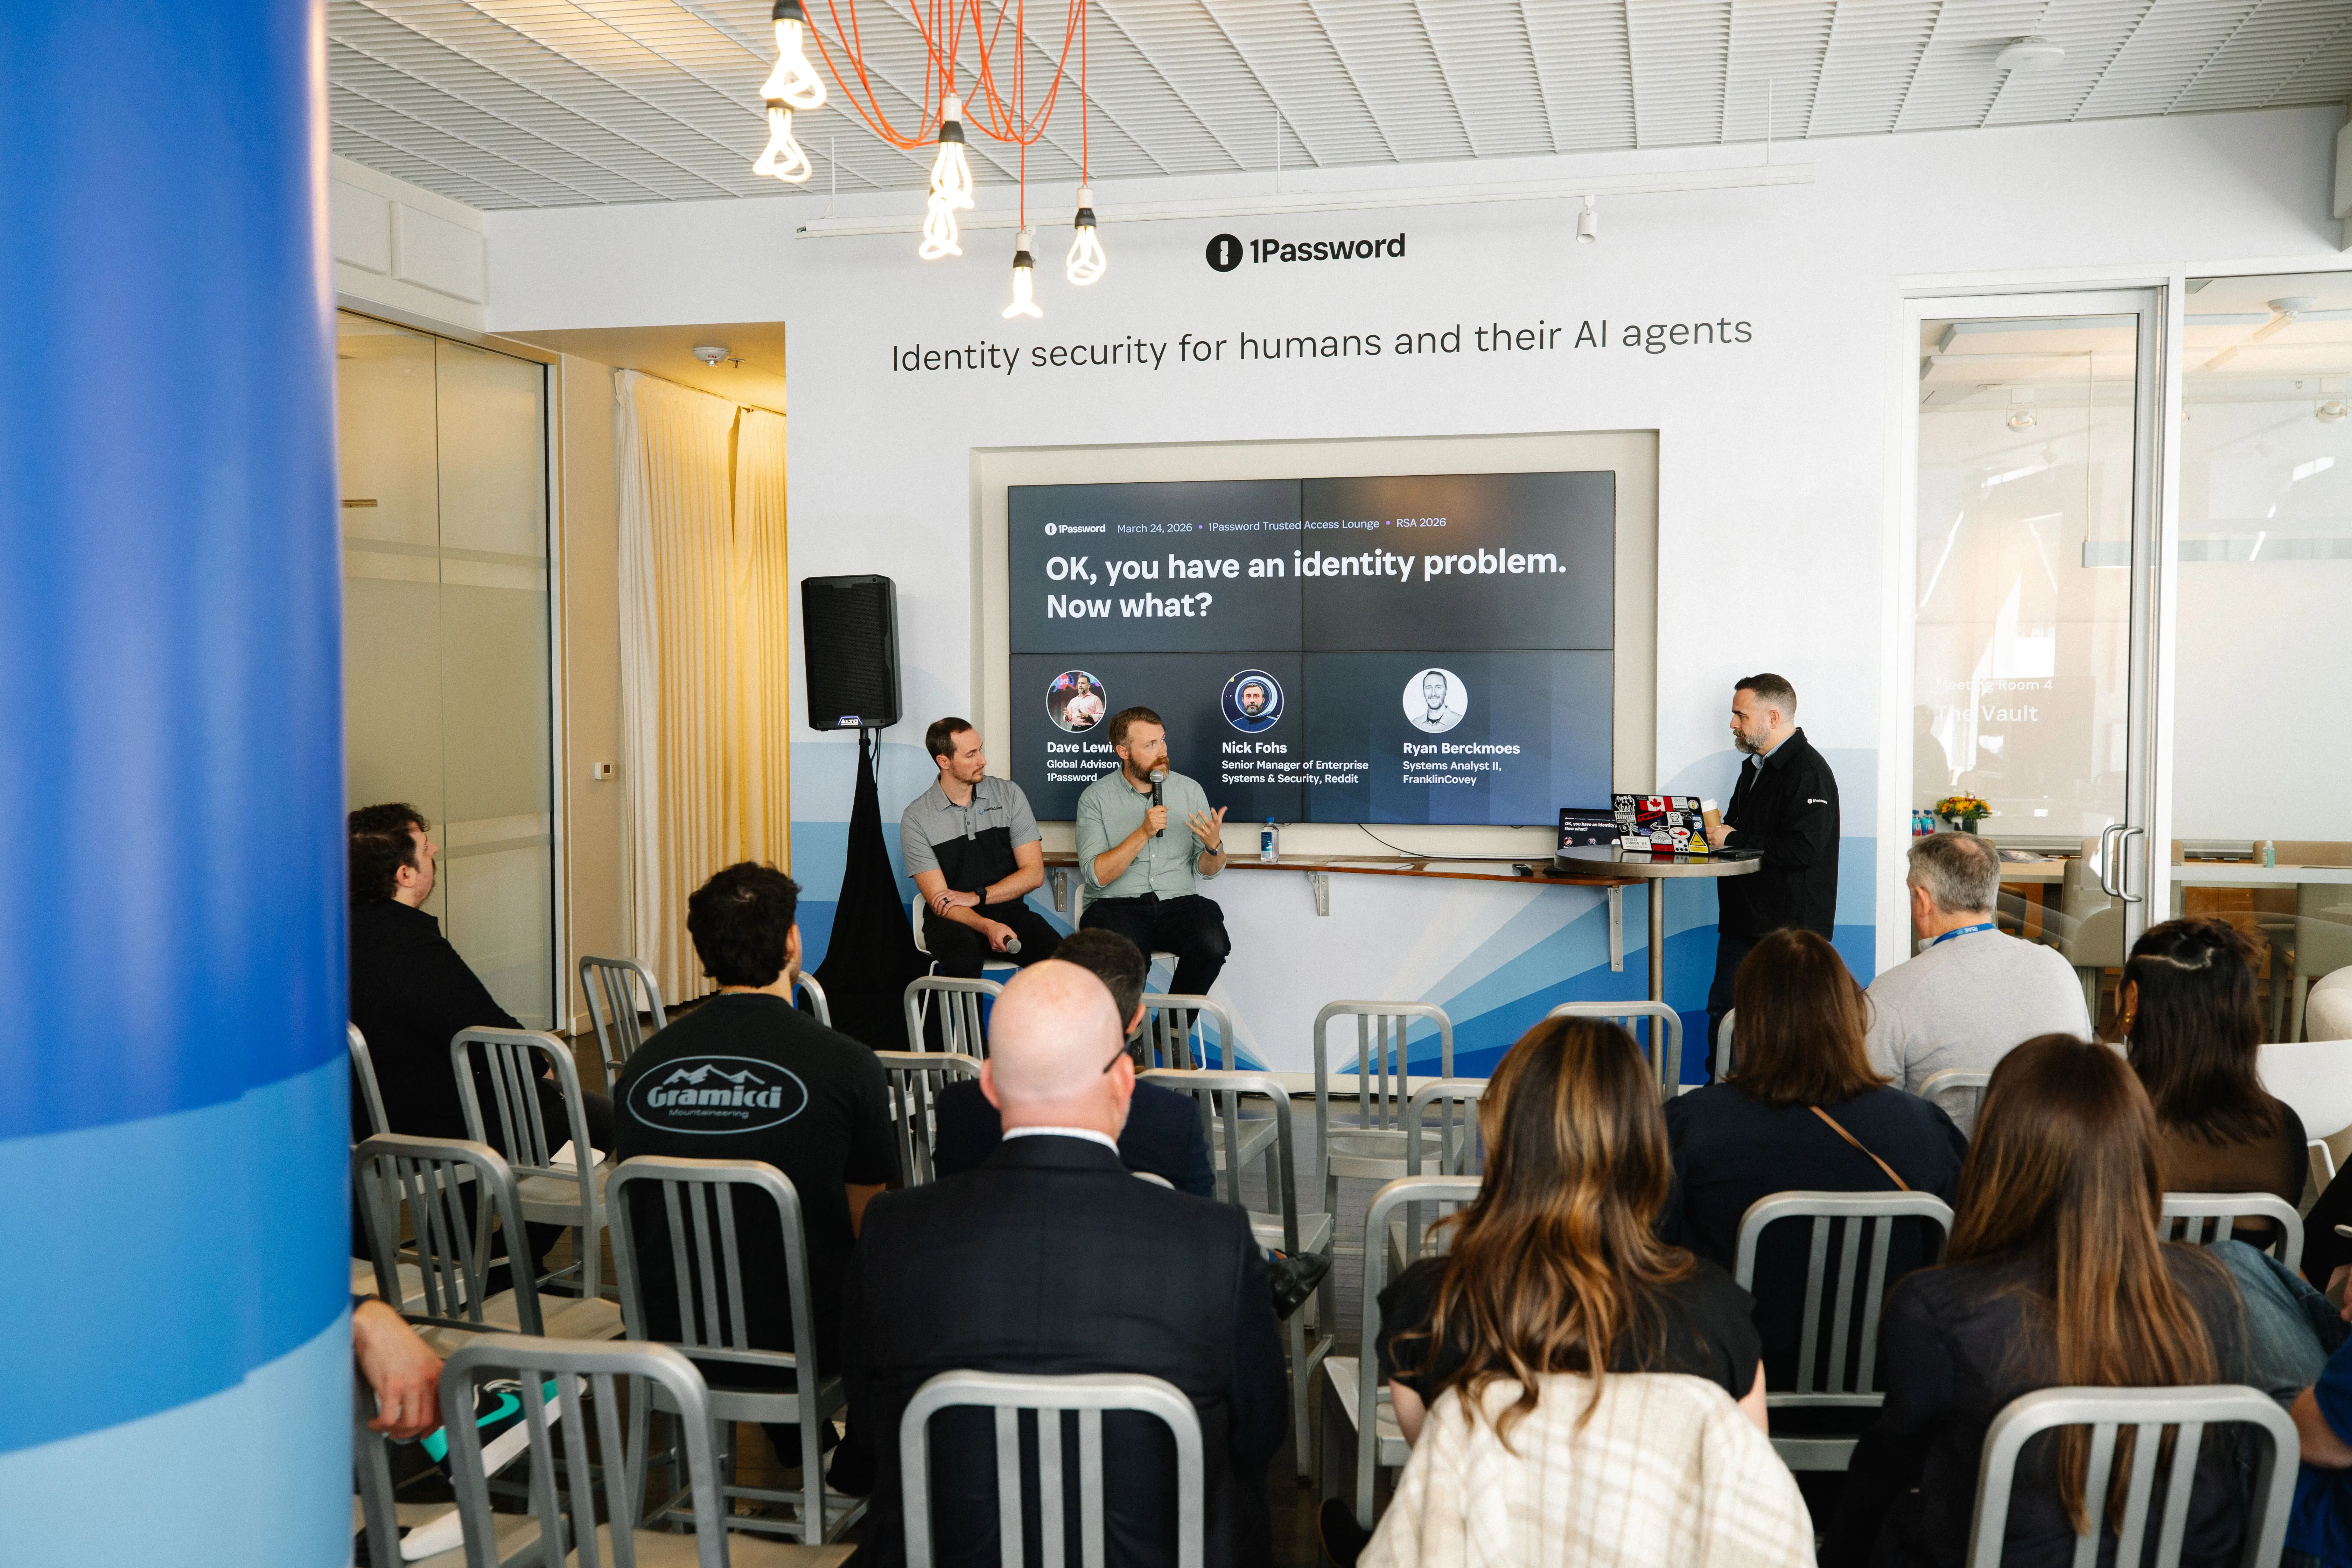
When we look at shadow AI and shadow IT, it’s never adopted out of a sense of malice. These are people literally just trying to get their jobs done. So how do we solve that problem? How do you distinguish acceptable experimentation from risky, unmanaged SaaS applications without being a blocker? You want to try and raise all boats.” - Dave Lewis, Global Advisory CISO, 1Password
Agentic AI permeated every conversation at RSAC 2026, and it was the primary focus of Wednesday's events. Leaders from some of the most trailblazing companies in AI joined 1Password for discussions that ranged from philosophical to highly technical.
In this fireside chat, Jacob DePriest, 1Password CISO and CIO, Sanjay Ramnath, VP of Product Marketing, and Francis Odum, SACR cybersecurity analyst, discussed the rapid evolution of identity security, and what needs to change in order to keep up.
They unpacked about how the access needs of AI agents and NHIs are breaking the traditional login-based authentication model and creating blind spots for security leaders. Francis Odum particularly emphasized the need for the C-Suite to invest in solutions to this problem, rather than waiting for a potentially devastating breach.
I think that the traditional model of login tied to a human is going to just go away. I don’t think we’re going to see that anymore... I think we’re going to see a more continuous model even for humans." -Jacob DePriest, CISO and CIO, 1Password
Next, 1Password’s Jeff Malnick, VP of Engineering, Developer & AI, and Jason Meller, VP of Product, were joined by Travis McPeak, CISO of Cursor, and Tal Peretz, founder of Runlayer.
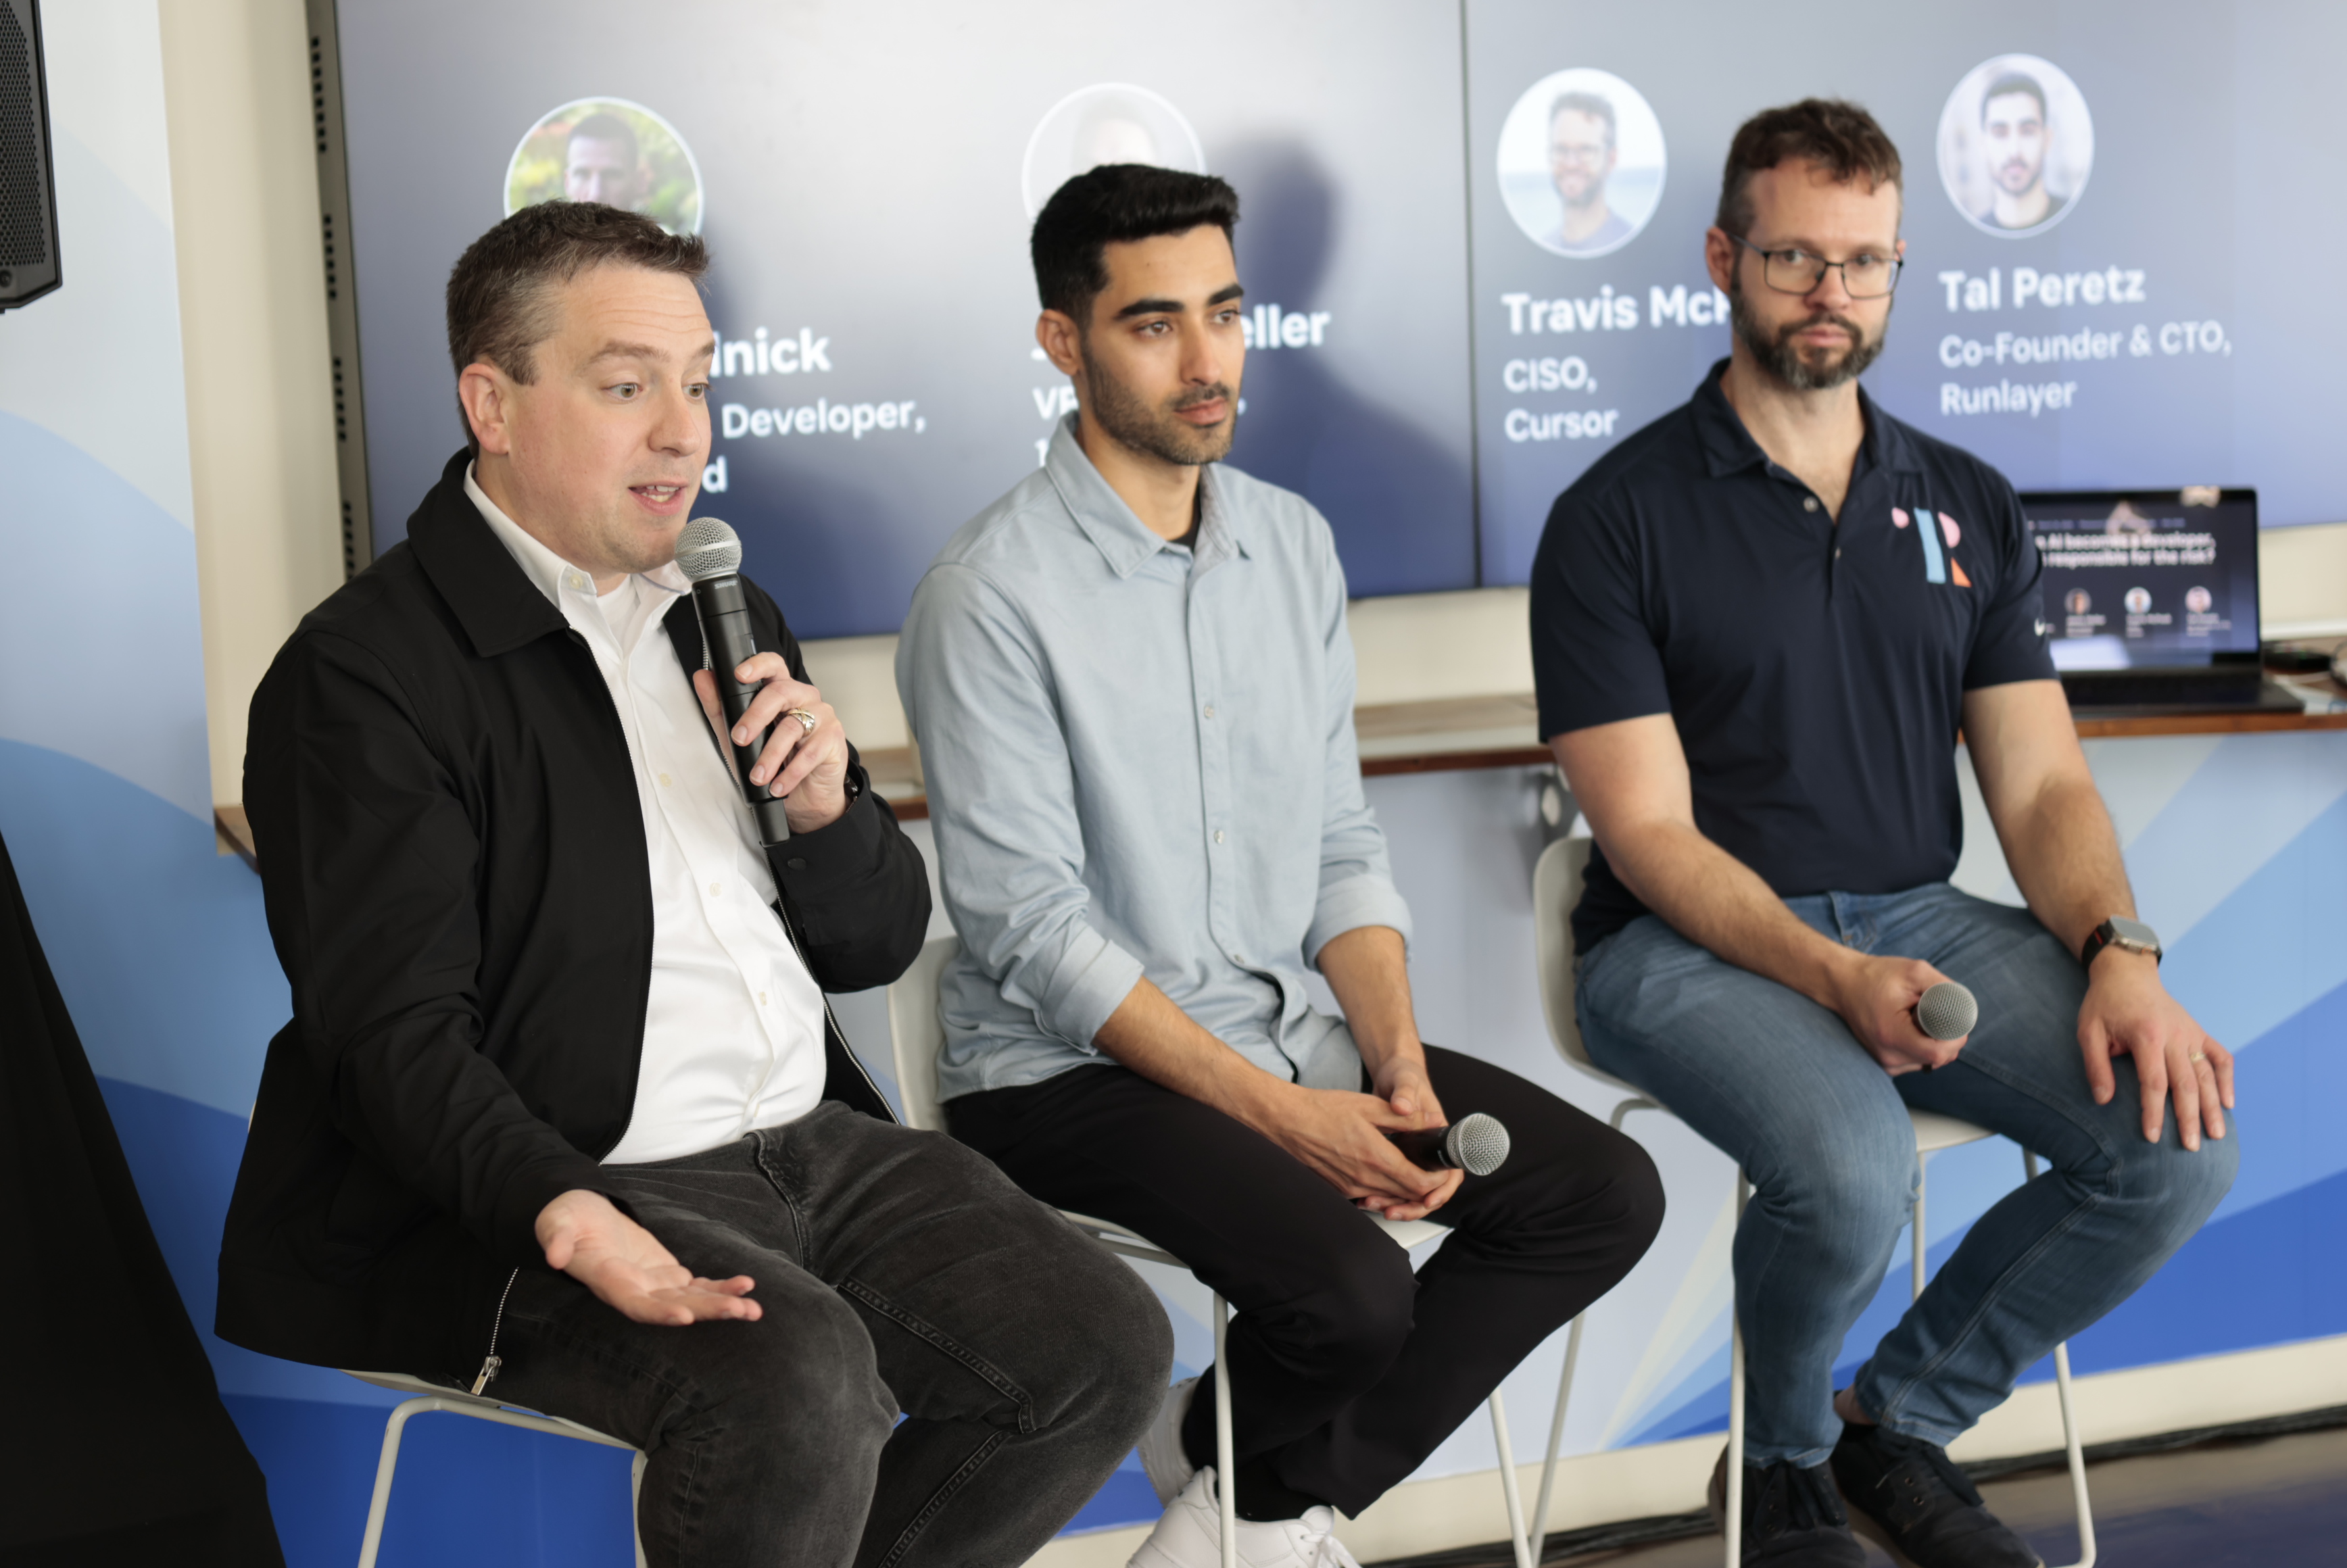
They shared anecdotes of how they’re using agentic AI in their own workflows, considered the future of human vs AI code review, and debated whether AI agents could be considered tools or actors. The eventual consensus was that regardless of how autonomous an agent is on a philosophical level, the ultimate responsibility for their outcomes remains with humans.
I use agents all the time to not only diagnose things but to actually fix them. And I approve every single one of those commands… The reason I approve every single command is if my agent goes nuts or gets prompt injection, like, deletes prod, nobody in the business is going to be under any illusion that it’s the agent’s fault. That’s 100% Travis’s fault.” - Travis McPeak, CISO, Cursor
In this session, Nancy Wang, CTO of 1Password and Fotis Chantzis, Agent Security Lead of Open AI examined why over-permissioning becomes exponentially riskier with always-on AI agents, and how to design time-bound, contextual access controls that enforce security at runtime.
This conversation delved into the details of how to mitigate over-permissioning and context leakage through technical safeguards that ensure agent permissions are timebound, auditable, and tightly-scoped.
The moment that any kind of secret material, credentials, passwords, whatever, that you consider sensitive are part of the context window of the agent, then it’s sort of game over.” – Fotis Chantzis, Security Lead, OpenAI
After a day of deep thinking, everyone was happy to cap things off with an after-conference gathering, where leaders from 1Password, Felicis, and Abnormal networked with RSA attendees.
1Password closed out RSA with more engaging conversations on the conference floor and our ancillary space.
This expert-led discussion on securing the next generation of autonomous AI agents included a host of security leaders: Dave Lewis Global Advisory CISO, 1Password; Steve Ragan, Principal, AI Security Advisory, 1Password; Ryan Marshall, AI Researcher, 1Password; and Rich Mogull, Chief Analyst, CSA.
We’ll end the RSA recap with some reflections from 1Password CEO Dave Faugno on the challenges of managing identities in a world of AI agents. Ultimately, 1Password is uniquely situated to solve those challenges based on the foundation we’ve already built: trusted, secure vaults, our presence on millions of endpoints, and a commitment to balancing security with simplicity.
While this year’s RSA may be over, the months ahead are going to be action-packed for 1Password, as we accelerate our mission to secure access for humans and their agents. The release of Unified Access marked a major milestone for our company, and more are on the way. Stay tuned.
Want to learn more about how 1Password is governing non-human access? Join the AI access shift webinar.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。