


by Robert Boettger | Guest Author
He walked into the lobby with a fake badge clipped to his shirt. He had bought it online the week before. It was not perfect, and it did not need to be. From a few feet away, it looked close enough: a logo, a name, a photo, and a lanyard. The kind of thing most people glance at for half a second before their brain decides, “Looks fine.”
That was all he needed.
He stepped through the front entrance like he had done it a hundred times. Calm, confident, and familiar enough. He smiled at reception, nodded at an employee walking past, and kept moving. Nobody stopped him. Nobody leaned forward to actually look at the badge. Nobody asked who he was there to see. He looked like he belonged. That is where the failure started.
He walked down the hallway and said good morning to two employees passing in the opposite direction. They said good morning back. One of them looked at the badge but did not really read it. The other did not look at all. He stopped at the vending machine, bought a coffee, checked his phone, and stood there for a moment like anyone else taking a break. Nothing about him caused alarm.
A few minutes later, he followed an employee toward a controlled door. The employee badged in, the door unlocked, and they both reached the entrance at almost the same time. The employee glanced back. The man smiled, lifted his drink slightly, and gave a polite nod. “Morning.” The employee smiled back and said, “Morning.” And just like that, he was in.
No force. No alarms. No broken locks. No dramatic breach. Just a door held open by habit and a human being who did not want to create an awkward moment.
He made his way deeper into the building, past offices, conference rooms, and people who were busy, distracted, and comfortable. Eventually, he reached a restricted area where he had no business being. Inside, he found access to equipment that mattered. Maybe it was a server. Maybe it was a workstation used for operations. Maybe it was a system tied to something the organization could not afford to lose. He plugged in a USB device. Then he walked out.
No one noticed. No one stopped him. No one remembered his name. No one could say for sure where he went. Later, when people started asking questions, the answers sounded familiar. “I thought he worked here.” “I saw a badge.” “He looked like he knew where he was going.” “I assumed someone else checked.”
That is the part nobody likes to admit. The attacker did not beat the system. The people inside the building helped him move through it.
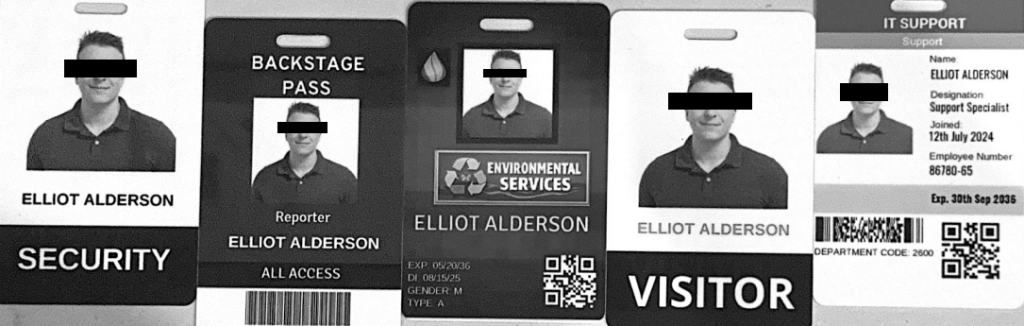
A badge is not decoration. It is not workplace jewelry. It is not a corporate accessory employees wear when convenient and forget when they are busy. A badge is a boundary. It tells everyone in the facility, “This person is authorized to be here right now.” Not yesterday. Not last month. Not before they were fired. Not before their contract ended. Not because people remember their face. Right now.
That distinction matters. Organizations love to talk about security culture, but basic badge discipline is where that culture gets tested. Anyone can say security matters. Anyone can hang posters in the break room or write policy language in an employee handbook. The real test happens at the front door, in the lobby, near the elevator, at the badge reader, and in the hallway when someone without proper identification walks by. That is where security either becomes real or becomes theater.
Most employees are not trying to be careless. They are busy. They are distracted. They do not want conflict. They do not want to seem rude. They do not want to challenge someone who might be important. So they guess. They tell themselves the person probably works there. The visitor is probably with someone. The badge probably looks real. They have probably seen that person before.
“Probably” is not a security control. “Probably” is how people get into places they should never reach.
This is why organizations need to have uncomfortable conversations with employees and managers. Not because security is trying to be difficult. Not because someone enjoys correcting people. Not because badge checks are about power or ego. These conversations matter because people actually care about the place they work. They care about their coworkers, their customers, the building, the equipment, the information, and the mission. They care enough to say something when something does not look right. That is not annoying. That is ownership.
The solution does not need to be complicated. In fact, it should not be. Physical security needs some KISS: Keep It Simple, Stupid rules!
Repeated often, enforced fairly, and practiced until they become normal.
If the badge is not visible, the person should be challenged. Badges should be worn above the waist where people can actually see them. Every person must badge in separately at controlled doors. No piggybacking. No tailgating. No “they’re with me” unless the policy allows it and they are properly escorted.
Visitor badges should be obvious. They should not look almost the same as employee badges. Use a different color, large “VISITOR” wording, date or time expiration, and a simple design that employees can recognize from a distance. If every badge looks the same, employees are being asked to inspect instead of recognize. That slows people down, creates confusion, and gives the wrong person more room to blend in.
Access also must be removed immediately when someone is terminated, resigns, transfers, or finishes a contract. Yesterday’s access cannot become today’s risk. A person who belonged last week may have no reason to be inside the building today.
The back of every badge should include a security contact number. That could be the security desk, SOC, guard force, or emergency contact. Employees should not have to search for who to call when something feels wrong. If you want people to report issues, make reporting easy.
Badge checks should also happen during patrols, but this cannot be only a security officer problem. Everyone has a role. Security can lead the culture, but employees have to live it. Bring people into an open area and run simple mock scenarios. Show them what a badge challenge sounds like. Let them practice saying, “Hi, I don’t see your badge. Can I walk you to the security office?” Make it friendly. Make it normal. Make it expected.
Security teams should test this periodically. Once a month or so, have an approved person walk through a hallway or common area without a visible badge and observe what happens. Who notices? Who says something? Who looks uncomfortable but stays quiet? This should not be used to embarrass people. It should be used to train them, encourage them, and build confidence.
When someone does the right thing, recognize it. Give them credit. Thank them. Hand out challenge coins or small awards to employees who do an exceptional job. The goal is to make badge challenges part of the culture, not something people fear. A strong challenge culture is not hostile. It is professional, friendly, and serious about protecting the workplace.
When the organization wants the highest level of validation, a physical penetration test can show whether the culture actually works. Not in theory. Not on paper. In real conditions. A good test shows whether people challenge, whether doors are controlled, whether visitor processes hold up, and whether the badge program is more than plastic and policy.
A real badge program only works when people are willing to enforce it. If employees do not look for badges, the badge does not matter. If leaders walk around without badges and expect special treatment, the badge policy does not matter. At that point, the badge program is not security. It is theater.
And attackers love theater.
They love organizations where people look the part but do not enforce the rules. They love doors where employees hold them open without thinking. They love lobbies where visitors are loosely managed. They love hallways where people assume someone else already checked. They love executives who believe security policy is for everyone beneath them.
From the CEO down — especially from the CEO down — the rule has to be visible, enforced, and respected. If leadership treats the badge like a suggestion, everyone else will too. And once that happens, the building is no longer protected by policy. It is protected by luck.
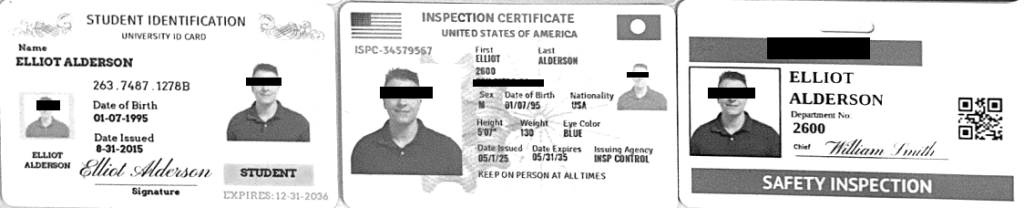
The art of the badge is not complicated. That is exactly why it gets ignored. It feels too basic, too small, too obvious. But physical security usually fails in the ordinary moments people excuse every day: one door held open, one badge turned backward, one fake badge accepted, one familiar face waved through, one employee who noticed and said nothing.
Every time someone sees it, ignores it, challenges it, or respects it, they are deciding what kind of security culture they actually work in.
And the wrong person only needs that decision to go their way once.
Explore the Infosec Survival Guide and more… for FREE!
Get instant access to all issues of the Infosec Survival Guide, as well as content like our self-published infosec zine, PROMPT#, and exclusive Darknet Diaries comics—all available at no cost.
You can check out all current and upcoming issues here: https://www.blackhillsinfosec.com/prompt-zine/
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。