


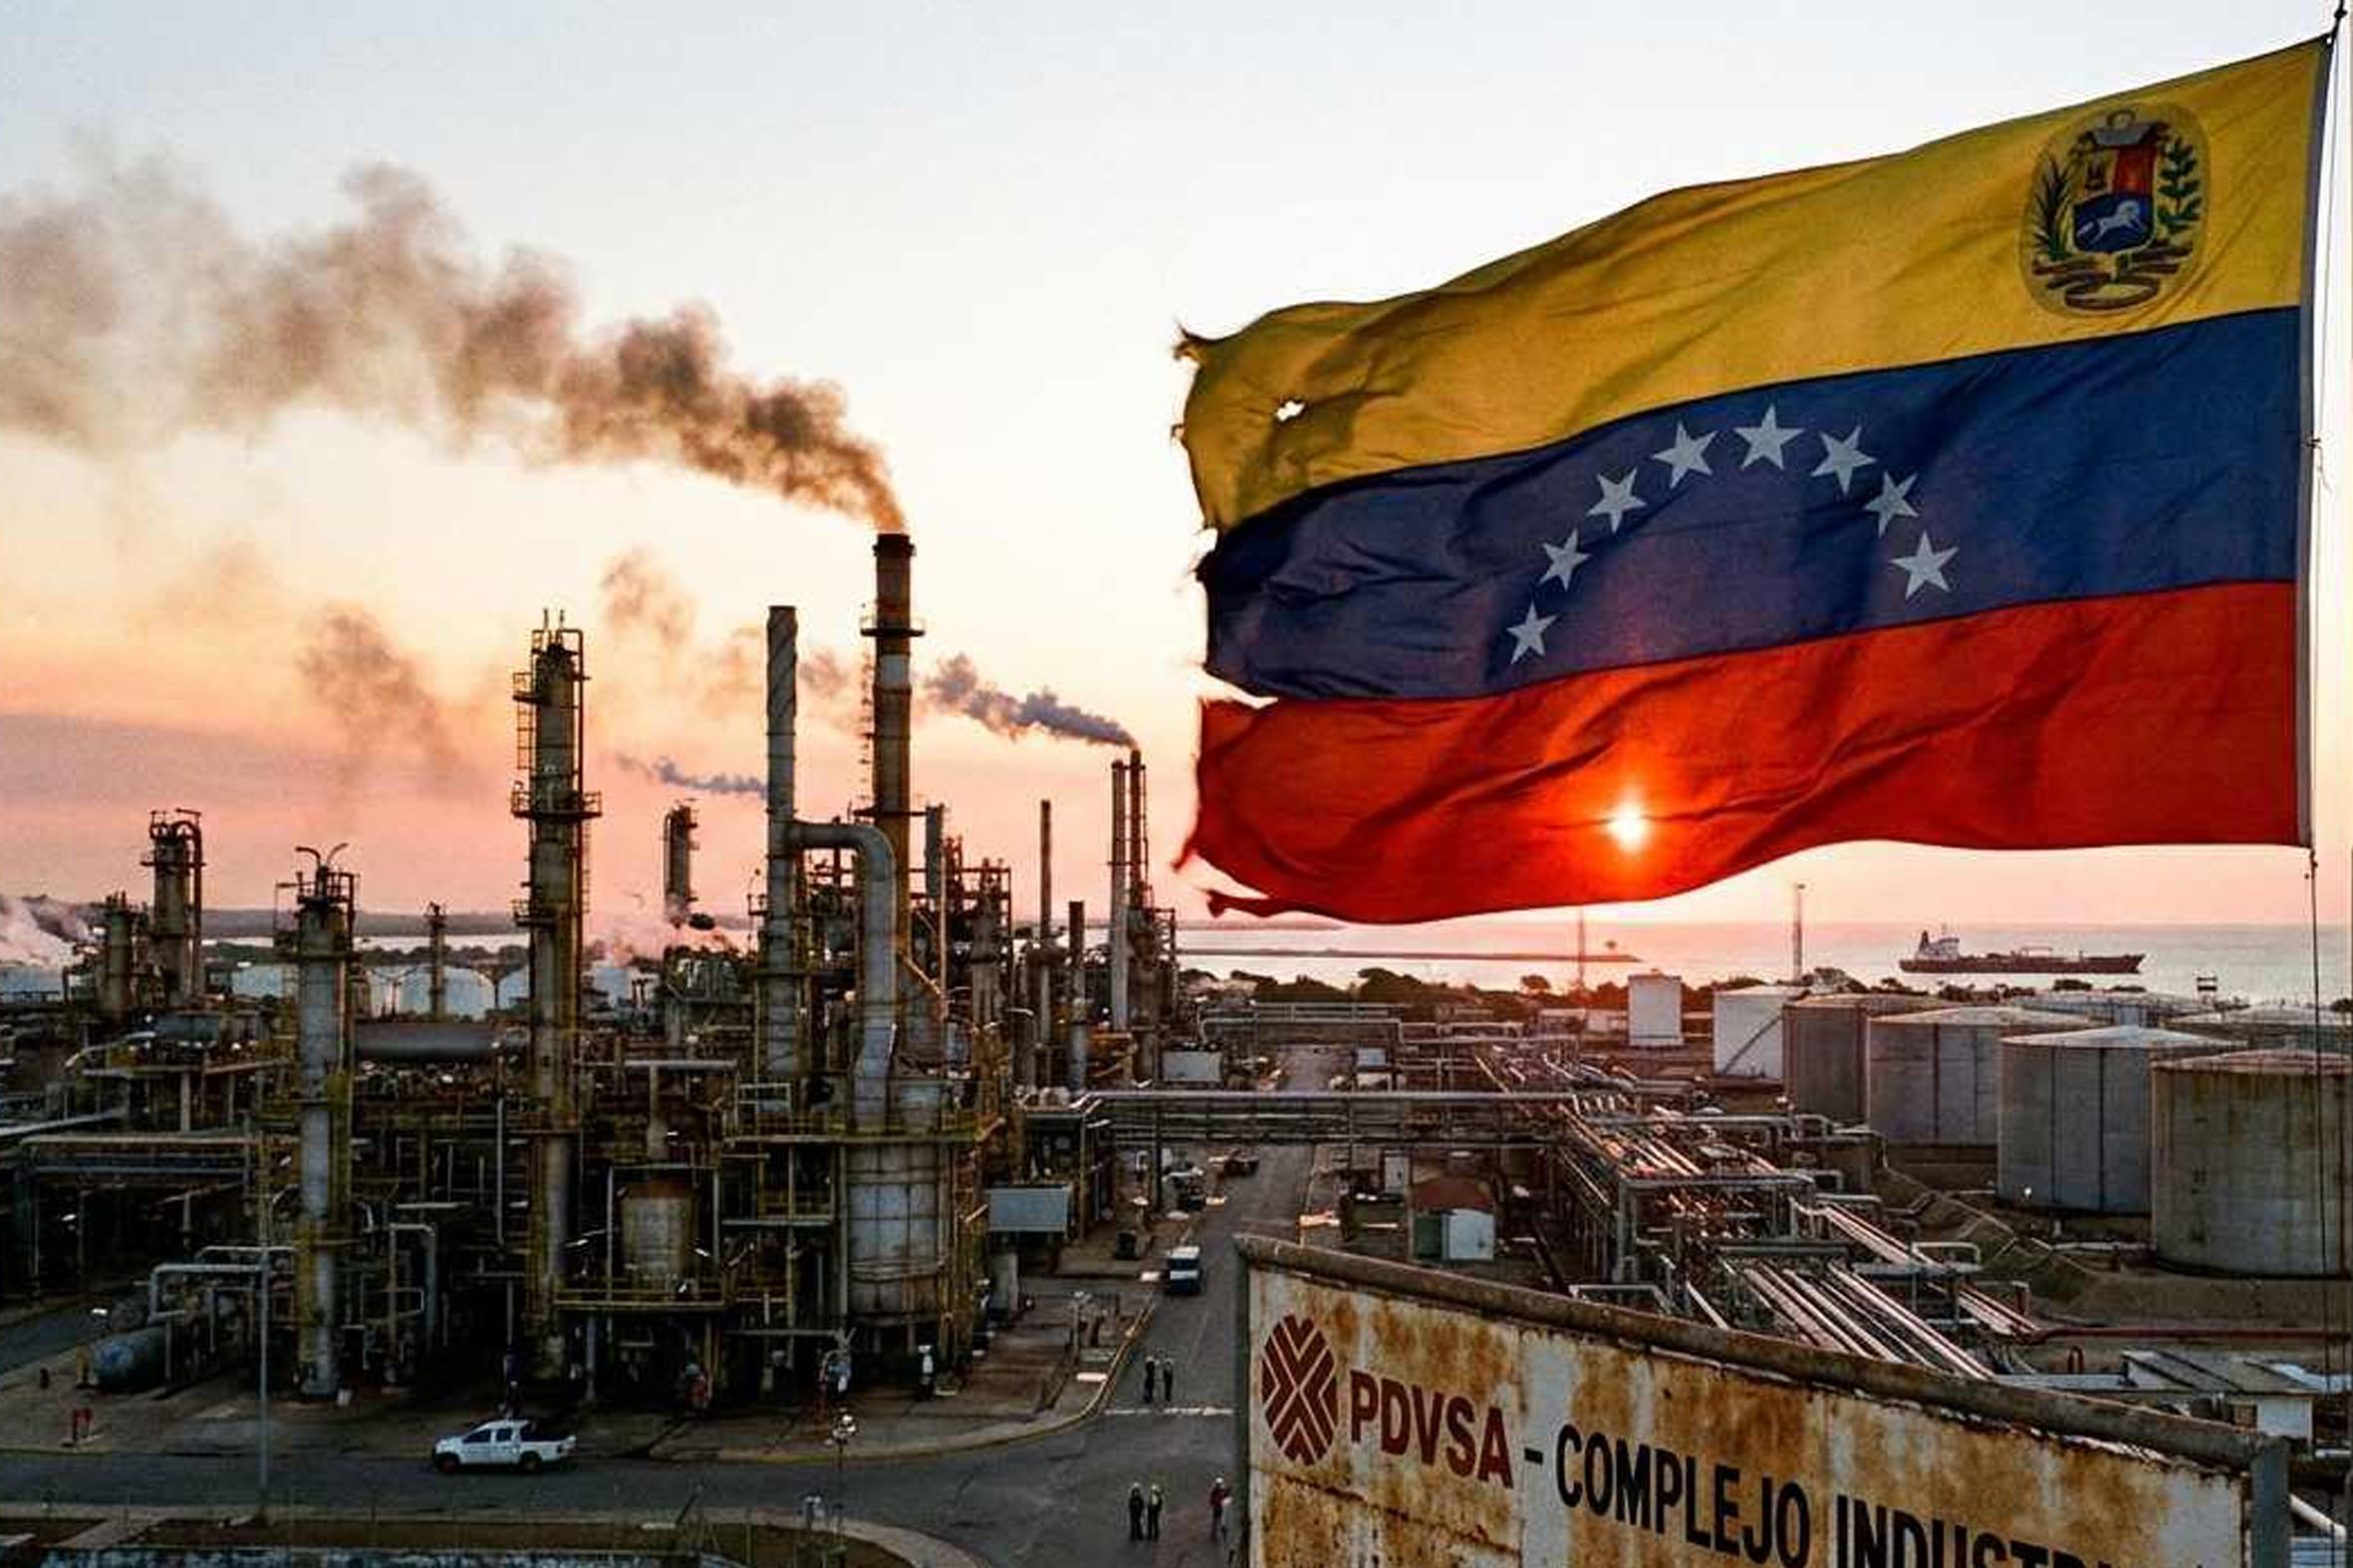
Kaspersky researchers found Lotus Wiper targeting Venezuela’s energy and utilities sector amid regional tensions in 2025–2026. Attackers first used batch scripts to weaken systems, disable defenses, and prepare the environment.
Then they deployed the wiper, which erased recovery tools, overwrote disks, and deleted all files, leaving systems unusable.
“Two batch scripts are responsible for initiating the destructive phase of the attack and preparing the environment for executing the final wiper payload. These scripts coordinate the start of the operation across the network, weaken system defenses, and disrupt normal operations before retrieving, deobfuscating and executing a previously unknown wiper that we dubbed ‘Lotus Wiper’.” reads the report published by Kaspersky. “The wiper removes recovery mechanisms, overwrites the content of physical drives, and systematically deletes files across affected volumes, ultimately leaving the system in an unrecoverable state.”
The researchers pointed out that no ransom demand appeared, showing that the malware was developed with a destructive purpose rather than profit. The campaign looks highly targeted and designed to permanently disrupt critical infrastructure.
The attack chain begins with a batch file called OhSyncNow.bat. It checks specific folders and network shares, then uses a hidden XML file as a trigger to decide whether to continue. If the conditions are met, it runs a second script that prepares the system for destruction.
In the next stage, the malware disables user accounts, forces active logoffs, blocks cached logins, and shuts down network interfaces to isolate the machine. It then searches all disk drives and runs destructive commands like diskpart clean all, which overwrites entire volumes and permanently deletes data.
The script also spreads across directories using file mirroring techniques, overwriting or removing content on a large scale. It then fills remaining disk space with large files to prevent recovery or forensic analysis.
Finally, it launches disguised system-like executables that hide as legitimate software components. These files load the final payload, known as Lotus Wiper, which completes the attack by erasing all remaining data and leaving the system completely unrecoverable.
The final stage of the attack runs the Lotus Wiper implant. A system-like executable first decrypts a hidden payload and prepares it for execution. Then the wiper starts with elevated privileges already present on the system. It removes Windows restore points to block recovery and then begins destroying data.
It wipes all physical disks by writing zeroes across every sector, making recovery impossible. It also clears system logs and update journals to erase traces of activity.
“In between waves of wiping physical drives, Lotus Wiper makes use of FindFirstVolumeW and then FindNextVolumeW, to identify each mounted volume.” continues the report. “It sends the volumes to a new thread that performs two wiping actions: deleting all the system’s files and clearing the volume’s change journal.”
Next, it scans all mounted volumes, deletes files, and corrupts file records. It overwrites file contents with zeroes, renames files with random names, and forces deletion. If a file is locked, it schedules removal on reboot.
The wiper repeats disk destruction multiple times and updates system disk properties to ensure changes persist. In the end, it fully erases data across drives and volumes, leaving the system permanently unusable.
Businesses and government bodies should audit permissions on domain shares and monitor NETLOGON for unauthorized changes, since shared files can trigger coordinated attacks across systems. The wiper requires elevated privileges, often gained after attackers move from low-level accounts to higher access.
Security teams should watch for token abuse, credential theft, and privilege escalation in logs. They must also detect unusual use of built-in tools like fsutil, robocopy, and diskpart, commonly used in “living off the land” attacks. Strong backup testing and recovery planning are essential to ensure systems and data can be restored after destructive incidents.
“An essential detail about the presence of Lotus Wiper attackers in the environment is revealed by the batch scripts. Given that the files included certain functionalities targeting older versions of the Windows operating system, the attackers likely had knowledge of the environment and compromised the domain long before the attack occurred.” conlcudes the report. “Moreover, we observed that Lotus Wiper was compiled in late September 2025, while the sample was uploaded to a publicly available resource in mid-December of that year. Prior to this, the malware had not been used in any other attacks. Assuming the compilation time of the PE file has not been altered, this indicates that the attacker had been preparing for this attack for several months.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, wiper)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。