









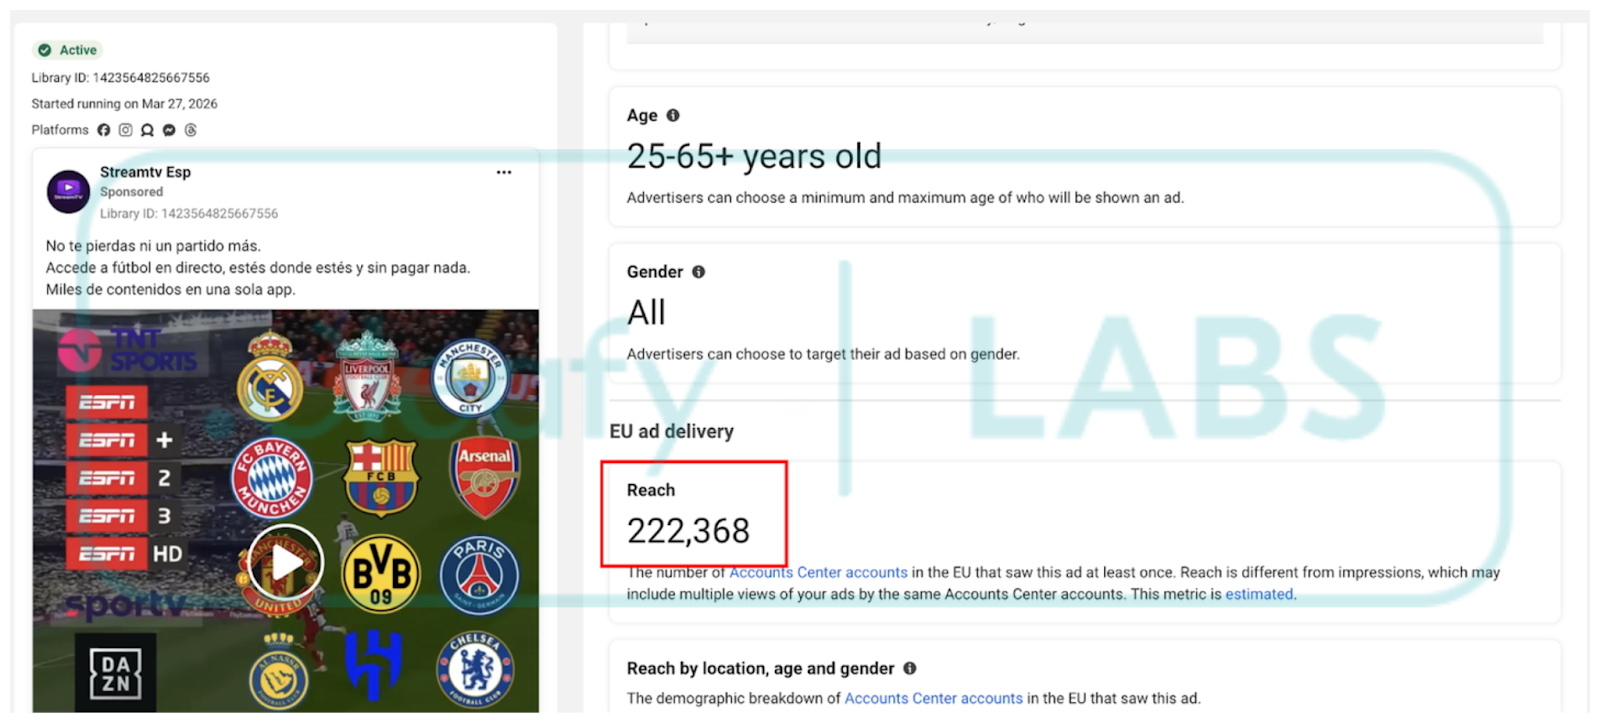
Mirax is a new Android remote access trojan spreading through ads on Meta platforms, targeting mainly Spanish-speaking users and reaching over 220,000 accounts. The malicious code lets attackers fully control infected devices in real time and goes further by turning them into SOCKS5 proxy nodes, routing malicious traffic through victims’ IPs.
The Android RAT is sold as malware-as-a-service, and shows how mobile threats are evolving in scale and sophistication.
“Mirax is a newly identified Android Remote Access Trojan (RAT) and banking malware that has rapidly gained traction within the cybercriminal ecosystem. Publicly promoted on underground forums since December 19, 2025, it has been actively monitored by the Cleafy Threat Intelligence team since March 2026, when multiple campaigns targeting primarily Spanish-speaking regions were observed.” reads the report published by Cleafy. “Unlike typical MaaS offerings, Mirax is distributed through a highly controlled and exclusive model, limited to a small number of affiliates. “
Mirax is distributed through a multi-stage campaign using Meta ads on platforms like Facebook and Instagram to lure users into downloading malicious apps. Victims are redirected to phishing sites offering fake services, such as illegal sports streaming apps, exploiting users’ привычка to sideload APKs. The sites restrict access to mobile devices to avoid detection.

The malware is delivered via droppers hosted on GitHub Releases, frequently updated and repacked to evade security checks. Once installed, the dropper unpacks the payload, applies strong obfuscation, and connects via WebSockets. Attackers also reuse existing GitHub releases instead of creating new ones, making detection harder.
The campaign reached over 200,000 users and reflects a growing trend of abusing legitimate platforms, combining social engineering, evasive techniques, and scalable distribution methods.

Mirax uses a two-stage infection chain with a dropper designed to hide the real malware and its permissions. The malicious code is disguised as an IPTV app and tricks users into enabling installation from unknown sources. The dropper contains an encrypted .dex file hidden deep in the app structure, using obfuscation and uncommon paths to evade analysis. Once executed, it extracts and decrypts the payload using RC4 with a hardcoded key, revealing the malicious code.
The final payload is another encrypted APK stored inside the app, decrypted via XOR and then installed. In some cases, it could also be downloaded remotely. The malware relies on packers like Golden Encryption to avoid detection and uses dynamic loading to stay hidden.
“One interesting section of the documentation explains the different packer options that the builder offers: Virbox and Golden Encryption. While the former is easy to detect thanks to multiple indicators in the code, Golden Encryption (also known as Golden Crypt) is not well documented but is widely used and promoted on underground malware forums.” continues the report. “This packer was also used in Albiriox“.
After installation, it poses as a video app and requests Accessibility permissions. Once granted, it runs in the background, displays fake error pages, and uses overlays to bypass security controls and maintain persistence.
After installation, the malware mimics a video app and requests Accessibility permissions to gain control.
With these permissions, Mirax runs silently, using overlays and fake pages to steal credentials and bypass protections. It offers full RAT capabilities, including screen control, data theft, app management, and spyware functions.
It communicates with command-and-control servers via WebSockets, enabling real-time control and data exfiltration. A key feature is its ability to turn infected devices into SOCKS5 residential proxies, masking attacker activity and enabling broader attacks like fraud, lateral movement, and DDoS.
Mirax highlights the evolution of Android malware, shifting from broad malware-as-a-service to a more restricted “private MaaS” model. By limiting access to trusted actors, attackers reduce the risk of leaks and detection. This approach allows the malware to operate more stealthily and remain active for longer periods without attracting attention.
Attackers abuse trusted platforms to spread malware at scale, using evasion tricks to bypass detection and reach hundreds of thousands of users quickly.
“The introduction of SOCKS5 and residential proxy functionality into an Android RAT is groundbreaking for several reasons. Firstly, malware developers recognize the profitability of residential proxies, as they can obscure the origin IP address, making it appear to originate from legitimate subnets.” concludes the report. “Furthermore, a residential proxy application needs fewer permissions than a Remote Access Trojan (RAT). This reduced requirement allows the threat actor to deploy it even if the full infection process is incomplete. Consequently, the actor avoids losing these devices entirely and can maintain their inclusion in the botnet.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Mirax Android RAT)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。