
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Microsoft Azure Blog
aimingoo的专栏
aimingoo的专栏
F
Fortinet All Blogs
Blog — PlanetScale
Blog — PlanetScale
GbyAI
GbyAI
MongoDB | Blog
MongoDB | Blog
月光博客
月光博客
The Cloudflare Blog
量子位
T
Tailwind CSS Blog
Cyber Security Advisories - MS-ISAC
B
Blog
MyScale Blog
MyScale Blog
T
The Blog of Author Tim Ferriss
The GitHub Blog
The GitHub Blog
G
Google Developers Blog
D
DataBreaches.Net
V
Visual Studio Blog
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
Last Week in AI
Last Week in AI
U
Unit 42
博客园 - 聂微东
有赞技术团队
有赞技术团队
A
About on SuperTechFans

Security Affairs

Copy Fail: New Linux bug enables Root via page‑cache corruption Agent’s claims on WhatsApp access spark security concerns Meta accused of violating DSA by failing to safeguard minors Large-scale Roblox hacking operation shut down by Ukrainian authorities CVE-2026-42208: LiteLLM bug exploited 36 hours after its disclosure Internet censorship index reveals Russia’s lead and widespread content blocking All supported cPanel versions hit by critical auth bug, now patched U.S. CISA adds Microsoft Windows Shell and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities catalog ShinyHunters exploit Anodot incident to target Vimeo CVE-2026-3854 GitHub flaw enables remote code execution Signal Phishing Campaign Targets German Officials in Suspected Russian Operation Microsoft fixes Entra ID flaw enabling privilege escalation New Android spyware Morpheus linked to Italian surveillance firm NCSC launches SilentGlass, a plug-in device to secure HDMI and DisplayPort links Medtronic discloses security incident after ShinyHunters claimed theft of 9M+ records Chinese spy posed as researcher in spear-phishing campaign targeting NASA to steal defense software LINKEDIN BROWSERGATE Firefox bug CVE-2026-6770 enabled cross-site tracking and Tor fingerprinting Fast16: Pre-Stuxnet malware that targeted precision engineering software Italy moves to extradite Chinese national to the U.S. over hacking charges U.S. utility giant Itron discloses a security breach Critical bug in CrowdStrike LogScale let attackers access files GopherWhisper: new China-linked APT targets Mongolia with Go-based malware SECURITY AFFAIRS MALWARE NEWSLETTER ROUND 94 Trigona ransomware adopts custom tool to steal data and evade detection Security Affairs newsletter Round 574 by Pierluigi Paganini – INTERNATIONAL EDITION U.S. CISA adds SimpleHelp, Samsung, and D-Link flaws to its Known Exploited Vulnerabilities catalog Over 400,000 sites at risk as hackers exploit Breeze Cache plugin flaw (CVE-2026-3844) CISA reports persistent FIRESTARTER backdoor on Cisco ASA device in federal network 12-year-old Pack2TheRoot bug lets Linux users gain root privileges
Operation PowerOFF: 53 DDoS domains seized and 3 Million ...
Pierluigi Pa · 2026-04-17 · via Security Affairs

Operation PowerOFF shut down 53 DDoS-for-hire domains, arrested four suspects, and exposed data on over 3 million criminal user accounts.

Operation PowerOFF is an international law enforcement action that dismantled 53 domains linked to DDoS-for-hire services used by over 75,000 cybercriminals. Authorities arrested four suspects, seized infrastructure, and gained access to databases containing more than 3 million user accounts. They are now warning identified users, while continuing investigations with multiple search warrants.

DDoS-for-hire services, or “booters,” are illegal platforms that let users pay to launch DDoS attacks that flood websites or servers with traffic, causing outages. They are used for harassment, extortion, or disruption and can lead to serious legal consequences for users.

“On 13 April 2026, 21 countries joined forces in a coordinated action week that focused on enforcement and prevention measures against over 75 000 criminal users engaging in distributed denial-of-service (DDoS)-for-hire services.” reads the press release published by EUROPOL. “With over 75 000 warning emails and letters being sent to identified criminal users and 4 arrests, the action week also led to the takedown of 53 domains and the issuing of 25 search warrants.”

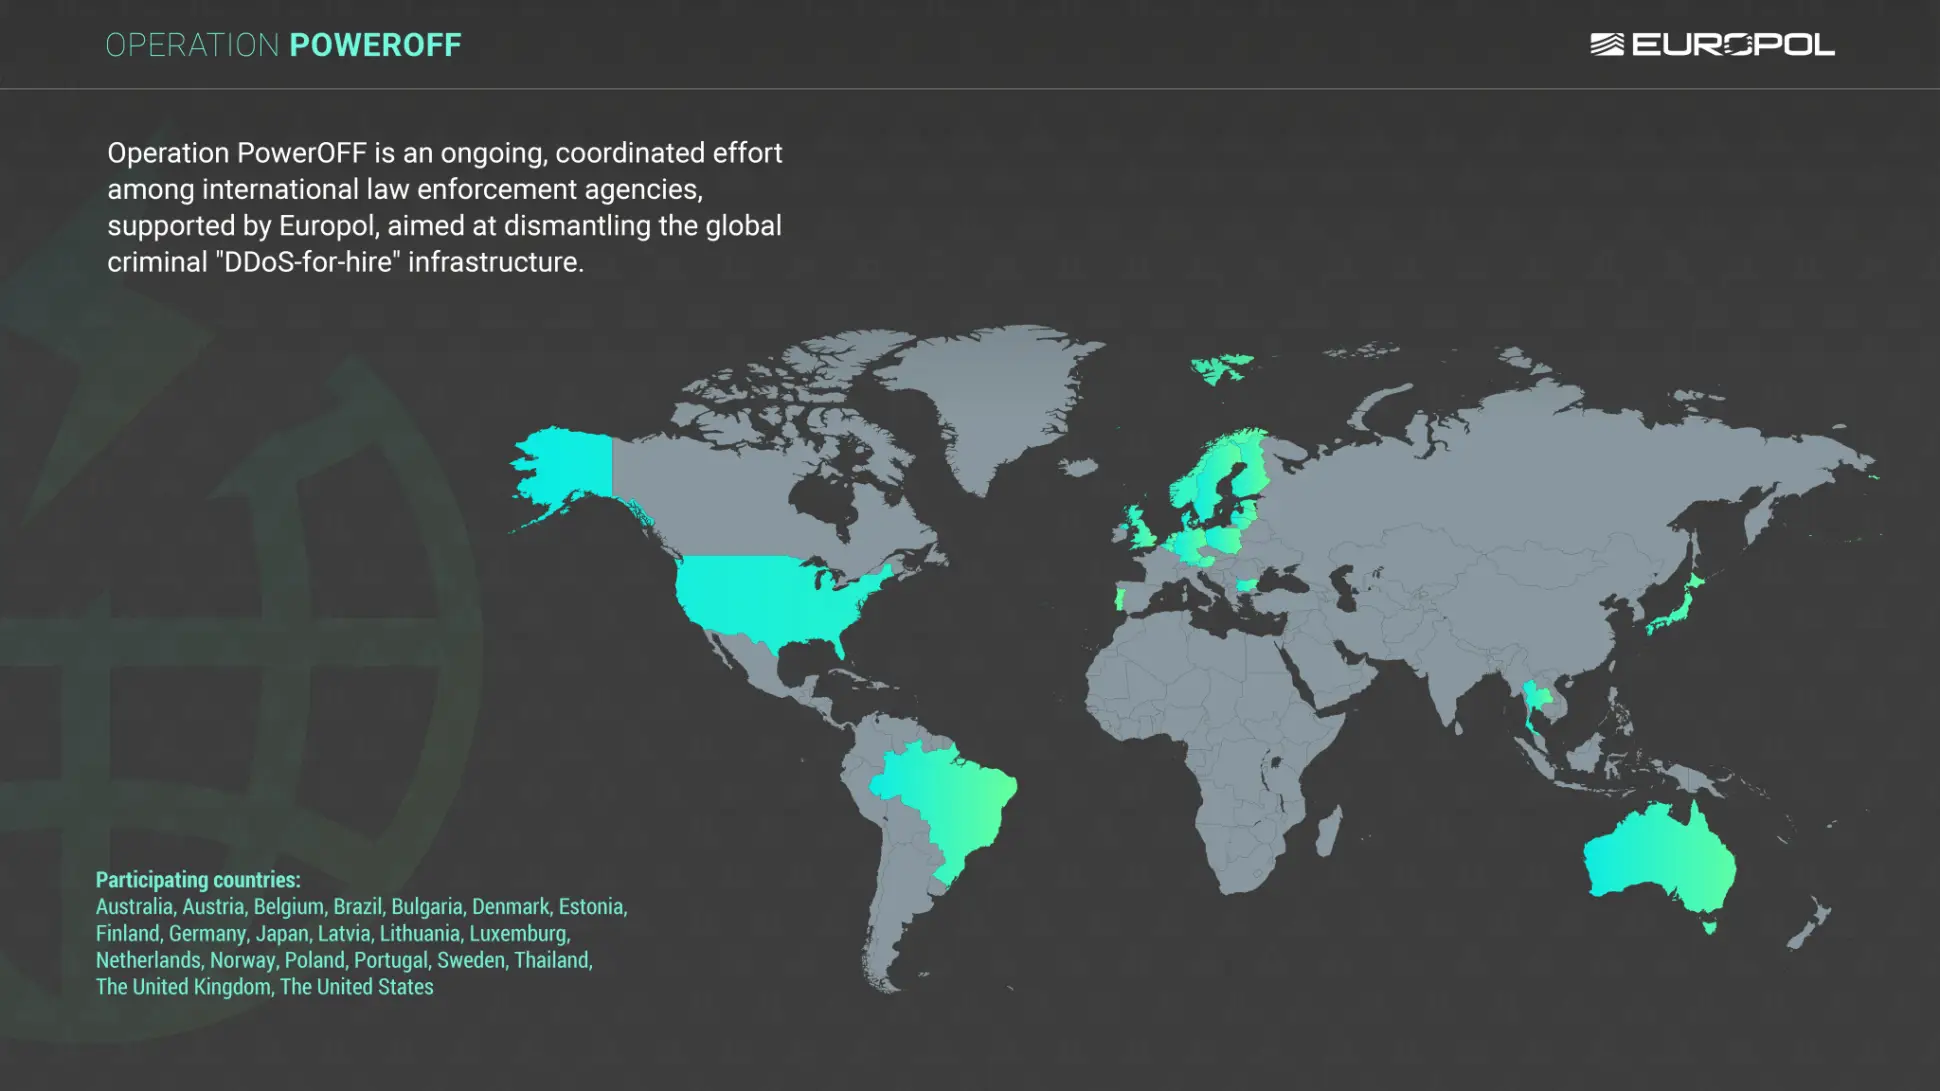
21 countries participated in the law enforcement operation PowerOFF: Australia, Austria, Belgium, Brazil, Bulgaria, Denmark, Estonia, Finland, Germany, Japan, Latvia, Lithuania, Luxembourg, the Netherlands, Poland, Portugal, Sweden, Thailand, the U.K., and the U.S.

Authorities disrupted booter services by seizing servers and infrastructure used to launch attacks, limiting further harm. Access to seized databases with over 3 million user accounts enabled coordinated global actions against cybercriminals and raised awareness about the illegality of these services.

Operation PowerOFF continues with a strong prevention phase to stop future DDoS attacks. Authorities launched campaigns targeting users, including ads warning young people searching for attack tools, removal of over 100 malicious URLs, and warning messages sent via blockchains used for payments. They also updated the official website to highlight ongoing actions and raise awareness about the risks and illegality of DDoS-for-hire services.

Authorities continue dismantling global DDoS-for-hire networks under Operation PowerOFF. In August 2025, the U.S. also took down the RapperBot botnet, used for large-scale attacks across more than 80 countries since 2021.

In December 2024, law enforcement agencies operating under Operation PowerOFF disrupted 27 of the most popular platforms (including zdstresser.net, orbitalstress.net, and starkstresser.net) to launch Distributed Denial-of-Service (DDoS) attacks. The authorities also arrested three administrators of these platforms in France and Germany, and identified over 300 users.

Pierluigi Paganini

Follow me on Twitter: @securityaffairs and Facebook and Mastodon

(SecurityAffairs – hacking, Operation PowerOFF)