


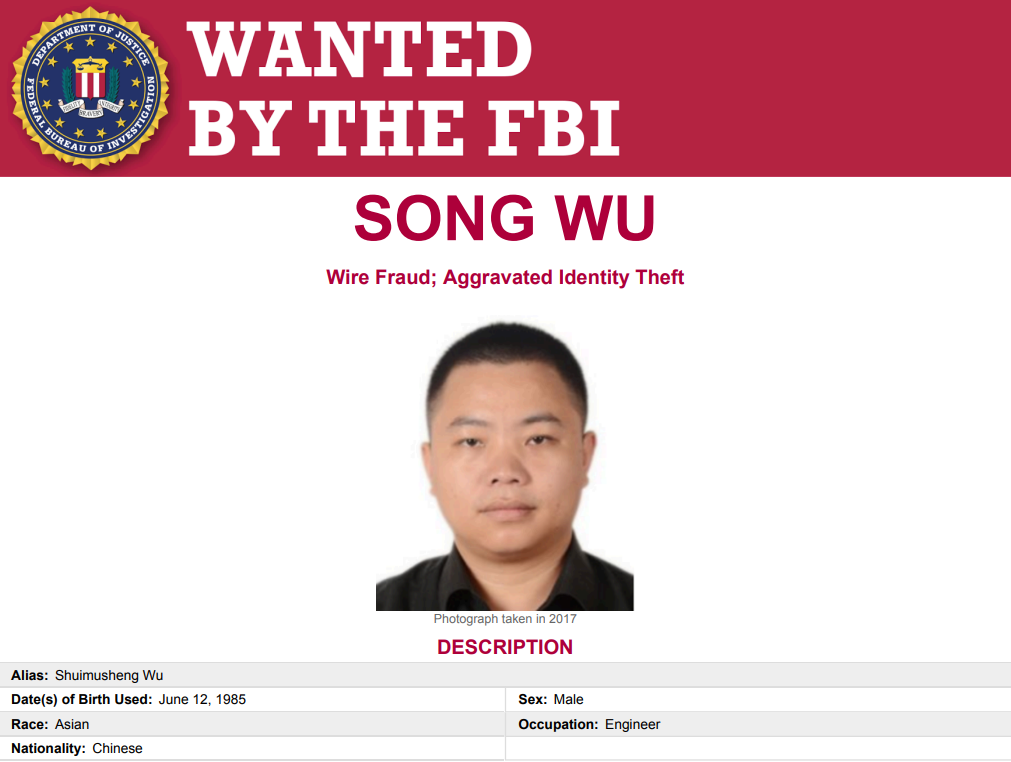
A Chinese national ran a spear-phishing campaign by posing as a U.S. researcher and tricked NASA employees into sharing sensitive information. The NASA Office of Inspector General (OIG) and federal partners discovered the scheme that also targeted government agencies, universities, and private firms.
U.S. export controls limit sharing sensitive technology, and NASA’s OIG enforces them to protect critical data and defense-related assets. Investigators uncovered a long-running phishing scheme in which Chinese national Song Wu impersonated a trusted aerospace professor to trick targets into sharing export-controlled software and source code. Between 2017 and 2021, he targeted dozens of victims across NASA, the U.S. military, government agencies, universities, and private firms.
“According to U.S. Attorney Buchanan, the indictment, and other information presented in court: Song allegedly engaged in a multi-year “spear phishing” email campaign in which he created email accounts to impersonate U.S.-based researchers and engineers and then used those imposter accounts to obtain specialized restricted or proprietary software used for aerospace engineering and computational fluid dynamics.” reads the press release published by DoJ in 2024. “This specialized software could be used for industrial and military applications, such as development of advanced tactical missiles and aerodynamic design and assessment of weapons.”
While carrying out spear phishing attacks, Song was employed as an engineer at Aviation Industry Corporation of China (“AVIC”), a Chinese state-owned aerospace and defense conglomerate headquartered. AVIC is one of the largest defense contractors in the world.
Song faces charges for wire fraud and aggravated identity theft, with up to 20 years per fraud count plus a 2-year sentence for identity theft. He remains at large.
“In September of 2024, following a joint investigation by NASA OIG and the Federal Bureau of Investigation, Song was indicted on 14 counts of wire fraud and 14 counts of aggravated identity theft.” reads the press release published by the OIG. “He faces a maximum sentence of 20 years in prison for each count of wire fraud, and a two-year consecutive sentence if convicted of aggravated identity theft. He remains at large and there is a federal warrant for his arrest.”

NASA OIG warns that export control compliance and vigilance in daily emails are critical to protect sensitive technology. In the Song Wu case, red flags included repeated requests for the same software, unclear justifications, unusual payments, and attempts to hide identity or bypass restrictions. By identifying and prosecuting such schemes, OIG helps safeguard research, national security, and economic interests.
“Song Wu is wanted for wire fraud and aggravated identity theft arising from his alleged efforts to fraudulently obtain computer software and source code created by the National Aeronautics and Space Administration (NASA), research universities, and private companies.” reads the statement published by the FBI on the U.S. Most Wanted List. “The specialized software could be used for industrial and military applications, such as development of advanced tactical missiles and aerodynamic design and assessment of weapons.”
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, spear-phishing)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。