


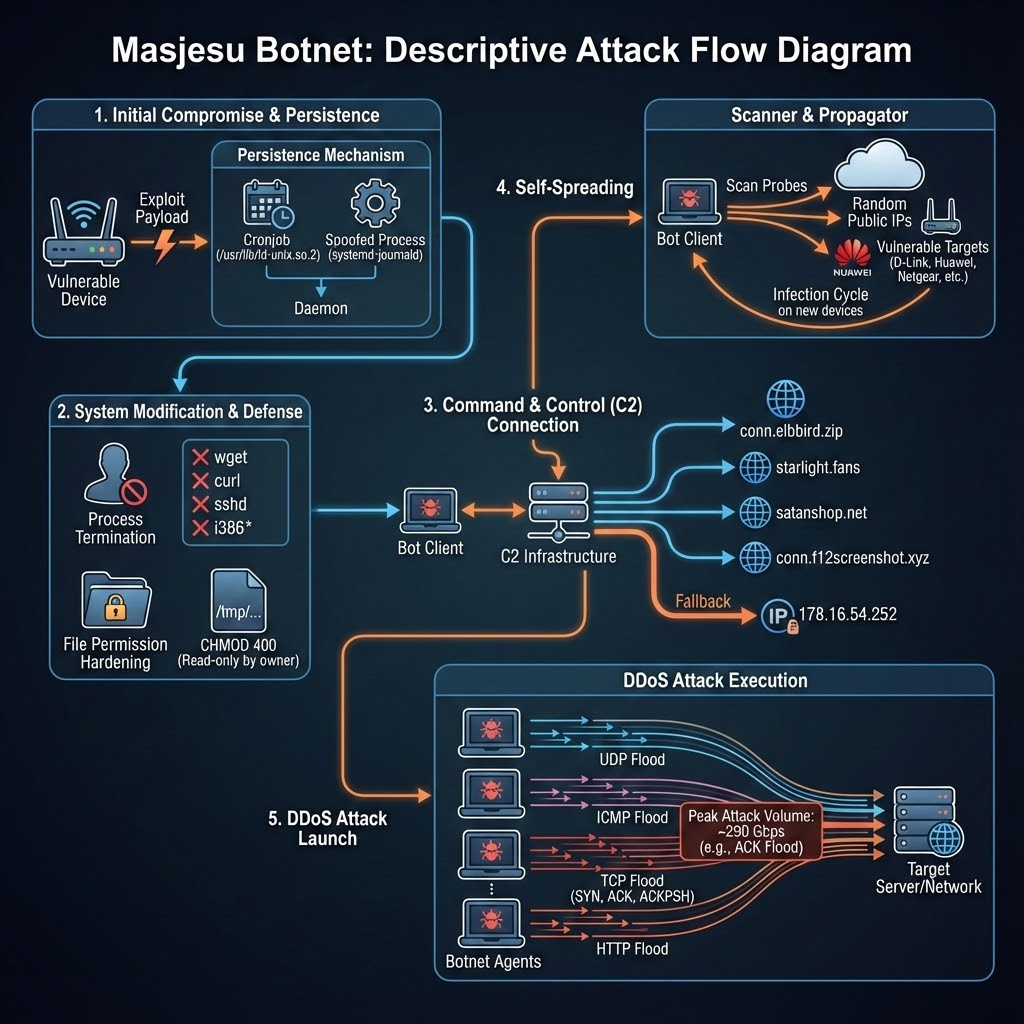
Masjesu is a stealthy botnet active since 2023, advertised as a DDoS-for-hire service. It targets IoT devices like routers and gateways, spanning multiple architectures. Designed for persistence, it executes carefully, avoiding high-profile IP ranges such as the U.S. Department of Defense to remain undetected and survive long-term, favoring low-key attacks over mass infection.
“The Masjesu botnet, a sophisticated, commercially-run Internet of Things (IoT) threat, has been operational and evolving since early 2023, continuing into 2026. Its primary focus is stealth, and it is offered as a “Distributed Denial of Service (DDoS)-for-hire service,” typically marketed via Telegram. It targets a wide array of IoT devices, such as routers and gateways, across multiple architectures (including i386, MIPS, ARM, and AMD64).” reads the report published by Trellix. “Built for persistence and low visibility, Masjesu favors careful, low-key execution over widespread infection, deliberately avoiding blocklisted IP ranges such as those belonging to the Department of Defense (DoD) to ensure long-term survival.”
Masjesu hides its strings, configs, and payloads with XOR encryption to bypass static detection. It scans random IPs and exploits vulnerabilities in devices from D-Link, GPON, and Netgear to spread. Its C2 setup uses multiple domains and fallback IPs and runs TCP, UDP, and HTTP flood attacks.

The botnet targets IoT devices across multiple architectures like i386, MIPS, ARM, SPARC, PPC, 68K, and AMD64, hitting routers, gateways, and embedded systems. Operators advertise on Telegram. The original channel with over 2,000 subscribers was banned; the new channel “Masjesu Botnet / 僵尸网络” has aroud 420 subscribers. Posts appear in English and Chinese, showing attacks and metrics.
Masjesu launched DDoS floods up to approximately 290 Gbps, drawing traffic from countries like Vietnam, Ukraine, Iran, Brazil, Kenya, and India, with Vietnam providing nearly half. Operators market its large, stable, and geographically diverse botnet to target CDNs, game servers, and enterprises.

The bot starts by binding to a fixed TCP port (55988) and hardens itself by ignoring termination signals. The malware hides critical data using multi-stage XOR encryption and decrypts it only at runtime, revealing C2 domains and system details.
To achieve persistence, the malware renames itself as a legitimate system file (e.g., /usr/lib/ld-unix.so.2), installs a cron job to run every 15 minutes, and daemonizes to operate silently. It also spoofs process names like systemd-journald to avoid detection.
Masjesu kills competing processes (wget, curl, sshd) and locks down /tmp to maintain exclusive control. Its C2 uses multiple domains with a fallback IP, retrieving commands and payloads via HTTP.
For propagation, the bot scans random IPs, avoids sensitive ranges (e.g., DoD), and exploits known flaws in routers and IoT devices (D-Link, GPON, Netgear, etc.).
“Masjesu utilizes the Createchildrenreplic() function for further propagation. This function scans random IP addresses,excluding a catalog of blocklisted IP address ranges (Table 2), for specific hardcoded open ports.” continues the report. “Based on the port identified, a corresponding vulnerability exploit is executed on the target device. Upon successful exploitation, the malicious payload is downloaded onto the compromised device.”
Once infected, bots execute DDoS attacks (TCP, UDP, HTTP floods) based on C2 instructions.
Overall, Masjesu combines obfuscation, resilience, and wide exploitation to sustain a distributed, hard-to-detect attack infrastructure.
“Masjesu (XorBot) is a rapidly maturing IoT botnet focused on DDoS-for-hire, primarily marketed via Telegram and resistant to takedowns. Technically, it minimizes detectability and maximizes attack effectiveness by randomizing packet headers and payloads to better mimic legitimate traffic.” concludes the report. “The botnet continues to expand by infecting a broad range of IoT devices across multiple architectures and manufacturers. “
Follow me on Twitter: @securityaffairs and Facebook and Mastodon
(SecurityAffairs – hacking, Masjesu botnet)
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。