惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

aimingoo的专栏
aimingoo的专栏
WordPress大学
WordPress大学
阮一峰的网络日志
阮一峰的网络日志
博客园 - 司徒正美
月光博客
月光博客
宝玉的分享
宝玉的分享
Recent Announcements
小众软件
小众软件
H
Hackread – Cybersecurity News, Data Breaches, AI and More
美团技术团队
博客园 - 三生石上(FineUI控件)
A
About on SuperTechFans
J
Java Code Geeks
云风的 BLOG
云风的 BLOG
罗磊的独立博客
大猫的无限游戏
大猫的无限游戏
IT之家
IT之家
Vercel News
Vercel News
量子位
Martin Fowler
Martin Fowler
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
V
Visual Studio Blog
腾讯CDC
有赞技术团队
有赞技术团队

WeLiveSecurity

Supply chain dependencies: Have you checked your blind spot? Recovery scammers hit you when you’re down: Here’s how to avoid a ‘second strike’ As breakout time accelerates, prevention-first cybersecurity takes center stage Digital assets after death: Managing risks to your loved one’s digital estate This month in security with Tony Anscombe – March 2026 edition RSAC 2026 wrap-up – Week in security with Tony Anscombe Virtual machines, virtually everywhere – but not all protected Cloud workload security: Mind the gaps Move fast and save things: A quick guide to recovering a hacked account EDR killers explained: Beyond the drivers Face value: What it takes to fool facial recognition Cyber fallout from the Iran war: What to have on your radar Sednit reloaded: Back in the trenches What cybersecurity actually does for your business How SMBs use threat research and MDR to build a defensive edge Protecting education: How MDR can tip the balance in favor of schools This month in security with Tony Anscombe – February 2026 edition Mobile app permissions (still) matter more than you may think Faking it on the phone: How to tell if a voice call is AI or not PromptSpy ushers in the era of Android threats using GenAI Is Poshmark safe? How to buy and sell without getting scammed Is it OK to let your children post selfies online? Naming and shaming: How ransomware groups tighten the screws on victims Taxing times: Top IRS scams to look out for in 2026 OfferUp scammers are out in force: Here’s what you should know A slippery slope: Beware of Winter Olympics scams and other cyberthreats This month in security with Tony Anscombe – January 2026 edition DynoWiper update: Technical analysis and attribution Love? Actually: Fake dating app used as lure in targeted spyware campaign in Pakistan Drowning in spam or scam emails lately? Here’s why
A cunning predator: How Silver Fox preys on Japanese firm...
Dominik BreitenbacherTakahiro Sajima · 2026-03-27 · via WeLiveSecurity

Business Security

Silver Fox is back in Japan, spoofing tax and HR emails timed to the one season when no one thinks twice about opening them

27 Mar 2026  •  , 4 min. read
A cunning predator: How Silver Fox preys on Japanese firms this tax season

Japan has entered its annual tax filing and organizational change season, a period when companies generate a high volume of legitimate financial and HR‑related communications. A threat actor known as Silver Fox is actively exploiting this busy period by conducting a targeted spearphishing campaign against Japanese manufacturers and other businesses.

The ongoing campaign uses convincing phishing lures related to tax compliance violations, salary adjustments, job position changes, and employee stock ownership plans. All emails share the same goal – trick the recipients into opening malicious links or attachments. As employees actually expect to receive emails about these subjects this time of year, they’re more likely to trust and act on such messages without a second thought. Needless to say, this significantly increases the risk of compromise.

The operation is also a reminder for organizations to increase vigilance, reinforce awareness around phishing attempts, and ensure that employees verify the authenticity of tax‑ and HR‑themed requests – including those that look routine. Immediate reporting of suspicious emails to security teams is essential to reduce exposure and prevent successful compromise.

What is the threat?

Active since at least 2023, Silver Fox initially focused on Chinese-speaking targets before expanding into Southeast Asia, Japan, and potentially North America, running each campaign in a local language. This broadened scope shows in the range of verticals the group has hit over the years – finance, healthcare, education, gaming, government and even cybersecurity. The group also primarily operates in Southeast Asia and has a well-documented history of finance-themed spearphishing campaigns during seasonal business cycles.

In the ongoing campaign, the group is taking advantage of Japan’s annual cycle of tax filing, financial reporting, salary adjustments, and personnel changes. This pattern isn’t new – similar activity was observed during the same period last year, indicating that Silver Fox deliberately aligns its operations with this season. The volume and urgency of legitimate internal communication around these topics is high this time of year, which is exactly what Silver Fox is counting on and what makes its campaigns effective.

In this operation, Silver Fox sends tailored spearphishing emails crafted to look like legitimate HR or tax-related messages. To make the emails appear authentic, the attackers often include the name of the targeted company directly in the subject line. Examples of subjects observed in this campaign include:

  • 「会社名 」【従業員持株会規約改正に関するお知らせ】
    (Translation: <Company Name> Notice of amendments to the ESOP terms and conditions])
  • 「会社名 」【従業員持株会規約の一部改正について】
    (Translation: <Company Name> [Revisions to the ESOP Terms and Conditions])
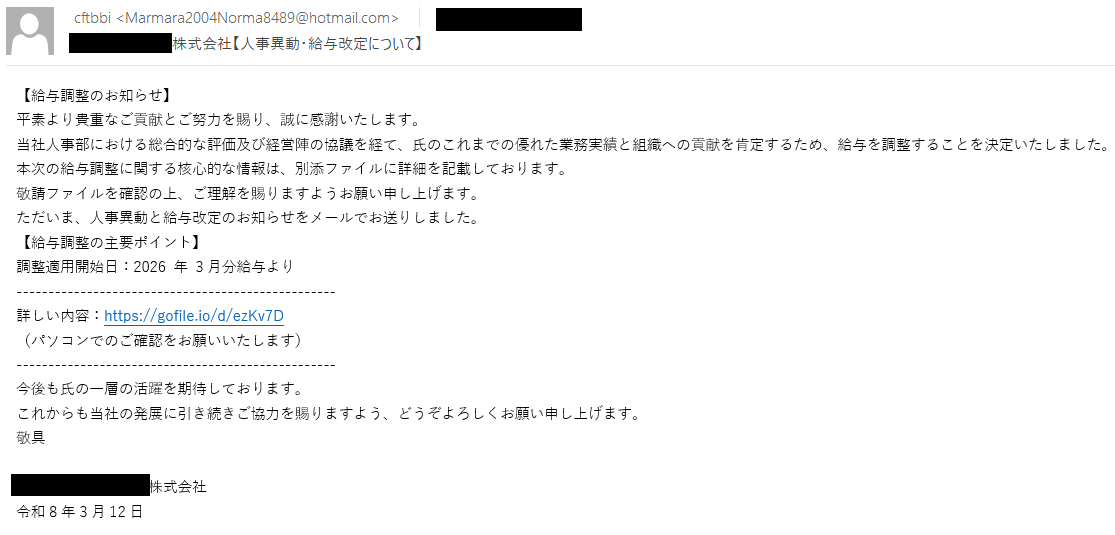
  • 「会社名 」【人事異動・給与改定について】
    (Translation: <Company Name> [Personnel Changes and Salary Adjustments])
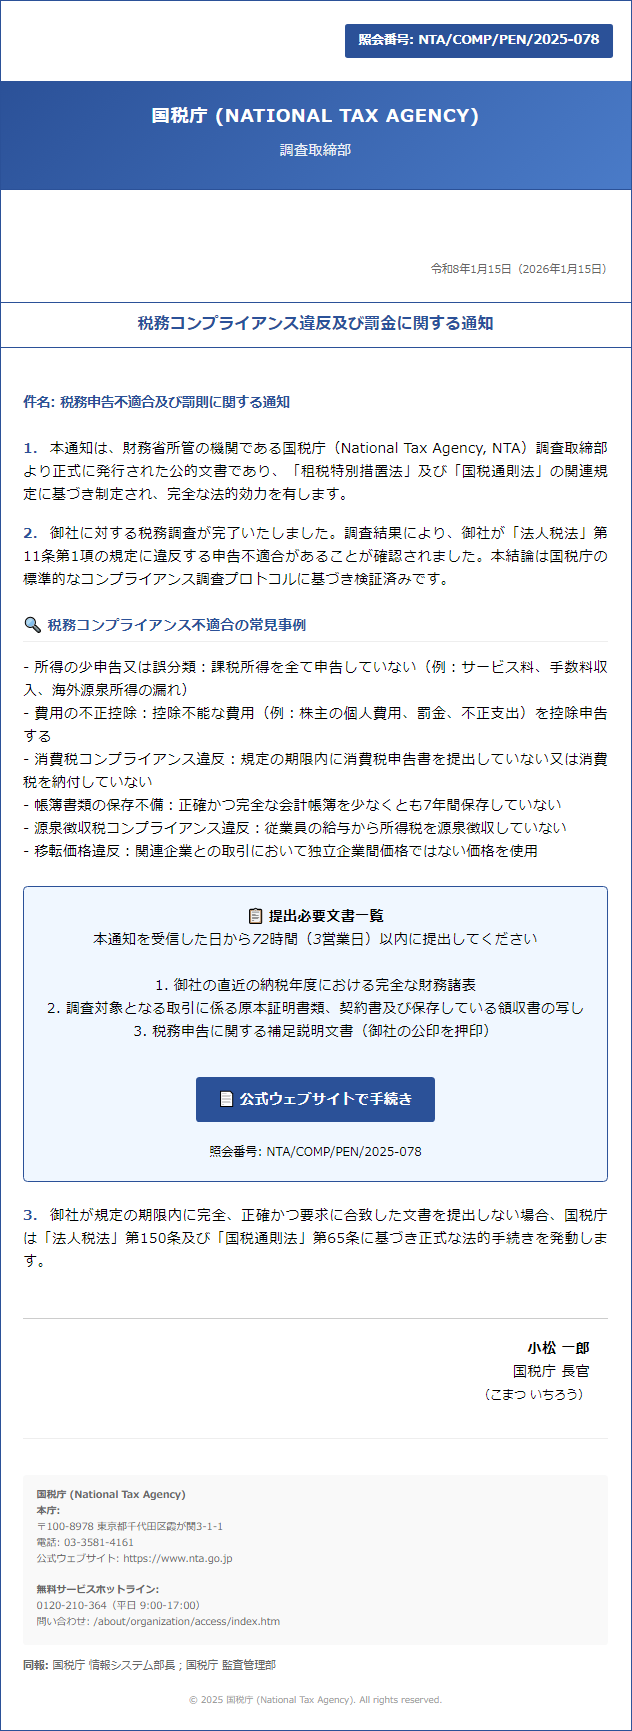
  • 税務コンプライアンスおよび罰金通知
    (Translation: Tax Compliance and Penalty Notice)

The sender fields impersonate real employees and even CEOs at the targeted companies. Silver Fox is clearly doing some reconnaissance on each target before sending what aren’t generic blasts. The attackers are picking names that the targets are likely to recognize and trust, which makes it more difficult for the recipients to distinguish the malicious messages from real internal notifications.

The emails typically contain either a malicious attachment or a link leading to a malicious file. The files are named to resemble common HR, financial, or tax-related documents, such as:

  • 【給与調整のお知らせ】
    (Translation: Salary Adjustment Notice)
  • 人事異動・給与改定について
    (Translation: Personnel Changes and Salary Adjustments)
  • 人事異動及び給与改定に関するお知らせ
    (Translation: Notice regarding personnel changes and salary adjustments)
  • 【従業員持株会規約の一部改正について】
    (Translation: [Partial amendment to the Employee Stock Ownership Plan terms and conditions])

The following are examples of observed emails and lures:
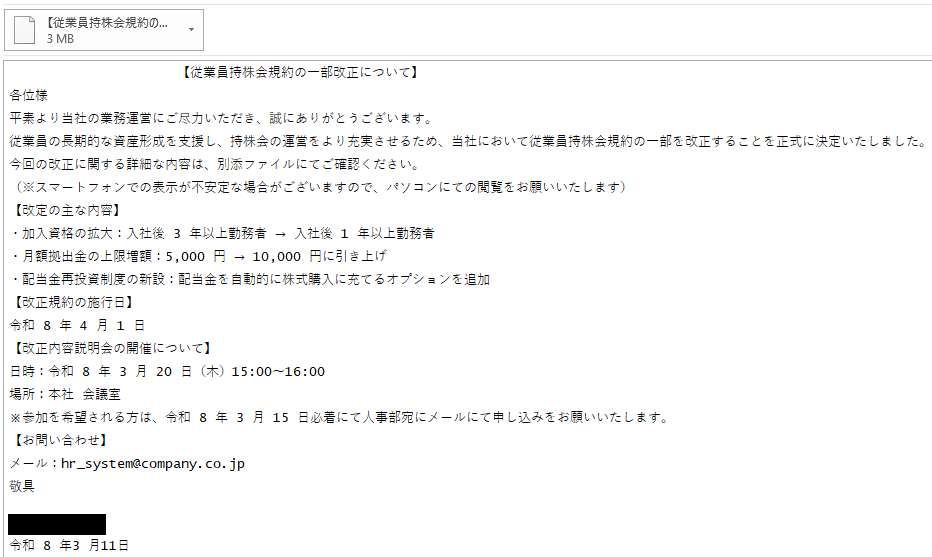
Figure_1_CN_SilverFox_spearphishing_2026-03-11
Figure 1. Spearphishing email distributed on 2026-03-11
Figure_2_CN_SilverFox_spearphishing_2026-03-12
Figure 2. Spearphishing email distributed on 2026-03-12
Figure_3_CN_SilverFox_tax-related_lure_webpage
Figure 3. Tax-related lure webpage instructing the target to download a malicious file

Opening the malicious files drops ValleyRAT, a remote access trojan that Silver Fox has used across multiple campaigns. ESET products detect this malware as Win64/Valley. Once deployed, ValleyRAT enables the actor to take remote control of the compromised machine, harvest sensitive information, monitor user activity, and maintain persistence in the targeted environment. This can allow the attacker to burrow deeper into the network, steal confidential data, or prepare additional stages of an attack.

How to recognize the threat and protect yourself

While Silver Fox’s emails may appear credible at the first glance, especially during Japan’s busy tax and organizational change season, a closer look reveals hints rendering the emails suspicious. The following signs are the key to recognizing and stopping the attack:

  • If you receive an email about salary changes, tax penalties, or personnel updates, verify it through a separate channel (Teams, phone, or direct email lookup) before acting on it. This applies even if the message looks routine.
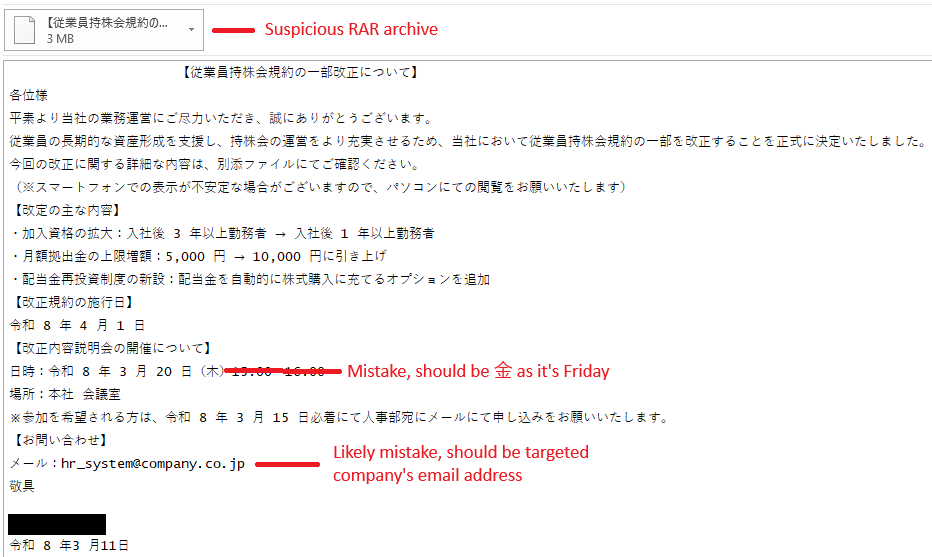
  • Even if the sender’s name belongs (or seems to belong) to a colleague, make sure that the email address and the name match. If they don’t or the address looks unfamiliar, treat the email as suspicious.
  • Ask yourself whether this communication follows your company’s usual HR or Finance process.
  • Be cautious if the language feels overly formal, stiff, or mismatched with typical internal communications. Since the threat actor is not a native Japanese speaker, the emails may contain awkward phrasing and subtle giveaways.
  • Documents are unlikely to be shared through a publicly available file hosting services such as gofile[.]io or WeTransfer.
  • Pay attention to the attachment type. If it’s an archive such as RAR or ZIP, look at what’s actually inside before opening the files.
  • Install software updates when prompted.
  • Ensure your security software is running and up-to-date.
  • If something feels off about an email, forward it as an attachment to your IT or security team. Reporting is never a mistake – even if the email turns out to be legitimate.

The following are illustrative examples of what to watch out for:
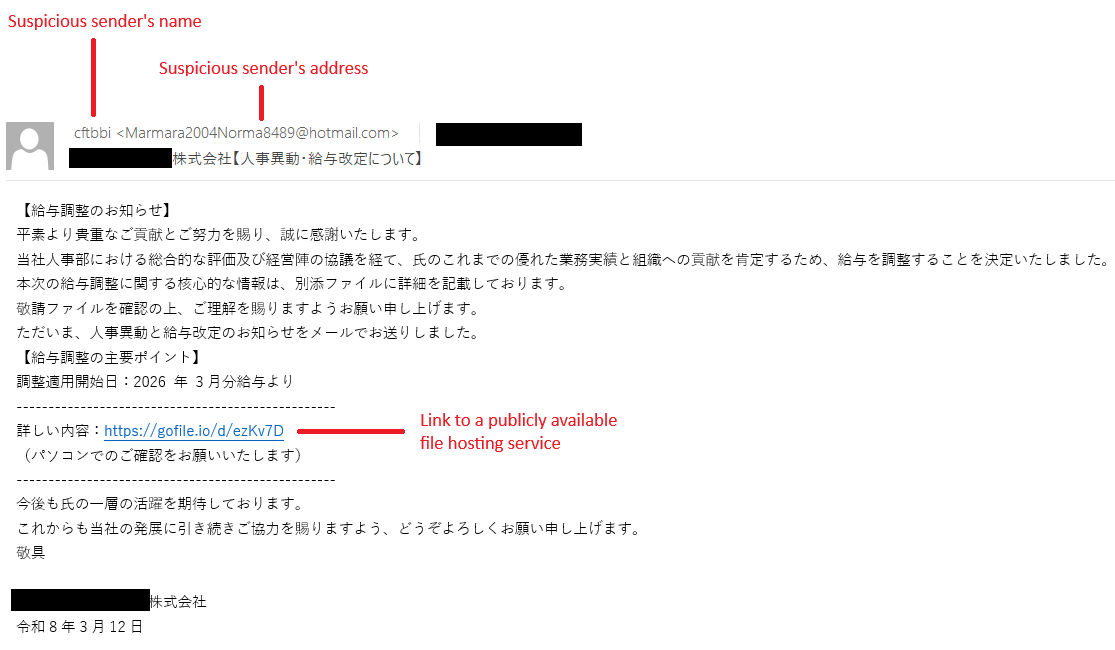
Figure_4_CN_SilverFox_spearphishing_2026-03-12_indicators
Figure 4. Signs revealing that the email is not legitimate
Figure_5_CN_SilverFox_spearphishing_2026-03-11_indicators
Figure 5. Signs revealing that this email is not legitimate, either

IoCs

A comprehensive list of indicators of compromise (IoCs) and samples can be found in our GitHub repository.


Let us keep you
up to date

Sign up for our newsletters