




惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
T
Tailwind CSS Blog
J
Java Code Geeks
Microsoft Azure Blog
GbyAI
GbyAI
爱范儿
爱范儿
量子位
Martin Fowler
Martin Fowler
V
V2EX
博客园 - 三生石上(FineUI控件)
I
InfoQ
MongoDB | Blog
MongoDB | Blog
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
N
Netflix TechBlog - Medium
D
DataBreaches.Net
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
Last Week in AI
Last Week in AI
U
Unit 42
Apple Machine Learning Research
H
Help Net Security
T
The Blog of Author Tim Ferriss
Hugging Face - Blog
Hugging Face - Blog
美团技术团队
Engineering at Meta
Engineering at Meta

Latest from Tom's Hardware in Tech-industry

Samsung engineer sentenced to 7 years in prison for selling chipmaking trade secrets to Chinese chipmaker — ex-employee supplied 10nm DRAM data to CXMT for $2 million Microsoft facing $2.8 billion UK lawsuit for overcharging 60,000 businesses using Microsoft Server on other clouds — Azure users allegedly received lower wholesale pricing Ransomware negotiator pleads guilty after leaking victims' insurance details to 'BlackCat' hackers — perp gave attackers a precise picture of exactly how much each target could afford to pay Congress moves to strip the DoC of chip-export discretion with the MATCH Act — DUV lithography machines among those targeted in chipmaking tool crackdown Anthropic's Model Context Protocol includes a critical remote code execution vulnerability — newly discovered exploit puts 200,000 AI servers at risk Iran claims US exploited networking equipment backdoors during strikes — says devices from Cisco and others failed despite blackout in attack that 'indicates deep sabotage' Cerebras files for IPO — company remains unprofitable despite 20x revenue growth Scientists solve decades-old 2D physics puzzle — Chaotic growth in a 2D quantum system obeys statistical laws Anthropic nuked a company's access to Claude, stopping 60 employees dead in their tracks — support via Google Form is the only recourse for vague usage policy violation Biohacker claims to have sequenced their own genome at the kitchen table with M3 Ultra Mac Studio, Claude, and a $3,200 sequencer — DIY project requires 100GB of data storage per run, oodles of RAM New Jersey datacenter expansion got $77m in tax breaks to create exactly one permanent job — JPMorgan's site already scored $35m and currently employs just 25 workers Chinese chipmakers made record profit in 2025, despite slipping margins — U.S shipments fall 34% as Beijing shores up local chipmaking efforts AI cloud company Vercel breached after employee grants AI tool unrestricted access to Google Workspace — hacker… Every SK hynix employee could receive $477,000 bonuses this year, almost $900,000 next year — 35,000 workers reportedly set to benefit from share of $169 billion projected operating profit US gov't blocks China's largest LED chipmaker's $239 million bid to acquire Dutch lighting firm Lumileds… Tokyo court rules movie and anime 'spoiler articles' are copyright infringement in landmark criminal case — detailed, monetized plot summaries land man in Japanese prison Voyager 1 gets emergency instrument shutdown to solve escalating power crisis and give it ‘about a year of breathing room’ — interstellar spacecraft's nuclear power source is dying, leading to intensifying countermeasures Russian-made Shahed drones are ‘disintegrating in the air before reaching their targets’ due to shoddy manufacturing, video shows — commentators call Russian clones of Iran's drones 'flying garbage' Inventor showcases 3D printer filament dryer that mines Bitcoins and dries filament with waste heat, capable of 6 TH/s at 140W — joins Bitcoin-mining 3D printer in hobbyist-focused miner lineup Bluetooth tracker hidden in a postcard and mailed to a warship exposed its location — $5 gadget put a $585 million… Techie buys fake Ledger Nano S+ hardware crypto wallet and almost falls for phishing — a convincing clone would… Nvidia CEO Jensen Huang ‘nearly lost his composure’ when pressed on selling chips to China — ‘You’re not talking to someone who woke up a loser’ US lawmakers amend new restrictions on Chinese chipmakers — MATCH Act Analytics group signals possible delays at 40% of AI data center construction sites — companies deny schedule holdups, but satellite imagery indicates otherwise Local political revolts threaten to derail US data center projects — mounting delays are already costing AI hyperscalers billions Intel hires tenured Samsung exec to lead Foundry Services — signals company focus on winning business from potential Foundry suitors Elon Musk pushing forward with Terafab at TSMC ups revenue guidance and CapEx, buoyed by Google and Pentagon in talks to run custom AI chips inside classified environments — Google pushes for tight controls for TPUs surrounding use for mass surveillance and autonomous weapons TSMC warns of Intel Foundry
Microsoft BitLocker-protected drives can now be opened wi...
Bruno Ferreira · 2026-05-13 · via Latest from Tom's Hardware in Tech-industry
Falling laptop cracking
(Image credit: Getty Images)

There's nothing more dangerous than a bored engineer with a screwdriver, and hell hath no fury like a security researcher scorned. Last month, Security researcher Chaotic Eclipse (aka Nightmare-Eclipse) published two zero-day exploits, BlueHammer and RedSun, that made Windows Defender offer up system administrator privileges. They did this after their disclosure reports were allegedly dismissed by Microsoft's security team, resulting in a vendetta of sorts. Eclipse has now done it again, posting two new zero-day exploits, the first one an extremely serious BitLocker exploit named Yellow Key that grants full access to a locked drive. The second one, GreenPlasma, doesn't have a complete proof-of-concept (PoC), but it allegedly performs a local privilege escalation and gains system-level access. Given Eclipse's track record, it's a fair bet that it works as advertised.

YellowKey can be triggered simply by merely copying some files to a USB stick and rebooting to the Windows Recovery Environment. We tested this ourselves, and sure enough, not only does it work, it bears all the hallmarks of a backdoor, down to the exploit's files disappearing from the USB stick after it's used once.

The process is dead simple: grab any USB stick, get write access to the "System Volume Information," and copy into it the "FsTx" folder and its contents. Shift+click Restart to get Windows to the recovery environment, but then switch to holding down the Control key and don't let go. The machine will reboot, and without asking any questions or showing any menus, will drop you in an elevated command line with full access to the formerly Bitlocked drive, without asking for any keys.
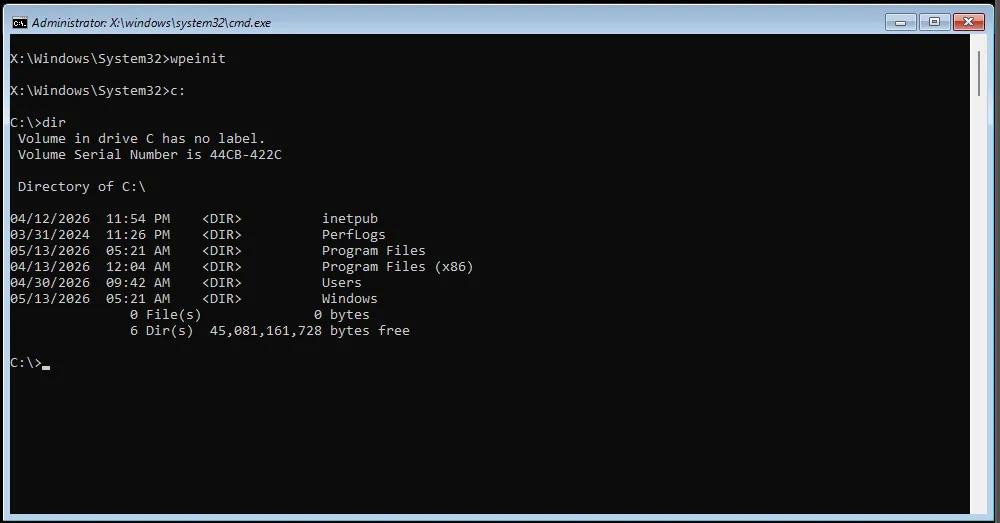
YellowKey Bitlocker exploit

Look ma, no keys! (Image credit: Future)

To say that this is dangerous is an understatement. Not only is it an immediate concern as BitLocker cannot be trusted for encrypting drives, but the way the exploit executes and its files disappear also raises very uncomfortable corporate and/or political questions. YellowKey also reportedly works in Windows Server 2022 and 2025, but not in Windows 10.

BitLocker protects millions of machines worldwide across home, enterprises, and governments, especially as it's enabled by default in Windows 11. As far as we can tell, a drive can't be taken from machine Alice and opened in machine Bob because the encryption keys are in Alice's TPM, but it's not hard to just up and steal a laptop, mini-PC, or even desktop.

Eclipse notes that using a full TPM-and-PIN setup doesn't help, as apparently, they have a variant for that scenario that they haven't published a PoC for. They also state the vulnerability is well-hidden, and that they "could have made some insane cash selling this, but no amount of money will stand between me and my determination against Microsoft."

As for GreenPlasma, it's supposed to get an attacker full system-level access (even higher than administrator) by manipulating the CTFMon process into placing a crafted memory section object — a slice of memory that can be shared between processes or mapped to a file — in any Windows' Object Manager section the SYSTEM user has write access to, bypassing regular access controls.

Get Tom's Hardware's best news and in-depth reviews, straight to your inbox.

From thereon, the exploit code can get access to regions of memory they're not meant to and leverage that for any number of shenanigans, the most obvious one being getting full system access. This is bad enough for a desktop system, as any program can get full access, but it's particularly bad for server environments, where any regular user can get control of the server and, by extension, everyone else's data.

Meanwhile, as of this writing, there is no official response from the company about YellowKey or GreenPlasma. BlueHammer has already been patched, and Chaotic claims that Microsoft silently patched RedSun, but there's no official word on that either.

Google Preferred Source

Follow Tom's Hardware on Google News, or add us as a preferred source, to get our latest news, analysis, & reviews in your feeds.

Bruno Ferreira is a contributing writer for Tom's Hardware. He has decades of experience with PC hardware and assorted sundries, alongside a career as a developer. He's obsessed with detail and has a tendency to ramble on the topics he loves. When not doing that, he's usually playing games, or at live music shows and festivals.