




ThreatDown has uncovered a new campaign spreading the MobiDash adware for Android.
Someone is trying very hard to infect your Android device with malicious adware.
ThreatDown’s Android experts recently became aware of a campaign spreading MobiDash adware for Android using phishing emails, links on social media posted by people or bots, and at least one pornography website (xnxxvideosporn[.]net).
Android/Adware.MobiDash is Malwarebytes’ detection name for an adware that targets mobile devices running the Android OS, which became prevalent in 2015 and continues to be spread via hundreds of variants. It comes in the form of a Software Development Kit (SDK), a pre-packaged set of tools that can be added easily onto any Android Application Package (APK), the format used to distribute Android apps.
It is common for nefarious actors to take legitimate APKs and repackage them with adware SDKs so that besides the game, mod, movie, or whatever app they were promised, unsuspecting users are also infected with the MobiDash adware, and any other malware that MobiDash is used to install.
A unique characteristic of MobiDash is that it can wait up to three days after being installed before it starts to display ads. From then on, infected devices will display ads until the app is uninstalled. Since the MobiDash SDK is attached to a legitimate APK that will continue to work as expected, the victim may be left wondering where the advertisements are coming from, and won’t know which app to uninstall.
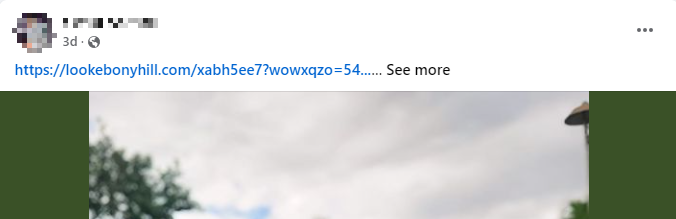
In the recent campaign, users who clicked the Facebook link in the screenshot above were sent through a chain of redirects (lookebonyhill.com > apkretro.com > 3-dl-app.com) that ends in the automatic download of an APK file, although some users will have to use the Download button.
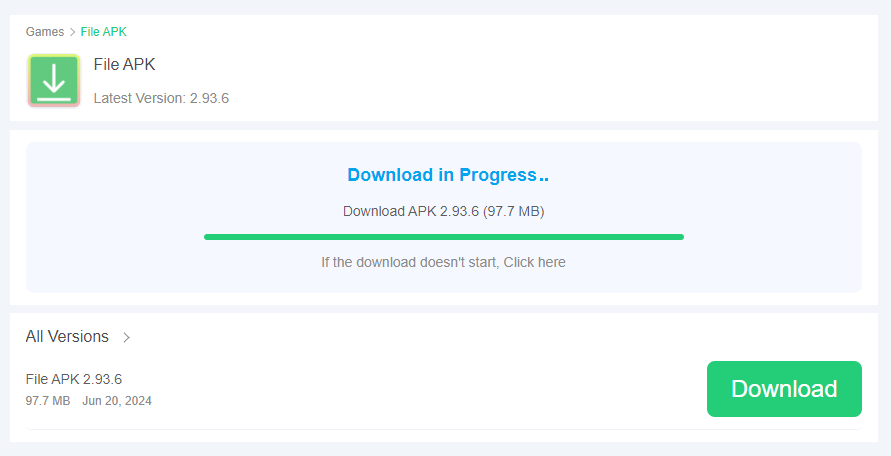
ThreatDown and Malwarebytes block the start of the redirect chain and can detect and remove MobiDash from your device.

IOCs
lookebonyhill[.]com
cinepornogratis[.]com
mobileoffers-ek-download[.]com
apkdw[.]online
mobileoffers-et-download[.]com