
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

WordPress大学
WordPress大学
博客园 - 司徒正美
宝玉的分享
宝玉的分享
阮一峰的网络日志
阮一峰的网络日志
The Cloudflare Blog
月光博客
月光博客
博客园 - 【当耐特】
让小产品的独立变现更简单 - ezindie.com
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
博客园 - 三生石上(FineUI控件)
博客园 - 聂微东
小众软件
小众软件
Hugging Face - Blog
Hugging Face - Blog
酷 壳 – CoolShell
酷 壳 – CoolShell
Apple Machine Learning Research
V
V2EX
Jina AI
Jina AI
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
罗磊的独立博客
雷峰网
雷峰网
博客园 - 叶小钗
量子位
IT之家
IT之家

Kaspersky official blog

ChatGPT Computer History: the risks and a safe setup How to completely uninstall apps on Mac and free up storage Hacking the Boeing 737: inside the Bus Driver attack | Kaspersky official blog Getting AI for schoolwork right: 25 helpful prompts + usage tips This Android malware steals banking credentials even without an internet connection Detection blind spots: non-standard file formats in malicious email campaigns What to do if you find someone else's bank card How to spot scam websites that your browser says are safe Malware in car infotainment systems: how infection occurs How to protect yourself from webcam spying: five simple steps ClickFix on Steam forums: how malicious PowerShell commands install a crypto miner How to tell an AI-written book from an expert's What we know about the cryptocurrency theft through Adform ads Detection blind spots: polyglot file formats in mass mailings and targeted attacks How to prevent autonomous agents from breaching corporate infrastructure CrashStealer, a new infostealer for macOS: how it works and how to stay safe ScreenConnect leveraged in cyberattacks ClickFix on macOS: how the Terminal-based attack works, and how to protect yourself Why live chat agents can read your messages before you hit “Send” Real-world attacks on corporate AI agents How Google phone number verification works, and whether you should turn it off ConsentFix: a new ClickFix variation for compromising Microsoft 365 accounts How to protect your data after a breakup Email hijacking via OAuth Prompt attacks on the Gemini AI-assistant and Google Workspace with Gemini Key vulnerabilities of Microsoft’s July 2026 Patch Tuesday Meta launched and almost instantly rolled back a feature that trained its AI image generator on Instagram user content. What’s wrong with Meta's NameTag feature and why you should be wary of it Why CAPTCHAs are about to vanish: how AI rewrote the "prove you're human" test The unpatchable backdoor in Yarbo robot mowers
Targeted phishing attacks on manufacturing companies
Roman Dedenok · 2026-07-09 · via Kaspersky official blog

Before launching a phishing attack, attackers initiate correspondence with the victim.
Targeted phishing attacks on manufacturing companies

We have identified a new targeted phishing campaign in which cybercriminals attempted to attack manufacturing companies. The attack employed a multi-stage approach — before sending the phishing link directly, the attackers engaged in correspondence with the victim to lower their guard. The email texts were apparently generated using large language models. As of this post’s publication, the attack is still ongoing, so we recommend staying vigilant!

Phishing scheme

The attackers attempt to pose as potential clients. The emails are sent from addresses registered on free email services — these services do not have a known bad reputation, and are often actually used for business correspondence, especially by small companies. Regardless of the victim’s native language (and we’ve seen attacks targeting companies in Russia, the Czech Republic, Malaysia, and Egypt), the attackers’ emails are always written in English.

In the first email, the attackers ask questions about the products being offered, citing actual product names. This indicates thorough preparation for the attacks — the attackers do not send identical emails to manufacturing companies with similar profiles, but rather carefully research publicly available information about each victim online. If someone responds to the first email, the attackers continue the correspondence. Sometimes, before moving directly to their objective — extracting credentials from corporate email accounts — they exchange several messages in which, as a distraction, they clarify certain details or ask additional questions. But more often than not, they send the phishing link as early as the second email.

The attackers send detailed specifications for a product they claim to be interested in, ask if the product can be engraved according to a sketch, or use any other pretext to try to get the victim to open the file they’ve sent.
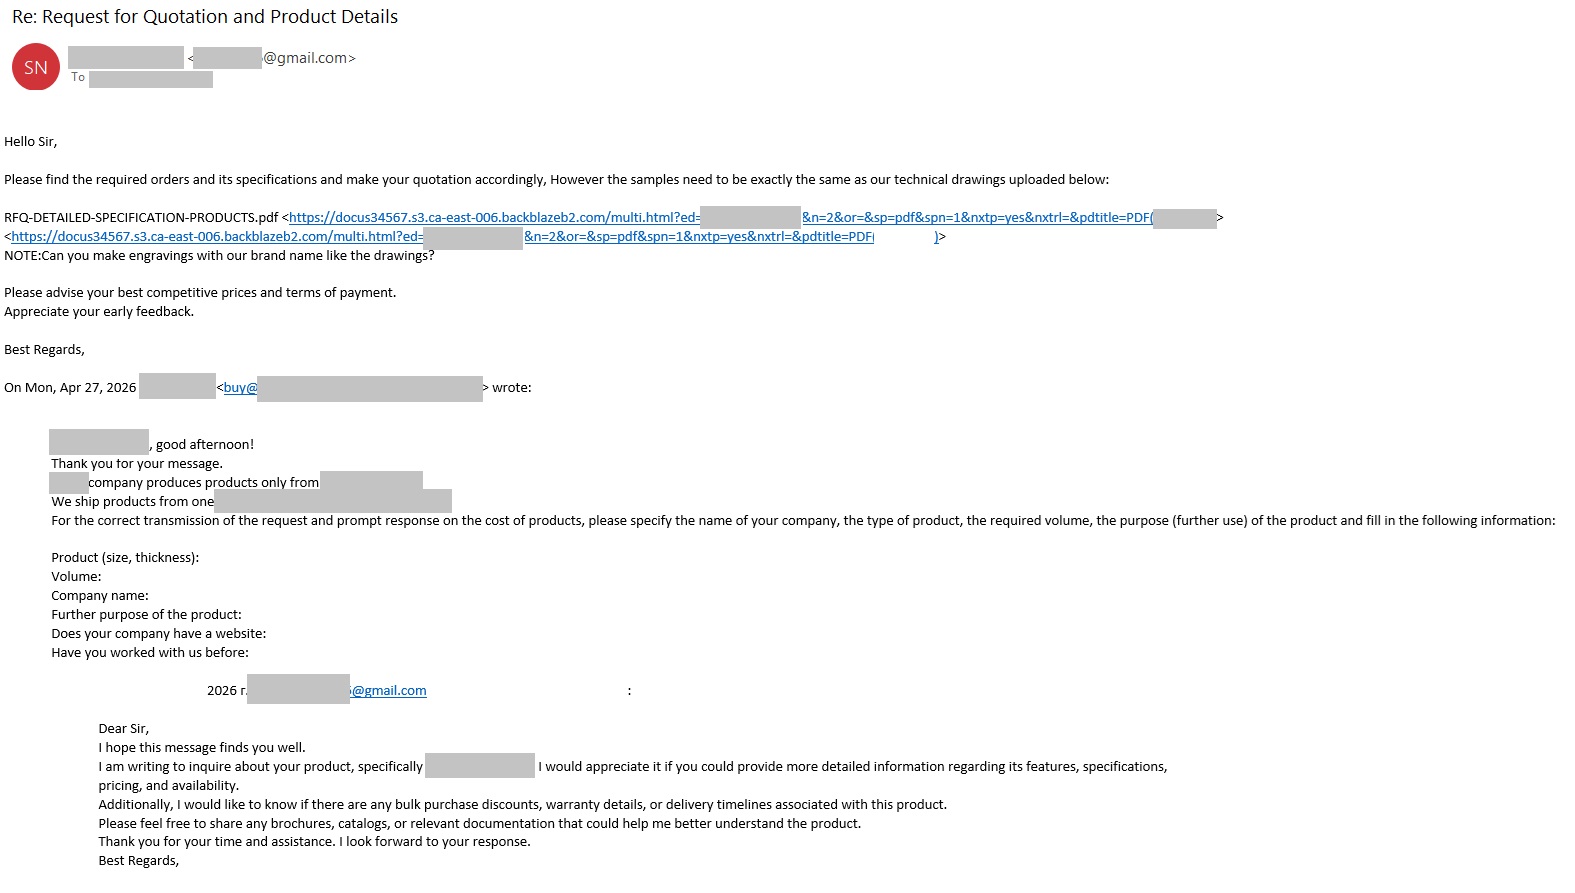
A chain of emails ending with a phishing link

A chain of emails ending with a phishing link

Phishing website

In reality, there is no file at all. The phishing site that opens when victim clicks the link mimics a popular cloud service for working with PDF documents. The “Download” button leads to a login form where the victim is asked to enter their work email address and password to access the confidential file. Of course, this is “for security purposes.” If an employee of the targeted company doesn’t stop to think about why they would enter their corporate login credentials on a completely unrelated website — one that clearly has no way of verifying their authenticity — then their email address and associated password will be sent to the attackers’ server.

How to stay safe?

Modern phishing attacks are becoming increasingly sophisticated and, thanks to attackers’ use of AI tools, even more convincing. That’s why, first and foremost, we always recommend periodically raising employee security awareness. And to ensure they have to put this knowledge into practice as rarely as possible, it is recommended to deploy a security solution at the email gateway level. Specifically, our Kaspersky Secure Mail Gateway detects this phishing attack even before the attackers move on to the actual phishing attempt.
Why CAPTCHAs are about to vanish: how AI rewrote the

AI beat CAPTCHA. What’s next?

For over a decade, internet users have had to squint at blurry fire hydrants, bridges, and bicycles — until AI came along. What’s next for the CAPTCHA?

Why CAPTCHAs are about to vanish: how AI rewrote the
Tips

AI beat CAPTCHA. What’s next?

For over a decade, internet users have had to squint at blurry fire hydrants, bridges, and bicycles — until AI came along. What’s next for the CAPTCHA?

Cracked in under a minute: (nearly) every other password

We’ve revisited our study on the crackability of real-world passwords leaked on the dark web — originally conducted two years ago. The findings are sobering: nearly every other password can be cracked in under a minute, and three out of five take less than an hour. How can we move away from insecure passwords?