





An email attachment leads to the installation of a malicious Chrome extension. Researchers say it is part of a Windows backdoor delivered via a phishing email. The malware abuses Chrome Native Messaging to move control from the browser into the host system. Its most notable trick isn’t the phishing lure itself, but the way it uses legitimate browser and Windows features to run PowerShell and collect data while staying inside expected workflows.
The attack starts with an email attachment disguised as a PDF. The file uses the misleading extension .pfd.js to look like a PDF document, but it’s actually an obfuscated JavaScript file that drops additional files into the temporary folder and starts the rest of the infection chain.
As part of that chain, a PowerShell script prepares a Chrome extension and changes Chrome policy settings so that the extension can be installed. The malware makes the installation appear to be an administrator-controlled deployment rather than a normal extension installation.
Once active, the extension and its native companion collect browser cookies, open tabs, URLs, language settings, and fingerprinting data. The operators also use the setup as a remote command channel, sending instructions that can launch PowerShell and enumerate the contents of the C: drive.
With the stolen authenticated session cookies, the attackers can hijack active browser sessions rather than just stealing passwords, which is more useful to them as it lets them access accounts already logged in on the victim’s browser, bypassing multi-factor authentication (MFA).
The most interesting aspect of the attack is its abuse of Chrome Native Messaging as a bridge between the browser sandbox and the operating system. Chrome allows extensions to communicate with a registered native host, and the attackers weaponized that legitimate feature to make the extension a controller for local code execution. The extension doesn’t launch PowerShell directly. Instead, it sends messages to the native host, which then launches or interacts with PowerShell on the host system.
How to stay safe
The first line of defense against attacks of this kind is to avoid opening email attachments unless you can verify the sender. In addition:
- Always check the real file extension instead of relying on the displayed filename.
- Use an up-to-date, real-time anti-malware solution to detect and block malicious activity.
- Check the installed Chrome extensions on your device and remove any you don’t recognize or no longer use.
- To be extra cautious, sign out of important accounts when you’re finished. That invalidates your session, so even if someone has stolen your session cookie, they won’t be able to use it to access your account.
- Regularly check the login history for important accounts. Many online services let you see which devices have signed in, when, and from where.
IOCs
Attachment:
Fattura-2819889242.pfd.js (displayed as Fattura-26189991026.pdf)
Malicious files:
client_124578.exe
d3d11.dll
Chrome extension:
Name: Cloud vn105rkj64
ID: gghagmhimhgfeajfdmjkgmmehbokmglg
Domain:
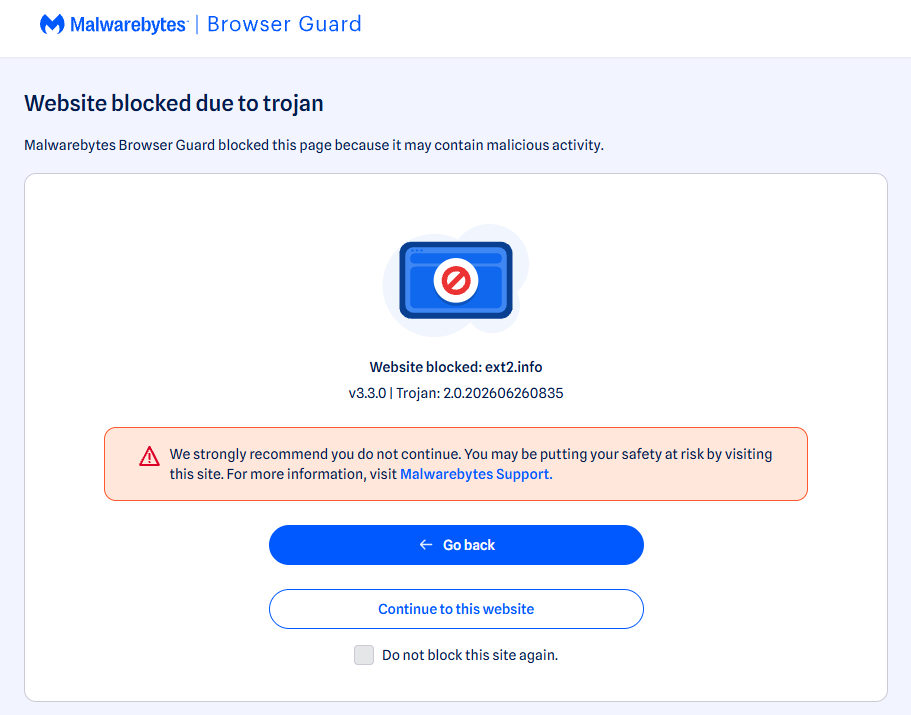
ext2[.]info
This is blocked by Malwarebytes Browser Guard, our free browser extension that blocks ads, trackers, malware, and more.
We don’t just report on threats—we remove them
Cybersecurity risks should never spread beyond a headline. Keep threats off your devices by downloading Malwarebytes today.