

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

GbyAI
GbyAI
Martin Fowler
Martin Fowler
云风的 BLOG
云风的 BLOG
让小产品的独立变现更简单 - ezindie.com
T
The Blog of Author Tim Ferriss
大猫的无限游戏
大猫的无限游戏
A
About on SuperTechFans
小众软件
小众软件
博客园_首页
博客园 - 聂微东
罗磊的独立博客
Recent Announcements
U
Unit 42
N
Netflix TechBlog - Medium
Blog — PlanetScale
Blog — PlanetScale
阮一峰的网络日志
阮一峰的网络日志
博客园 - 叶小钗
V
V2EX
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
IT之家
IT之家
Stack Overflow Blog
Stack Overflow Blog
博客园 - Franky
D
DataBreaches.Net
Last Week in AI
Last Week in AI

Malwarebytes

Kali365 phishing kit bypasses MFA and steals Microsoft logins Company bragged phone mics could listen to conversations. They couldn’t. Fake LinkedIn emails abuse Adobe to track victims Fake software on GitHub and SourceForge distribute Deno RAT 700+ education and tech websites hijacked in huge ClickFix malware campaign Scammers pretending to be Microsoft had help from US executives A week in security (May 18 – May 24) Update Chrome now: Critical bugs could let attackers run code Microsoft Defender vulnerabilities are being exploited in the wild TikTok, YouTube, and Roblox face scrutiny, but age gates won’t fix child safety Catch spyware in the act with Windows Webcam Monitoring Researchers left AI agents alone in a virtual town and watched it all unravel Fake malware-signing service Fox Tempest dismantled by Microsoft Firefox 151 packs big privacy upgrades into a small update Biometrics, diagnoses, and bank details exposed in major healthcare breach Facebook scam promises cheap Aldi meat boxes, steals payment info instead YouTube wants your face to fight deepfakes Microsoft is changing Edge’s plaintext password behavior A week in security (May 11 – May 17) AI is distorting the Holocaust (Lock and Code S07E10) Attackers replaced JDownloader installer downloads with malware Meta’s confusing new approach to chat privacy Why Malwarebytes blocks some Yahoo Mail redirects Deepfake sextortion forces schools to remove student photos from websites Texas sued Netflix over claims it secretly collected and sold users’ data May 2026 Patch Tuesday: no zero-days but plenty to fix Fake Claude search results lure Mac users into ClickFix attack 1 in 8 employees have sold company logins or know someone who has Stolen Canvas data was “returned” after hacker agreement, Instructure says Yarbo responds to robot flaws that could mow down their owners
Microsoft working on a fix for RoguePlanet, a flaw that g...
Pieter Arntz · 2026-06-18 · via Malwarebytes

A publicly available exploit called RoguePlanet can give attackers the highest level of access on Windows systems. Microsoft has confirmed the vulnerability and says it’s working on a security update.

RoguePlanet is tracked under CVE-2026-50656, where it’s described as a Microsoft Defender Elevation of Privilege (EoP) vulnerability.

In its advisory, Microsoft says:

“Microsoft is aware of an elevation of privilege in the Microsoft Malware Protection Engine in Microsoft Defender publicly referred to as “RoguePlanet “. We are working to provide a high quality security update that addresses this vulnerability. We will provide information in this CVE when the update is available.”

If successfully exploited, RoguePlanet can allow an attacker to elevate privileges from a standard user account to NT AUTHORITY\SYSTEM, the highest privilege level on Windows.

This means an attacker who manages to get access to a standard user account on your computer could use the vulnerability to gain complete control of the system. They don’t need advanced hacking skills or administrator permission to do this.

The success of the published exploit does depend on a race condition, though. This means its success depends on the precise timing of two events. The researcher wrote:

“I have managed to get a 100% success rate on some machines while it struggled to work on others.”

It seems that the problem lies in a high-level part of the Microsoft Defender code, which may help to explain why Microsoft says it’s working on a “high quality security update.”

This same researcher has submitted three earlier Microsoft Defender vulnerabilities known as BlueHammer (CVE-2026-33825), UnDefend (CVE-2026-45498), and RedSun (CVE-2026-41091), as well as four other Windows zero-days, all of which have since been patched by Microsoft.

How to protect your machine

The exploit reportedly works whether you’re using active protection or not, so disabling Microsoft Defender is not a solution. But there are a few things you can do to protect your machine:

  • Look out for a Microsoft security update addressing this vulnerability and install it as soon as it becomes available.
  • Back up your important data on a platform or device that is not directly connected to your computer.
  • Be careful about downloading executable files from unknown sources or running files that are recommended to you without you asking for them.
  • Do not rely on Microsoft Defender as your only anti-malware solution. Malwarebytes detects RoguePlanet.exe (the exploit code) based on its behavior.
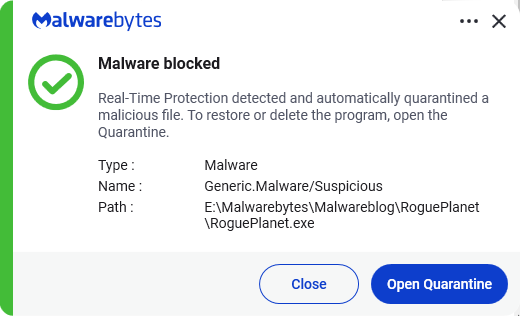
    Malwarebytes blocks the exploit code

Obviously, we’ll keep you posted about this and other security issues, so stay tuned.

CNET Editors' Choice Award 2026

“One of the best cybersecurity suites on the planet.” 

According to CNET. Read their review


About the author

Was a Microsoft MVP in consumer security for 12 years running. Can speak four languages. Smells of rich mahogany and leather-bound books.