


The Eastman Kodak Company (Kodak) confirmed to BleepingComputer that it is investigating a security breach after the ShinyHunters extortion group claimed responsibility for the incident.
Kodak is the latest organization to land on the group’s leak site. ShinyHunters claims it stole more than 2.2 million records and threatened to publish the data unless the company responded by June 18.
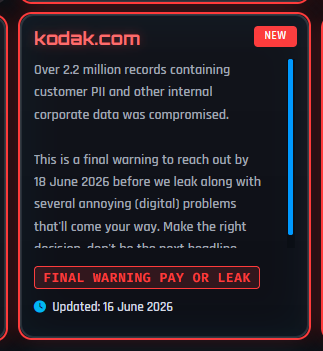
“Over 2.2 million records containing customer PII and other internal corporate data was compromised. This is a final warning to reach out by 18 June 2026 before we leak along with several annoying (digital) problems that’ll come your way.”
Kodak has now confirmed a data breach, while also saying the incident was limited in scope, contained, and did not pose a threat to its systems or operations.
ShinyHunters has been busy making the same point across multiple victims: modern extortion is often less about ransomware (encryption) and more about access, stealing valuable data, and applying pressure.
ShinyHunters claims it stole customer information and internal corporate data, but has not publicly provided proof. That’s a common pattern for extortion groups. They make public claims, set a deadline, and use the threat of a data leak to pressure victims before the full facts are known.
Kodak told SecurityWeek that an unauthorized third party gained access to a limited amount of company data, and that the incident appears to have been contained. The company said it brought in external cybersecurity experts, notified law enforcement, and believes there is no threat to its systems or operations.
It’s not yet known how the attackers gained entry to Kodak’s systems, but the extortion group is well-known for social engineering, bribery, and utilizing zero-day vulnerabilities to perform supply-chain attacks. The investigation is ongoing.
How to stay safe
While Kodak works to determine who was affected and exactly what information was accessed, there’s no reason to panic. But there are a few things you can do:
- Change the password on your Kodak account and make sure you haven’t reused the same password on other accounts.
- Turn on multi-factor authentication (MFA) wherever possible, to ensure that a stolen password is not enough to take over your account.
- If you’re in the US, consider placing a credit freeze with Equifax, Experian, and TransUnion. A credit freeze helps prevent identity thieves from opening new accounts in your name by blocking lenders from accessing your credit file.
- Depending on the information involved, Kodak may offer affected customers free credit monitoring. Even if it doesn’t, you may want to consider identity monitoring services, which can alert you if your personal information appears in suspicious places or is used to open accounts, apply for credit, or commit fraud.
- Check your Digital Footprint regularly to see if your personal details have been exposed.
Cybercriminals often exploit the confusion that follows a breach. They know victims will be expecting emails and updates from the affected company, making phishing messages more convincing.
Monitor Kodak’s official website for updates, and be skeptical of unsolicited emails, texts, or phone calls the reference the incident. Look for inconsistencies, unusual sender addresses, and strange links, and watch out for the two biggest warning signs: pressure to act immediately and requests for money, passwords, or personal information.
Let’s face it, an incognito window can only do so much.
Breaches, dark web trading, credit fraud. Malwarebytes Identity Theft Protection monitors for all of it, alerts you fast, and comes with identity theft insurance.