




惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

H
Help Net Security
Cyber Security Advisories - MS-ISAC
博客园 - 【当耐特】
Microsoft Azure Blog
Google DeepMind News
Apple Machine Learning Research
有赞技术团队
有赞技术团队
Y
Y Combinator Blog
H
Hackread – Cybersecurity News, Data Breaches, AI and More
爱范儿
爱范儿
L
LangChain Blog
IT之家
IT之家
酷 壳 – CoolShell
酷 壳 – CoolShell
MongoDB | Blog
MongoDB | Blog
Hugging Face - Blog
Hugging Face - Blog
G
Google Developers Blog
T
Tailwind CSS Blog
Engineering at Meta
Engineering at Meta
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
宝玉的分享
宝玉的分享
博客园 - 三生石上(FineUI控件)
D
DataBreaches.Net
Recent Announcements
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More

NetBird - Networking Knowledge Hub - RSS Feed

NetBird Is Now on the Vultr Marketplace Native NetBird on the GL.iNet Comet Pro (GL-RM10) NetBird v0.71 - IPv6 Overlay Addressing NetBird Exit Nodes - Appear at Home, or Anywhere Else Reporting Bugs and Requesting Features in NetBird Setup and Use Local AdGuard Home Anywhere with NetBird DNS How to Set Up NetBird on PiKVM for Secure Remote KVM Access NetBird v0.69 - CrowdSec IP Reputation for the Reverse Proxy Cloudflare Mesh vs NetBird vs Tailscale: Performance Compared Self-Hosting Nextcloud with Docker and NetBird Implementing Zero Trust with NetBird NetBird v0.67 - Layer 4 Proxy Support for TCP, UDP, and TLS Solwr Enhances Remote Connectivity with NetBird Self-Hosting NetBird with Authentik Jellyfin Media Server - Self-Host Your Movies, TV, and Music Cloudflare Tunnels vs. NetBird Reverse Proxy INFITX Builds Zero-Touch Kubernetes Networking with NetBird NetBird v0.66 - Expose Local Services to the Internet from the CLI Pangolin vs. NetBird Home Assistant Setup Guide with EASY Remote Access NetBird v0.65 - Built-in Reverse Proxy with Custom Domains Docker for Beginners - Everything You Need to Get Started NetBird for SOC 2 Compliance NetBird v0.63 - Custom DNS Zones for Private Network Resolution Vibecode This in a Weekend and Take 5% of the Company NetBird v0.62 - Built-in Local Users with Optional IdP Integration NetBird v0.61.0 - Granular SSH Access Control and Automatic Updates Top 5 Alternatives to OpenVPN Top 5 Open Source Alternatives to Tailscale Top 5 Alternatives to ZeroTier
Improving Unidirectional Access Control
Written byJack Carter · 2025-09-29 · via NetBird - Networking Knowledge Hub - RSS Feed

NetBird's access control policies had a significant limitation: when you configured ALL or ICMP protocol access between peers, traffic flowed in both directions by default. Our previous method for handling reply traffic opened the reply path based on the reversed connection details, which worked for specific TCP or UDP ports but created limitations and was too rigid for broader policies like ALL where reply ports couldn't be predicted. This gap significantly limited true Zero Trust micro-segmentation.

NetBird's new unidirectional access control policies required different approaches depending on the platform. On Linux, NetBird leverages native firewall capabilities with established rules like that automatically handle reply traffic through the kernel's connection tracking. For non-Linux platforms where NetBird doesn't integrate with native firewalls, we built our own stateful firewall in userspace with a connection tracker that dynamically creates temporary rules for reply traffic on demand. For TCP, we track the full state machine. For UDP and ICMP, we track sessions using timeouts. This essentially recreates what Linux firewalls accomplish with "related, established" connection states, but entirely in userspace.

The frontend changes were more straightforward: removing the restrictions in both the API and UI that previously forced ALL, ICMP, and all-ports TCP/UDP policies to be bidirectional. The new interface provides intuitive direction indicators and smart warnings when you select network resources as the destination, eliminating guesswork about policy direction.
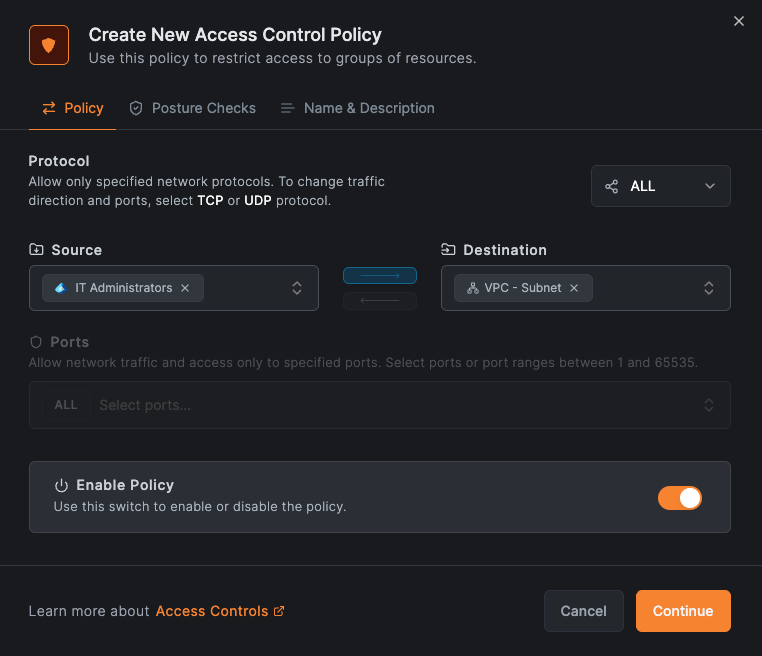
Unidirectional Access Policy

The security impact is immediate and powerful. Unidirectional policies enforce a fundamental principle: backend resources shouldn't initiate outbound connections. Your application servers maintain full access to databases and file servers, but those backend systems can't reach back out to applications or other systems. If a database gets compromised, it stays contained instead of becoming a launching point for network-wide attacks.

Available in NetBird version v0.36.6, this capability delivers the enterprise-grade directional access control that makes Zero Trust implementations actually work as intended.