


Socket proactively blocks malicious open source packages in your code.
Socket now detects missing lockfiles with Manifest Alerts, a new kind of alert for supply chain risks found in project manifests.
The feature was built in response to a real problem customers faced during the Axios npm compromise. Due to the complexities of modern dependency resolution, the blast radius of this incident was much wider than it initially appeared. Exposure was not limited to projects that directly depended on the compromised Axios version.
For teams with committed lockfiles and deterministic installs, it was easier to verify what dependency versions were resolved. But for repos without lockfiles, the dependency tree was not pinned. A fresh install could resolve to a different set of versions depending on when it ran, what versions were available in the registry, and whether the workflow introduced new dependency resolution.
Manifest Alerts are designed to make that risk more visible. They surface problems found in your manifests, not in the dependencies themselves.
A lockfile records the exact dependency versions resolved by a package manager. Without one, installs can drift over time. Two identical install commands can produce different dependency trees if the registry changes between runs.
That is what makes missing lockfiles different from most dependency alerts. The risk is not tied to one dependency artifact. The risk is in the project setup itself.
A missing lockfile turns dependency resolution into a moving target. Security teams may be able to inspect the manifest, but the manifest alone does not show the exact dependency tree that will be installed. Manifest Alerts flag that gap directly, so teams can identify projects where the resolved dependency graph is not reproducible from the files in the repo.
Missing lockfiles make dependency exposure harder to reproduce, harder to verify, and harder to contain.
Socket now includes Manifest Alerts alongside Dependency Alerts.
Dependency Alerts continue to show risks tied to specific packages. Manifest Alerts show risks tied to the manifest itself. With this release, Socket detects when a package manifest exists without a corresponding lockfile and alerts that the dependency tree is not pinned.
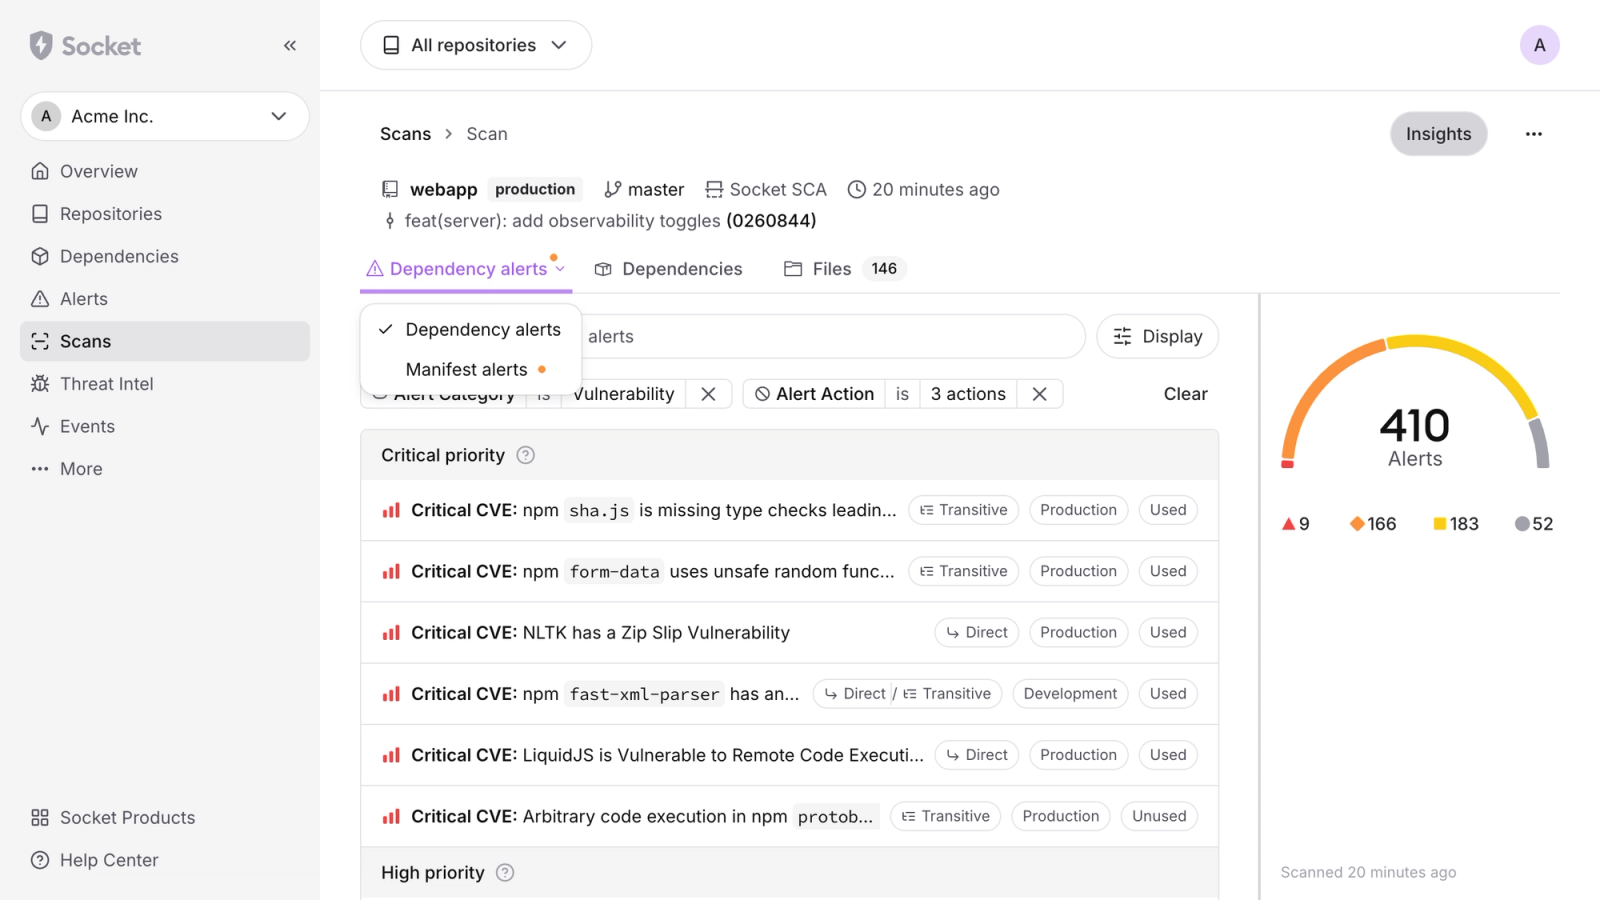
In scan results, Socket separates alerts into Dependency Alerts and Manifest Alerts. If a scan has alerts in the other view, Socket shows a banner so users can switch between them without missing important findings.

When Socket detects a missing lockfile, the alert identifies the manifest where the issue was found and explains that the dependency tree is not pinned. The dedicated alert drawer includes:
Impact: How the missing lockfile affects dependency resolution and reproducibility.
Remediation: Package-manager-specific guidance for generating a lockfile with npm, pnpm, yarn, or bun.
About: Additional details about the manifest alert.

Teams can ignore a Manifest Alert, undo the ignore action, or create a ticket from the alert drawer if Jira or Linear are connected.
Manifest Alerts help teams find repositories where dependency installs are not reproducible, and the missing lockfile alert is the first one we’re shipping. This is part of a broader direction for surfacing issues that live in manifests rather than individual packages. We’re exploring additional alerts for cases like malformed manifests, plain HTTP dependency references, and lockfiles that are out of date with the primary manifest.

Manifest Alerts are available today in Socket. They extend Socket’s visibility beyond individual packages and into the project configuration decisions that determine how dependencies are installed.
Run a scan to identify missing lockfiles in your repositories, then use the remediation guidance in the alert drawer to generate the right lockfile for npm, pnpm, yarn, or bun.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。