

惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

美团技术团队
N
Netflix TechBlog - Medium
WordPress大学
WordPress大学
云风的 BLOG
云风的 BLOG
J
Java Code Geeks
V
Visual Studio Blog
H
Help Net Security
Engineering at Meta
Engineering at Meta
Hugging Face - Blog
Hugging Face - Blog
Microsoft Security Blog
腾讯CDC
博客园 - 【当耐特】
B
Blog
Stack Overflow Blog
Stack Overflow Blog
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
大猫的无限游戏
大猫的无限游戏
GbyAI
GbyAI
博客园 - 司徒正美
博客园 - 叶小钗
Y
Y Combinator Blog
MyScale Blog
MyScale Blog
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
G
Google Developers Blog
酷 壳 – CoolShell
酷 壳 – CoolShell

Socket

Fake Corepack Site Distributes Infostealer and Proxyware to ... Large-Scale GitHub Actions Abuse Powers a Distributed cPanel... New Study Identifies 53 Slopsquatting Targets Across 5 Front... White House Launches Gold Eagle Initiative to Manage Surge i... Suno Breached via Shai-Hulud Worm, Leaked Code Exposes AI Mu... Next.js moves to scheduled security releases - Socket 11 Malicious NuGet Tools Pose as Game Cheats to Drop a Windo... Compromised npm Packages in the AsyncAPI Namespace Deliver M... jscrambler npm Package Compromised in Supply Chain Attack - ... Fake Braintree NuGet Package Skims Credit Cards and Harvests... Compromised Injective SDK npm Package Exfiltrates Wallet Key... npm v12 Ships With Install Scripts Off by Default, Begins De... Malicious Go Module Exposes GitHub Malware Lure Network Span... pnpm 11.10 Hardens Registry Authentication to Block Token Re... Coordinated npm and PyPI Campaign Typosquats Popular Secure ... Node.js Considers Public Workflow for Security Reports Amid ... PolinRider: North Korea-Linked Supply Chain Campaign Expands... Risky Biz Podcast: AI Agents Are Raising the Stakes for Soft... Chrome and Firefox Extensions Posing as Free VPNs Add Clipbo... Miasma Mini Shai-Hulud Hits ImmobiliareLabs npm Packages - S... Rolldown Pulls Rust React Compiler Integration After Binary ... Miasma Mini Shai-Hulud Hits LeoPlatform npm Packages and Git... Frontier AI Is Now Critical Infrastructure - Socket The Code You Didn't Write Is Still Yours to Defend - Socket GitHub Actions Checkout Now Blocks Risky pull_request_target... Introducing Repository Access Permissions and Custom Roles -... Socket MCP Adds Org Alerts, Threat Feed Review, and Package ... Socket Firewall Now Blocks Malicious VS Code and Open VSX Ex... 140+ Mastra npm Packages Compromised in Coordinated Supply C... npm Package Uses Prompt Injection and Token Flooding to Disr...
Socket Partners with Replit to Block Malicious Packages i...
Feross Aboukhadijeh · 2026-06-11 · via Socket

The way software gets built is changing fast. Developers are no longer the only ones choosing dependencies. AI agents can now recommend, install, and wire open source packages into applications as part of the build process.

Replit is at the center of that shift, giving millions of builders a faster path from idea to working software. As more of that work happens inside AI-powered workflows, dependency security has to move closer to the moment packages are selected and installed.

Socket Firewall is now built into that experience to give Replit users stronger protection. It evaluates open source packages as they are introduced into the build, helping stop attacks that do not wait for code review, such as typosquatted and impersonated packages, malicious transitive dependencies, install scripts that fetch second-stage payloads, credential stealers, and packages tied to known malicious infrastructure.

The impact is already visible at scale. Since rolling out the firewall, Replit is already blocking around 8,000 packages per day across builders on the platform. Over the course of a year, that adds up to millions of blocked package installs, giving Replit users stronger protection by default.
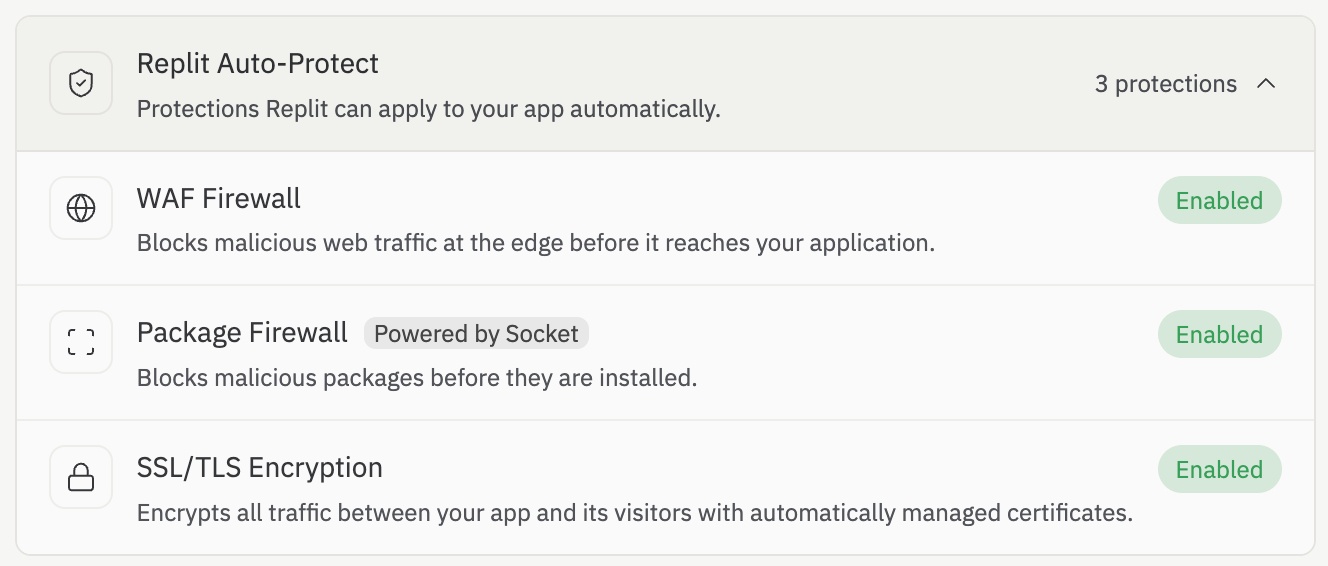
We’ve seen a relentless wave of fast-moving attacks hitting open source lately: malicious packages that do serious damage during installation, before anyone has time for manual review. Once they land in the build environment, it's already too late. By partnering with Replit, we are putting Socket’s threat intelligence directly in the install path, helping builders move fast while blocking supply chain attacks.

“Software is being created faster than at any moment in history, and attackers are racing to take advantage. This is one of the defining problems of the AI era. Replit and Socket are putting security in the building loop, blocking malicious code before it ever runs, so millions of builders stay protected while they create.” — Amjad Masad, CEO of Replit.

Open source makes modern software possible. It also gives attackers a direct path into the development process. That risk is amplified in AI-assisted development where agents are empowered to pull in dependencies automatically when completing tasks.

The answer is not to slow builders down. It is to put better security inside the tools they already use. We’re excited to partner with Replit to help builders continue shipping with confidence.