








Socket proactively blocks malicious open source packages in your code.
In May 2026, GitHub disclosed that attackers compromised an employee device through a poisoned third-party VS Code extension, allowing them to exfiltrate roughly 3,800 GitHub-internal repositories.
The extension was Nx Console 18.95.0, a malicious release that reached both the Visual Studio Marketplace and Open VSX before removal. That incident should change how security teams think about editor extensions.
Socket researchers have also documented repeated GlassWorm attacks across Open VSX, including malicious and compromised extensions designed to steal developer credentials and spread through trusted editor marketplaces.
What many teams still underestimate is the level of access code editor extensions have. These extensions are third-party code running inside developer environments, often with access to source code, terminals, files, credentials, tokens, and internal systems.
Organizations standardizing on AI-first editors inherit a marketplace they can’t gate. The install and update is the moment to intervene.
Today, Socket is extending Firewall protection to editor extensions.
Socket Firewall now supports VS Code Marketplace and Open VSX extension installs, helping organizations block malicious editor extensions before they reach developer environments. The same enforcement layer that protects package installs can now sit in front of editor extension traffic, filtering marketplace results and blocking extension downloads based on threat verdicts.
Most extension security starts too late. An inventory tool can tell a security team which extensions are already installed. It can help with visibility, cleanup, and compliance. But by the time a malicious extension appears in inventory, the code has already run.
That is the gap Socket Firewall is built to close.
Socket Firewall gives organizations an install-time and update-time control point for editor extensions. When an editor browses, installs, or updates an extension, the request flows through Socket’s proxy. Socket forwards the request to the real registry and filters the response against threat verdicts so flagged extensions are blocked before they can install or update.
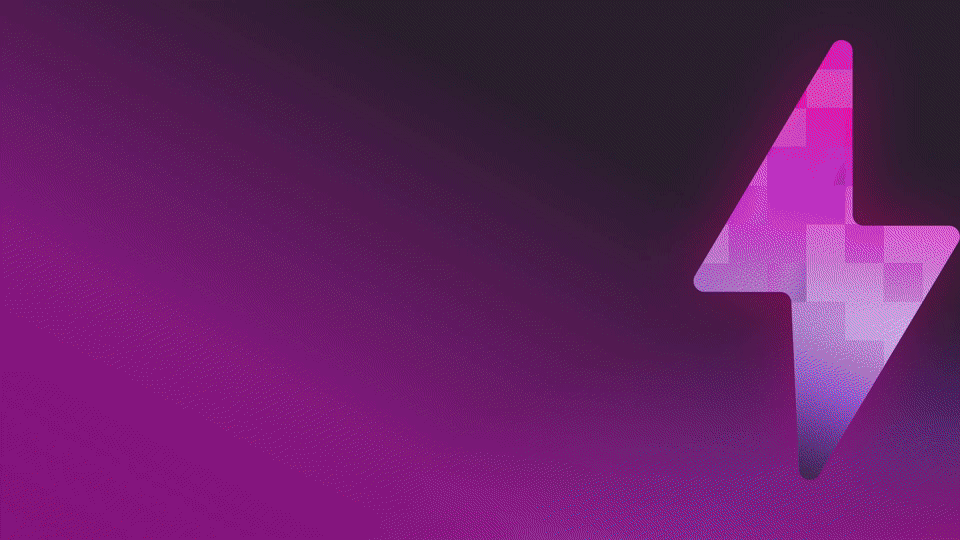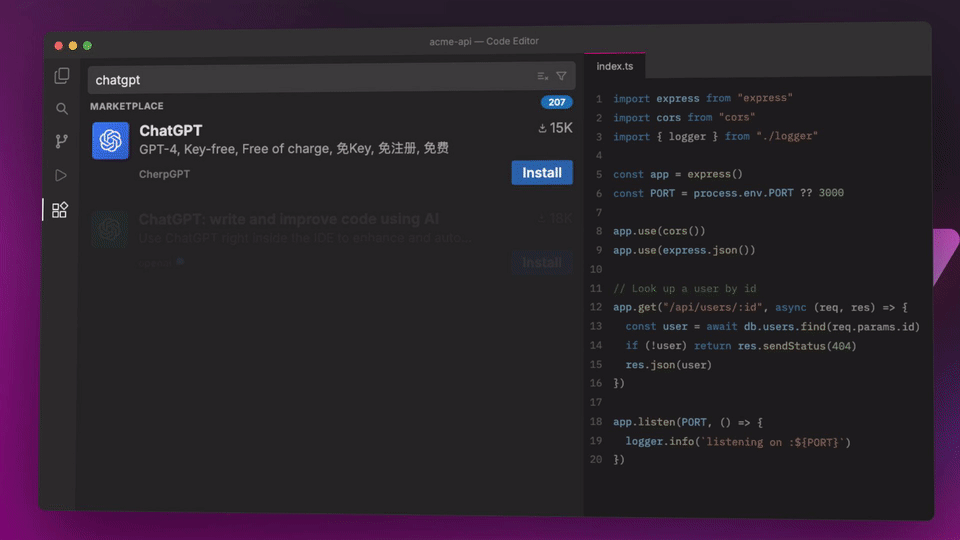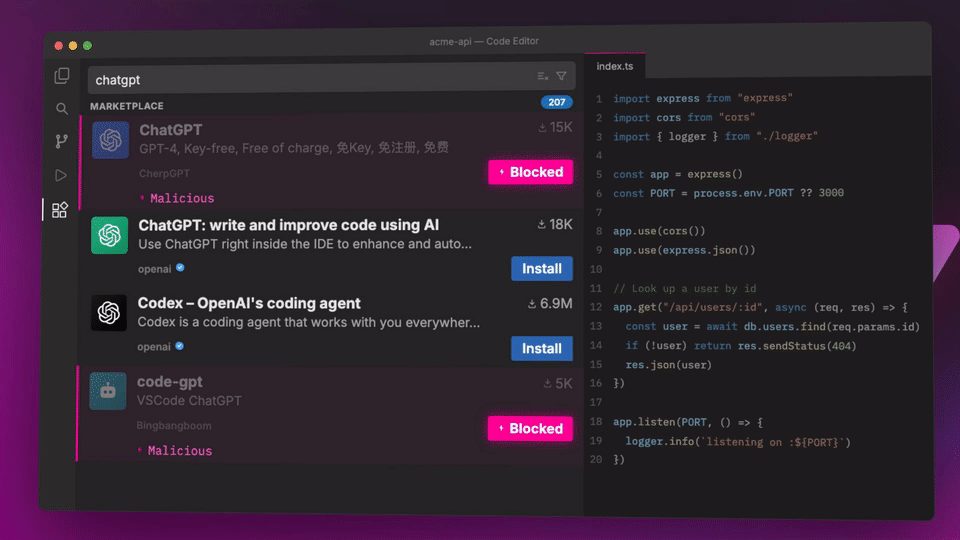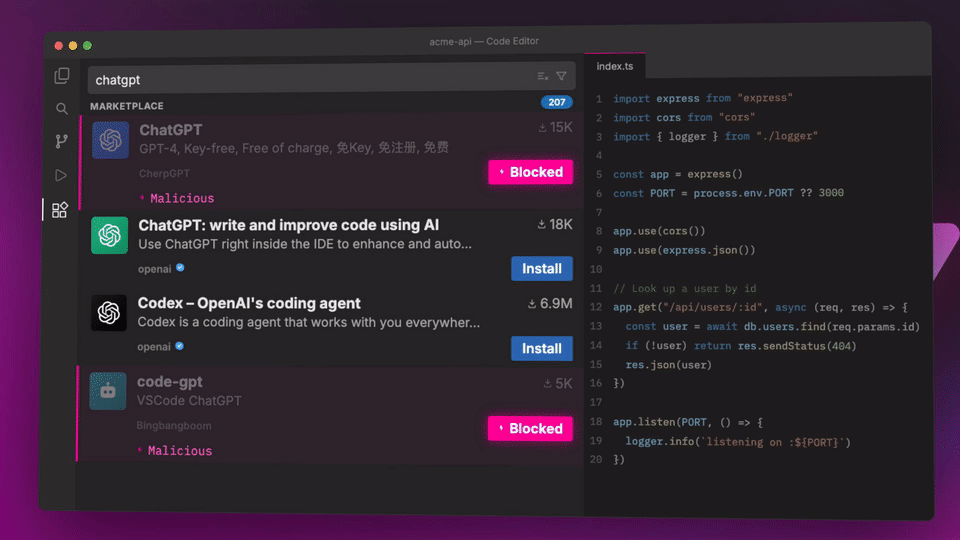
When a developer searches for or installs an extension, the editor’s marketplace request flows through Socket’s proxy. Socket forwards the request to the real registry, checks extension verdicts, and filters or blocks flagged extensions during the marketplace flow.
That means malicious extensions can be stopped before they install, instead of being discovered only after they are already running inside a developer environment. The proxy sits in front of each registry’s extension asset domains and checks verdicts before forwarding VSIX downloads. This gives organizations a second enforcement point beyond marketplace search results, helping block malicious extensions even when an install flow reaches the underlying download URL.
In the developer experience, clean extensions remain available. Flagged extensions are blocked from installation, with the firewall enforcing policy in the path between the editor and the extension registry.
Socket Firewall already protects package manager traffic across ecosystems such as npm, PyPI, Go, Maven, and more. Now, that same prevention model extends to two major editor extension ecosystems:
Developer extension risk is not limited to one editor. Many organizations now support multiple coding environments, including AI-native editors and VS Code forks that rely on Open VSX. Security teams need one enforcement model that can cover both marketplace ecosystems.
Socket Firewall gives teams an install-time and update-time control point for editor extensions, using the same enforcement model already protecting package installs.
For developers, the workflow stays simple: safe extensions continue to work, while malicious extensions are blocked before install or update.
Extension Firewall is available in beta today for Socket Enterprise customers. The feature supports marketplace filtering, VSIX download blocking, and multiple rollout paths across editor configuration, DNS override, and enterprise egress forwarding.
To turn on access and learn more about deploying Socket Firewall for editor extensions, contact our sales team.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。