







Every security team knows the moment: a scan finishes, results appear, and there’s no clear next step. Thousands of findings, dozens of critical vulnerabilities, and no obvious place to begin. The real question isn’t what to fix, but where to start and how to finish.
At Sysdig we’re reimagining this experience. Vulnerability management shouldn’t be a guessing game or a race against endless alerts. It should be an intelligent, end-to-end workflow that identifies what matters, guides remediations, and proves progress. That’s exactly what we’re building with Sysdig Sage™, our AI cloud security analyst.
If you spend your day dealing with vulnerability data, you already know the problem: finding issues is easy, but fixing them efficiently isn’t. Most scanners overwhelm you with results and leave you sorting through generic risk scores with little context to help you take action.
Sysdig Sage changes this by combining AI reasoning with real runtime visibility. Instead of working just with scan results, Sysdig Sage analyzes what’s actually running in your environment, like which packages are loaded at runtime, which images are deployed, and which workloads are exposed. It uses this context to determine which vulnerabilities to prioritize and what to fix first.
From there, Sysdig Sage generates clear, step-by-step remediation guidance, tailored to your environment, helping you focus on high-impact fixes that make a measurable difference to your risk posture. The outcome? Fewer false positives, less manual triage, and more effective remediation.
The first step in effective vulnerability management is separating real risk from background noise. Many tools flag everything, leaving you buried in results that lack context. Sysdig simplifies this by combining AI reasoning with runtime intelligence to highlight the vulnerabilities that require your immediate focus.
With Sysdig Sage, your vulnerability scope shrinks considerably. It automatically identifies your production environments and applies several layers of intelligent filtering. For example, it removes vulnerabilities tied to inactive packages and deprioritizes those that require missing runtime conditions. Each filter is explained directly in the platform, so you can see how noise is reduced and act with confidence.
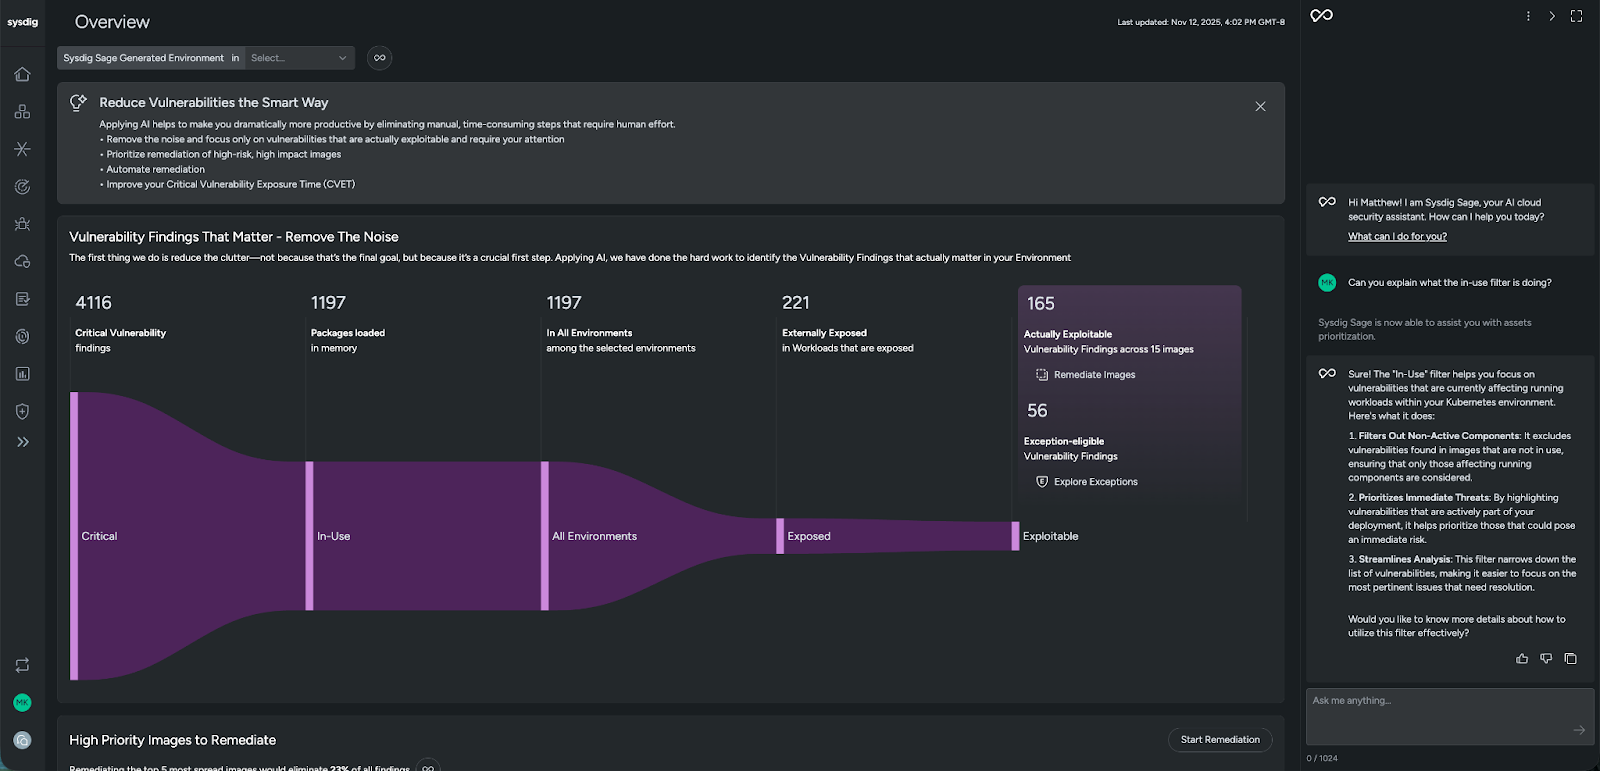
Once the clutter is gone, Sysdig Sage goes beyond basic severity scoring to determine what deserves attention first. It analyzes factors like how widely a vulnerability appears across your environment, identifying common images or dependencies that multiply exposure. For example, a single base image upgrade might resolve a dozen critical vulnerabilities and reduce risk across hundreds or even thousands of workloads in one move.
At the same time, Sysdig Sage factors in real-world impact and fixability. Vulnerabilities that could expose sensitive data or interrupt business-critical services are moved to the top, along with low-risk fixes that can be applied cleanly without breaking dependencies. By weighing these elements together, Sysdig Sage delivers not just a sorted list, but an actionable plan to focus on what’s widespread, what’s dangerous, and what’s fixable right now.
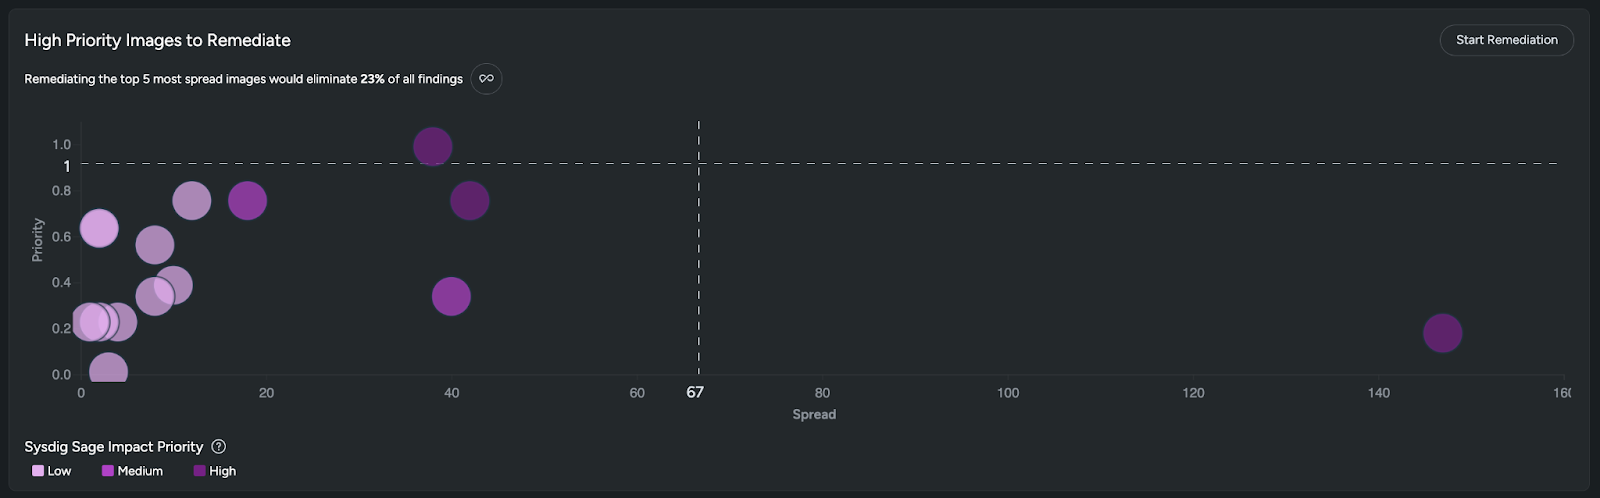
After identifying what to fix, the next hurdle is figuring out how. You shouldn’t have to research which library version or base image patch is safe to use. Sysdig Sage eliminates that guesswork.
Within Sysdig’s vulnerability management workflow, Sysdig Sage generates step-by-step remediation guidance in clear, actionable language. Each recommendation includes the exact package or image update to apply.
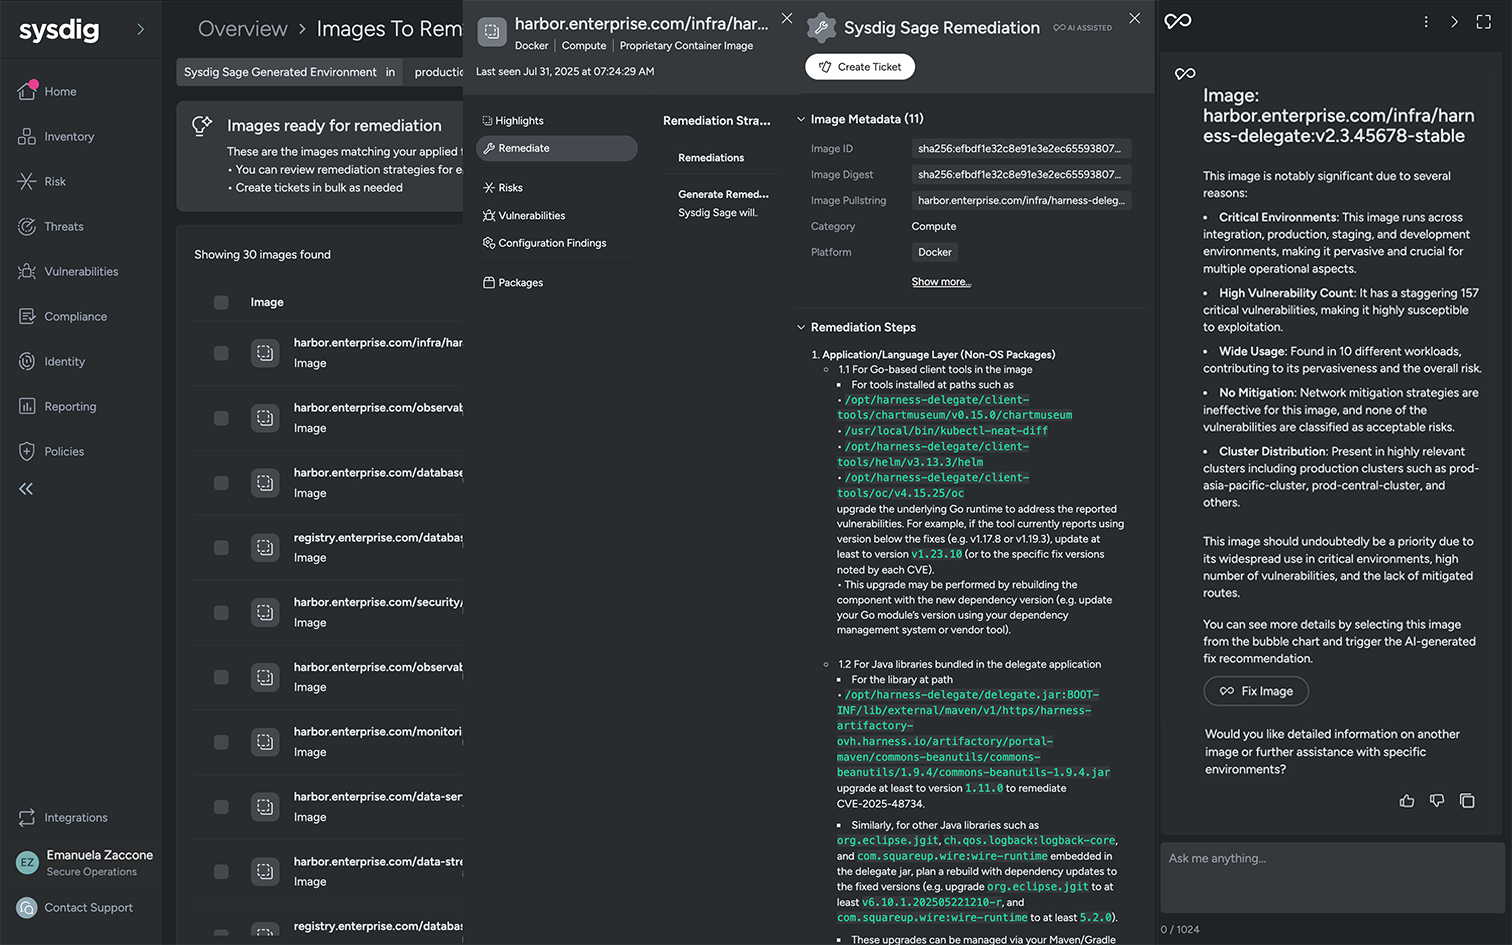
You can push these instructions directly into a ticketing system like Jira, pre-filled with the context developers need. Instead of extended back-and-forths about priorities, your developers receive a clear request that’s easy to act on.
By pairing precise guidance with integration into development workflows, Sysdig Sage removes the lag between discovery and remediation, reducing the time risk exists in your environment.
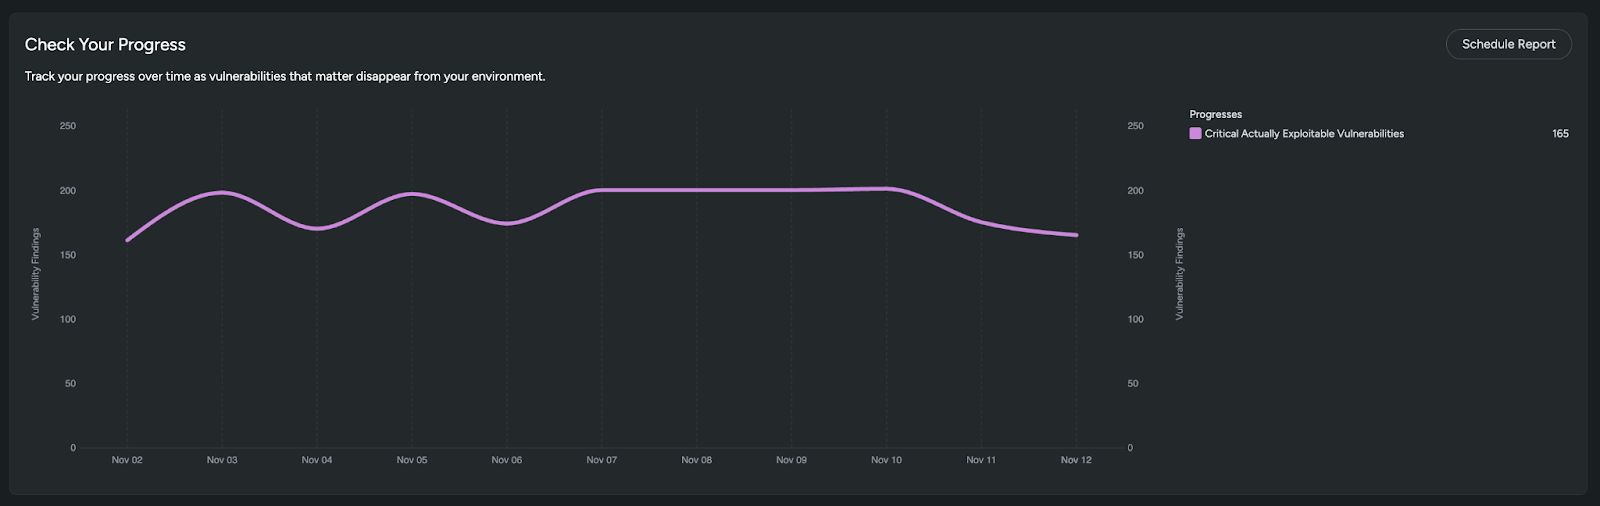
For many security practitioners, showing progress is as important as making progress. Whether you’re reporting to a security lead, a compliance manager, or just keeping track for yourself, you need metrics that reflect real improvements.
Sysdig Sage tracks risk posture metrics like exposure time and time to remediation. When it’s time to report, audit-ready summaries highlight remediation trends, business impact, and compliance progress without needing to export data or build custom dashboards. You can easily share these results with leadership or development teams to close the loop and keep everyone aligned on outcomes
Sysdig Sage is at the core of Sysdig’s Agentic Cloud Security Platform, which means AI isn’t just suggesting, it’s acting.
Agentic AI is goal-oriented intelligence designed to handle repetitive security tasks autonomously. It continuously monitors your environments, adapts to its unique characteristics, and takes action with minimal human input. It’s like having another member of your team that never gets tired of sorting through CVEs or misses a deployment change.
This autonomy is powered by Sysdig’s deep runtime visibility. By capturing live system calls, logs, package activity, and process behavior across containers, servers, and cloud services, Sysdig Sage operates with the most complete context in the industry. Its recommendations aren’t based on static assumptions but are grounded in what’s actually happening in your environment. When it comes to vulnerability management, this foundation lets Sysdig Sage determine whether a vulnerable library is ever loaded, whether an image is externally exposed, or whether a vulnerability's impact goes beyond a single instance.
For practitioners, this means fewer false alarms, smarter prioritization, and far less back-and-forth between security and development. Teams using Sysdig Sage have reported saving up to 80 hours per week on manual triage and achieving 90% faster remediation of critical vulnerabilities. When AI understands how your environment truly runs, every recommendation becomes more accurate, actionable, and valuable.
Vulnerability management is evolving fast, and Sysdig Sage is closing the gap, helping security practitioners focus on what’s real, automate repetitive work, and have confidence that every fix makes a measurable difference.
As Sysdig continues to evolve, Sysdig Sage is moving vulnerability management toward continuous remediation, where identification, prioritization, and remediation happen in sync with your environment. Vulnerabilities are surfaced earlier in the pipeline, package updates are recommended automatically, and low-risk fixes can be executed within defined guardrails. The goal isn’t just faster remediation. It’s security that operates continuously, at the speed of the cloud.
For practitioners, this means less time chasing alerts and more time strengthening defenses. At the end of the day, vulnerability management isn’t complete until vulnerabilities are fixed. With Sysdig Sage, you can do it faster, smarter, and continuously.
See how Sysdig Sage turns vulnerability management into intelligent action by requesting a demo today!
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。