









Over the past year, several signals have pointed to an important shift in how modern applications are being built and how they must be secured. With the rapid acceleration of AI development, cloud-native infrastructure continues to expand to support these new workloads. Kubernetes has quickly become the foundation for modern cloud applications and is becoming the platform of choice for AI workloads.
Recent industry data reflects just how quickly this shift is happening. A majority of organizations are using Kubernetes to run AI workloads, reinforcing that AI development is overwhelmingly cloud-native. These environments rely on complex open source stacks, containerized applications, and highly dynamic infrastructure. For security teams, understanding risk now depends on visibility into what workloads actually do once they’re running.
This shift toward runtime visibility is reflected in the latest GigaOm Radar for Cloud Workload Security, which evaluates leading vendors across the market. We’re proud to share that Sysdig was named a Leader and Fast Mover in the report, highlighting our strong capabilities for protecting modern cloud workloads built on containers and Kubernetes.
To learn more about why Sysdig was named a Leader, get access to the full report.
One of the clearest insights from GigaOm’s report is how rapidly the cloud workload security market is maturing. Capabilities like threat detection and response have become foundational elements of cloud workload security (CWS) and are now widely expected across vendors.
What differentiates solutions is how effectively they bring these capabilities together with deeper runtime visibility and context to deliver more advanced workload defense. By correlating detection signals with information about active workloads, vulnerabilities, and configuration risks, security teams can gain a clearer understanding of what is actually happening in their environments and act on risks that require immediate attention.
In modern cloud environments, containerized workloads can appear and disappear quickly as applications scale and evolve. Vulnerabilities may exist across thousands of images and services, but only a small percentage are actually exploitable in running workloads. Without runtime visibility, teams are often left chasing alerts that may never create real risk.
As the market evolves, organizations need to adjust how they evaluate cloud workload security tools, looking beyond basic detection capabilities toward deeper runtime insight and contextual risk analysis.
According to GigaOm’s analysis, leading cloud workload security platforms increasingly bring together multiple layers of visibility and protection.
This includes runtime monitoring that detects suspicious behavior in active workloads, attack path analysis that correlates vulnerabilities and misconfigurations into real-world risk scenarios, and integrations that connect security insights directly into development workflows.
By combining these capabilities, organizations can move beyond isolated alerts and gain a more complete picture of real-time risk in their cloud environments. Security teams are able to focus on the vulnerabilities and threats that truly matter, improving response speed while reducing alert fatigue.
As the cloud workload security market evolves, organizations are looking for platforms that can deliver strong runtime protection while connecting insights across complex cloud environments.
In their report, GigaOm named Sysdig a Leader and Fast Mover, reflecting Sysdig’s strong capabilities for protecting container and Kubernetes workloads.
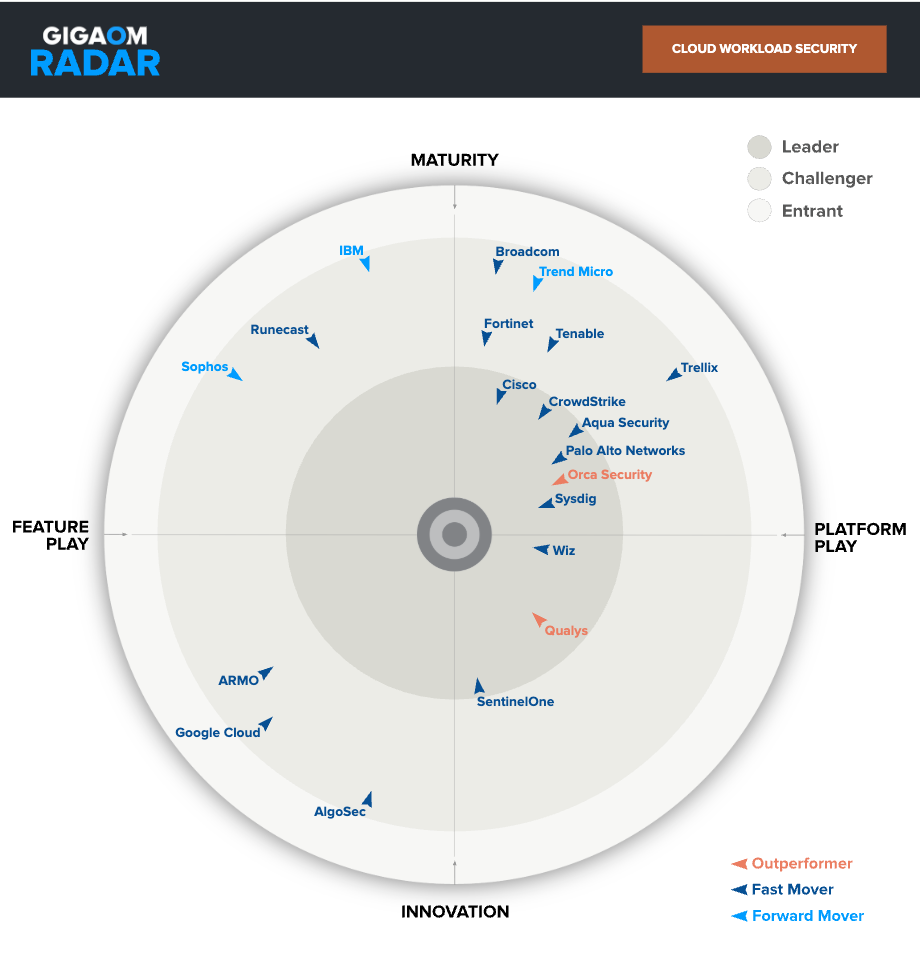
The evaluation highlights Sysdig’s “expertise in container security and deep system visibility” validating Sysdig’s runtime-centered approach to cloud security and alignment with the needs of organizations with significant container and Kubernetes deployments. The report also notes Sysdig’s strengths across several areas, including hybrid environment support, continuous visibility of workloads, and CI/CD integration.
GigaOm specifically noted “[Sysdig] Sage AI technology enhances operational expertise by providing contextual explanations that develop staff technical capabilities.” This reflects the momentum behind Sysdig Sage™, the AI-powered cloud security analyst that employs multi-step reasoning and contextual awareness to accelerate the resolution of complex cloud attacks.
These capabilities reflect Sysdig’s focus on providing deep runtime visibility combined with contextual insights that help security teams defend the cloud-native and AI-driven workloads increasingly running on Kubernetes. By bringing together runtime telemetry with vulnerability, configuration, and threat signals, Sysdig helps organizations prioritize real risk and respond more effectively as workloads evolve.
To explore these findings in more detail, join us for our upcoming webinar, “From Detection to Defense in Cloud Workload Security.”
In this session, we’ll discuss what the latest GigaOm Radar reveals about the evolution of the cloud workload security market and why runtime visibility and contextual risk prioritization are becoming essential for protecting modern cloud environments. We’ll also look at how organizations are evaluating solutions as the market shifts beyond basic detection capabilities.
Register for the webinar to learn more about where cloud workload security is headed and what effective protection looks like in containerized and Kubernetes-driven environments.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。