


惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

J
Java Code Geeks
GbyAI
GbyAI
Google DeepMind News
Jina AI
Jina AI
B
Blog
aimingoo的专栏
aimingoo的专栏
酷 壳 – CoolShell
酷 壳 – CoolShell
T
The Blog of Author Tim Ferriss
Last Week in AI
Last Week in AI
月光博客
月光博客
H
Help Net Security
V
Visual Studio Blog
量子位
A
About on SuperTechFans
博客园 - Franky
人人都是产品经理
人人都是产品经理
N
Netflix TechBlog - Medium
云风的 BLOG
云风的 BLOG
雷峰网
雷峰网
Martin Fowler
Martin Fowler
Microsoft Security Blog
博客园 - 叶小钗
P
Proofpoint News Feed
MongoDB | Blog
MongoDB | Blog

Sysdig Blog

Masterclass: AI is more than ChatGPT and LLMs CVE-2026-39987 update: How attackers weaponized marimo to deploy a blockchain botnet via HuggingFace Kubernetes 1.36 - New security features 5 steps to securing AI workloads Marimo OSS Python Notebook RCE: From Disclosure to Exploitation in Under 10 Hours Security briefing: March 2026 The Sysdig MCP server is now available in AWS Marketplace Risk isn’t reduced until you take action: How teams resolve issues in the cloud AI infrastructure security: Why it deserves its own category Three pillars for building effective runtime-powered cloud defense, the right way Closing the cloud security gap with runtime security Seeing risk isn’t stopping it: Why visibility alone isn’t enough TeamPCP expands: Supply chain compromise spreads from Trivy to Checkmarx GitHub Actions AI coding agents are running on your machines — Do you know what they're doing? Runtime security for AI coding agents: Protecting AI-assisted development How runtime insights power every cloud security use case CVE-2026-33017: How attackers compromised Langflow AI pipelines in 20 hours Inline Cloud Response: Accelerating AWS threat containment for SOC teams Runtime malware detection for AWS Fargate Detecting CVE-2026-3288 & CVE-2026-24512: Ingress-nginx configuration injection vulnerabilities for Kubernetes Malware detection with Sysdig Security briefing: February 2026 Leveling up Kubernetes Posture: From baselines to risk-aware admission Eliminating runtime blind spots: How CleanStart and Sysdig build continuous trust across the container lifecycle LLMjacking: From Emerging Threat to Black Market Reality Real risks live at runtime: Why CISOs must care about deep telemetry in 2026 Sysdig named a Leader in the Forrester Wave™: Cloud Native Application Protection Solutions, Q1 2026 How to run rootless containers AI-assisted cloud intrusion achieves admin access in 8 minutes Security briefing: January 2026
From triage to action: How Sysdig’s agentic cloud securit...
2025-08-05 · via Sysdig Blog

Cloud vulnerability management is broken. Teams are drowning in alerts, chasing false positives, and spending more time debating what to fix than actually fixing it.

But what if your tools could understand what matters and take action on your behalf?

That’s the promise of agentic AI, a new generation of goal-oriented, autonomous AI that doesn’t just assist but actively drives security outcomes. If you’re new to the concept, start here: What is Agentic AI.

At Sysdig, we’re turning that vision into reality, starting with the biggest source of security toil: vulnerability management.

Agentic cloud security: The next chapter for Sysdig Sage™

With Sysdig Sage™, we’ve already helped security teams investigate, respond, and reduce risk across the CNAPP lifecycle. But now, we’re going further.

Agentic cloud security builds on that foundation, introducing autonomous agents that analyze your environment, understand your business, and take action with minimal human effort. Vulnerability management is the first use case, and it sets the tone for what’s next.

Traditional vulnerability management is full of friction

Managing vulnerabilities is notoriously tedious. There's too much noise, too many false positives, and far too many manual steps. We’re here to change that.

Let’s look at the standard vulnerability management lifecycle and why it’s painful:

  1. Asset discovery and assessment
    Collect and scan all workloads. Results are often noisy and incomplete.
  2. Prioritization of identified vulnerabilities
    Manually review hundreds or thousands of findings to decide what matters.
  3. Remediation and mitigation
    Track down owners, open tickets, gather fix guidance, and follow up.
  4. Validation and monitoring
    Manually check whether fixes worked and watch for regression.
  5. Reporting and improvement
    Build executive reports, analyze metrics, and try to iterate.

Every step is heavy with manual work. That means delays, burnout, and risk exposure.

The agentic way with Sysdig Sage

We’ve reimagined every step with autonomous AI agents working on your behalf. Here’s how it works.

Remove the Noise

The first step is cutting through the clutter, not as the final goal, but as the foundation for meaningful action. Every alert we eliminate is time you gain back.
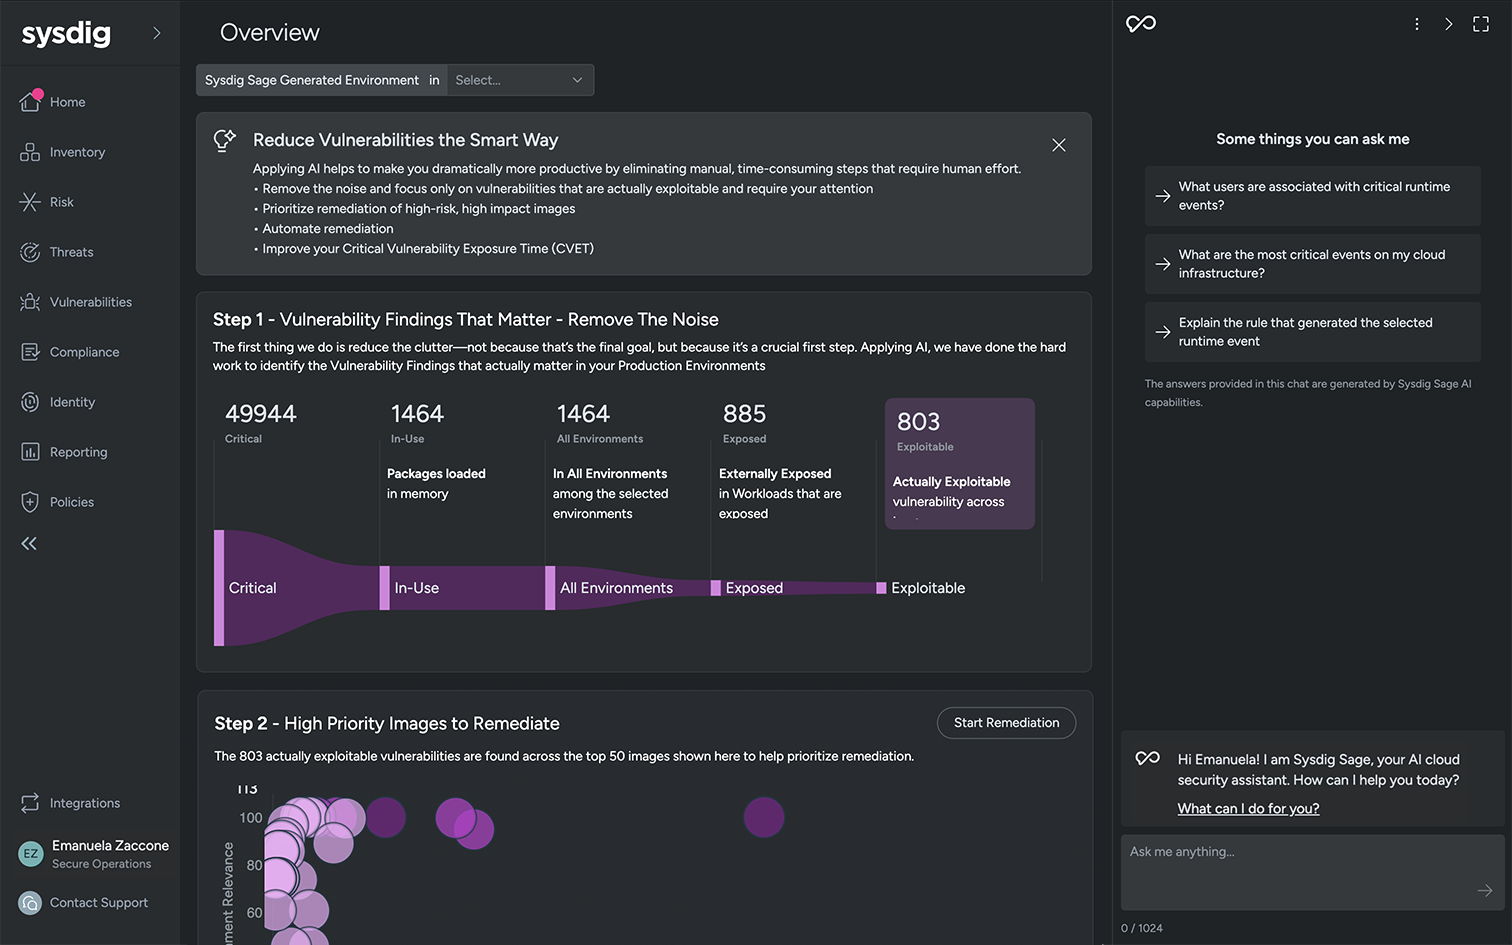
  • Automatically identify production environments using semantic analysis.
  • Runtime-aware filtering removes vulnerabilities not loaded in memory (~50–90% noise reduction)
  • Context-aware filtering deprioritizes CVEs that require missing runtime conditions (~30–90% more)
  • Deep vulnerability analysis adds 5%-10% more by evaluating exploitability in real-world context.
  • You can act on these findings, for example letting Sysdig Sage open JIRA tickets with full context.

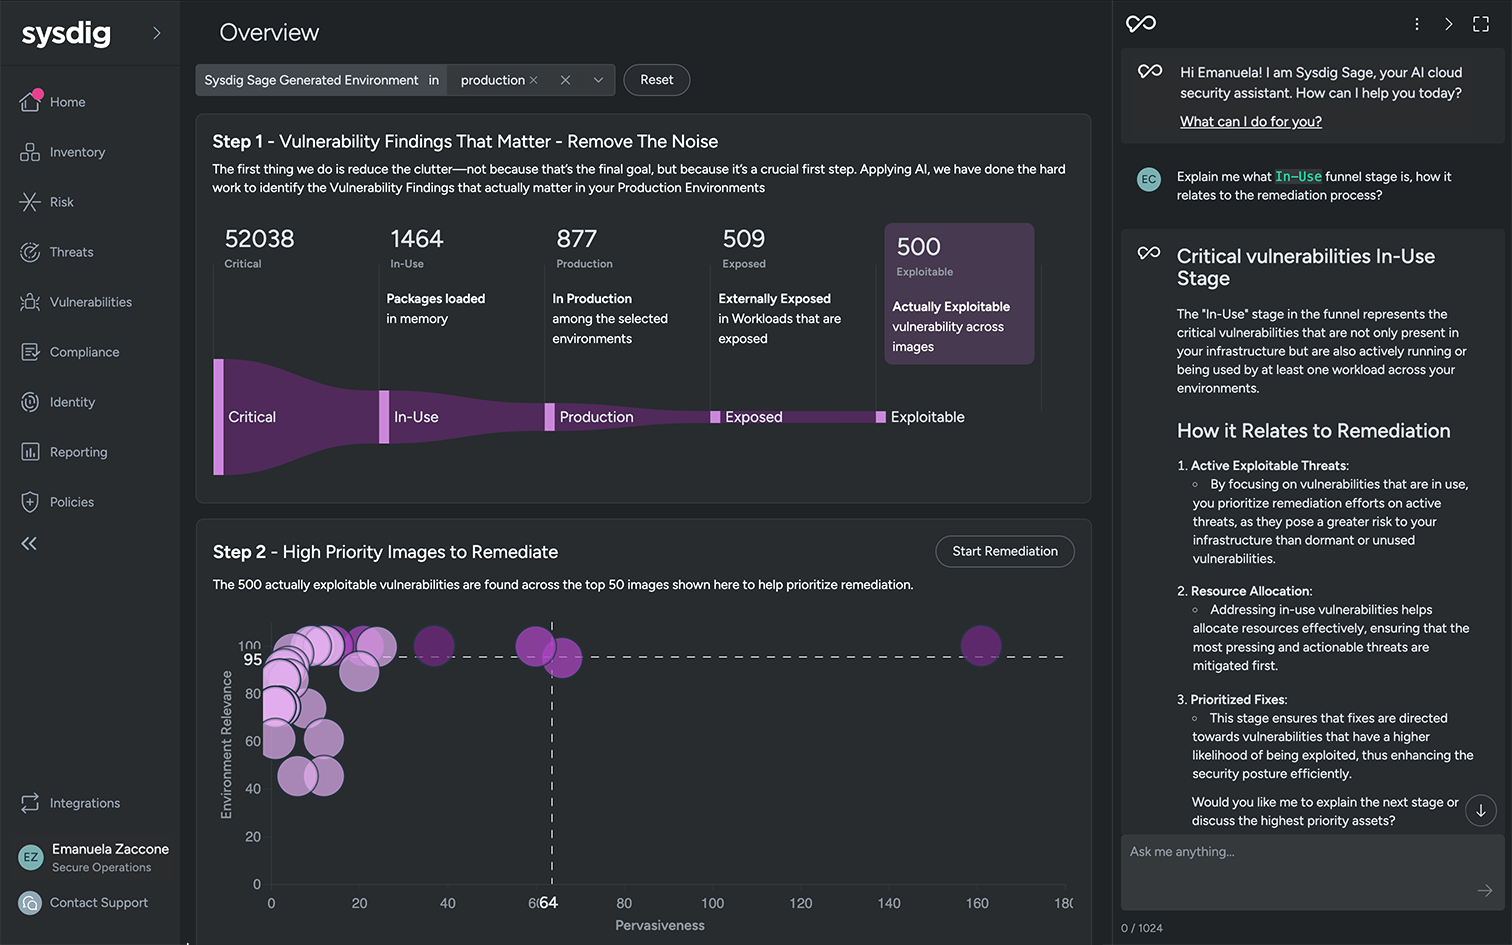
Explain what matters, in context

We don’t just show data, we help you understand what it means.

For every stage in the vulnerability funnel, Sysdig Sage can explain what’s included and why it matters. Without needing to type anything into chat, you can simply click the Sysdig Sage icon directly in the UI and immediately get a clear, contextual explanation of what a specific step of the funnel means, how it’s calculated, and how it helps reduce noise.

This lowers the learning curve for new users and builds trust in the system's decisions.
It's a small interaction, but it reinforces a big idea: Agentic Cloud Security is here to guide the users, not just inform them.

Also, this builds confidence in the filtering logic and helps you trust the prioritization.
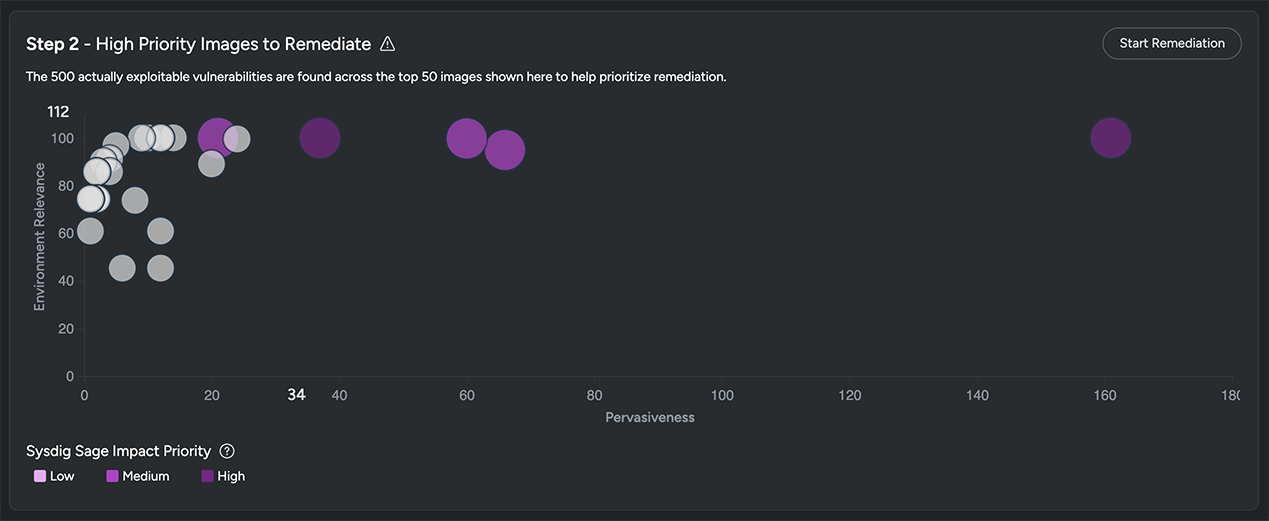
Focus on the vulnerabilities that matter

After the noise is gone, we help you zero in on high-leverage actions.

  • Widespread issues
    Fixing one container image could eliminate thousands of findings.
  • Severity and impact
    We highlight vulnerabilities that could expose sensitive data or create real business risk.
  • Fixability
    If something can be fixed easily, we move it to the front of the line.

Example: Fixing a single image with seven critical vulnerabilities might reduce 7,000 findings across your environment and address 20% of your overall risk.

The bubble chart will focus on three main KPIs: 

  • Environment relevance: Measures the business impact of where the image is running.
  • Pervasiveness: Measures how widespread the image is across workloads.
  • Sysdig Sage impact priority: AI-generated score combining severity, exposure, and environment signals.

Sysdig Sage handles the triage, so you don’t have to. 

The result: faster decisions, less risk, and no wasted effort.
Time to fix

Now that you know what to fix, Sysdig Sage will help you act with:
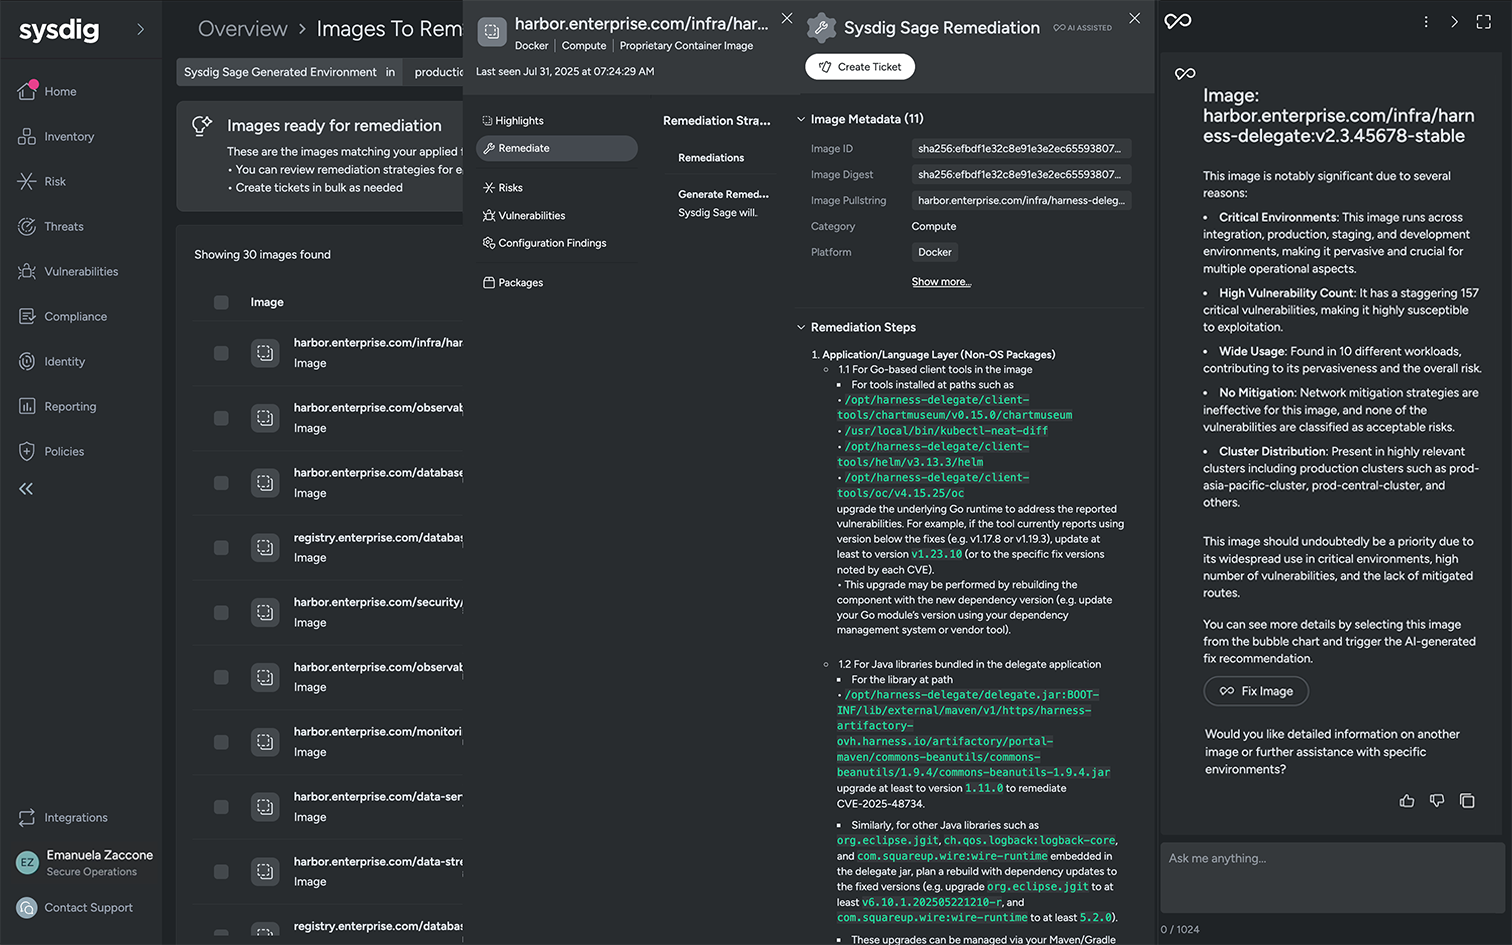
  • AI-generated remediation instructions
    Clear, specific guidance tailored to your environment
  • Automated ticket creation
    Create issues at the image or finding level, pre-filled with all relevant context

Track progress over time

Remediation isn’t just about fixing, it’s about proving progress.

Sysdig Sage makes it easy to track progress and share it with relevant stakeholders.
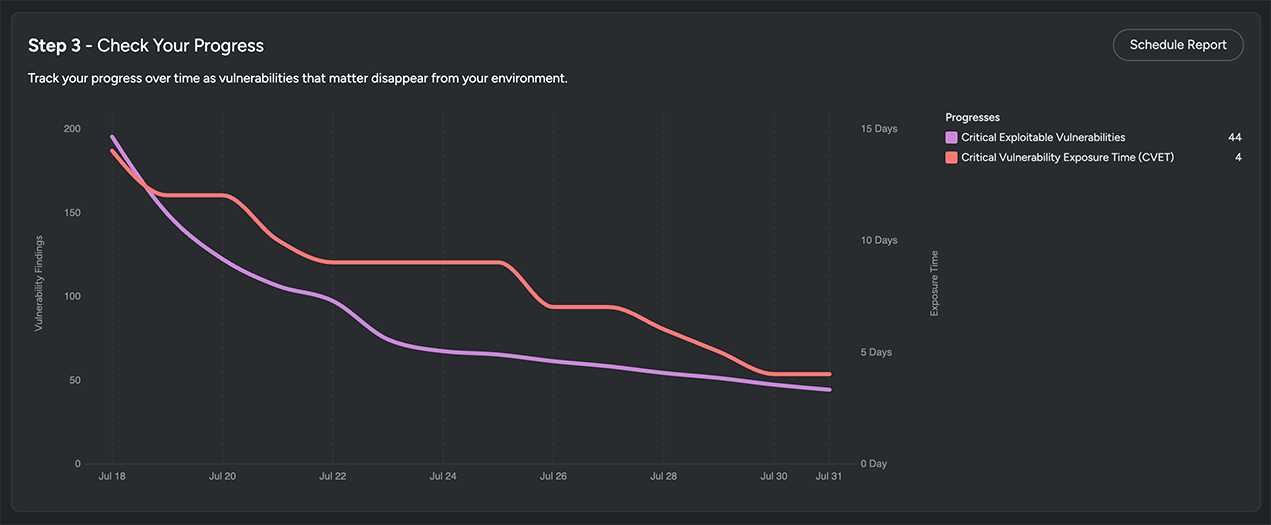
  • Risk posture tracking
    Visualize reductions in exposure and time to resolution.
  • Audit-ready reports
    Demonstrate business impact and compliance.
  • Feedback loop
    Share results with the board, the C-suite, or your dev teams to close the loop.

.

The results, quantified

By turning traditional VM workflows into agentic processes, Sysdig Sage helps you:

  • Save up to 80 hours per week of manual triage and remediation work
  • Reduce time-to-fix for critical vulnerabilities from days to minutes
  • Filter out more than 95% of low-risk noise
  • Shift security teams from reactive ticket triage to strategic improvement

What comes after vulnerability management?

This is only the beginning.

The same agentic architecture will power future capabilities in Cloud Detection and Response (CDR), Posture Management, and Threat Remediation.

We’re building toward a world where AI doesn’t just give you insights, it helps you get things done.

This is how innovation should work. This is cloud security the right way.

Ready to see agentic cloud security in action?

Ready to explore the next chapter of Sysdig Sage and see how agentic AI is reshaping the future of security? Register to attend our webinar: See the Future of Cloud Defense: Agentic Cloud Security in Action.