
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

博客园_首页
H
Help Net Security
N
Netflix TechBlog - Medium
Apple Machine Learning Research
P
Proofpoint News Feed
A
About on SuperTechFans
V
V2EX
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
宝玉的分享
宝玉的分享
aimingoo的专栏
aimingoo的专栏
F
Fortinet All Blogs
博客园 - 【当耐特】
Microsoft Security Blog
Martin Fowler
Martin Fowler
I
InfoQ
Google DeepMind News
人人都是产品经理
人人都是产品经理
Engineering at Meta
Engineering at Meta
腾讯CDC
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
B
Blog RSS Feed
U
Unit 42
The Cloudflare Blog
Y
Y Combinator Blog

Blog | Orca Security

Langflow RCE Actively Exploited to Deploy Cryptominers on AI Infrastructure Orca MCP: When Text Stops Scaling Kubernetes Compliance Tools: Automating CIS Benchmarks Risk-Based Vulnerability Management for the Cloud: A 2026 Guide Private Cloud Security: Top Risks and Best Practices (2026) What Is Generative AI in Cybersecurity? Best Vulnerability Management Tools and Software in 2026 2026 State of Application Security Report Recap: What the Data Says and What Security Teams Should Do About It AI Security for Sensitive Data: Best Practices and Guidelines Best AI Code Security Solutions 2026: How to Secure AI-Generated Code From Platform to Program: How to Ensure Your Cloud Security Solution Delivers Best AI Cybersecurity Providers 2026: A Buyer's Guide to AI-Powered Security Platforms Join Orca Security at Black Hat USA 2026 CNAPP Tools That Reduce Security Tool Sprawl: CNAPP vs. Dedicated Solutions What Is Container Runtime Security? A Practical Guide 2026 What Is Application Security Testing? Tools and Types What Is Managed Cloud Security? A Practical Guide What Is SaaS Security Posture Management? SSPM Guide Top 10 Cloud Security Standards for Compliance What is the MIT License? Compliance and Comparisons AI Agents vs. Agentless Security vs. Agent-based Security 144 Mastra npm Packages Compromised via Supply Chain Attack The Complete Guide to LLM Security: Risks, Best Practices, and Solutions Cloud Security LIVE 2026: Top 10 Takeaways Practitioners Can Use Now Cloud Security LIVE 2026: Top 10 Takeaways CISOs Can Use Now (and What to Do Next) How Orca Traced an nginx Flaw to 1.45 Million Tengine Servers All Running Vulnerable Code What to Look for in Container Security Tools Cloud Application Security Best Practices for DevSecOps Cloud Security Tools: 10 Types Explained for Teams What Is NIST CSF? Framework 2.0 Explained
Critical Apache HTTP Server HTTP/2 Vulnerability Could En...
Roi Nisimi · 2026-05-08 · via Blog | Orca Security

A high-severity vulnerability (CVE-2026-23918, CVSS 8.8) was disclosed affecting Apache HTTP Server, allowing attackers to potentially achieve remote code execution via specially crafted HTTP/2 requests. Due to the potential for server compromise and denial-of-service conditions, immediate patching is strongly recommended.

About the Vulnerability: CVE-2026-23918

The issue originates from Apache’s HTTP/2 protocol handling in mod_http2, where a double-free memory corruption flaw in the stream cleanup logic can lead to heap corruption and possible remote code execution. By sending specially crafted HTTP/2 HEADERS frames followed by an early RST_STREAM request with a non-zero error code, attackers can trigger the vulnerable code path, potentially causing service crashes or gaining arbitrary code execution on affected servers. No authentication is required to exploit this issue.

The following component is affected: Apache HTTP Server mod_http2 in version 2.4.66. The vulnerability was addressed in Apache HTTP Server version 2.4.67.

Apache HTTP Server remains one of the most widely deployed web servers globally and is commonly used across Linux distributions, cloud-hosted applications, enterprise reverse proxies, containerized workloads, and internet-facing environments. Deployments with HTTP/2 enabled are particularly exposed. Other services or products embedding vulnerable Apache HTTP Server versions may also be impacted.

Risk Impact

At the time of writing, public proof-of-concept technical details discussing exploitation conditions are already available, although no confirmed in-the-wild exploitation has been publicly reported. Regardless, the severity and low complexity of exploitation make this vulnerability high risk, especially for internet-facing deployments.

Successful exploitation could allow attackers to crash vulnerable web servers, execute arbitrary code, bypass availability protections, and potentially pivot deeper into internal infrastructure, leading to service disruption, sensitive data exposure, or full server compromise.

Mitigation Recommendations

Users should immediately upgrade to Apache HTTP Server 2.4.67, which addresses the underlying memory handling flaw. Organizations unable to patch immediately should consider temporarily disabling HTTP/2 support until upgrades can be completed.

How can Orca help?

Orca enables customers to quickly identify assets running vulnerable Apache HTTP Server versions, understand their exposure in context, including internet accessibility, runtime reachability, and asset criticality, and prioritize remediation based on real risk rather than CVSS alone. Orca’s platform highlights affected assets directly in the alert view, helping security teams focus on the most critical remediation paths first.
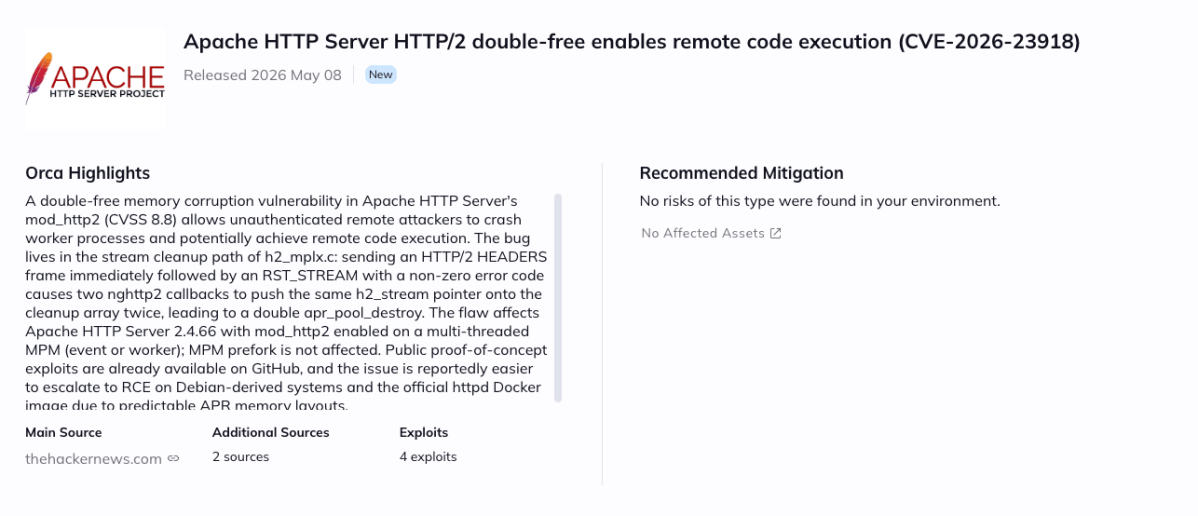
Orca Security platform alert for a critical Apache HTTP Server HTTP/2 double-free (CVE-2026-23918) enabling unauthenticated remote code execution.
From the News Item in the Orca Platform