








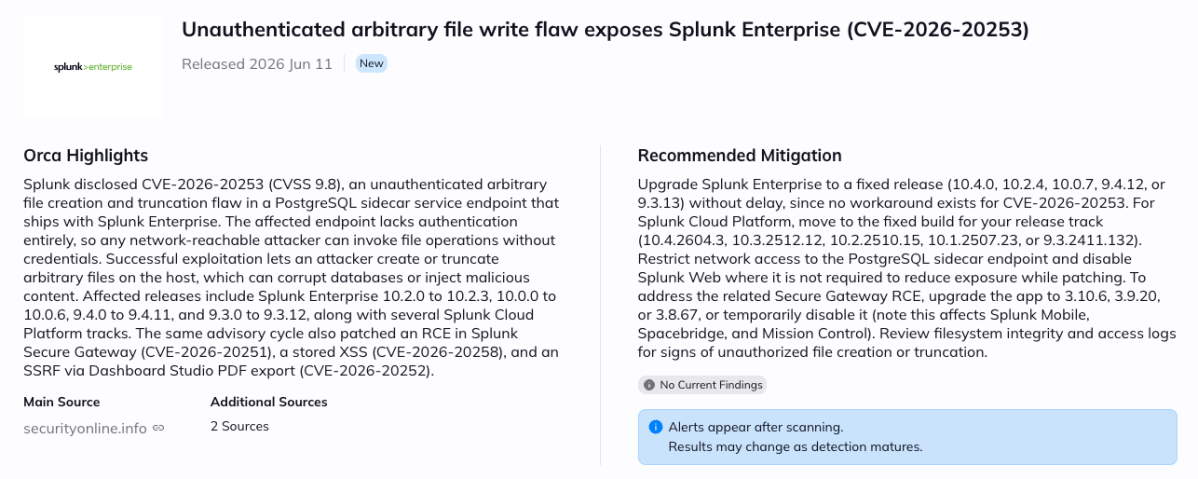
A critical vulnerability (CVE-2026-20253, CVSS 9.8) was disclosed alongside three additional high-severity flaws affecting Splunk Enterprise, Splunk Cloud Platform, and the Splunk Secure Gateway app, allowing attackers to perform unauthenticated arbitrary file creation/truncation, remote code execution, stored cross-site scripting, and server-side request forgery. Due to the potential for full infrastructure compromise in enterprise and cloud environments, immediate patching is required.
The most severe issue, CVE-2026-20253, originates from a PostgreSQL sidecar service endpoint in Splunk Enterprise that completely lacks authentication controls (CWE-306). Because the endpoint performs no credential verification, any network-reachable attacker can invoke file operations on the underlying system without authentication. By sending crafted requests to this exposed endpoint, attackers can create or truncate arbitrary files, potentially disabling critical databases, injecting malicious content, or disrupting service availability. No authentication or user interaction is required to exploit this issue.
The second critical flaw, CVE-2026-20251 (CVSS 8.8), resides in the Splunk Secure Gateway app. The vulnerability stems from unsafe deserialization of App Key Value Store (KV Store) data through the jsonpickle Python library, which reconstructs arbitrary Python objects from crafted JSON without proper validation. An attacker with only low-privilege access (no admin or power role required) can achieve full remote code execution by supplying specially crafted serialized data.
Two additional high-severity vulnerabilities round out the advisory batch. CVE-2026-20258 (CVSS 7.1) is a stored cross-site scripting flaw in classic dashboard HTML panels that enables persistent script execution in the browsers of users viewing affected dashboards. CVE-2026-20252 (CVSS 7.6) is a server-side request forgery vulnerability in Dashboard Studio’s PDF export feature that bypasses trusted-domain validation through prefix matching and automatic redirect following, allowing low-privileged users to reach internal network destinations.
The following versions are affected:
These components are used extensively across enterprise security operations centers, IT infrastructure monitoring, and cloud observability platforms. Any organization running Splunk Enterprise with network-accessible PostgreSQL sidecar endpoints or the Secure Gateway app enabled is at elevated risk, particularly in internet-facing deployments or environments where network segmentation does not isolate Splunk management interfaces.
At the time of writing, no public proof-of-concept exploits have been identified, and there are no reports of active exploitation in the wild. Regardless, the severity and ease of exploitation, especially the unauthenticated nature of CVE-2026-20253, make these vulnerabilities high risk for any internet-facing or insufficiently segmented Splunk deployment.
Successful exploitation could allow attackers to create or destroy critical files on the Splunk server, execute arbitrary code within the Splunk environment, and pivot to internal network resources via SSRF, leading to service disruption, data exposure, or full infrastructure compromise.
Upgrade to the following patched versions immediately:
Where immediate patching is not possible:
Orca enables customers to quickly identify assets running vulnerable versions of Splunk Enterprise, understand their exposure in context, including internet accessibility, runtime reachability, and asset criticality, and prioritize remediation based on real risk rather than CVSS alone. Orca’s agentless scanning detects Splunk Enterprise installations and their versions across AWS, Azure, and GCP environments without requiring endpoint agents. Orca’s platform highlights affected assets directly in the alert view, helping security teams focus on the most critical remediation paths first.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。