
惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

宝玉的分享
宝玉的分享
J
Java Code Geeks
S
SegmentFault 最新的问题
L
LangChain Blog
M
MIT News - Artificial intelligence
Stack Overflow Blog
Stack Overflow Blog
IT之家
IT之家
量子位
奇客Solidot–传递最新科技情报
奇客Solidot–传递最新科技情报
雷峰网
雷峰网
OSCHINA 社区最新新闻
OSCHINA 社区最新新闻
The Cloudflare Blog
MongoDB | Blog
MongoDB | Blog
Microsoft Security Blog
腾讯CDC
H
Help Net Security
阮一峰的网络日志
阮一峰的网络日志
Jina AI
Jina AI
N
Netflix TechBlog - Medium
A
About on SuperTechFans
博客园 - 叶小钗
美团技术团队
人人都是产品经理
人人都是产品经理
D
DataBreaches.Net

Blog | Orca Security

Langflow RCE Actively Exploited to Deploy Cryptominers on AI Infrastructure Orca MCP: When Text Stops Scaling Kubernetes Compliance Tools: Automating CIS Benchmarks Risk-Based Vulnerability Management for the Cloud: A 2026 Guide Private Cloud Security: Top Risks and Best Practices (2026) What Is Generative AI in Cybersecurity? Best Vulnerability Management Tools and Software in 2026 2026 State of Application Security Report Recap: What the Data Says and What Security Teams Should Do About It AI Security for Sensitive Data: Best Practices and Guidelines Best AI Code Security Solutions 2026: How to Secure AI-Generated Code From Platform to Program: How to Ensure Your Cloud Security Solution Delivers Best AI Cybersecurity Providers 2026: A Buyer's Guide to AI-Powered Security Platforms Join Orca Security at Black Hat USA 2026 CNAPP Tools That Reduce Security Tool Sprawl: CNAPP vs. Dedicated Solutions What Is Container Runtime Security? A Practical Guide 2026 What Is Application Security Testing? Tools and Types What Is Managed Cloud Security? A Practical Guide What Is SaaS Security Posture Management? SSPM Guide Top 10 Cloud Security Standards for Compliance What is the MIT License? Compliance and Comparisons AI Agents vs. Agentless Security vs. Agent-based Security 144 Mastra npm Packages Compromised via Supply Chain Attack The Complete Guide to LLM Security: Risks, Best Practices, and Solutions Cloud Security LIVE 2026: Top 10 Takeaways Practitioners Can Use Now Cloud Security LIVE 2026: Top 10 Takeaways CISOs Can Use Now (and What to Do Next) How Orca Traced an nginx Flaw to 1.45 Million Tengine Servers All Running Vulnerable Code What to Look for in Container Security Tools Cloud Application Security Best Practices for DevSecOps Cloud Security Tools: 10 Types Explained for Teams What Is NIST CSF? Framework 2.0 Explained
Streamline Compliance Reporting with Orca and Drata’s Int...
2026-04-09 · via Blog | Orca Security

We are excited to announce Orca now integrates with Drata, an Agentic Trust Management Platform, to offer comprehensive vulnerability assessments to identify compliance risks across your digital estate. Orca’s integration empowers Drata with Vulnerability Management findings from your Orca Security platform. The combination of Orca’s deep technical telemetry with Drata’s governance framework ensures cloud assets are discovered, monitored, and satisfy compliance requirements.

In today’s cloud-centric reality, reactive remediation is not enough for security teams to address the two-front war of unknown and dangerously known exploits that leave your organization vulnerable to threat actors. Since its creation in 2021, CISA’s catalog of Known Exploited Vulnerabilities (KEV) has jumped from 287 to over 1,500 in less than 5 years. Security teams simply do not have the ability to be everywhere all at once and need the right solution to aid the discovery, enumeration, and reporting of compliance gaps. 

How the Drata Integration Automates Your Vulnerability Surface Monitoring

Closing these gaps requires an integrated system where Compliance Management and Vulnerability Management act as the strategy and the engine of your defense. This partnership ensures that the risk-reduction workflow is established and governed by a plan that aligns security actions with organizational objectives. This plan can then be operationalized through the deployment of Vulnerability Scanning–an automated technique used to proactively identify cloud-native assets, ephemeral infrastructure, and associated vulnerabilities. 
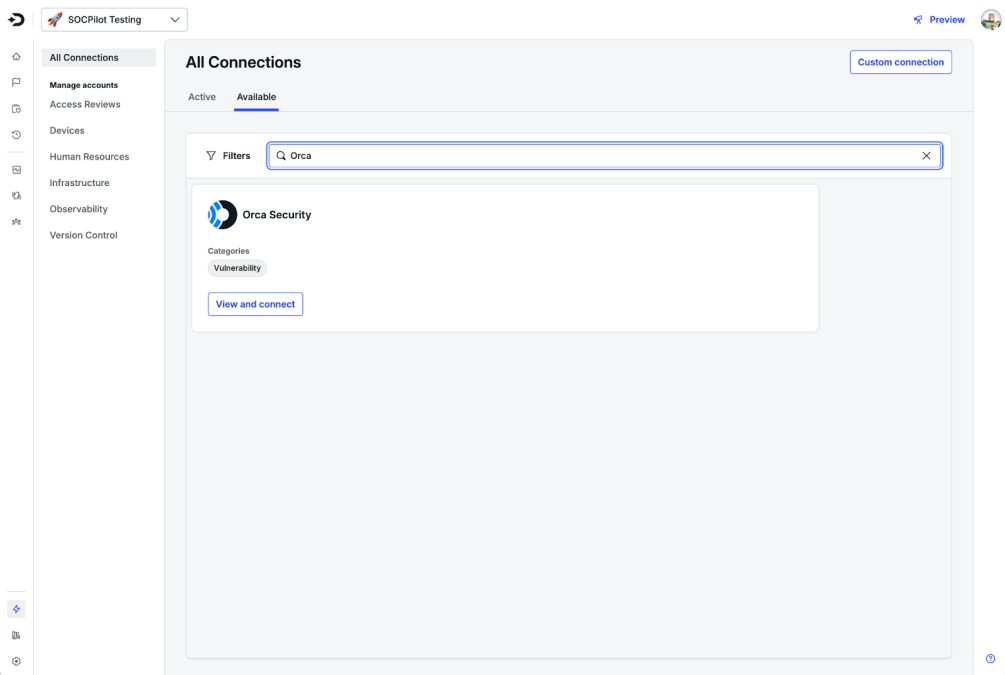
Screenshot of the SOCPilot platform's 'Available Connections' page showing an integration card for Orca Security under the 'Vulnerability' category.
Orca now integrates to ingest vulnerability scanning findings directly into Drata

The integration of Orca’s Vulnerability Management and scanning capabilities with Drata’s Compliance Management automation transforms mandatory regulatory compliance into a repeatable, audit-ready cycle of risk reduction. By connecting with Orca, you easily and automatically satisfy automated vulnerability monitoring test requirements within Drata. To get started, search for Orca Security in Drata under Available Connections.
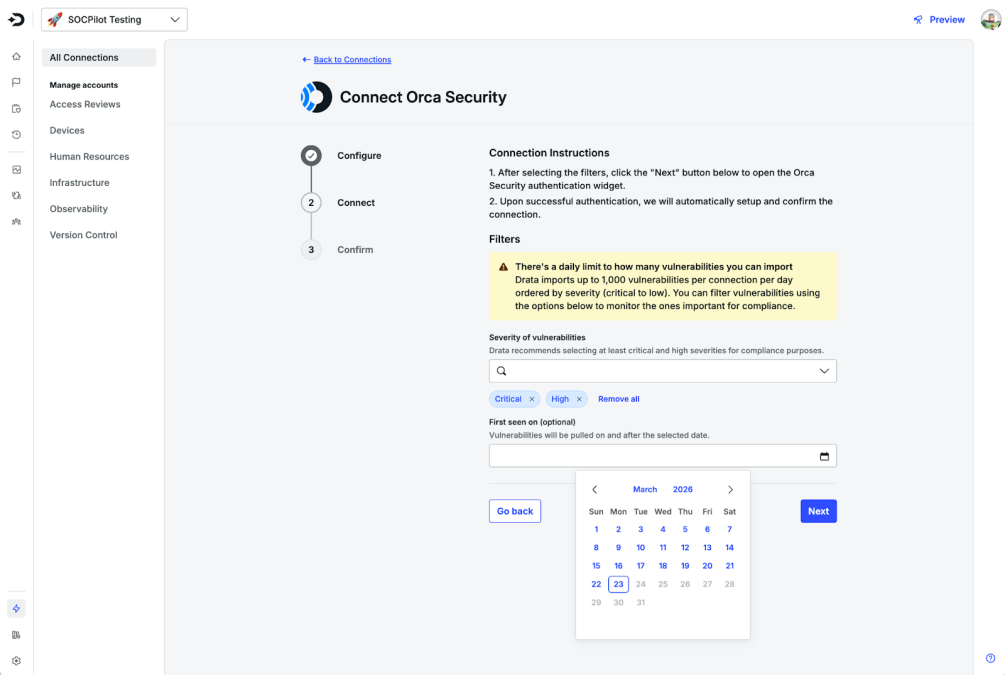
Mapping Findings to Evidence via the Orca and Drata Integration

Configuration screen for the Orca Security integration in Drata, featuring vulnerability severity filters and an active date selection menu.
Administrators set the minimum severity level for vulnerabilities to be included and to specify the starting date for data retrieval

Once you have connected and configured your vulnerability severity scope, Drata automatically maps evidence from Orca’s vulnerability data to the Drata Control Framework (DCF). The DCF is Drata’s centralized, proprietary set of controls to address scanning requirements across common industry regulations, standards, and frameworks (such as SOC 2, ISO 27001, and PCI DSS).
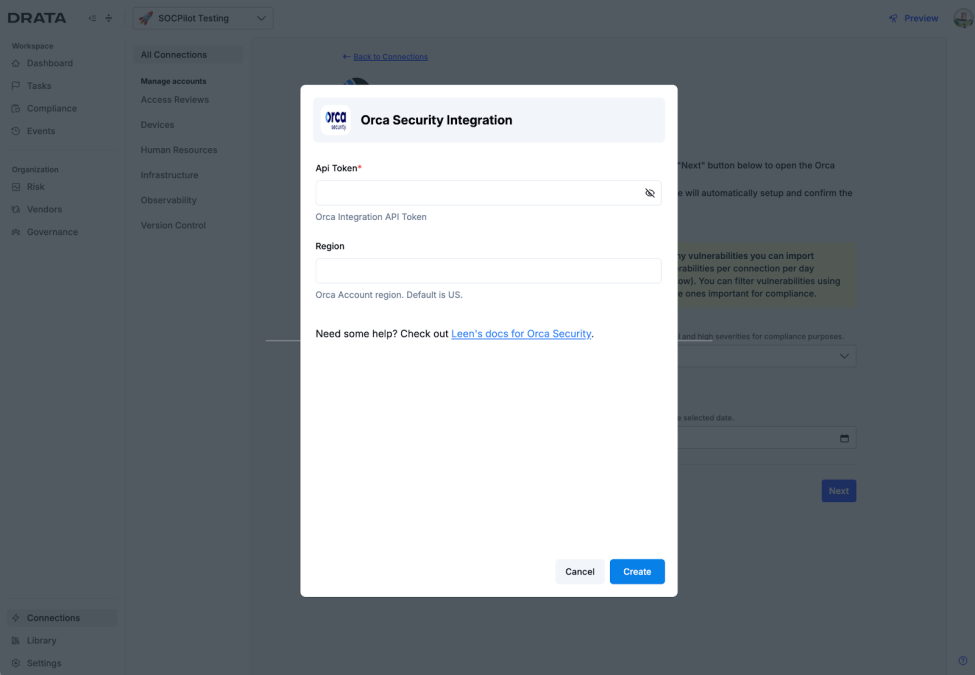
Screenshot of the Drata platform's Orca Security integration modal, requiring an API Token and Region to establish the connection.

Drata periodically pulls vulnerability data from Orca to verify that scans are being performed according to your internal policies. Thus eliminating the need for screenshots of scan reports by streamlining compliance reporting with automated evidence collection.
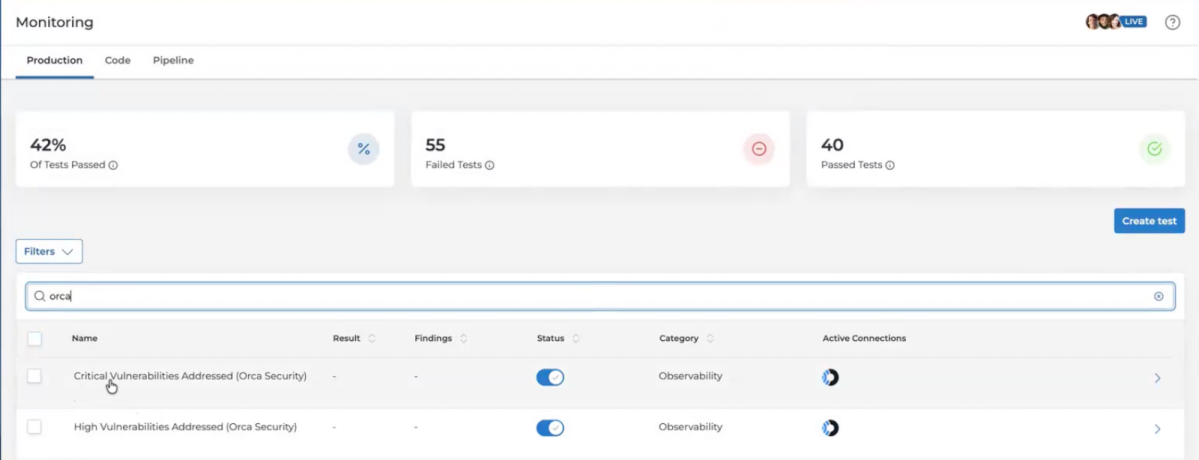
Drata monitoring dashboard filtered for Orca Security tests, displaying a 42% passage rate across production infrastructure.
Automated vulnerability test statuses are set to Active after connecting to Orca
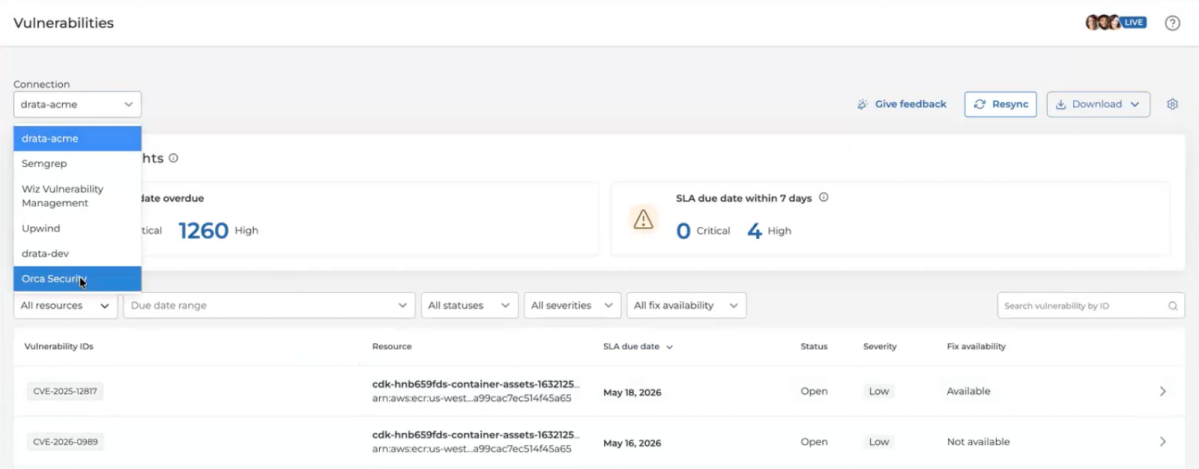
Drata Vulnerabilities dashboard with the Orca Security integration selected, showing a list of active CVEs and their respective SLA due dates.
Centralize vulnerability findings by connecting various scanning tools for a unified view

By integrating Orca with Drata, security findings automatically map to your organization’s compliance strategy, making it easier than ever to identify compliance gaps, gather the necessary evidence to take remediation action, and ensure full audit readiness.

Next Steps: Scale Your Compliance Program with Orca + DrataLearn more 

Interested in discovering the benefits of the Orca Platform and how it can be integrated with tools like Drata? Schedule a personalized 1:1 demo, and we’ll show how you can use Orca to identify, prioritize, and remediate risks in your cloud environment. If you already use both Orca and Drata, follow the steps in the documentation to set up the integration.

Command Your Cloud With Orca

Orca offers a unified and comprehensive cloud security platform that identifies, prioritizes, and remediates security risks and compliance issues across AWS, Azure, Google Cloud, Oracle Cloud, Alibaba Cloud, Tencent Cloud and Kubernetes. The Orca Cloud Security Platform leverages Orca’s patented SideScanning™ technology to provide complete coverage and comprehensive risk detection.