惯性聚合 高效追踪和阅读你感兴趣的博客、新闻、科技资讯
阅读原文 在惯性聚合中打开

推荐订阅源

Apple Machine Learning Research
Google DeepMind News
小众软件
小众软件
GbyAI
GbyAI
酷 壳 – CoolShell
酷 壳 – CoolShell
F
Fortinet All Blogs
博客园 - 三生石上(FineUI控件)
B
Blog
量子位
B
Blog RSS Feed
Vercel News
Vercel News
Blog — PlanetScale
Blog — PlanetScale
Last Week in AI
Last Week in AI
博客园 - 叶小钗
MongoDB | Blog
MongoDB | Blog
Cyber Security Advisories - MS-ISAC
钛媒体:引领未来商业与生活新知
钛媒体:引领未来商业与生活新知
爱范儿
爱范儿
Jina AI
Jina AI
C
Check Point Blog
freeCodeCamp Programming Tutorials: Python, JavaScript, Git & More
IT之家
IT之家
H
Hackread – Cybersecurity News, Data Breaches, AI and More
云风的 BLOG
云风的 BLOG

Heimdal Security Blog

Slow is a design principle, not a delay AI adoption that pays off is built around keeping humans in the driver's seat Phishing in 2026. Latest statistics and analysis Shift Browser is signed adware that fingerprints your endpoint before it drops payload 6 ThreatLocker alternatives that should make your shortlist 50+ insider threat statistics for 2026 The Planting Seeds philosophy. Selling into schools takes years, not quarters What the DfE's cyber security update means for multi-academy trusts 9 Proofpoint alternatives. Pros & cons of the leading options The risk awareness radar. A superpower every MSP needs to train Heimdal data reveals MediaArena adware completes persistence before antivirus quarantine finishes How Heimdal grew from a bold idea into a global cybersecurity platform Tools Change. Teach People How to Keep Up The 4 best managed EDR service suppliers (and how to choose) How to choose the best SOC platform in 2026 (and our top 4) Top 6 Managed Detection and Response Providers Cyber-Aware Customers Are Raising the Bar for MSPs and Other Vendors Cyber-Aware Customers Are Raising the Bar for MSPs and Other Vendors How to scale your patches without scaling your team (the patch wave) AI didn't break patching. It showed us patching was already broken. Heimdal Launches MSP Onboarding Wizard to Help Partners Onboard Microsoft CSP Customers in 2 Minutes How Dynamic Defense shuts an attacker out without shutting down the business Static security has run out of road. The case for Dynamic Defense Breaking the MSP Echo Chamber: The Power of Community How attackers built a RAT on a Windows machine using its own .NET compiler Attacker enables RDP, creates admin, erases evidence in ten seconds Heimdal Survey: Executives Four Times More Confident About AI Risk Than the Teams Managing It Your Next Insider Threat May Be an AI Coworker The OSI Model and Its Two Missing Layers Heimdal® Marks Six Years of Consecutive ISAE 3000 SOC 2 Type II Certification
MediaArena malvertising: why a quarantine isn't the end o...
Alexandru Gurgu · 2026-07-17 · via Heimdal Security Blog

If Microsoft Defender quarantines BrowserModifier:Win32/MediaArena on one of your endpoints, the alert reads like a win.

Our SOC data says treat it as a live persistence incident instead.

In the case we timed, the payload finished writing its persistence 21 seconds into execution. Quarantine didn’t complete until 29 seconds. By the time the alert fired, the persistence was already on disk.

We’ve seen this same adware cluster across more than 20 client environments in recent days. It’s the malvertising campaign that hides behind free “AI tool” lures, and it’s already been documented.

Compass Apex Security wrote it up in April, and the indicators have sat in public sandboxes since March. We’re adding what our own SOC can see. How fast it establishes persistence, and how widely.
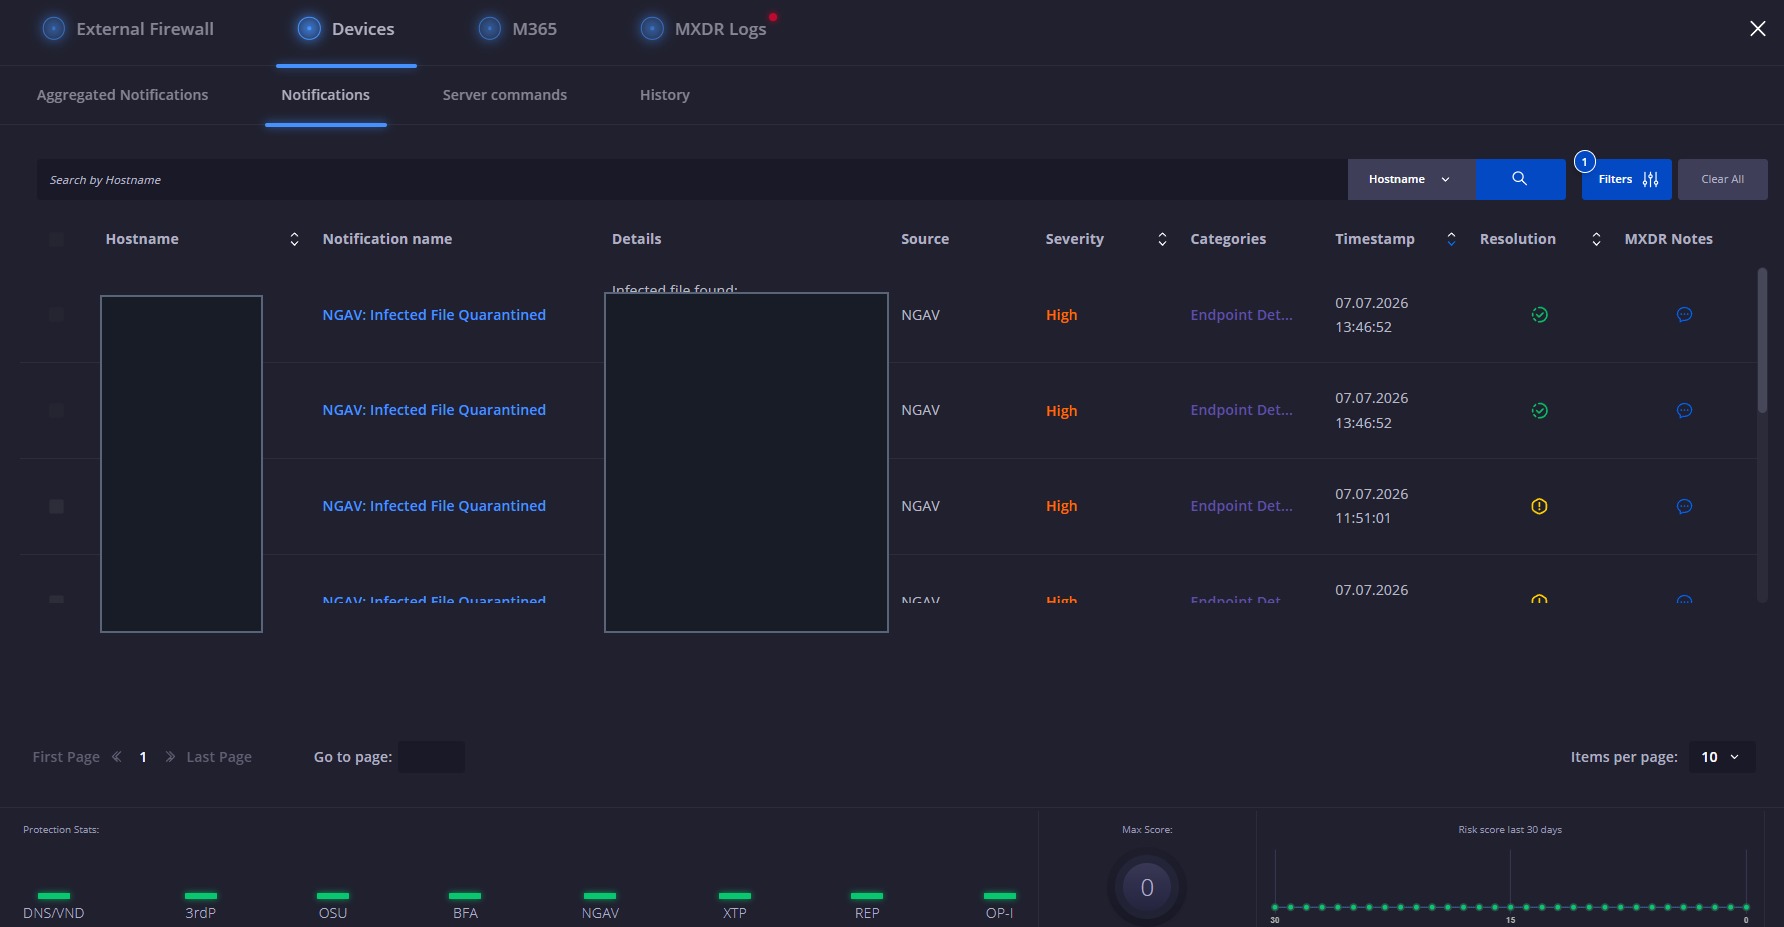
 A sample of affected hosts. The same detection landed across more than 20 client environments in days. Hostnames and paths redacted.

A sample of affected hosts. The same detection landed across more than 20 client environments in days. Hostnames and paths redacted.

Microsoft classifies MediaArena as a browser-modifier potentially unwanted application and has tracked it in its threat encyclopedia since 2023. It reconfigures browser settings, hijacks search, and harvests queries to sell on. It’s a nuisance, not a nation-state loader.

That’s the point.

Even a low-severity detection can leave persistence behind, so a closed alert and a clean endpoint aren’t the same thing.

The delivery is a fake free-app lure, currently themed as recipe and meal-planning tools, served through paid search ads.

The brand names rotate, and the domains rotate with them, so any single indicator has a short shelf life. That’s why detection built on brand strings ages out fast, and why the behaviour and the persistence artefacts are the signals worth hunting on.
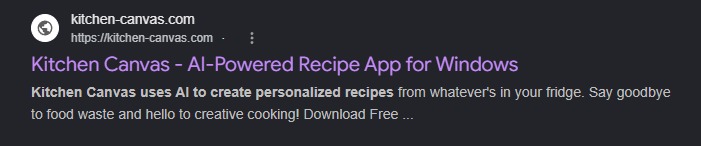
Paid search result for kitchen-canvas.com, a fake free AI recipe app for Windows used as a malvertising lure.

The lure surfaces through paid search.
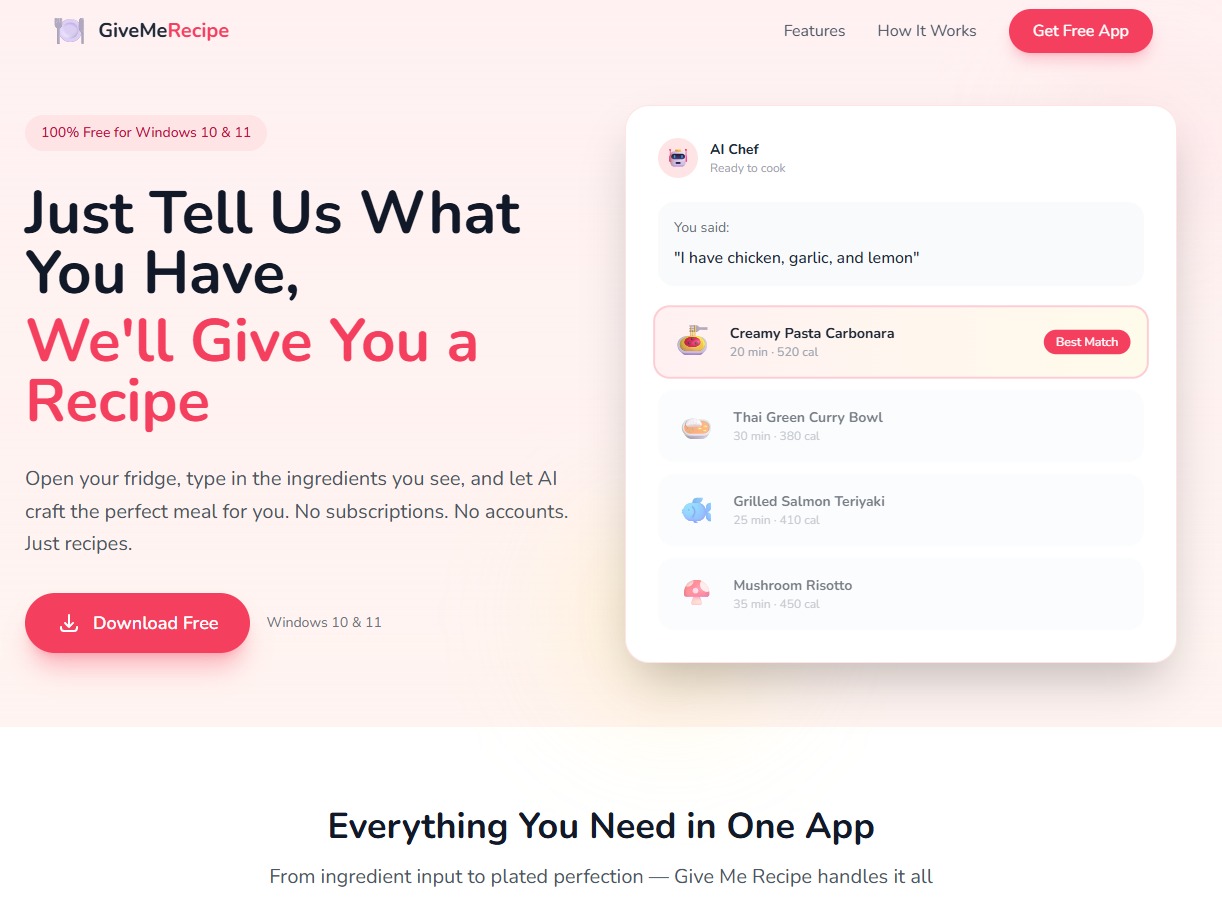
GiveMeRecipe landing page, a fake free AI recipe app for Windows delivering MediaArena adware.

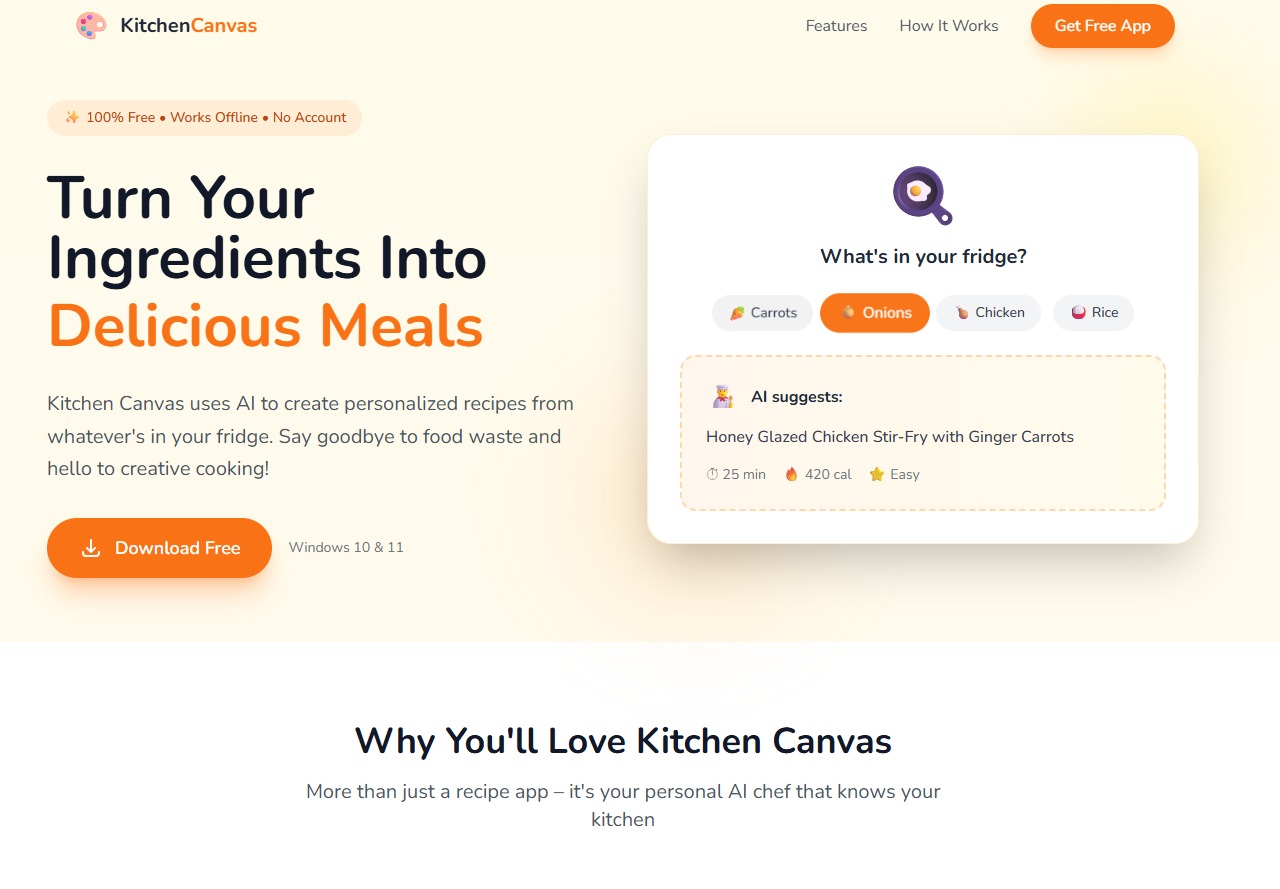
KitchenCanvas landing page, a fake free AI recipe app fronting the same MediaArena malvertising campaign.

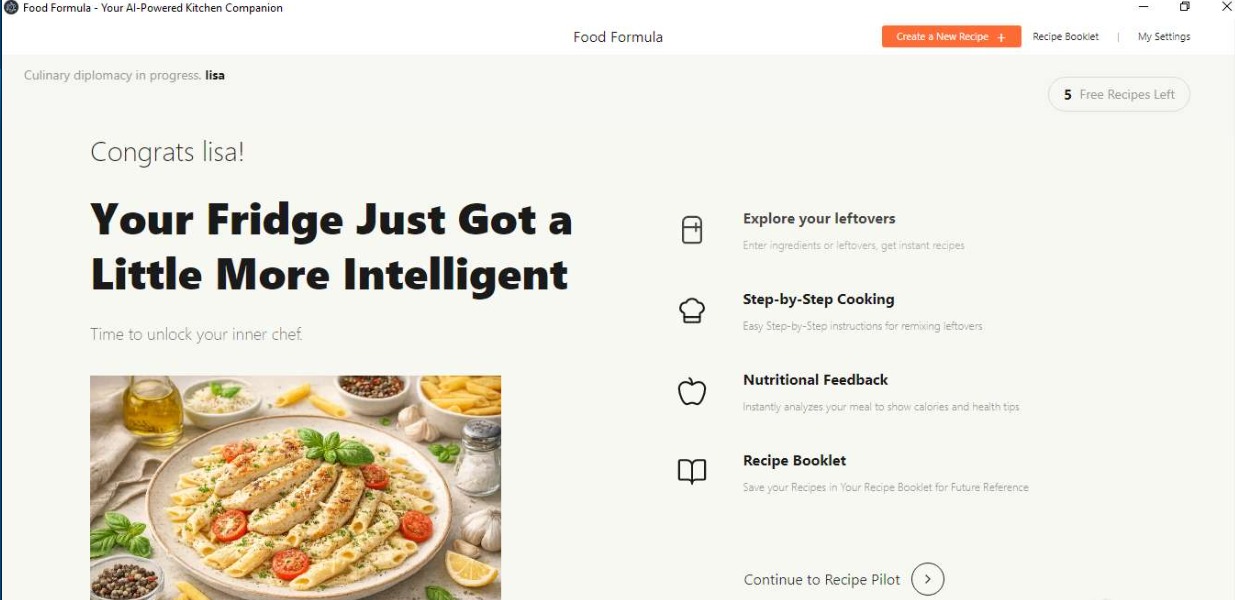
FoodFormula app interface, another rotating lure brand distributing the MediaArena browser hijacker.

Three of the rotating lure brands, GiveMeRecipe, KitchenCanvas, and FoodFormula, all fronting the same math.dll toolkit.

What actually happens on the endpoint

The installer needs no admin rights. In our confirmed case it wrote to AppData, dropped a Start Menu shortcut, added an HKCU Uninstall key to pass as a legitimate app, and left a Startup folder shortcut for boot persistence.

All of it landed before quarantine completed. Signature detection took roughly 78 days to catch up. That’s a long window for a browser hijacker to sit and run.
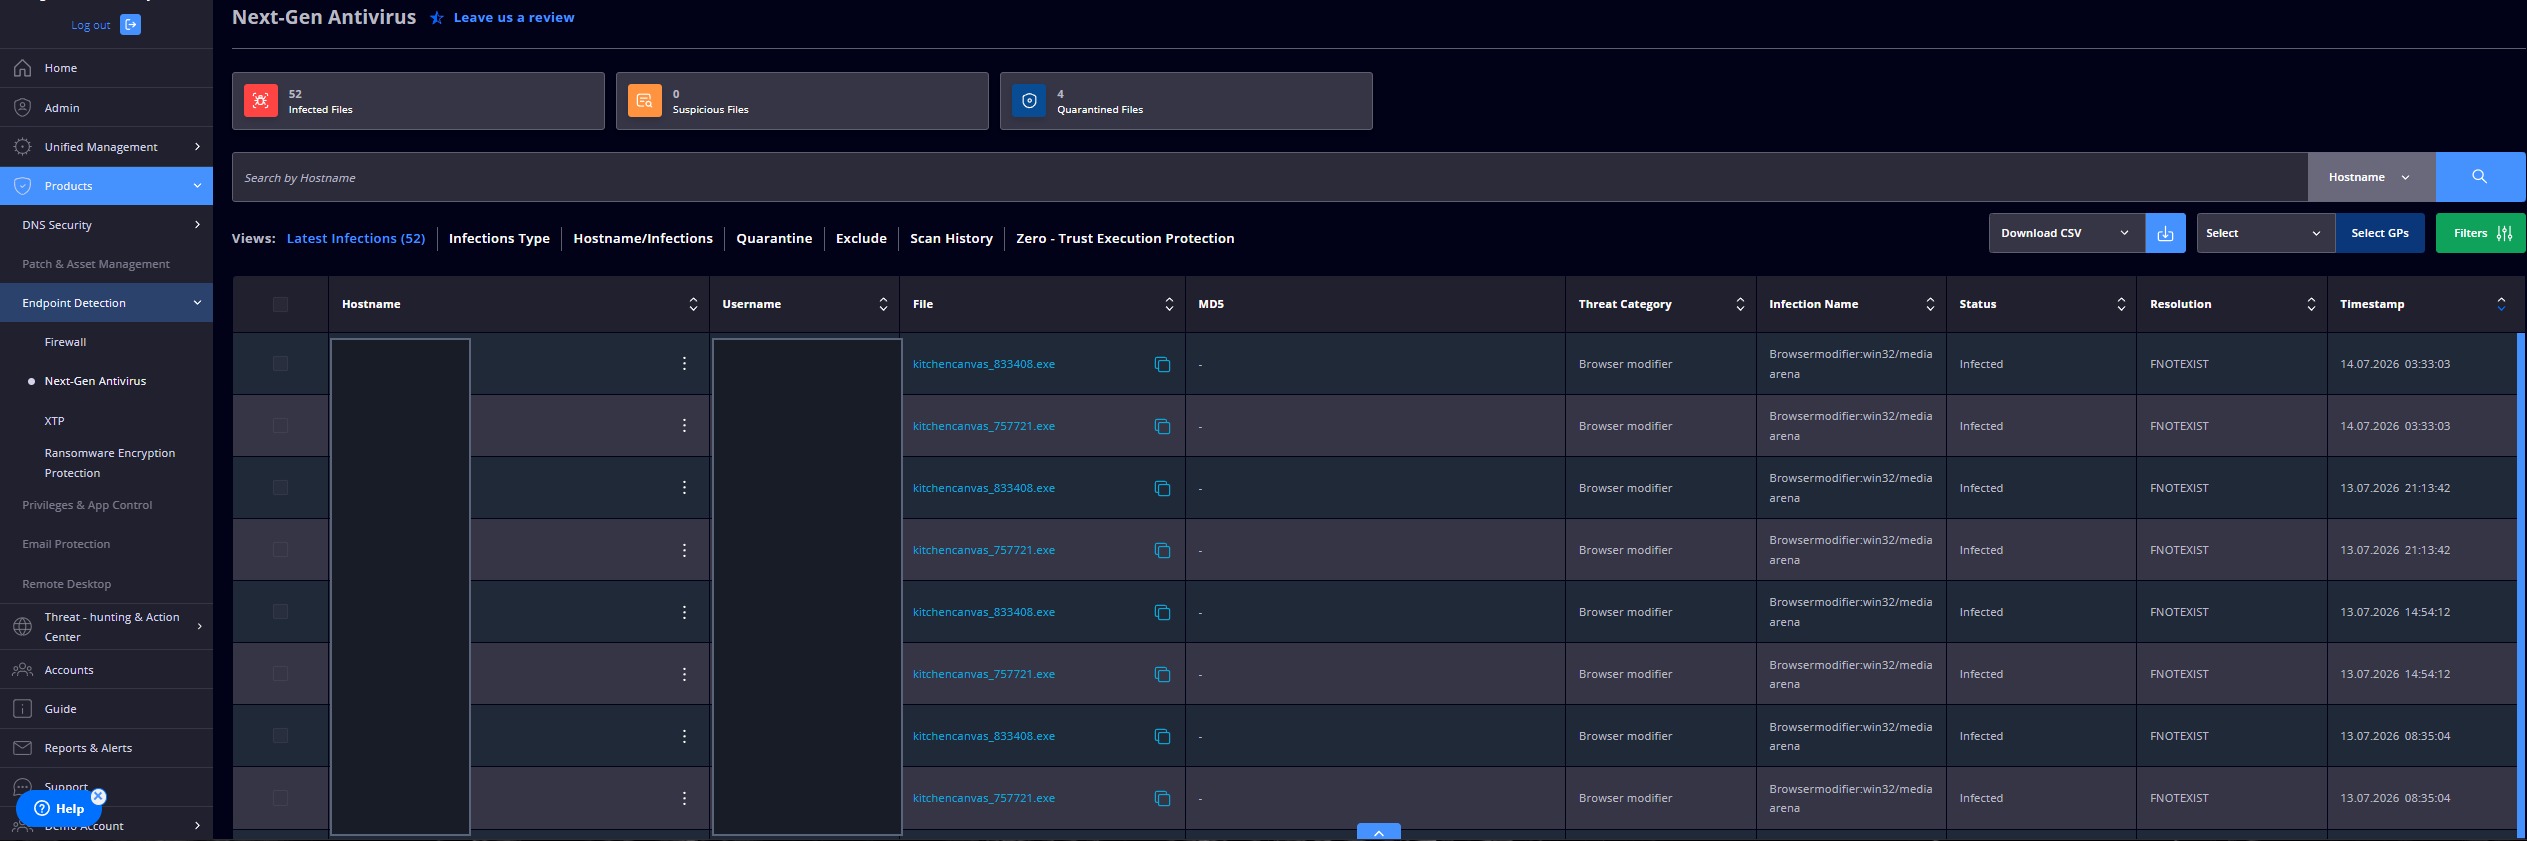
Heimdal Next-Gen Antivirus flagging fake recipe-app installers as BrowserModifier:Win32/MediaArena on an infected host, details redacted.

Our console. The branded installers flagged as BrowserModifier:Win32/MediaArena on an affected host. Hostname and username redacted.

The alert told us the file was caught. It didn’t tell us nothing had run first, and on these detections something always had. That’s why I treat a quarantine on this family as the start of the investigation, not the end of it.

What to hunt for after a MediaArena hit

Don’t close the alert on quarantine alone. Check the affected host for:

  • A Startup folder shortcut tied to the app name.
  • An HKCU Uninstall registry key mimicking a legitimate install.

Note the loader, math.dll, is injected in memory rather than dropped to disk, so hunt the persistence artefacts above rather than the file itself.

If either artefact is present, treat the host as still compromised and remediate the persistence directly.

Indicators

Credit to Compass Apex Security and public sandbox reporting for the campaign work. Indicators confirmed live at the time of writing. The infrastructure rotates, so revalidate before acting.

  • Lure domains: kitchen-canvas.com, givemerecipe.com (both still flagged malicious across public sandboxes)
  • Payload hosting: d3pth7js01bstg.cloudfront.net (AWS CloudFront)
  • Loader: math.dll (in-memory)
  • Detection: BrowserModifier:Win32/MediaArena
  • Hashes: GiveMeRecipe.exe SHA256 3c1dbc3f…eccc, MD5 273FD232…7CEC; FoodFormula.exe SHA256 b179bec7…fb53; KitchenCanvas.exe MD5 d749e0f8…4121 [KitchenCanvas SHA256 pending, see production note]