


Fintech security failures rarely start with highly sophisticated attacks. They usually begin with access that was too broad or integrations that were trusted without sufficient validation. These weaknesses intersect with real-time payments, third-party dependencies, fraud exposure, and regulatory scrutiny.
Capital One is a clear example. A cloud misconfiguration exposed credentials, but the real damage came from overly permissive IAM roles that allowed large-scale access to sensitive S3 data. The initial vulnerability created entry, but the authorization model determined the scale of the breach.
Robinhood’s 2021 incident followed a similar pattern. A support employee was socially engineered and the attacker gained access to internal systems. That access exposed data for millions of customers. Now add AI agents and agentic commerce into the mix, and fintech cybersecurity becomes even more complicated:
Fintech systems combine too many risk factors in a single stack. In retail banks or neobanks, a vulnerability does not just expose records. It can affect balances, payouts, or transaction limits in production. In platforms like Stripe or Plaid, one integration or leaked API key can impact thousands of downstream merchants because the architecture is multi-tenant by design. In BaaS or core banking infrastructure, weaknesses propagate to every fintech built on that ledger.
I was surprised to find out that nearly 46% of financial institutions reported at least one data breach in the last 24 months, and 65% experienced ransomware attacks in 2024 alone. And in 2023, finance accounted for 27% of all breaches handled globally, making it the most breached industry 😅.
The average cost of a financial sector breach is $5.90M. So fintech cybersecurity operates in an environment where breaches are frequent, and the consequences are expensive.
In my guide, I will outline 9 security risks fintech teams repeatedly face and the principles that reduce structural exposure across retail banking, B2B platforms, embedded finance, and payments infrastructure. So, what are the most common cybersecurity risks in fintech?
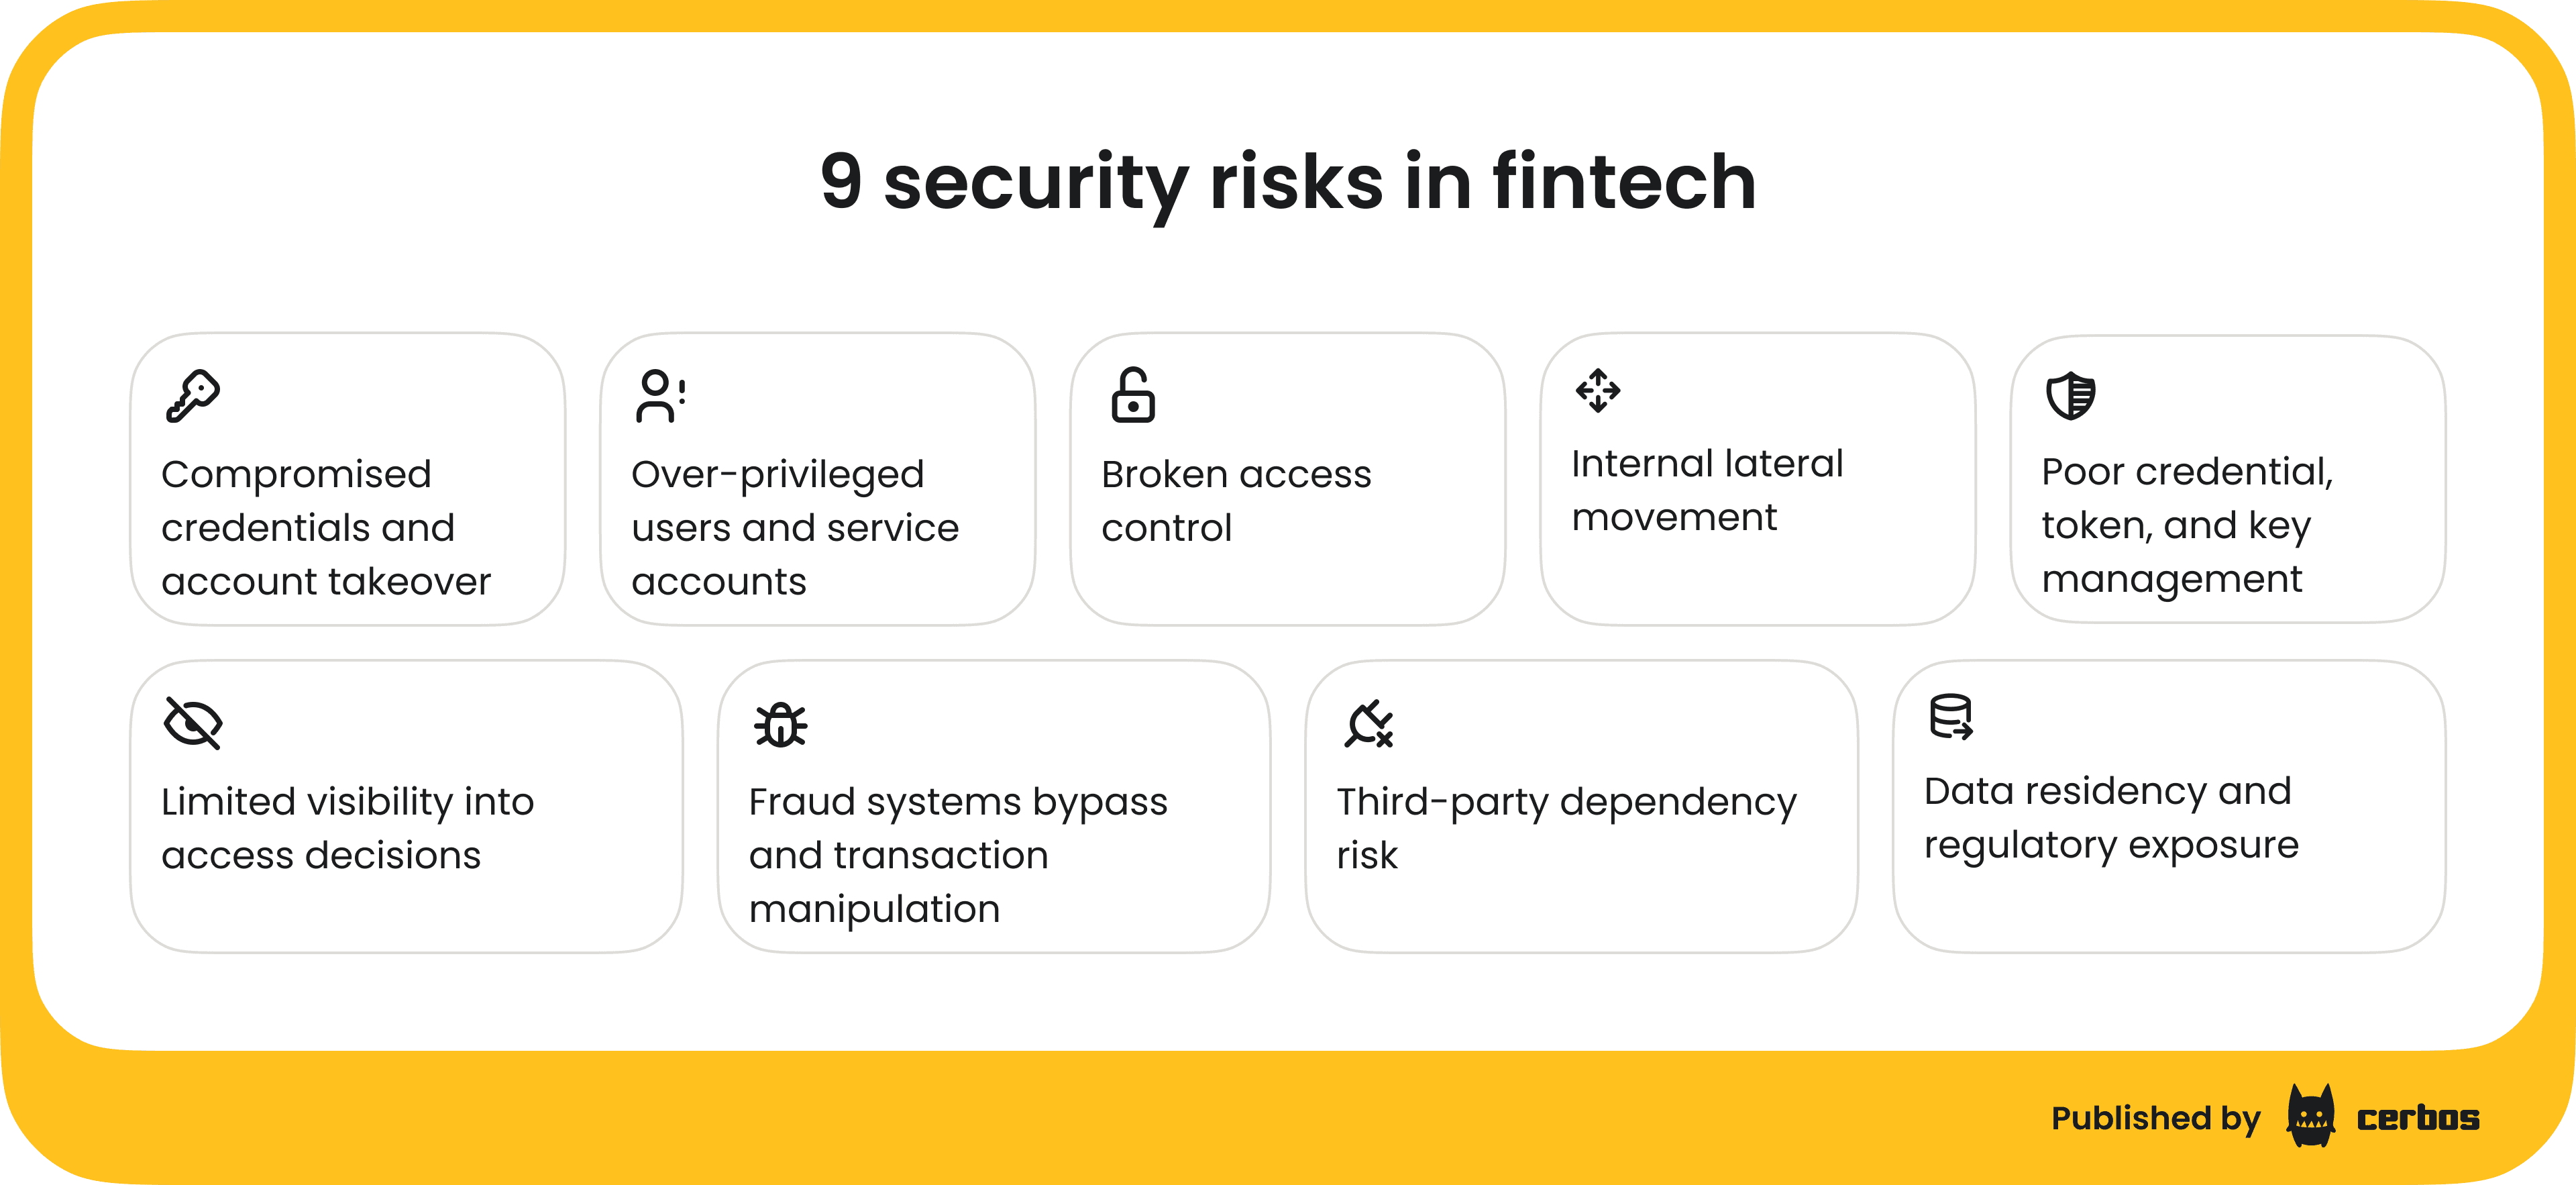
Social engineering remains one of the most effective cybersecurity threats in fintech, particularly in crypto platforms where transactions are irreversible. Between 2022 and 2024, more than $7 billion was stolen from crypto platforms, with phishing and credential theft playing a significant role in account compromise.
Coinbase has publicly disclosed coordinated social engineering campaigns targeting employees with the goal of obtaining valid credentials and accessing internal tools. The attackers did not rely on exploiting cryptographic weaknesses. They attempted to authenticate through legitimate flows by convincing employees to approve access.
In practice, compromised credentials are often enough. The financial impact depends on what that identity is allowed to access, modify, or execute once inside.
Permissions tend to expand over time. Support roles gain additional access during incidents. Service accounts are granted broad read rights to avoid breaking workflows. When access is not regularly reviewed and constrained, compromise of one identity can expose far more data than intended.
The introduction of AI agents increases that exposure. An AI system connected to internal APIs, data stores, or payment functions operates with the permissions it is given. If its identity is broadly scoped, misuse can result in automated data retrieval, bulk queries, or repeated execution of financial operations at scale.
OWASP continues to rank Broken Access Control as the most common application security risk. In fintech systems, this means an authenticated identity can access customer data or perform payment actions beyond its intended scope because fine-grained authorization is not enforced consistently.
Authorization must be enforced consistently across applications, APIs, services, and AI systems, and it must apply to every identity type. This is especially critical for regulated environments. If you want to dive deeper into authorization for fintech, here are some useful resources:
After initial access, attackers often move between internal services rather than targeting external interfaces. Financial platforms are composed of services such as account management, payments, ledger, risk scoring, and reporting, connected through authenticated service-to-service calls.
If downstream services validate workload identity at the transport or token layer but do not enforce their own resource-level authorization checks, a compromised workload can access additional internal APIs within its assigned scope. Weak segmentation and broad service permissions allow compromise to spread across systems that were never intended to be directly exposed.
For example, if a payments service accepts a ledger service token without verifying the specific account or transaction scope, a compromised internal workload can query or modify financial data outside its intended boundary. Transport-level authentication does not replace resource-level authorization!
When tokens are long-lived, broadly scoped, or insufficiently rotated, exposure persists. The 2024 Snowflake-related breach demonstrated how attackers used valid credentials to access cloud data environments across multiple companies, including financial services firms. No cryptographic bypass was required. The credentials worked because they were still valid 😅.
If signing keys or long-lived tokens are exposed, systems may treat forged or reused tokens as valid. Regular rotation and strict scope limits reduce that risk. Key lifecycle management directly affects how long an attacker can operate undetected.
Audit logging is not just an engineering concern. It is a regulatory expectation. When a suspicious transfer, limit change, or bulk data export occurs, the organization must explain who performed the action and why the system allowed it.
If you cannot reconstruct the authorization decision at the time of the action, incident response and regulatory reporting become significantly harder.
Fintech platforms process high transaction volumes in real time. Fraud attempts scale with that volume. Card testing, payout loops, bot-driven account creation, and API abuse are common patterns.
When fraud detection, rate limiting, and transaction monitoring are weak or disconnected from core controls, attackers can execute multiple financial actions before intervention. In fintech security, detection speed directly affects financial exposure.
This risk is not new but often forgotten. Fintech platforms depend on payment processors, KYC providers, credit bureaus, cloud vendors, and analytics tools. Each integration introduces external credentials, webhooks, and API trust relationships.
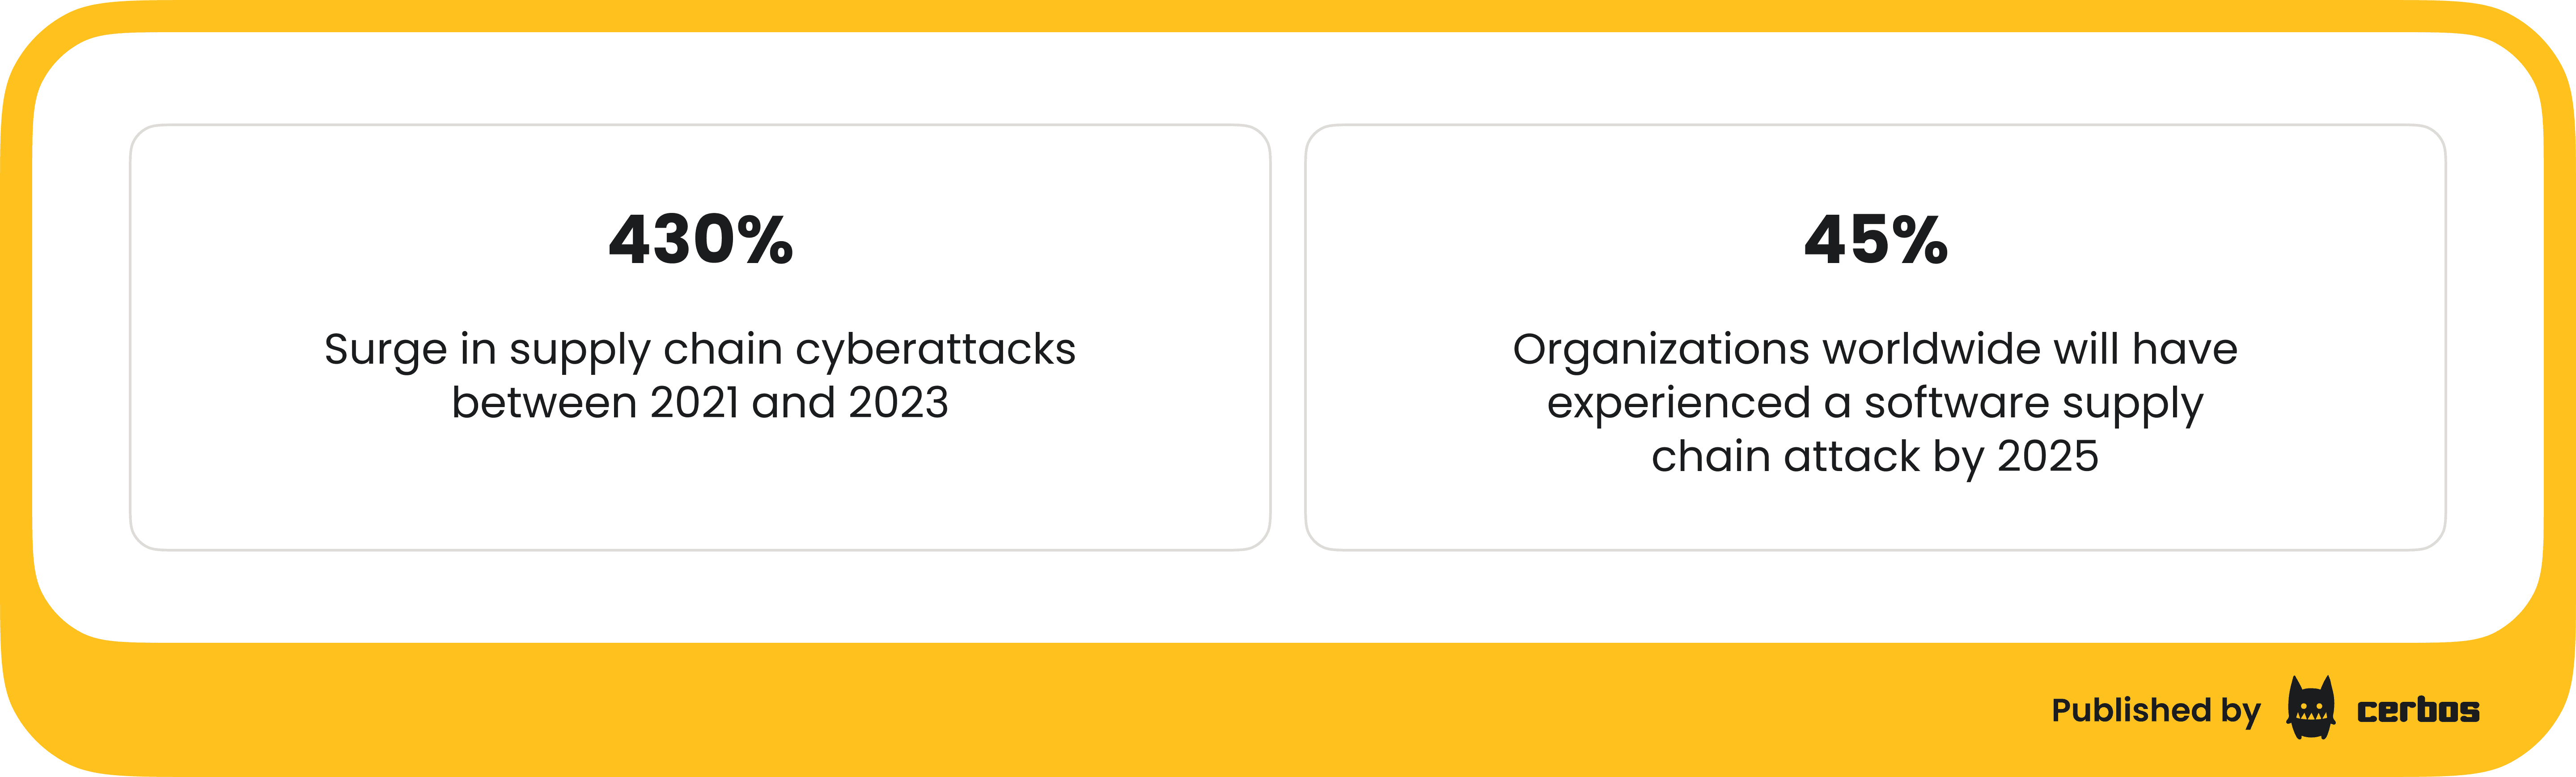
A compromised vendor account or leaked integration key can provide indirect access to internal workflows. Security boundaries must account for partner systems as part of the attack surface, not as trusted extensions. Software supply chain attacks have increased significantly in recent years:
In 2020, Wirecard collapsed after accounting irregularities and deficiencies in internal controls were uncovered. Investigations focused on governance, financial oversight, and the reliability of reporting processes. Weak segregation of duties and insufficient auditability contributed to regulatory action and loss of market confidence.
Fintech platforms process payment data, KYC documents, and transaction records across jurisdictions. Under GDPR and PCI DSS, insufficient restriction of access or incomplete audit logging can trigger enforcement action, fines, or operational constraints. You definitely want to avoid this.
I wanted to leave you with something easy to scan.
So the table below maps each fintech security risk to its primary mitigation strategies. Use it to quickly assess where your gaps are today. If you want to go deeper into implementation details, the next section breaks each control down further.
| Fintech risk | What you should implement |
|---|---|
| Compromised credentials | Enforce phishing-resistant MFA for employees and privileged users, and require step-up authentication with a fresh authorization check for high-risk financial actions |
| Excessive privileges | Run regular access reviews and enforce least privilege across users, service accounts, workloads, and AI agents to reduce blast radius |
| Broken access control | Enforce fine-grained and contextual authorization at runtime across applications, APIs, services, and AI systems |
| Weak internal segmentation | Enforce resource-level authorization at every service boundary and avoid relying only on mTLS or token validation between internal services |
| Credential, token, and key exposure | Use short-lived, narrowly scoped tokens, rotate signing keys regularly, and apply strict credential lifecycle management |
| Limited visibility into access decisions | Log and audit every authorization decision, including identity, action, resource, and outcome, to maintain regulatory traceability |
| Fraud systems bypass and transaction manipulation | Implement real-time transaction monitoring, rate limiting, and step-up verification for high-risk financial actions |
| Third-party dependency risk | Scope and isolate third-party integrations, restrict API keys, validate webhooks, and run regular vendor access reviews |
| Data residency and regulatory exposure | Enforce region-based data storage, strict access controls, and complete audit logging to meet PCI DSS, GDPR, and SOC 2 requirements |
Now let’s talk about how those controls actually translate into concrete actions inside a fintech platform. Each of them could easily deserve its own deep dive 🙂. But let’s keep it simple and focused on fintech security + Zero Trust.
A successful login should not establish implicit trust. Enforce phishing-resistant MFA for employees and privileged users, especially those who can initiate payments or access sensitive customer data.
Require step-up authentication before high-risk actions such as payouts, limit changes, and bulk exports. Sensitive financial operations should not rely solely on the initial authentication event that created the session.
After identity is verified, the next question is whether that identity is allowed to perform a specific action on a specific resource.
In a Zero Trust model, that decision is made at runtime for every protected request. Permissions should be narrowly defined across users, service accounts, workloads, and AI agents. Financial operations such as payments, balance updates, or data exports should be evaluated using fine-grained, contextual access policies that consider the action, the resource involved, and relevant attributes such as ownership or transaction value.
Do not assume that a request is safe because it came from another internal service. Every service should perform its own authorization check. Cerbos helps you implement this kind of fine-grained, runtime authorization out-of-the-box.
Access should reflect current responsibilities, not historical assignments. Regular access reviews help remove permissions that were granted temporarily and never revoked.
Credentials should be short-lived and tightly scoped. Use expiring tokens and rotate signing keys on a defined schedule so that exposed credentials cannot be reused indefinitely.
AI agents and automated workflows should operate under the same controls as human users. Their identities must be scoped to the exact financial actions required for their task, without broad or persistent access.
External providers should not be treated as trusted extensions of your system. Scope API keys narrowly, validate webhook signatures, isolate integration endpoints, and monitor partner activity. Vendor credentials require the same lifecycle management and review processes as internal identities.
In addition, integrate dependency scanning and software composition analysis into your CI/CD pipeline to detect vulnerable third-party libraries before they reach production. Supply chain exposure often originates from code you inherit, not code you write.
Technical controls are not enough if employees cannot recognize phishing attempts or handle sensitive data correctly. Regular security training should focus on real attack patterns:
Privileged users and support teams require additional controls because their access can directly affect financial operations. Human error remains a common entry point, so awareness and clear internal processes reduce the likelihood of initial compromise.
Authorization decisions that affect financial data or money movement should be logged with enough detail to reconstruct what happened. You should be able to see which identity performed which action on which resource, and under which conditions it was allowed. This will help you stay compliant with SOC 2, ISO 27001, PCI DSS, and GDPR.
Thanks for reading. Fintech security is ultimately about building systems where control boundaries hold, even when something goes wrong.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。