





The 2025 Gartner Identity and Access Management (IAM) Summit in London brought the identity community face-to-face with the future. From the surge of machine identities to evolving authorization patterns and policy-based control, the event underlined a clear shift: identity and access are no longer just IT plumbing - they're strategic infrastructure.
Machine identities - whether containers, VMs, services, or AI agents - have exploded in number and complexity. In a standout session, Gartner’s Erik Wahlstrom walked through the emerging discipline of Workload IAM, warning that many orgs are sitting on a mountain of unmanaged machine IAM debt.
The solution? A well-structured identity taxonomy that recognizes not just users, but also devices, workloads, and services as first-class identity types. This, paired with what Gartner calls an "identity fabric", creates a functional foundation for managing secrets, credentials, and access across hybrid and cloud-native environments.
For authorization vendors and platform teams alike, the takeaway is clear: machine identities need the same level of rigor and lifecycle management as human users, possibly more.
Another key theme was authorization modernization. Mehmet Yaliman challenged legacy approaches that hardcode access logic into apps and services.
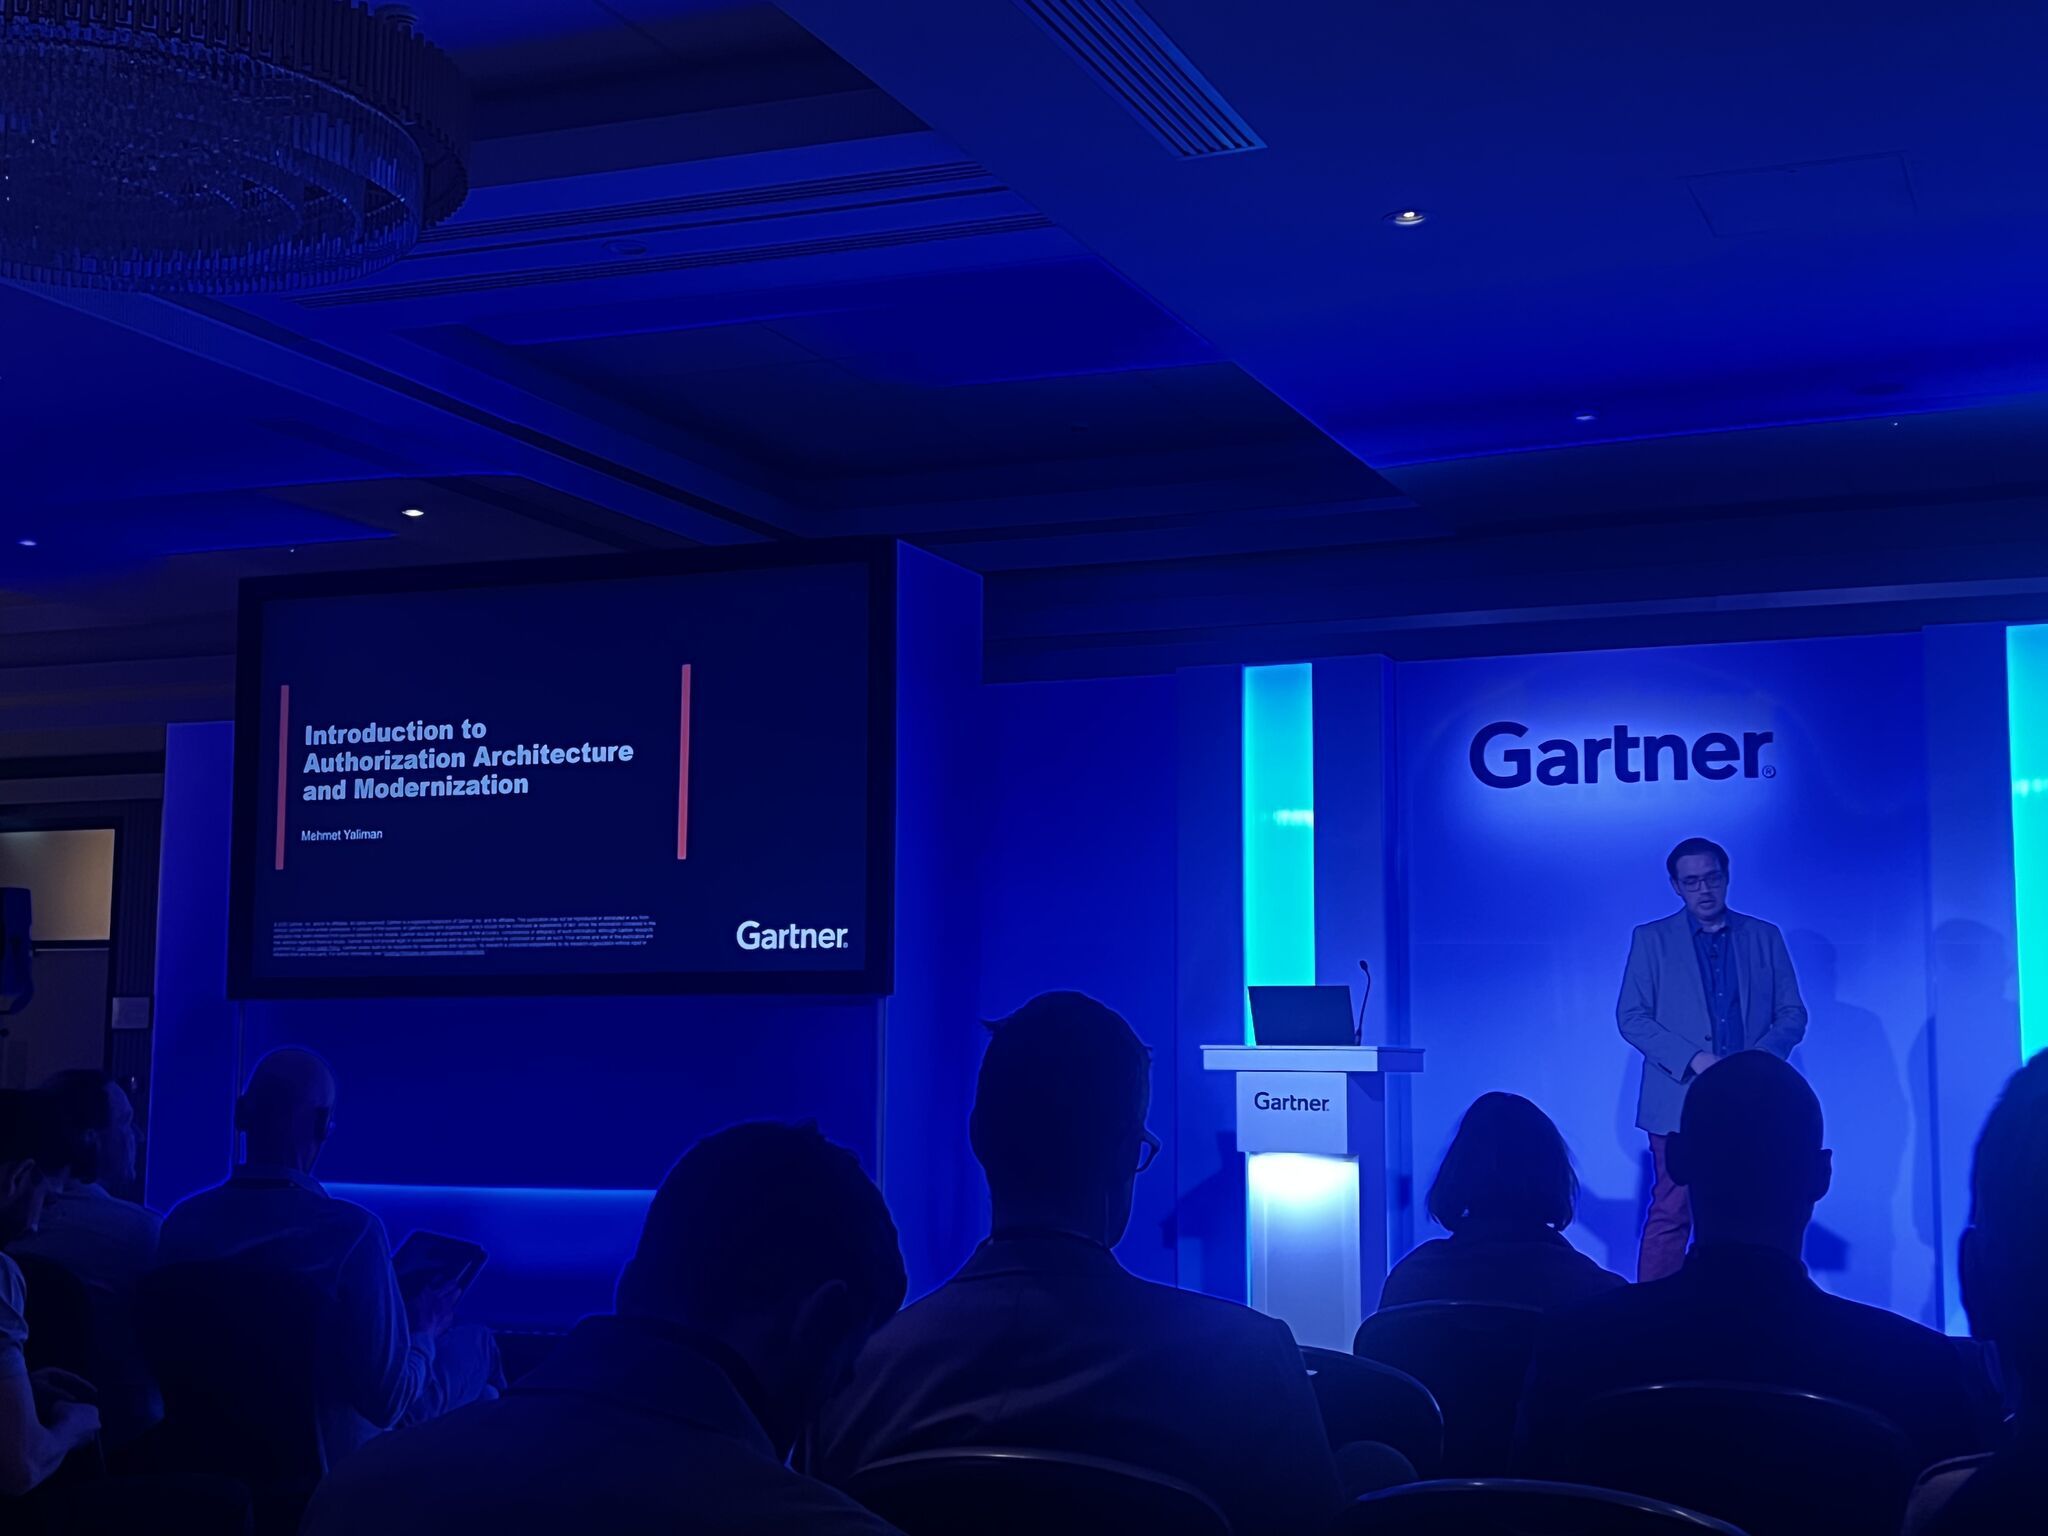
Authorization, he emphasized, should be:
The framework Gartner proposes combines admin-time controls (e.g., role provisioning) with runtime decisions (e.g., risk-aware access). It’s not either-or - it’s both, working in harmony, and the architecture we have been recommending since the inception of Cerbos.
Critically, the session called out the risks of “authorization sprawl” - a reality many engineering teams know too well. The prescription? Define standardized policy patterns for portals, APIs, services, and mesh layers. And use dedicated authorization tooling to implement them.
Building on that, Mehmet Yaliman’s follow-up session on policy-based authorization made the case for decoupling access control from code entirely. Policy becomes the bridge between strategic intent (Zero Trust, least privilege) and operational execution.
We loved the emphasis on “understanding your facts” - identifying the data needed to evaluate access decisions at runtime. It’s a call to action for engineers and architects to treat policies like first-class software artifacts: versioned, testable, and explainable.
For those evaluating tooling, Gartner compared various engines, policy languages, and authorization models across several factors such as expressiveness, usability, and ecosystem maturity. Spoiler: there’s no silver bullet. Multi-tool orchestration is inevitable.
One of the most exciting moments of the conference was the world-exclusive interop session of OpenID AuthZEN. This time, focusing on how to integrate authorization at the API Gateway layer using the specification.
Cerbos was proud to take part in this live interop event, alongside implementers like Aserto, Tyk, WSO2, Okta, Amazon Web Services, Kong, and others. This was the first public demo of API gateway use cases powered by externalized authorization policies, and it drew a queue that wrapped around the hall.

AuthZEN marks a huge step forward for composable authorization architectures - something we at Cerbos care deeply about. The goal is seamless integration between platforms and services, regardless of the policy engine underneath.
The signal from Gartner this year was unambiguous: authorization is no longer just about controlling access. It’s about enabling agility, enforcing compliance, and delivering secure experiences across complex, hybrid systems.
Key takeaways:
Cerbos was built for this shift. If you're designing for runtime authorization, multi-cloud policy control, or platform-native IAM, we're here to help.
此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。