





2025 was a transition year for us.
We entered the year with a strong authorization foundation. Our focus has shifted to extending that foundation for enterprise and regulated environments. Over the past 5 years, Cerbos earned the trust of the developer community. That trust increasingly translated into product usage, popularity of our open source PDP and commercial growth.
Demand for our authorization management platform grew 4x in 2025. Cerbos was recognized by Gartner as an authorization management platform vendor, and our founders were invited to speak at leading IAM and security events.
Our product wasn't the only thing that evolved. Our branding, positioning and the value we provide matured as well. We published 4 ebooks, held 7 webinars, and released 130+ guides helping engineers and security leaders understand emerging security risks with non-human identities, MCP, and AI agents, alongside authorization and security best practices.
In 2025, we focused on building Cerbos into a complete authorization management platform. The shift wasn't about adding features. It was about making authorization something enterprises can actually manage at scale. We expanded Cerbos Hub to support the full access control policy lifecycle:
Teams can now create, update, and deploy policies programmatically, rather than treating policies as static configuration.
Policy Stores made it possible to scale authorization by tenant, environment, or use case without duplicating logic. Organizations managing distributed systems gained a way to maintain consistency without forcing a single deployment pattern everywhere.
Git-based workflows brought authorization changes into existing engineering practices. Policies can be pushed from any Git provider or CI tool, with real-time distribution and built-in testing. Changes became auditable and reviewable, just like code.
Cerbos Hub now provides a complete audit trail of every authorization decision, with full context on who asked for what, under which policy version, and why it was allowed or denied.
Here are the major Cerbos Hub updates shipped in 2025:
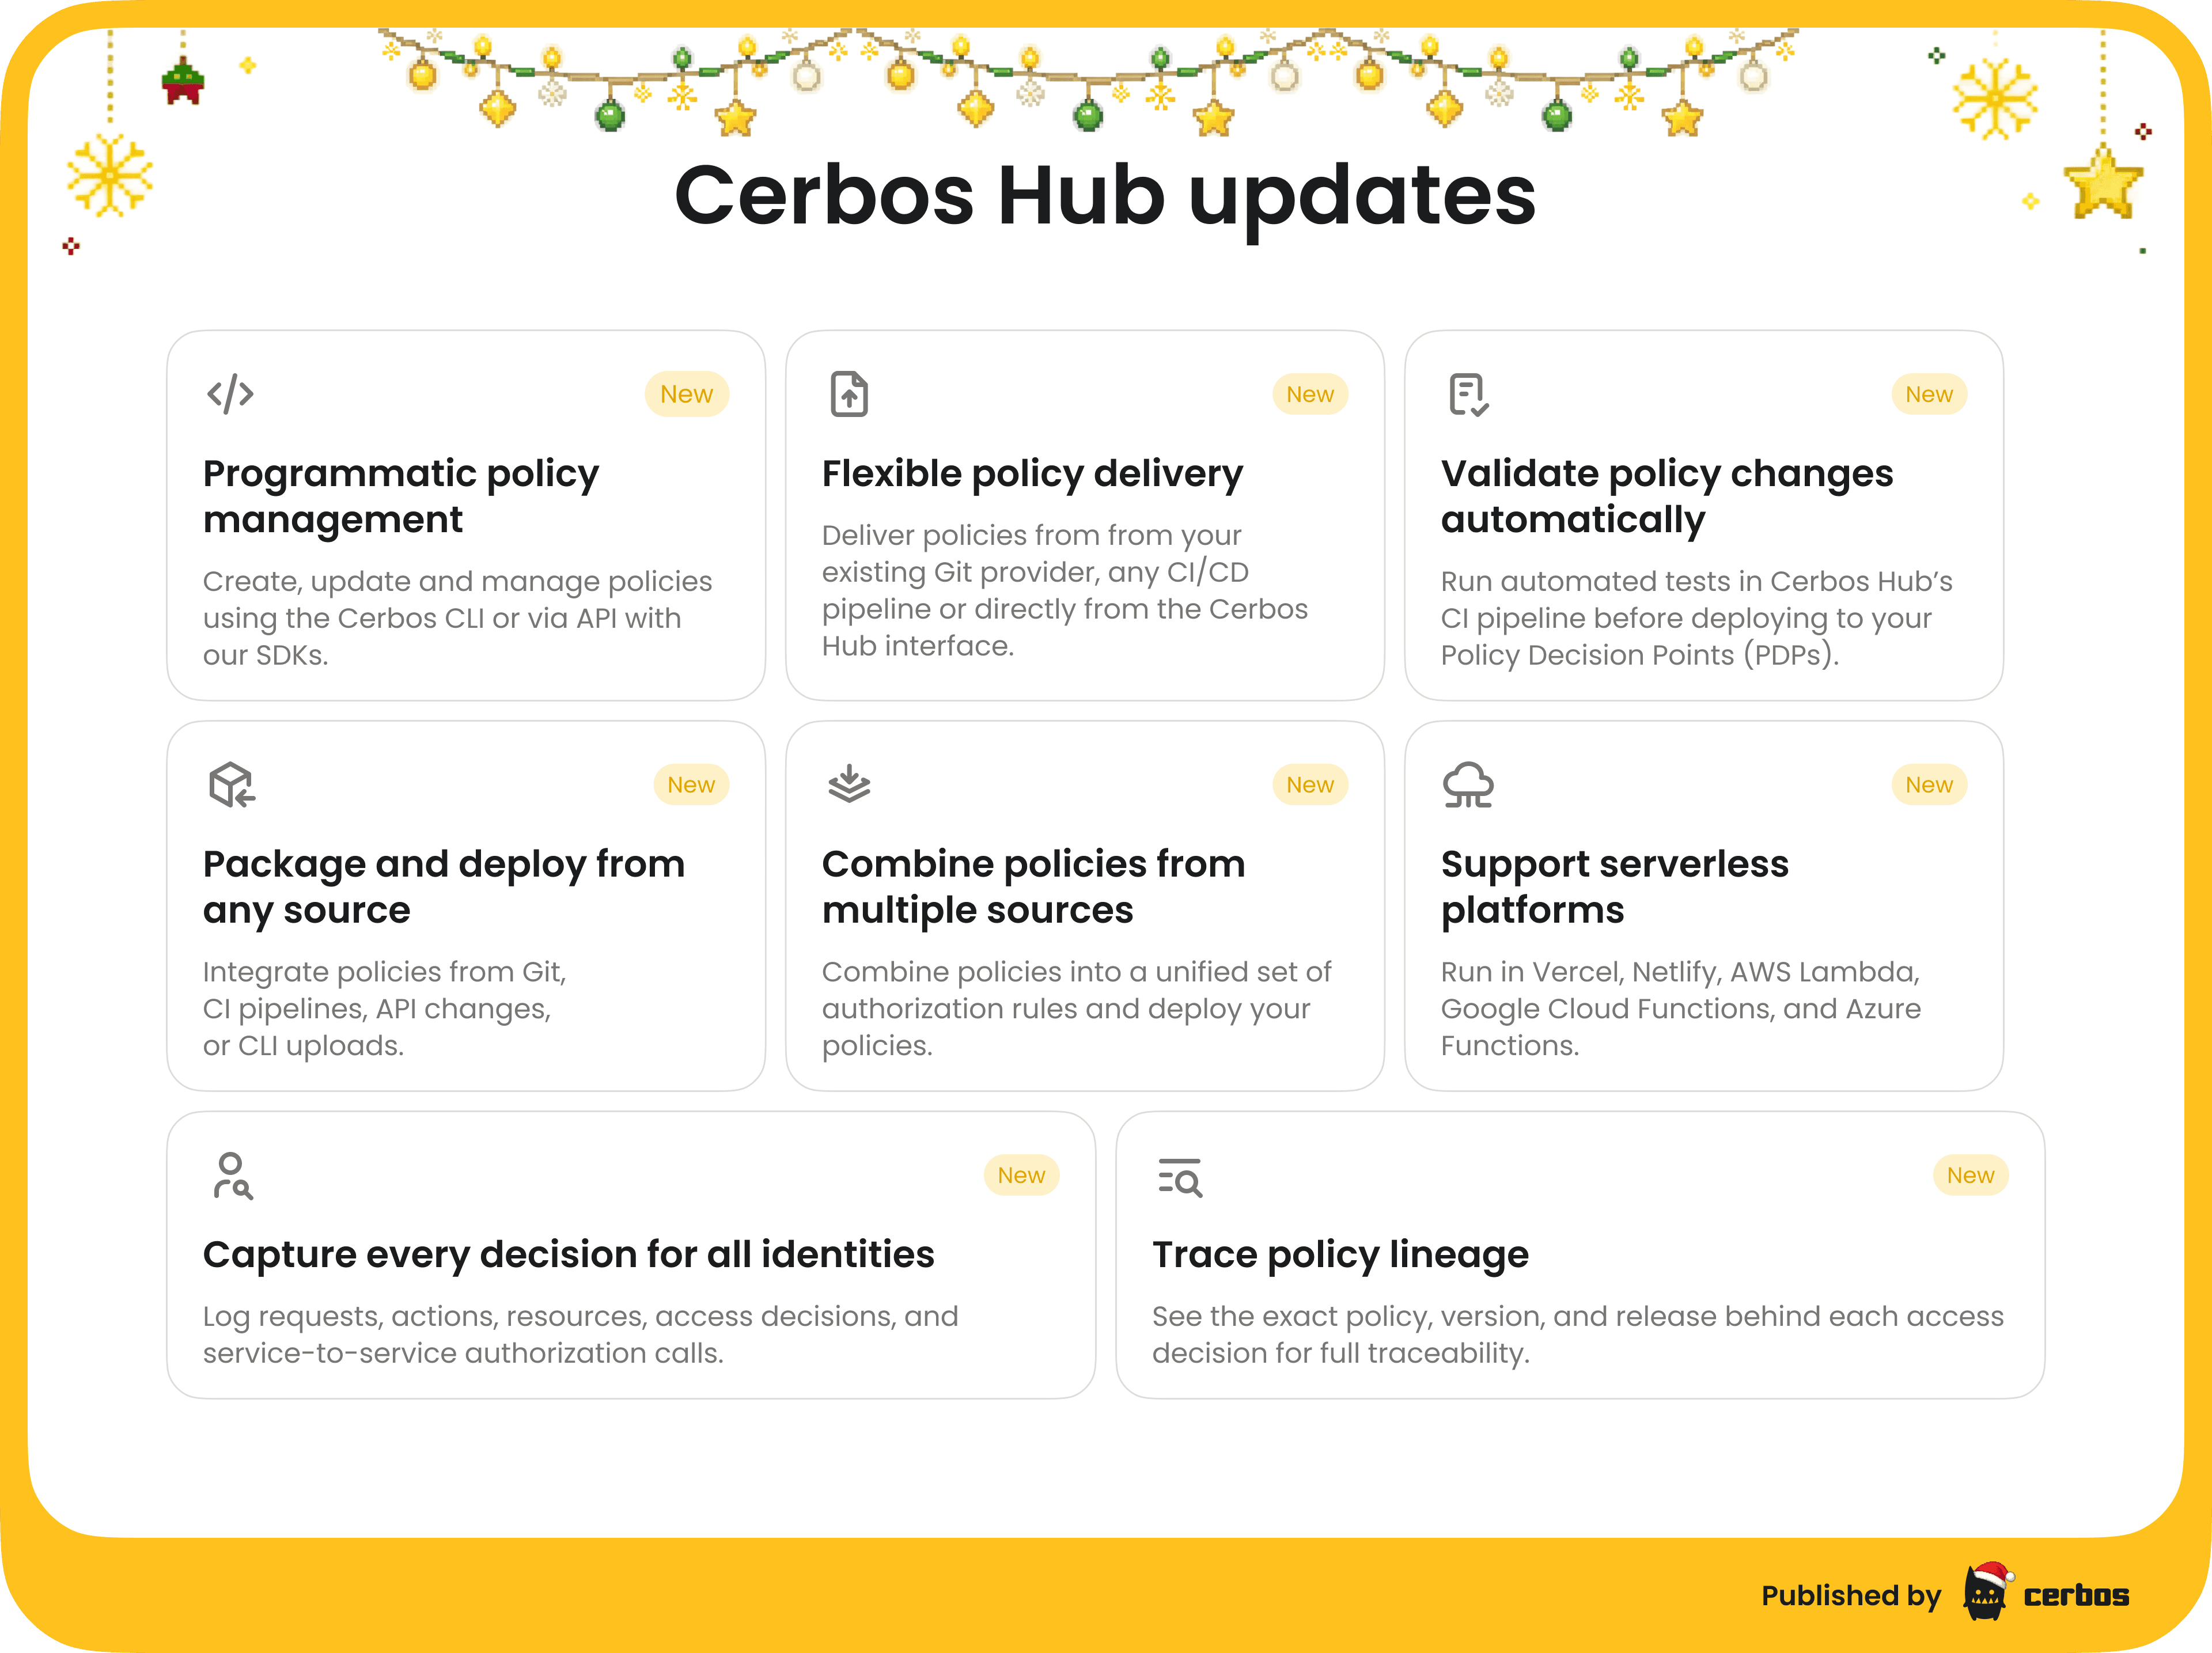
Cerbos PDP evolved alongside Hub. We strengthened policy validation, improved schema error reporting, and expanded testing capabilities so teams catch issues before production. We shipped 11 PDP updates and more than 20 product releases in total.
Together, Cerbos Hub and PDP provide a Zero Trust authorization system that enforces least privilege consistently across all environments.
Across the industry, we saw RAG, AI agents, MCP servers, and automated workflows being introduced faster than security models could keep up. These systems operate at a scale and speed that magnifies authorization risks. A single misconfigured permission can expose privileged and secure datasets. An overprivileged agent can cascade access across systems in ways that are difficult to trace or stop.
In many cases, these systems inherited permissions designed for humans or backend services, with little visibility into what they were actually doing. Traditional role-based access models break down when agents make thousands of context-dependent decisions per second. The question shifted from "who has access" to "what is being accessed, by what, under which conditions, and can we prove it."
We made a deliberate decision to treat AI as a first-class authorization problem by adding support for:
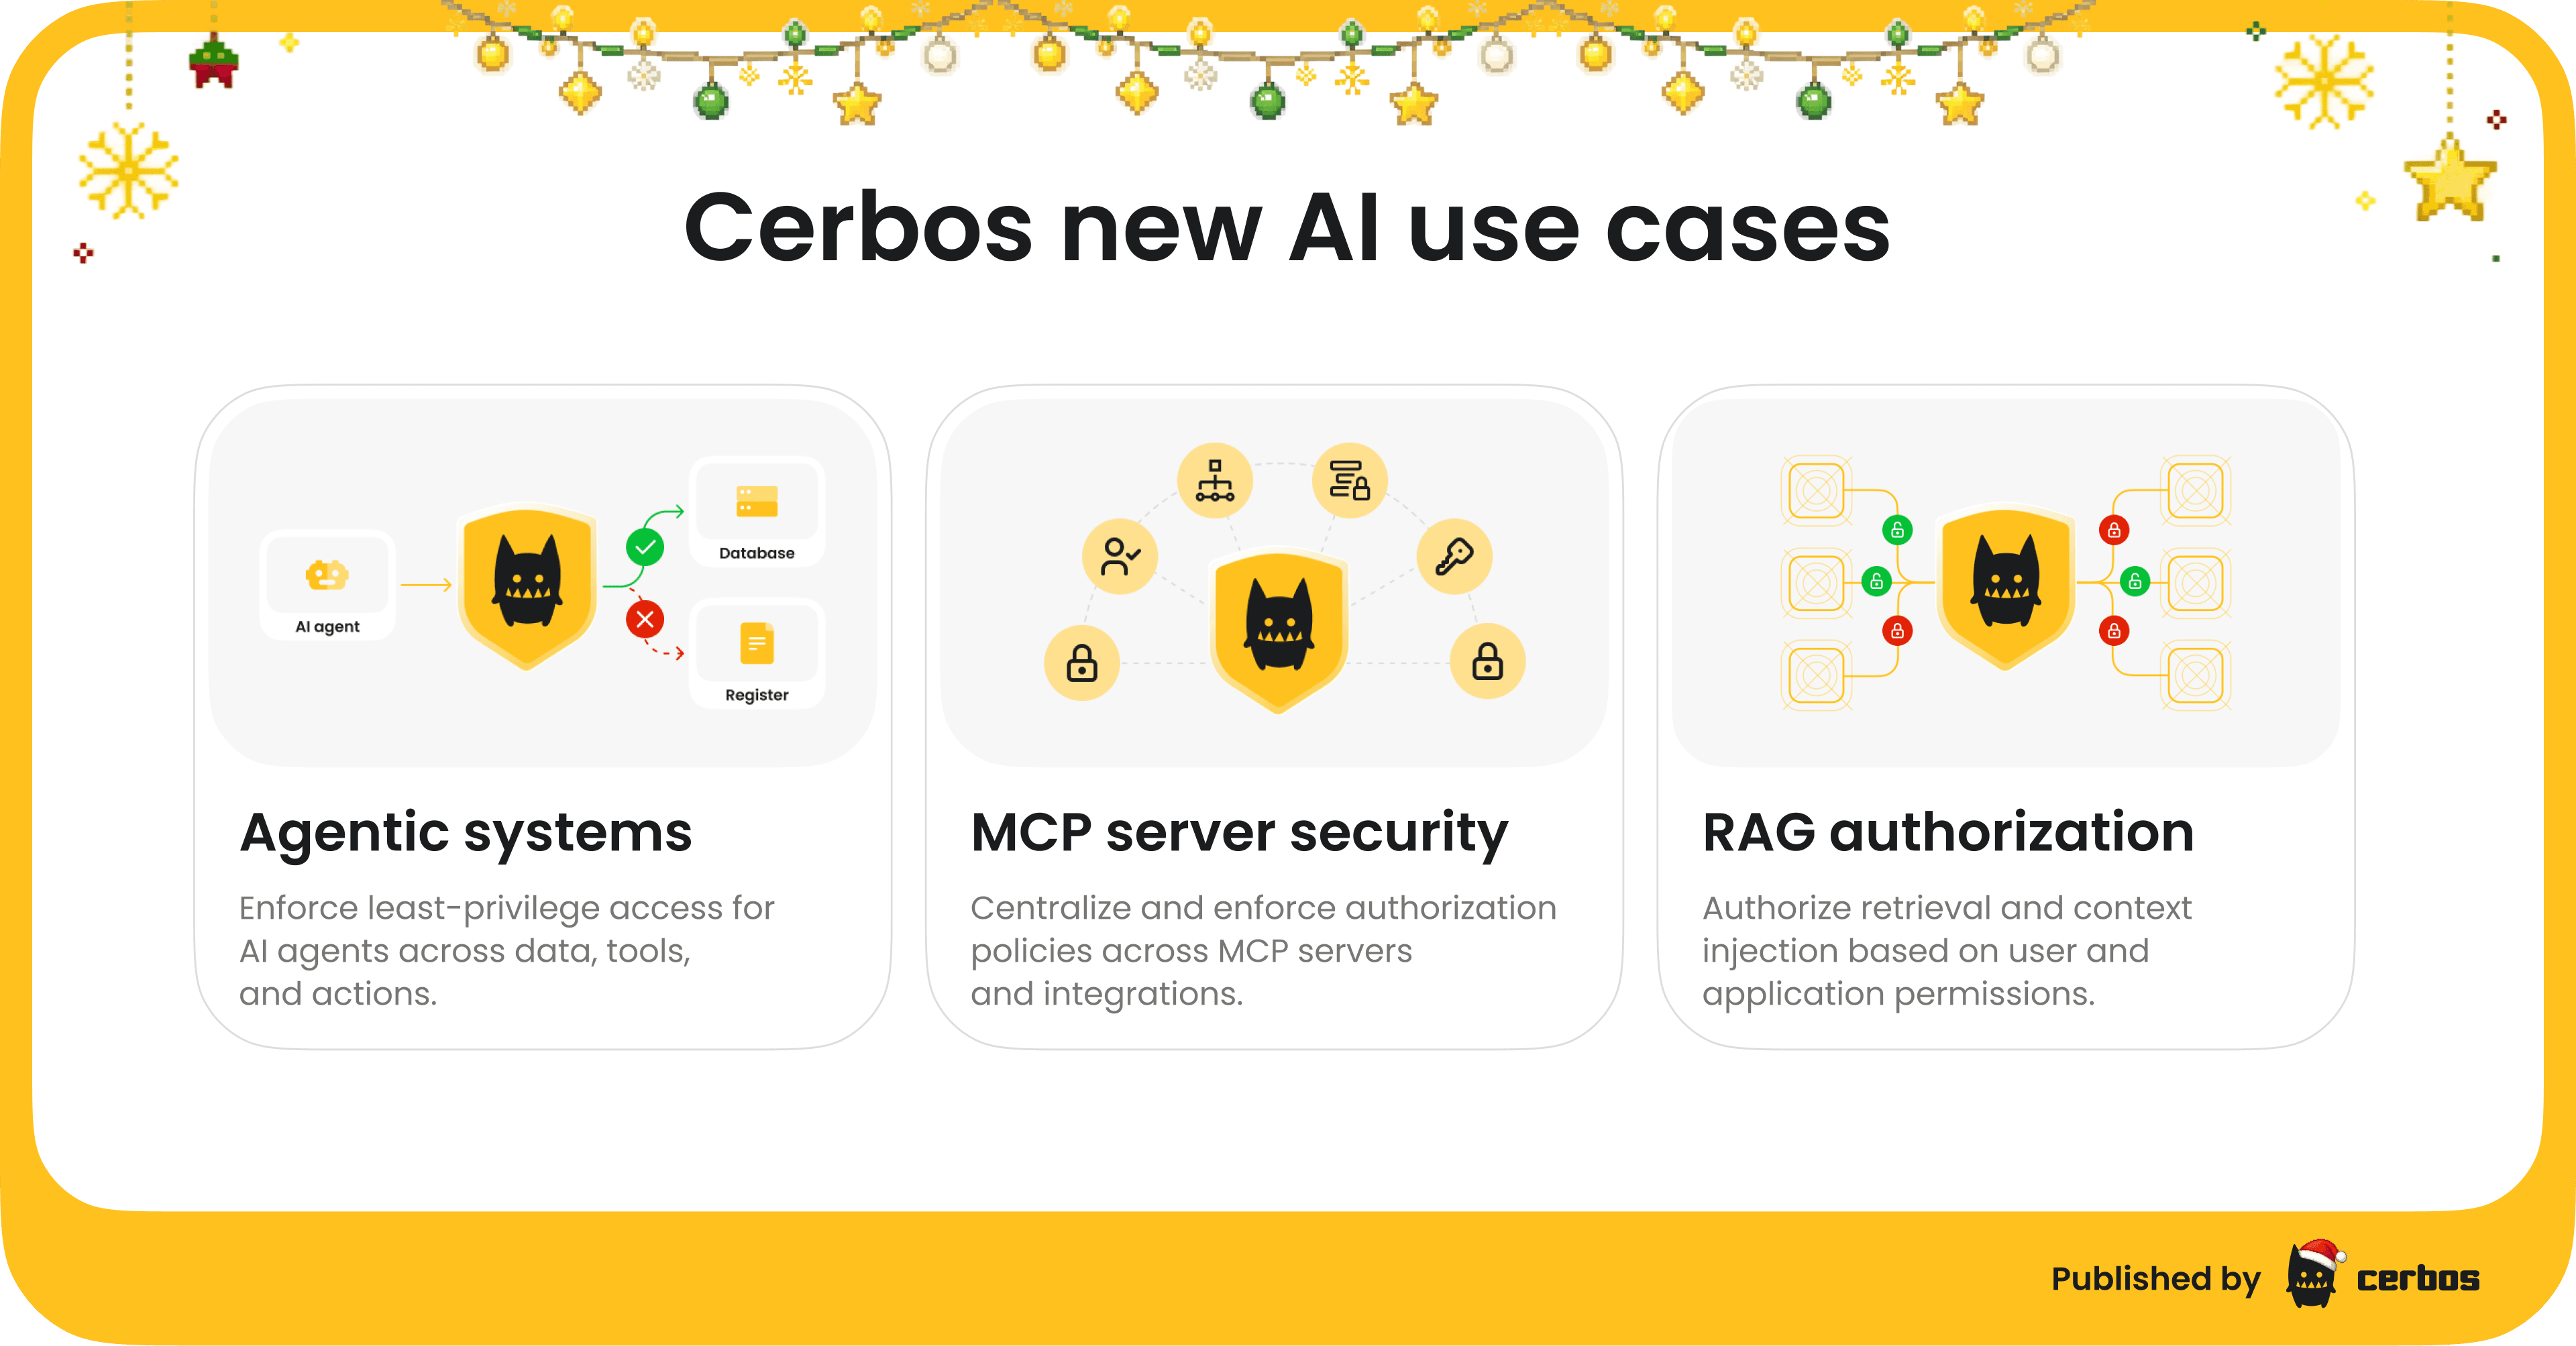
We focused on how authorization should work when agents act autonomously, call tools, and access sensitive data. Not in theory, but in real architectures teams are deploying today. That meant building authorization that evaluates context at runtime, audits every decision, and enforces least privilege without slowing agents down.
We built Cerbos to become a unified solution for all authorization use cases out of the box. In 2025, that scope expanded further based on how teams actually use authorization in production.
Beyond AI systems, Cerbos expanded to support:
The result is a single permission management platform for both human and non-human identities. One that fits into existing identity fabrics, enforces least privilege, and scales with the realities of enterprise systems, while still remaining developer-friendly.
A nice bonus was a complete refresh of our homepage with a new position & messaging, which I’m personally very proud of. The clearer positioning helped engineering teams understand the authorization risks they were carrying, while the product updates gave them a way to address them. And our marketing crew worked continuously to make sure these updates reached engineering teams.
In 2025, we invested more in education. The same questions kept coming up in conversations with teams, not about one single topic, but about how authorization works once systems become complex.
Non-human identities and AI were one part of that. Externalized authorization and permission model design were another. In practice, these problems show up together.
This is reflected in the ebooks we published this year:
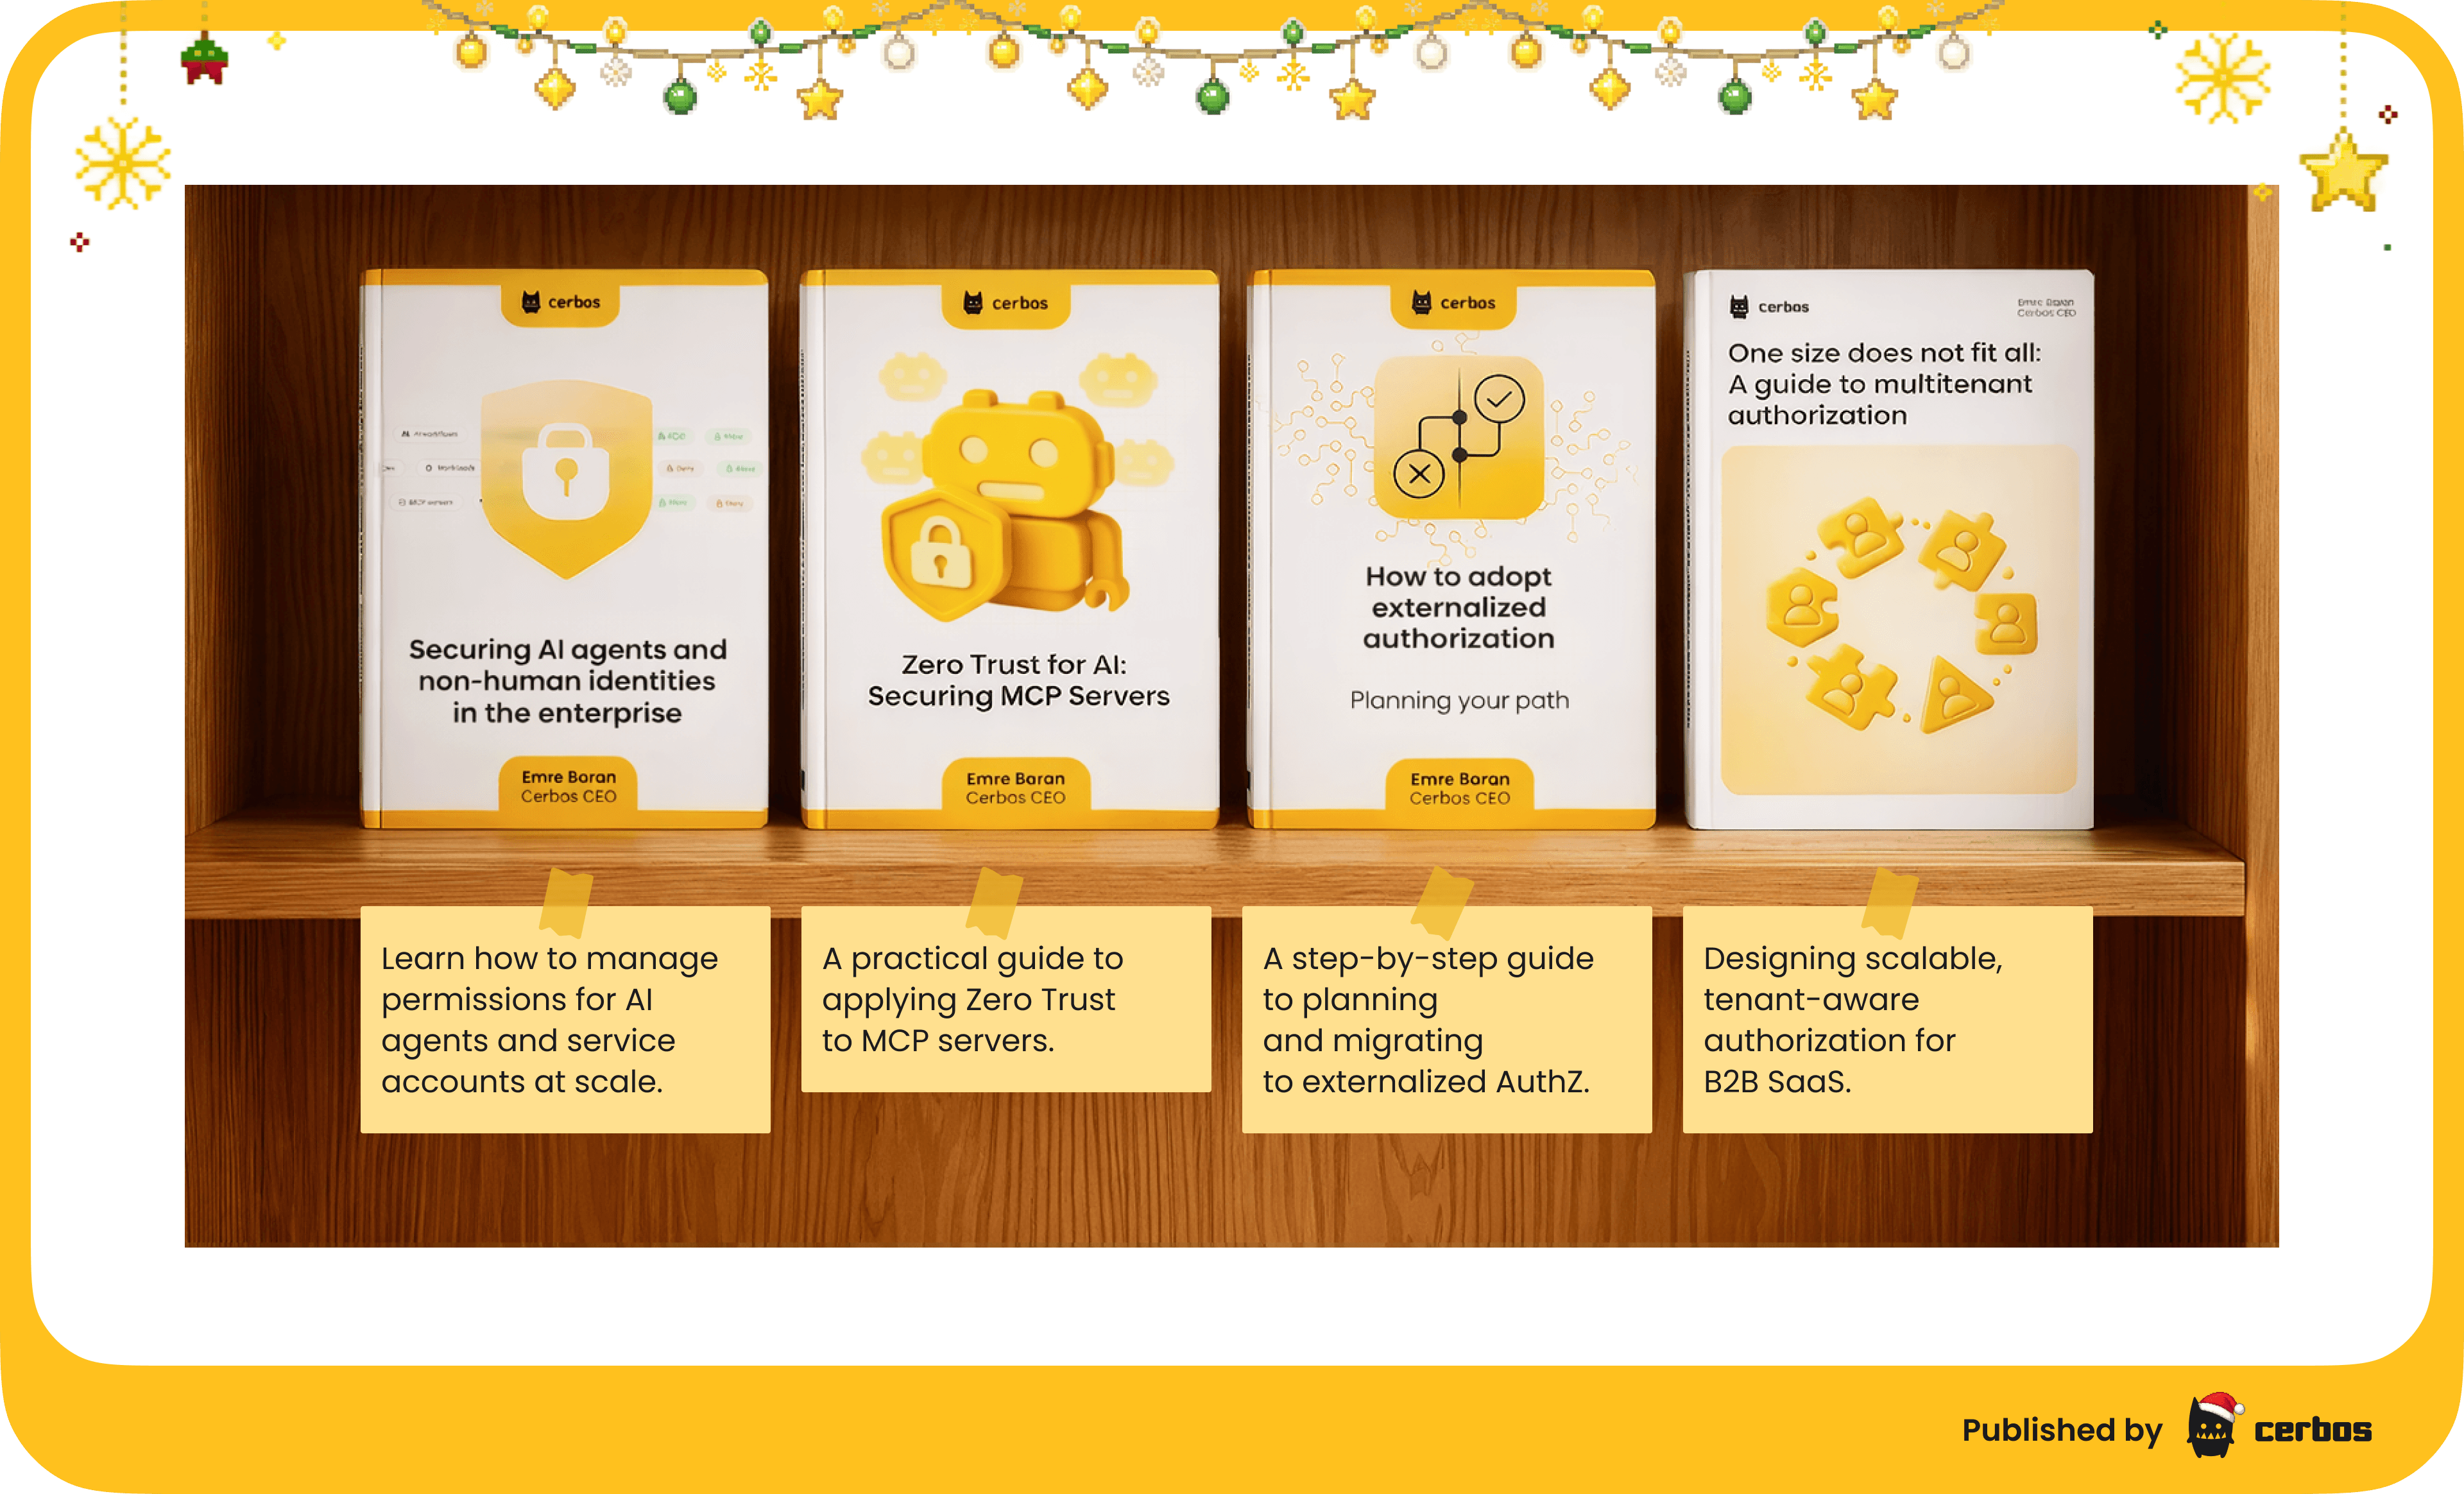
Webinars gave us a way to go deeper on those topics and use cases. Alongside AI security, MCP, and non-human identity topics, we covered authorization in fintech and permission management for multi-tenancy.
Most webinars were oversubscribed, and the ebooks were downloaded by thousands of engineers and engineering leaders.
Last year we spent a lot of time listening to the market. These conversations helped us understand how authorization challenges are evolving as systems grow more complex.
We took part in industry events including Gartner IAM Summit, CyberSec Asia, DevWorld Amsterdam, KubeCon EU, KubeCon North America, Identiverse, European Identity Conference, WeAreDevelopers, Web Summit, Authenticate, and others.
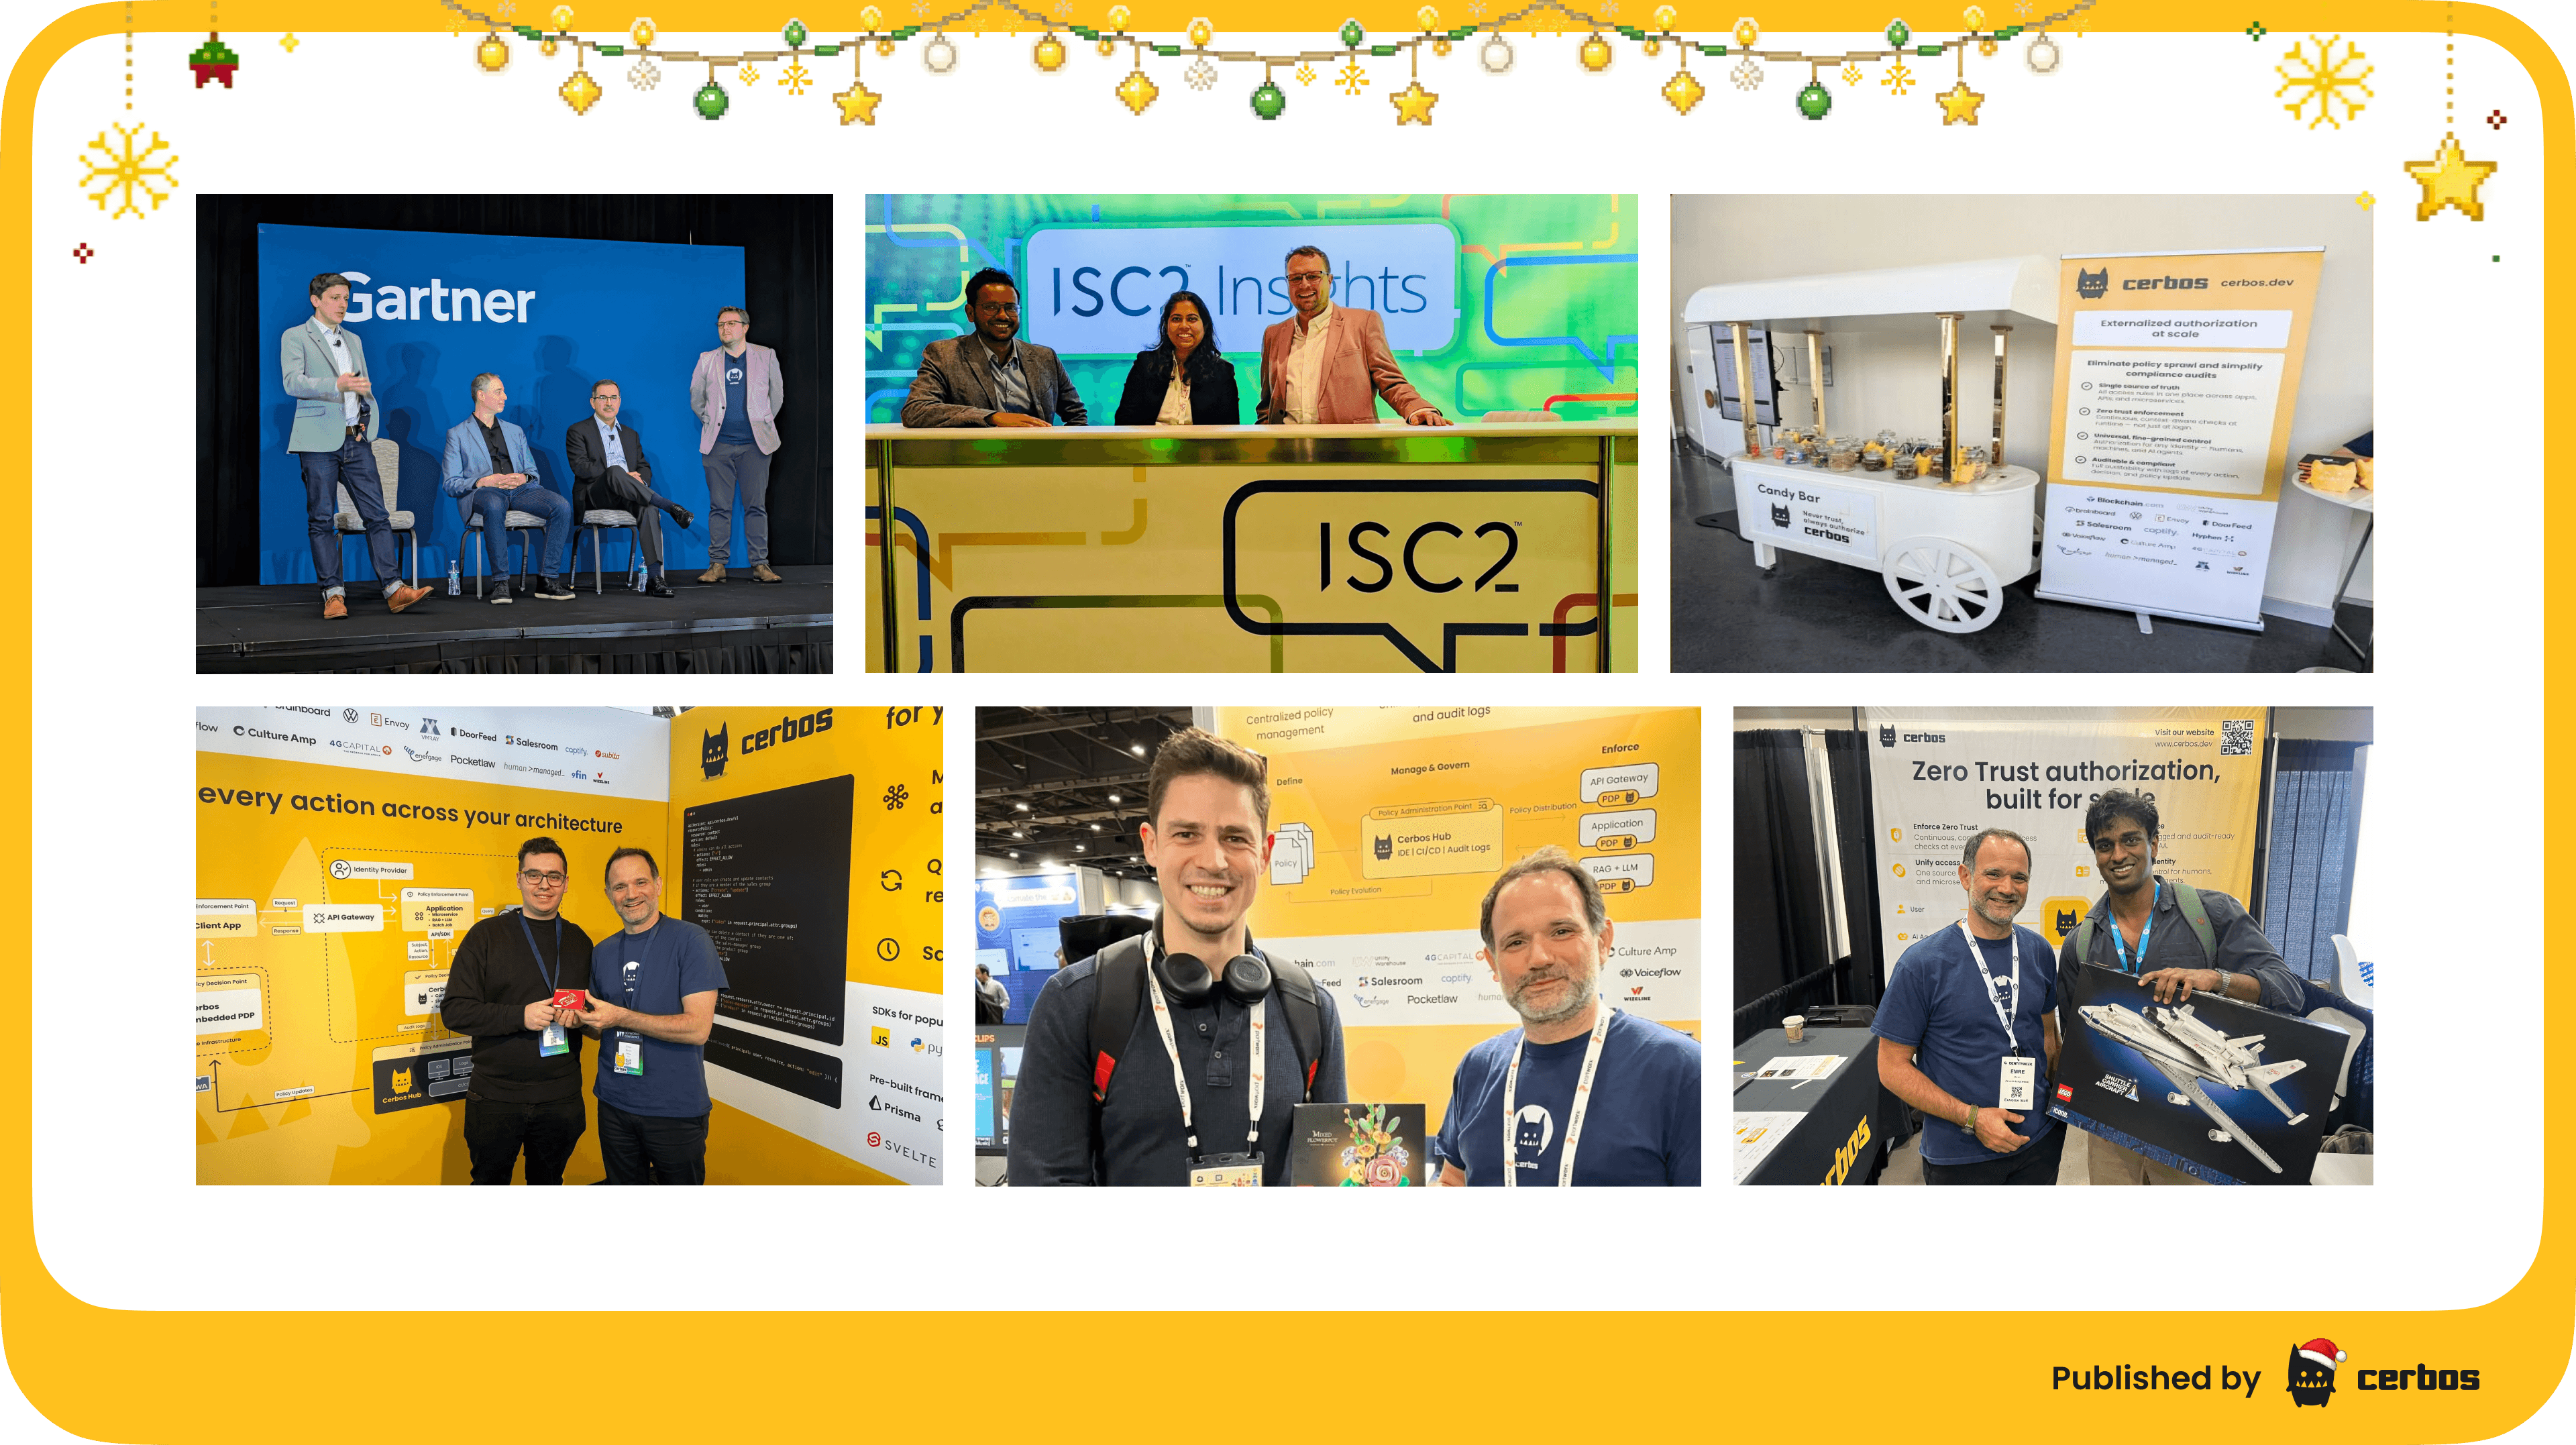
These conversations reinforced our direction. Authorization is moving beyond human access and static roles. Workloads, services, and AI-driven systems now dominate access decisions, and existing models are struggling to keep up.
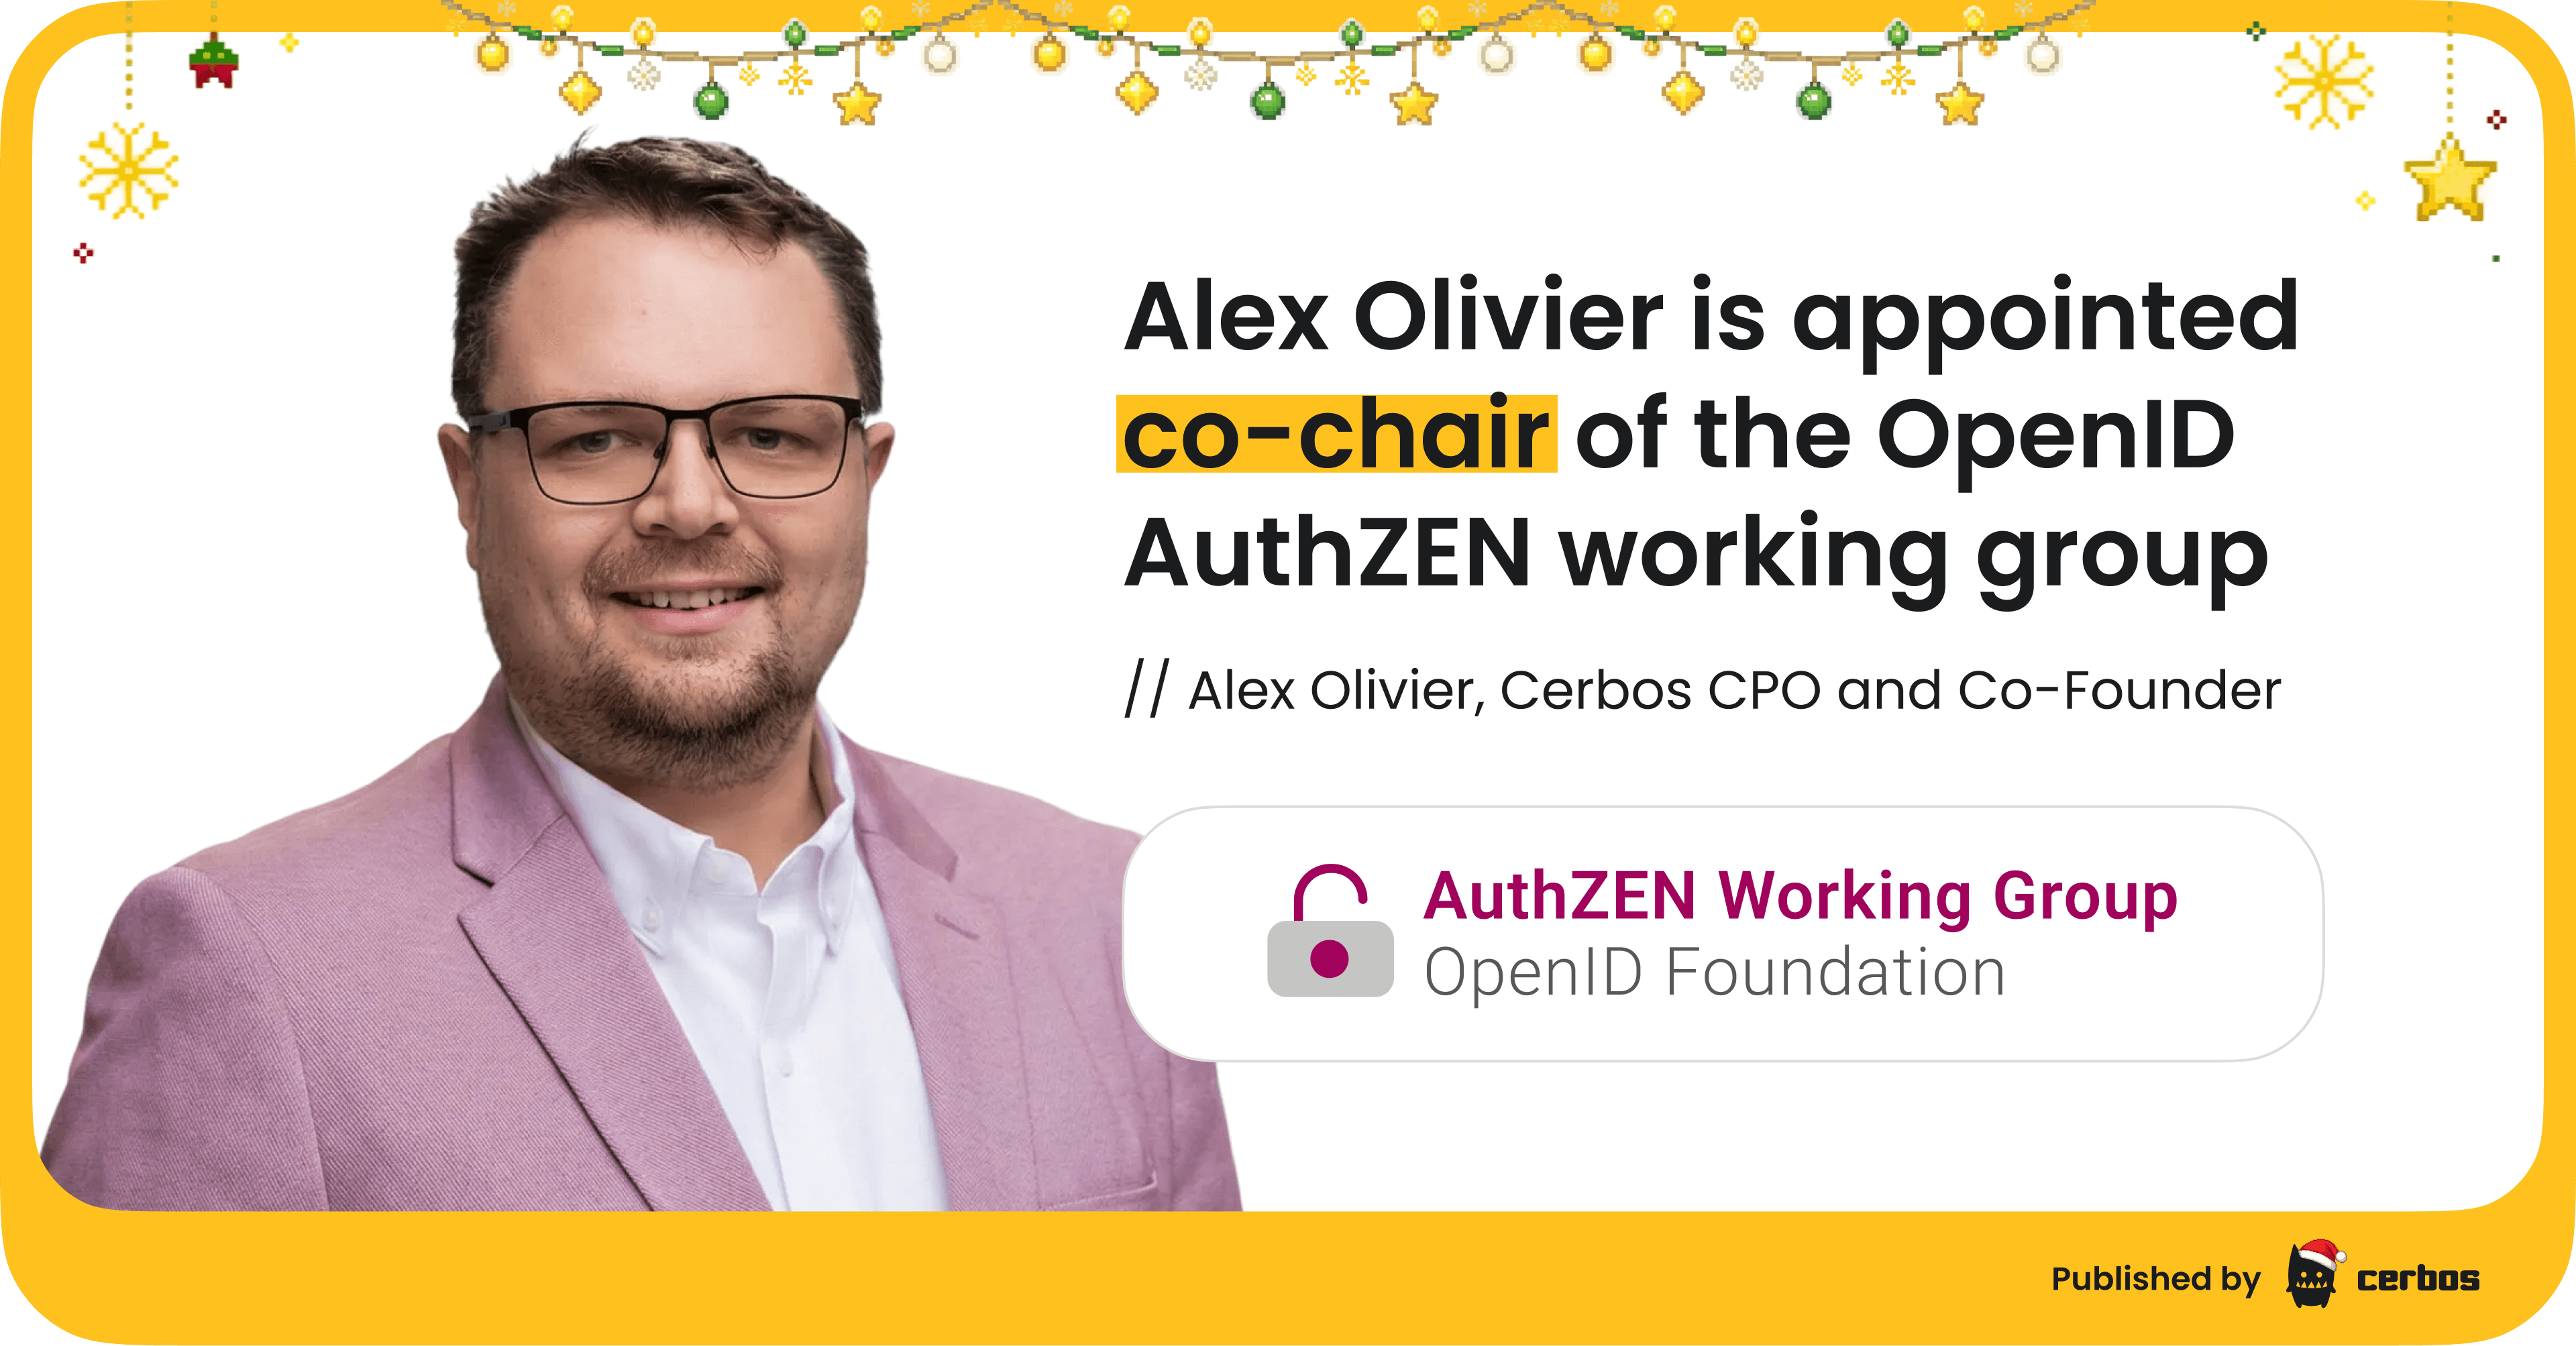
Alongside this, we actively contributed to authorization standardization efforts. Our cofounder was elected as co-chair of the AuthZEN working group, which focuses on standardizing authorization and is strongly supported by Gartner. This work reflects a broader push to define clear, interoperable models for authorization.
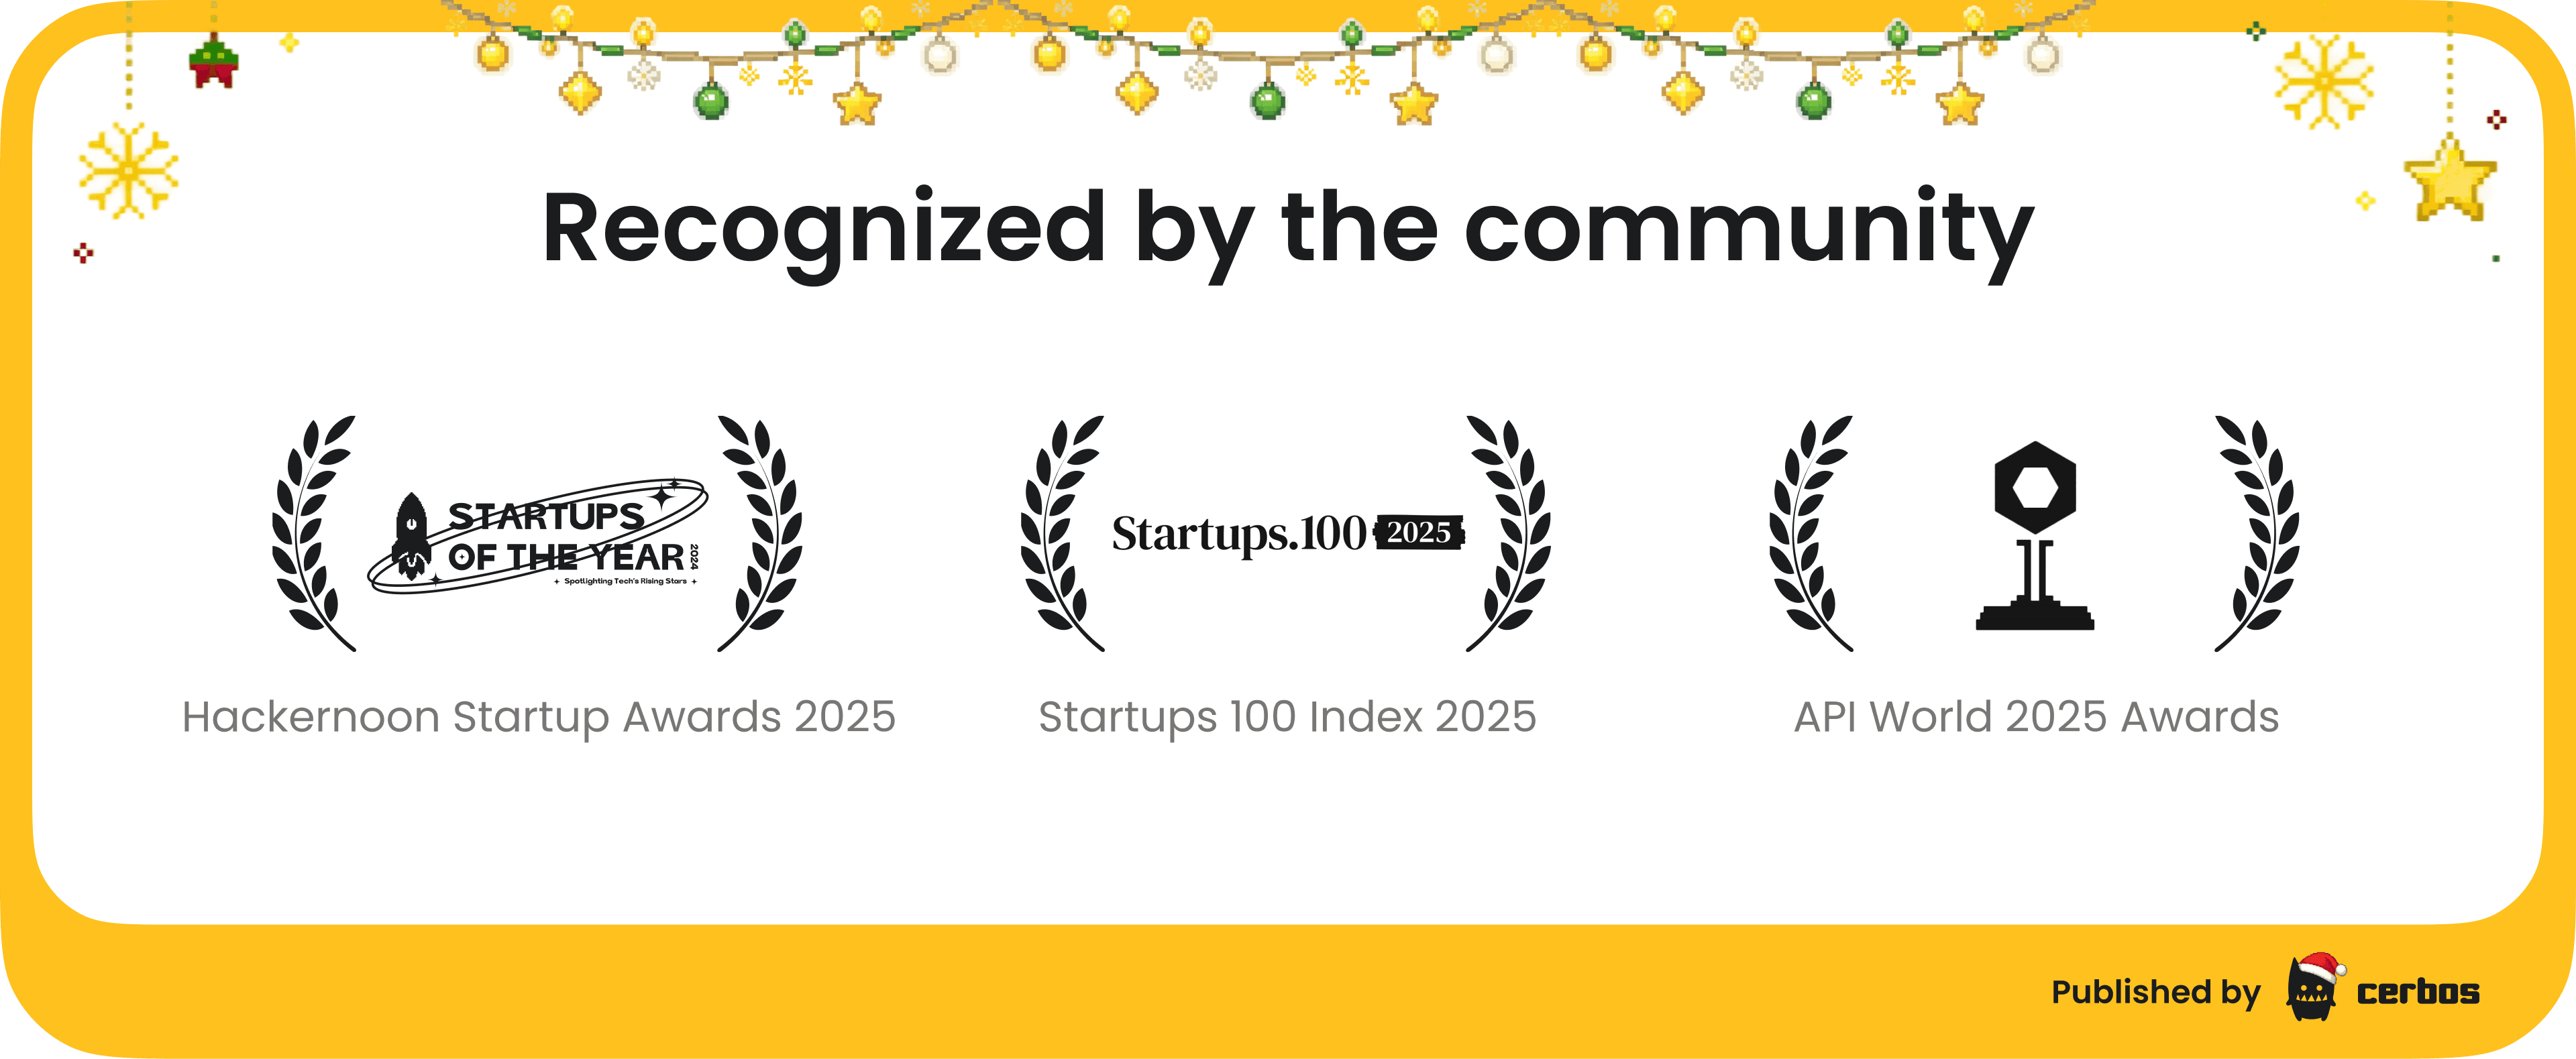
2025 also brought external recognition for the work we have been doing for years.
Cerbos was included in the 2025 Startups 100 list, which was a solid signal that what we are building resonates beyond the IAM space. We also received the API Award for Best in Microservices Infrastructure, recognising Cerbos’ role in securing distributed systems where authorization has to work reliably at scale. On top of that, we were named Startup of the Year in Access Control by HackerNoon.
We do not build for awards, but it was good to see authorization and the work we are doing around it getting visible credit in 2025.
2025 was a year of focus. Product, positioning, and market education came together as we helped define and shape the authorization management category. Continuous engagement with customers, partners, analysts, and the broader security community reinforced our strategic direction and growing leadership in the category.

此内容由惯性聚合(RSS阅读器)自动聚合整理,仅供阅读参考。 原文来自 — 版权归原作者所有。